> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md).
# Права, аудит и ACE
Заметки по безопасности Active Directory для прав, аудита и ACE, охватывающие перечисление, Kerberos, учётные данные, злоупотребление ACL, боковое перемещение, рабочий процесс эксплуатации и этапы проверки.
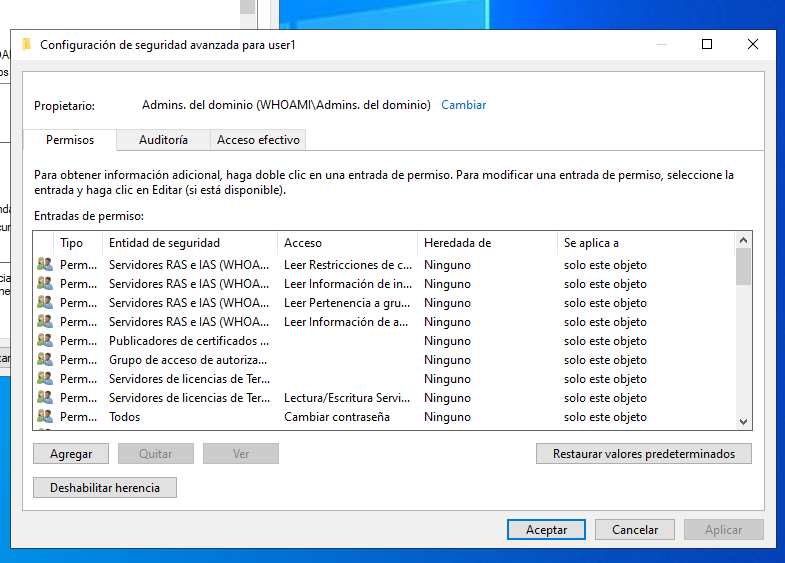
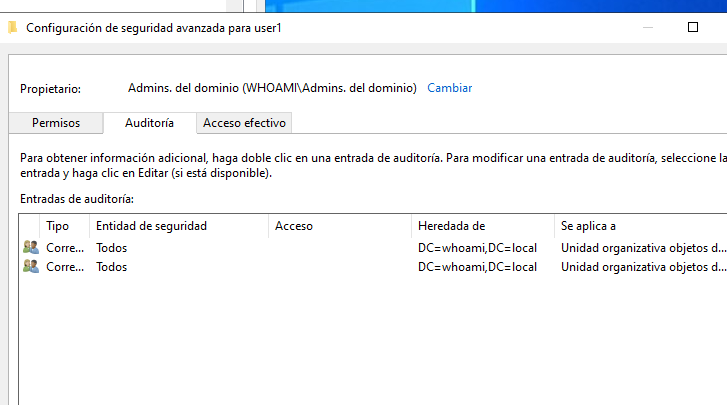
В дополнительных настройках безопасности объекта Active Directory обычно есть несколько важных разделов.
#### Разрешения
Эта **Разрешения** вкладка отображает пользователей или группы, имеющие права на объект.
Примеры возможных разрешений:
* читать объект;
* изменять определённые атрибуты;
* изменять владельца;
* изменять разрешения;
* добавлять участников в группу;
* удалять объект.
#### Аудит
Эта **Аудит** вкладка позволяет определить, какие обращения должны регистрироваться в журнале.
Она используется для отслеживания того, когда пользователь выполняет определённые действия над объектом.
Примеры:
* попытка чтения;
* изменение;
* изменение разрешений;
* удаление;
* Доступ запрещён.
#### Записи разрешений
**Записи разрешений** соответствуют подробным строкам, присутствующим в ACL.
Каждая запись называется **ACE**или **Элемент управления доступом**.
ACE указывает:
* соответствующего пользователя или группу;
* тип доступа;
* предоставленные права;
* соответствующий объект;
* наследуется разрешение или нет.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.