> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/active-directory/enumeration/ldapsearch.md).
# LDAP-поиск
Заметки по безопасности Active Directory для LDAP-поиска, охватывающие перечисление, Kerberos, учётные данные, злоупотребление ACL, боковое перемещение, рабочий процесс эксплуатации и этапы проверки.
### Проверка анонимного доступа к LDAP
{% code overflow="wrap" %}
```bash
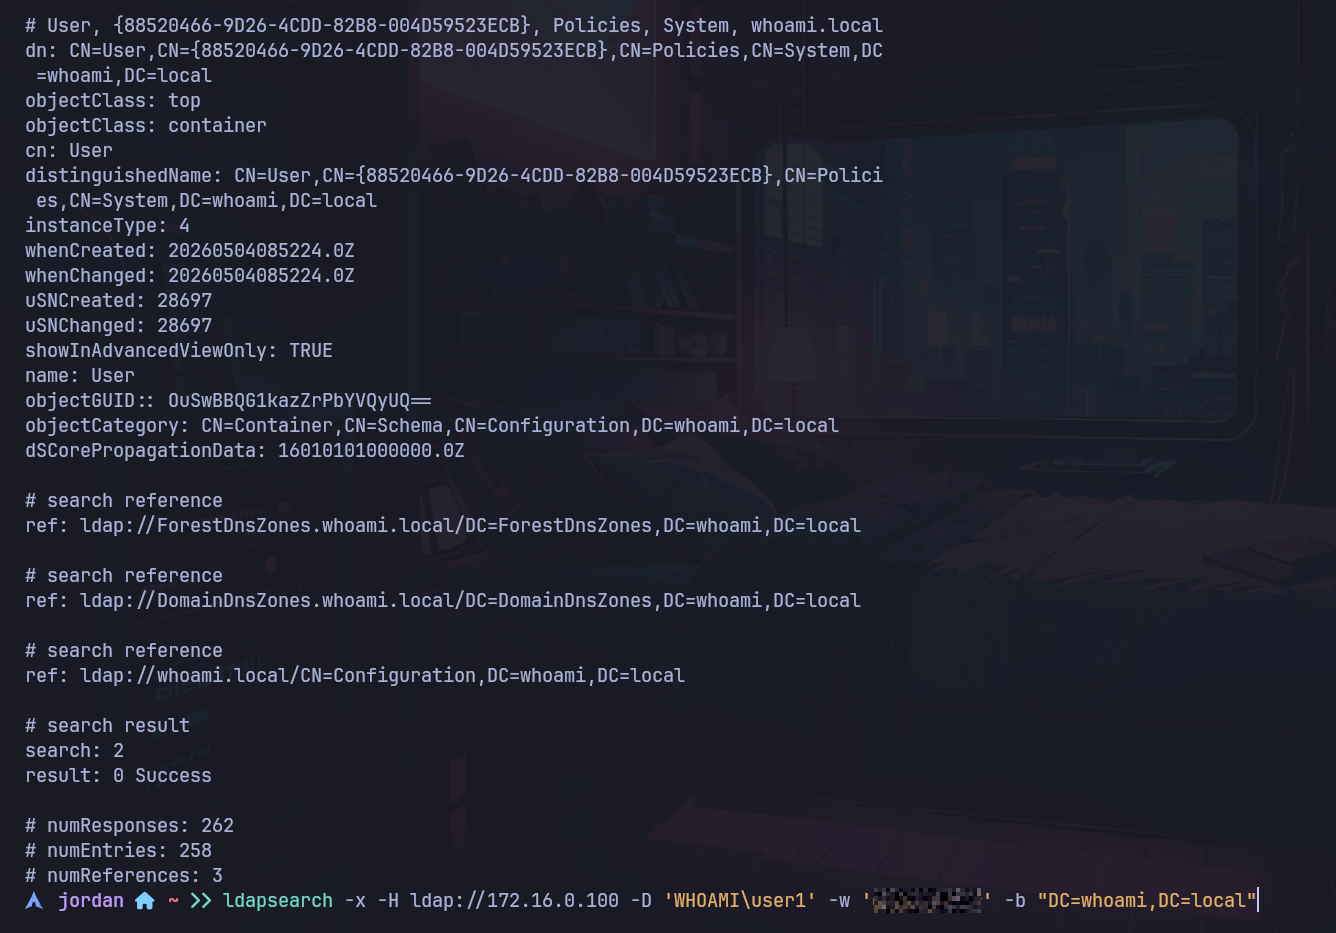
ldapsearch -x -H ldap://172.16.0.100 -b "DC=whoami,DC=local"
```
{% endcode %}
Эта команда пытается выполнить запрос к LDAP без аутентификации.
Во многих современных средах анонимный доступ ограничен или отключён.
### Подключение к LDAP с учётными данными
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "DC=whoami,DC=local"
```
{% endcode %}
Пояснение:
| Параметр | Назначение |
| -------- | ------------------------------------- |
| `-x` | Простая аутентификация |
| `-H` | Адрес сервера LDAP |
| `-D` | Идентификатор, используемый для входа |
| `-w` | Пароль |
| `-b` | Поиск в базе DN |
### Список пользователей в `CN=Users`
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=Users,DC=whoami,DC=local"
```
{% endcode %}
Здесь мы ищем в стандартном контейнере `Users`.
### Список OU
Если пользователи находятся в организационном подразделении, мы используем `OU` вместо `CN`:
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "OU=Users,DC=whoami,DC=local"
```
{% endcode %}
Важное отличие:
| Элемент | Значение |
| ------- | --------------------------------------------- |
| `CN` | Common Name, контейнер или стандартный объект |
| `OU` | Организационное подразделение |
| `DC` | Компонент домена |
### Поиск конкретного пользователя
{% code overflow="wrap" %}
```bash
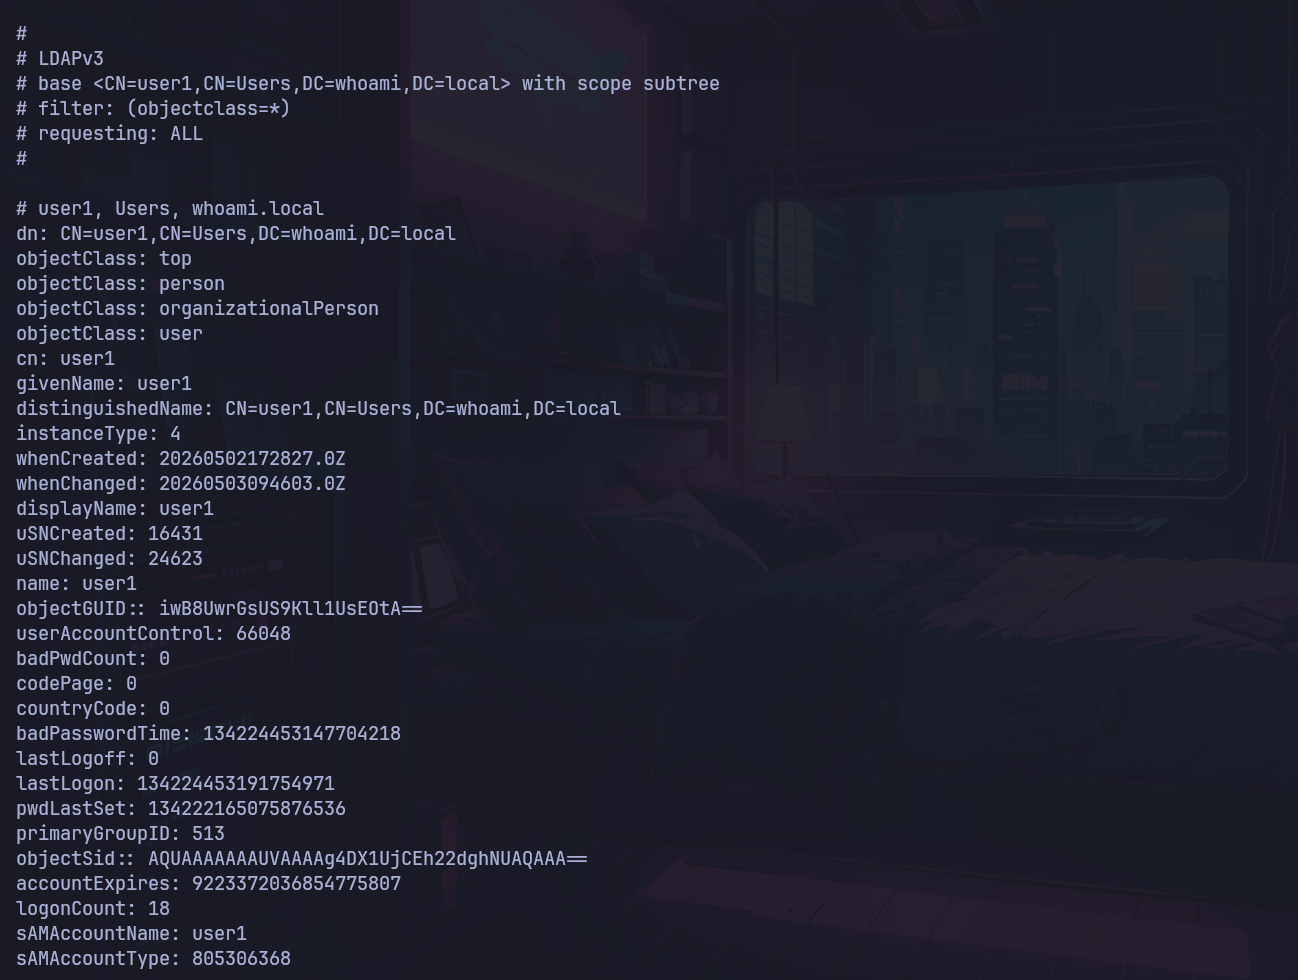
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=user1,CN=Users,DC=whoami,DC=local"
```
{% endcode %}
Эта команда напрямую обращается к `user1` объекту.
### Список компьютеров
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=computers,DC=whoami,DC=local"
```
{% endcode %}
Обратите внимание: в Active Directory стандартный контейнер обычно называется `CN=Computers`.
### Список встроенной группы Administrators
{% code overflow="wrap" %}
```bash
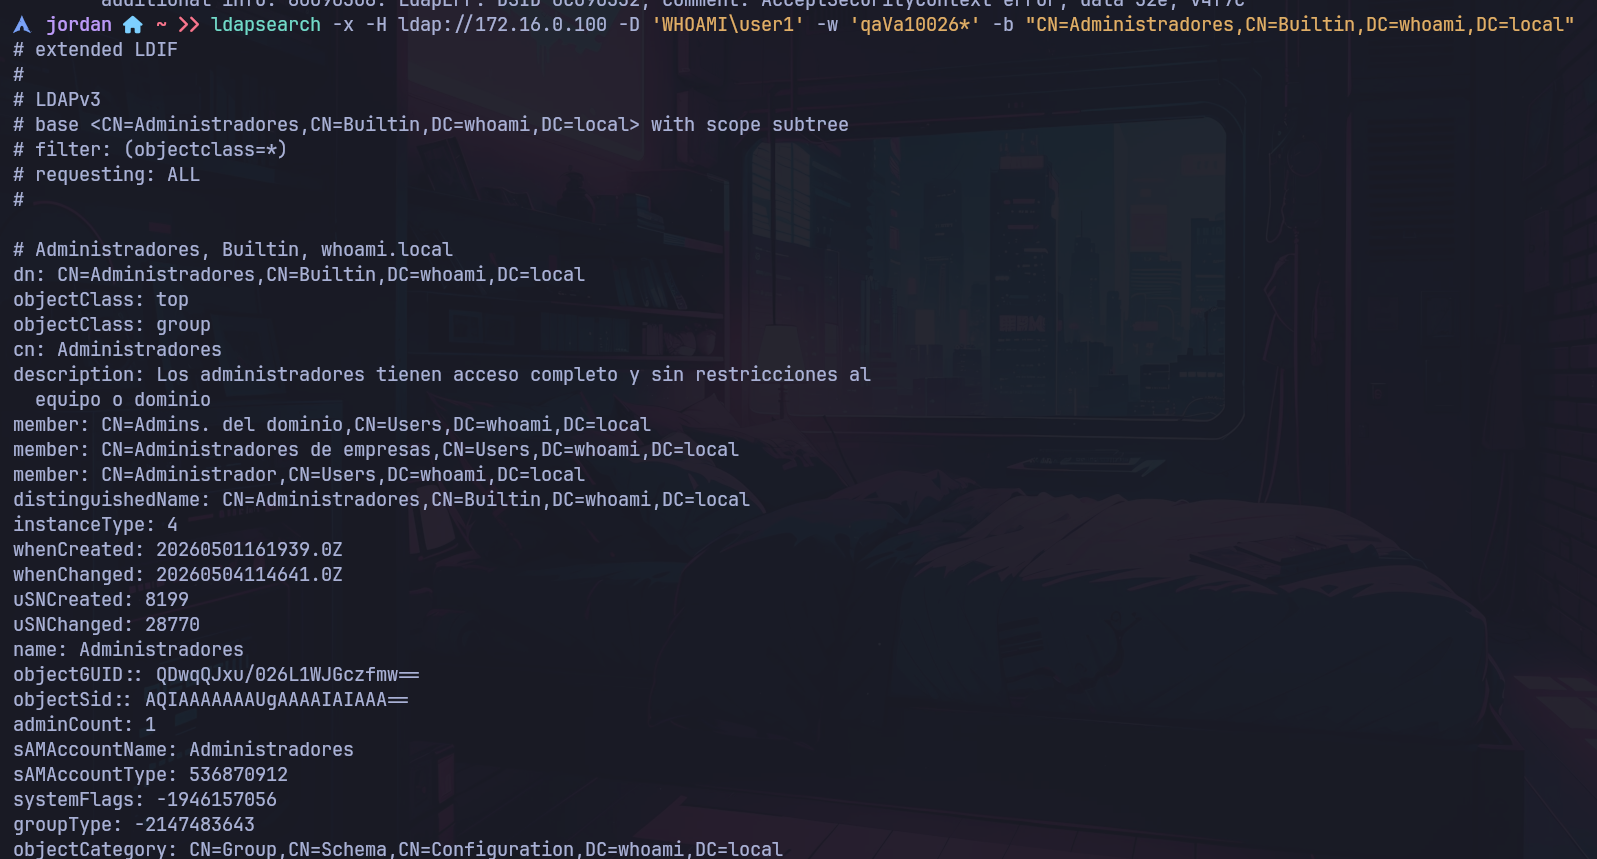
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=Administrators,CN=Builtin,DC=whoami,DC=local"
```
{% endcode %}
Эта команда нацелена на встроенную локальную группу `Administrators` в `Builtin` контейнере.
### Найти DN пользователя
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=user1,CN=Users,DC=whoami,DC=local" | grep dn
```
Пример результата:
```bash
CN=user1,CN=Users,DC=whoami,DC=local
```
* Эта **DN**или **Различающее имя**, это полный путь LDAP-объекта.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/active-directory/enumeration/ldapsearch.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.