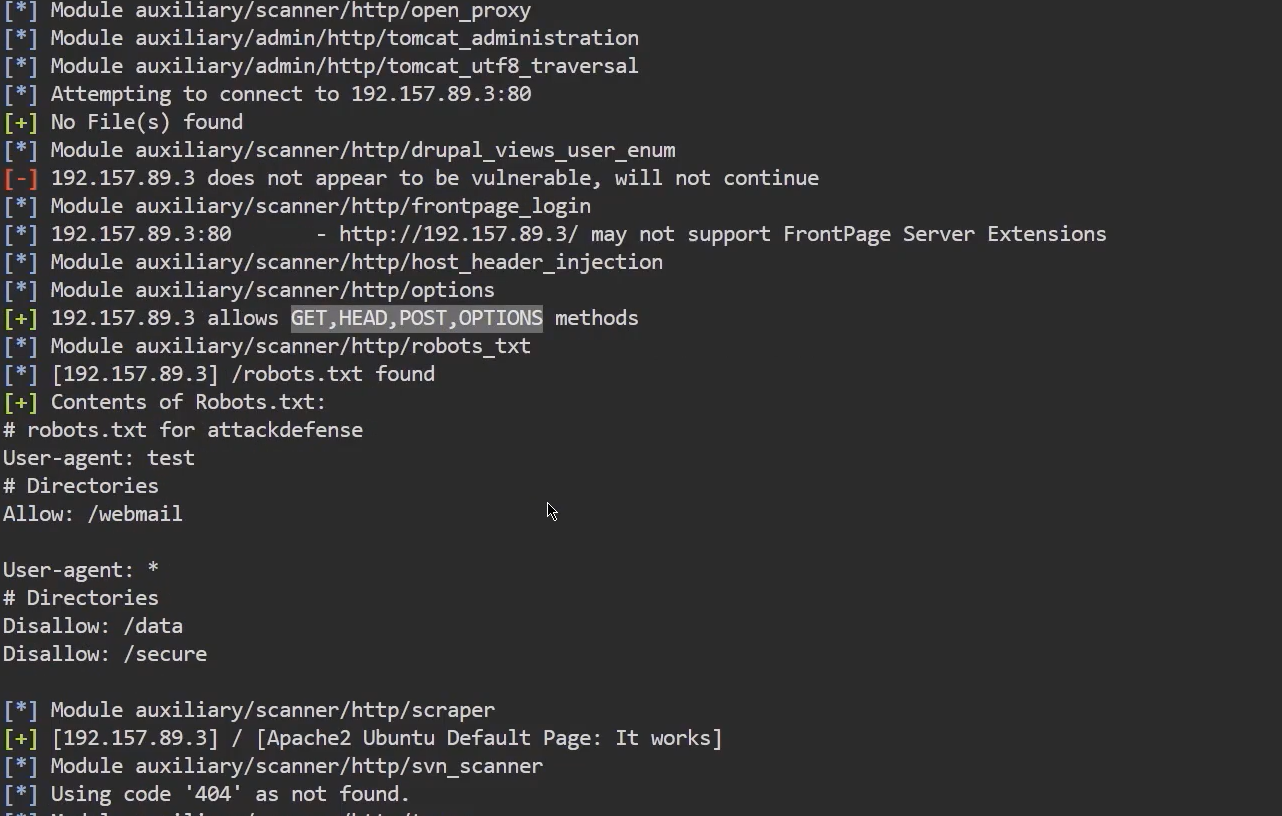
> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/hacking-tools/web/wmap-scan-web-vulnerabilities.md).
# Сканирование веб-уязвимостей WMAP
Заметки WMAP по запуску сканов веб-уязвимостей через Metasploit и анализу обнаруженных проблем приложения.
{% hint style="info" %}
WMAP — это плагин Metasploit, предназначенный для проведения тестирования на проникновение веб-приложений, в частности для выявления уязвимостей, характерных для конкретных сайтов. Он позволяет выполнять автоматизированное сканирование веб-целей.
{% endhint %}
**Подключение к Metasploit:** В отличие от других инструментов, WMAP не требует отдельного подключения к Metasploit — он напрямую интегрируется в фреймворк Metasploit для работы.
#### Запустить сканирование WMAP
1. **Загрузите модуль WMAP:** Для начала необходимо загрузить модуль WMAP в Metasploit с помощью следующей команды:
```
load wmap
```
2. **Создайте целевой сайт:** Вы должны указать IP-адрес или домен сайта для тестирования с помощью следующей команды:
```
wmap_sites -a 10.10.10.10
```
3. **Укажите цель:** Чтобы задать URL целевого сайта, используйте следующую команду, которая настраивает URL для сканирования:
```bash
wmap_target -t http://10.10.10.10/
```
4. **Запустите сканирование всех модулей:** Чтобы выполнить полное сканирование со всеми включенными модулями WMAP, используйте команду:
```bash
wmap_run -t
```
* Эта команда запускает сканирование с использованием всех доступных модулей для поиска уязвимостей в целевом веб-приложении.
```bash
wmap_run -e
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/hacking-tools/web/wmap-scan-web-vulnerabilities.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.