> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/business-logic/inconsistent-security-controls.md).
# Непоследовательные механизмы безопасности
Заметки по лабораторным работам PortSwigger Web Security Academy о непоследовательных механизмах безопасности, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Непоследовательные механизмы безопасности
**Цель лабораторной работы**
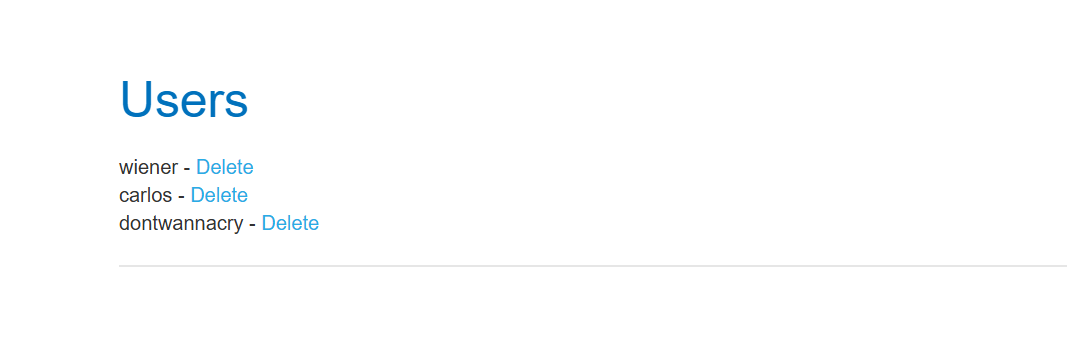
В этой лабораторной работе есть логическая ошибка, связанная с непоследовательными проверками безопасности. / Обычные пользователи могут получать доступ к административным функциям, обычно зарезервированным для сотрудников компании. / Цель — получить доступ к панели администратора и удалить пользователя **carlos**.
**Начальное наблюдение**
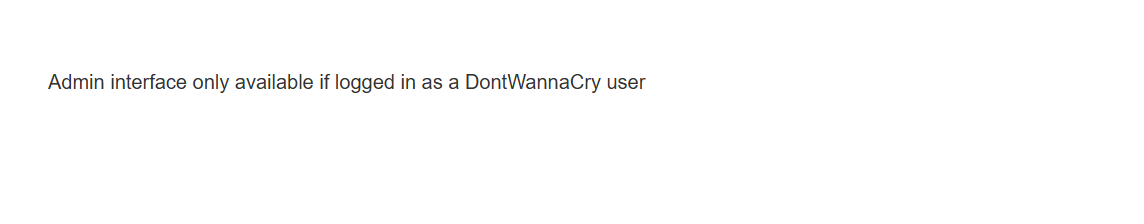
При попытке напрямую получить доступ к административному интерфейсу появится следующее сообщение:
> *Административный интерфейс доступен только при входе в систему как пользователь DontWannaCry*
Доступ к `/admin` и поэтому ограничен пользователями, принадлежащими к **DontWannaCry** домене.
**Попытка регистрации**
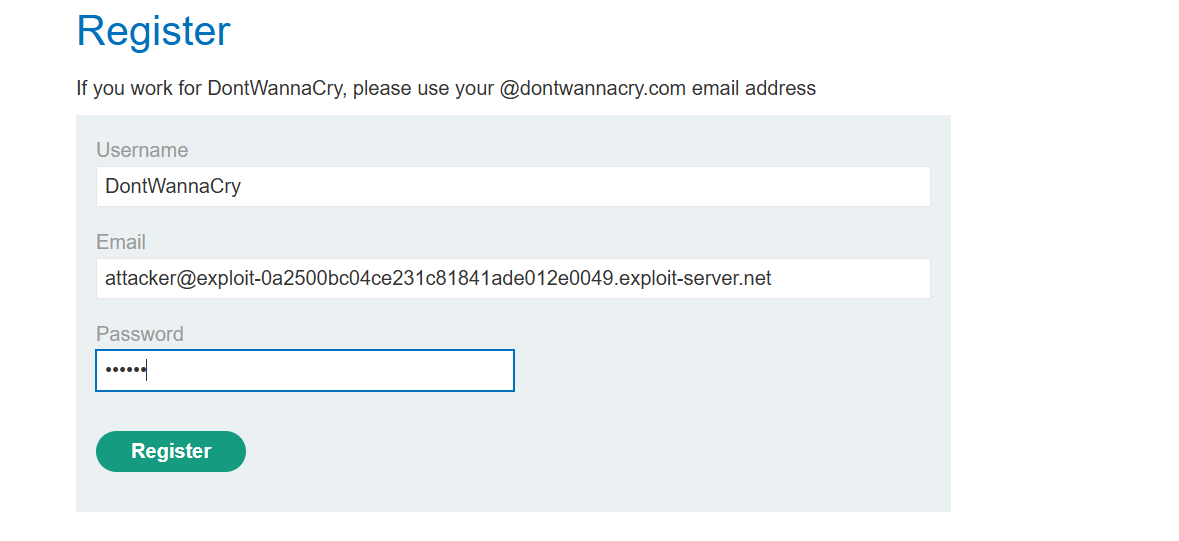
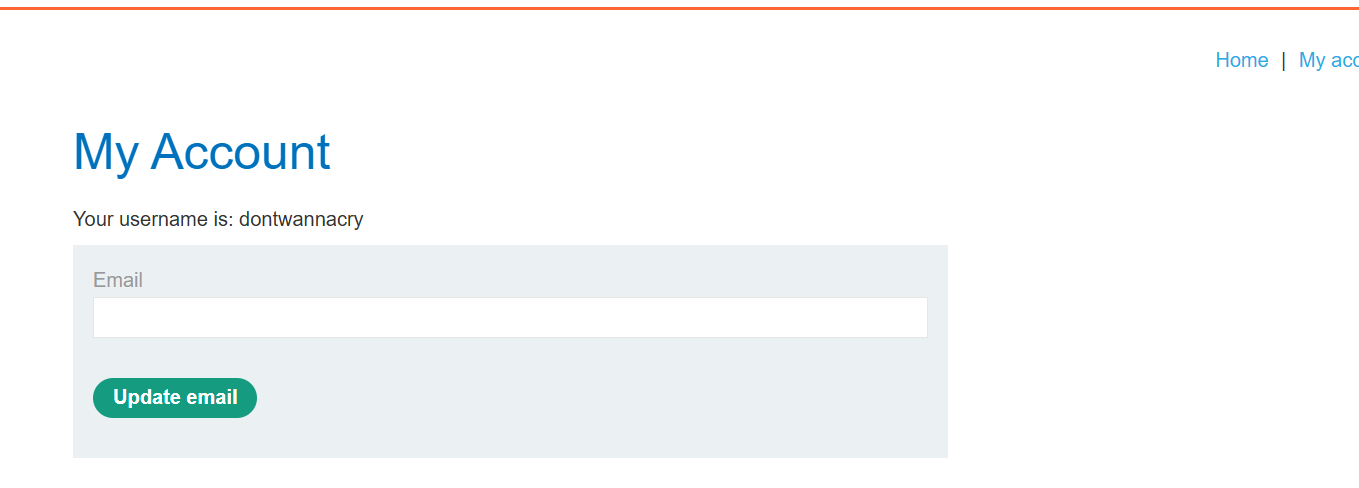
Новый пользователь регистрируется с использованием:
* **Имя пользователя**: `DontWannaCry` (уже существует)
* **Адрес электронной почты**: адрес, контролируемый атакующим/ `attacker@exploit-0a2500bc04ce231c81841ade012e0049.exploit-server.net`
После отправки формы приложение сообщает:
> *Проверьте свою электронную почту на наличие ссылки для регистрации учетной записи*
**Проверка учетной записи**
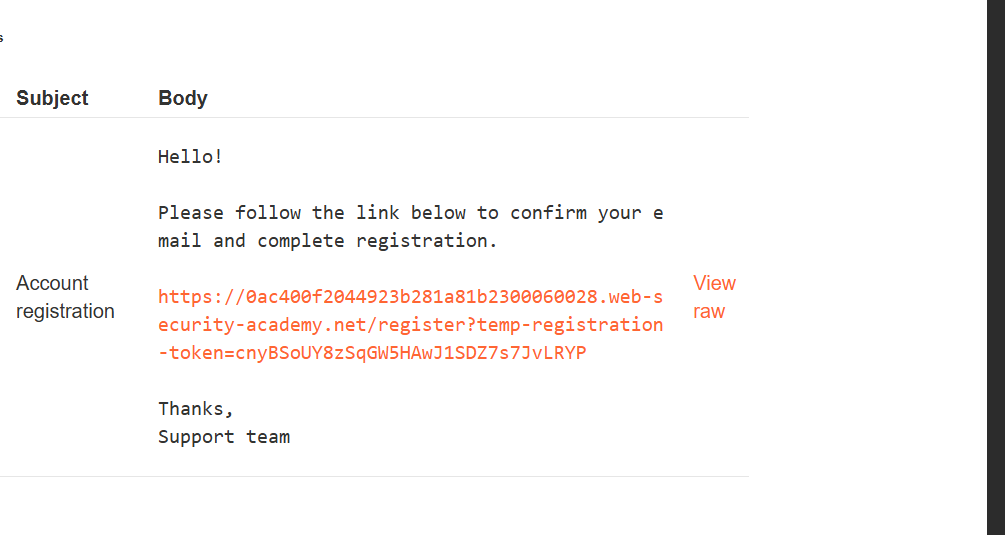
Поступает письмо с подтверждением и ссылкой, содержащей токен.
Используемые учетные данные:
* **Пользователь**: `DontWannaCry`
* **Пароль**: `jordan`
Соединение работает корректно.
**Изменение адреса электронной почты**
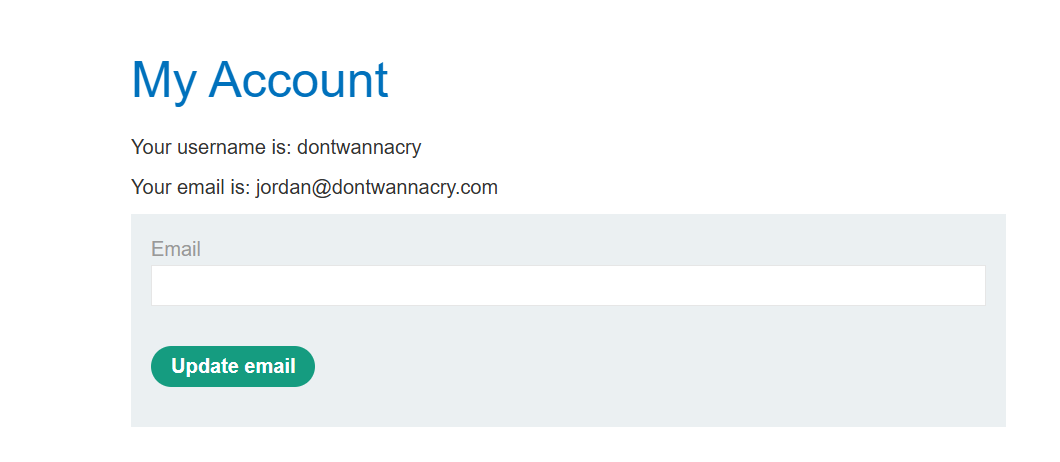
После входа в систему вы изменяете адрес электронной почты учетной записи без дополнительной проверки, используя:
```bash
jordan@dontwannacry.com
```
Подлинность этого изменения никак не проверяется.
**Доступ к административному интерфейсу**
После изменения адреса электронной почты пользователь теперь считается принадлежащим домену **DontWannaCry**. / Доступ к `/admin` интерфейсу затем разрешается.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/business-logic/inconsistent-security-controls.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.