> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/cache-poisoning/web-cache-poisoning-via-unkeyed-query-string.md).
# Отравление веб-кэша через неучитываемую строку запроса
Заметки по лабораторным работам PortSwigger Web Security Academy об отравлении веб-кэша через неучитываемую строку запроса, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Отравление веб-кэша через неучитываемую строку запроса
В этой лабораторной работе демонстрируется уязвимость к отравлению веб-кэша из-за того, что **строка запроса не включается в ключ кэша**. Законный пользователь регулярно посещает главную страницу сайта, используя **Google Chrome**.
Цель состоит в том, чтобы отравить главную страницу так, чтобы она возвращала ответ, содержащий **выполняющийся JavaScript `alert(1)`** в браузере жертвы.
***
**Шаг 1: Перехват главной страницы**
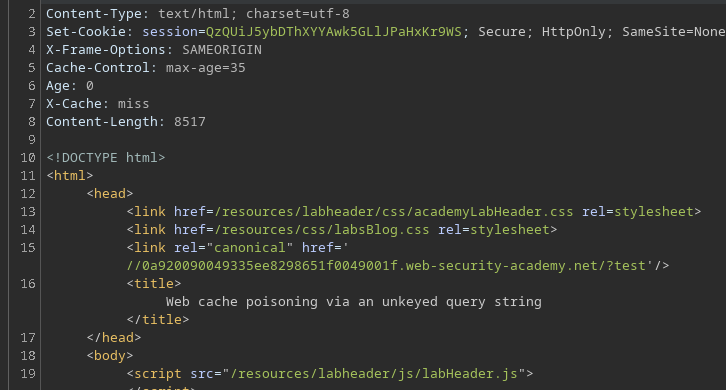
Запрос к корню сайта (`/`) перехватывается. / В ответе мы наблюдаем наличие канонического **ссылку**, что указывает на то, что некоторые элементы URL могут отражаться в HTML.
***
**Шаг 2: Проверка строки запроса**
В URL добавляется произвольная строка запроса:
```bash
/?test
```
Значение успешно **отражается в ответе**, что подтверждает, что строка запроса влияет на возвращаемое содержимое.
**Шаг 3: HTML-инъекция**
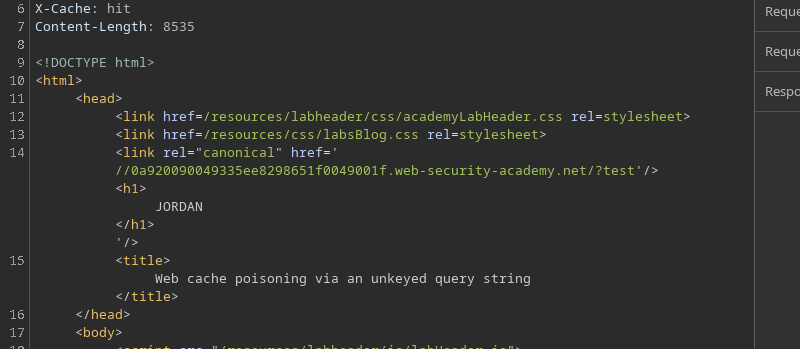
Затем строка запроса изменяется для внедрения HTML:
```bash
/?test'/>
JORDAN
```
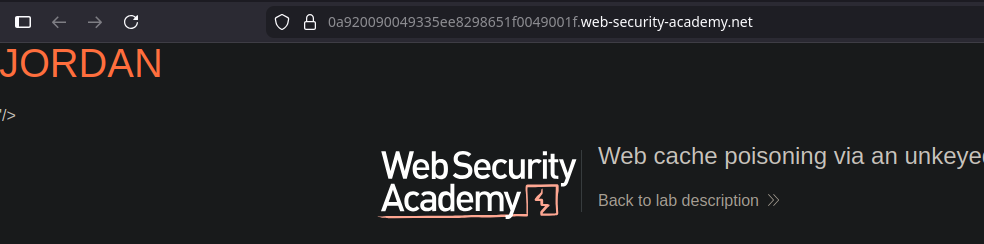
Эта `
` тег корректно интерпретируется браузером, демонстрируя работоспособную \*\*HTML-инъекцию\*\*.
**Шаг 4: Инъекция JavaScript (отравление кэша)**
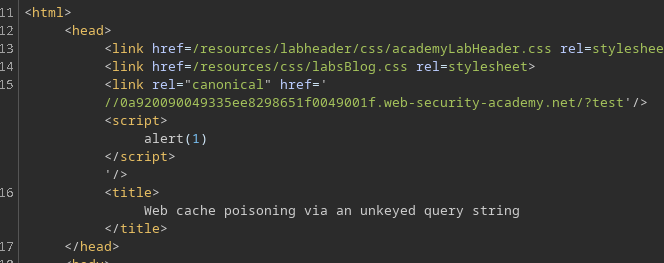
Замените HTML-инъекцию полезной нагрузкой JavaScript:
```bash
/?test'/>
```
Ответ теперь содержит скрипт, который \*\* выполняется браузером\*\*.
**Результат**
Поскольку строка запроса **не включается в ключ кэша**, отравленный ответ сохраняется и выдаётся другим пользователям, посещающим главную страницу. / Затем жертва автоматически запускает выполнение `alert(1)` во время его посещения, что подтверждает работоспособность лабораторной работы.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/cache-poisoning/web-cache-poisoning-via-unkeyed-query-string.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.