> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/essential-skills/fast-detection-with-targeted-scanning.md).
# Быстрое обнаружение с помощью целевого сканирования
Заметки по лабораторным работам PortSwigger Web Security Academy о быстром обнаружении с помощью целевого сканирования, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Быстрое обнаружение уязвимостей с помощью целевого сканирования
#### Контекст лабораторной работы
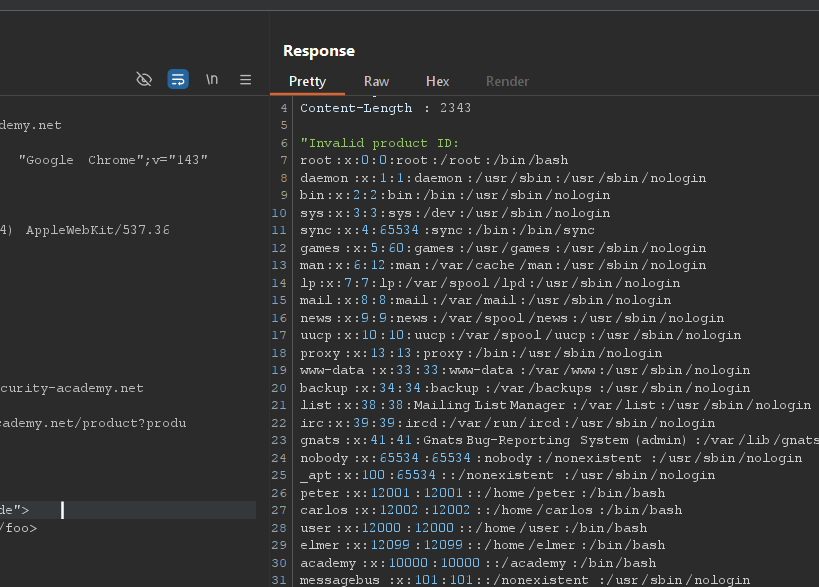
В этом лабораторном задании есть уязвимость к **чтению произвольных файлов на сервере**. / Цель состоит в том, чтобы **восстановить содержимое `/etc/passwd` файла менее чем за 10 минут**.
Из-за этого ограничения по времени рекомендуется использовать **Burp Scanner** вместо полного аудита приложения.
#### Временное ограничение
* Активен \*\*10-минутный таймер\*\* с начала лабораторной работы.
* Полное сканирование сайта может быть слишком медленным.
* Поэтому предпочтительнее **умно нацеливаться на потенциально уязвимые точки входа**.
#### Методология
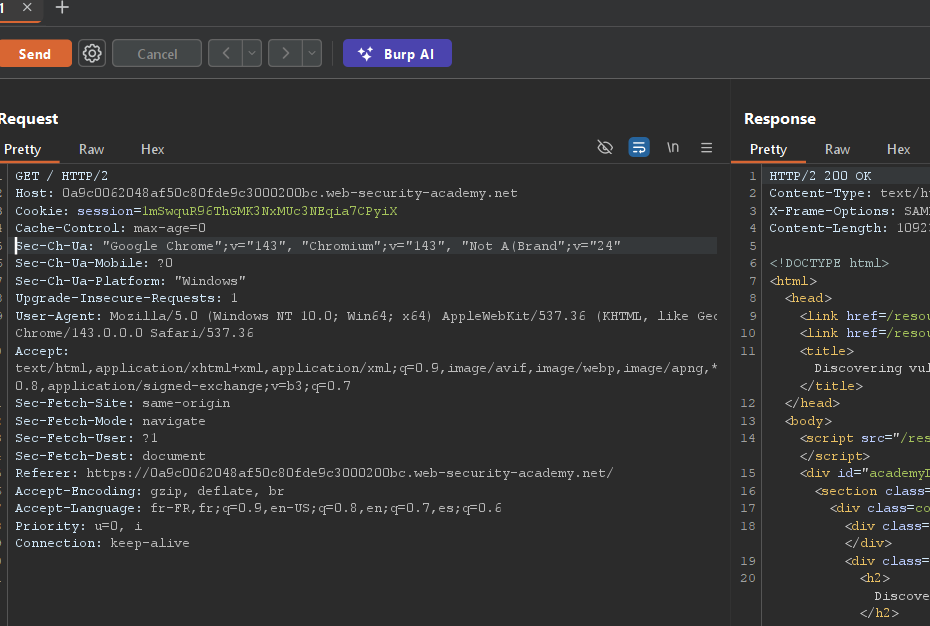
1. **Перехватите соответствующий HTTP-запрос** с помощью Burp Proxy.
Быстро проанализируйте логику запроса, чтобы определить интересную конечную точку.
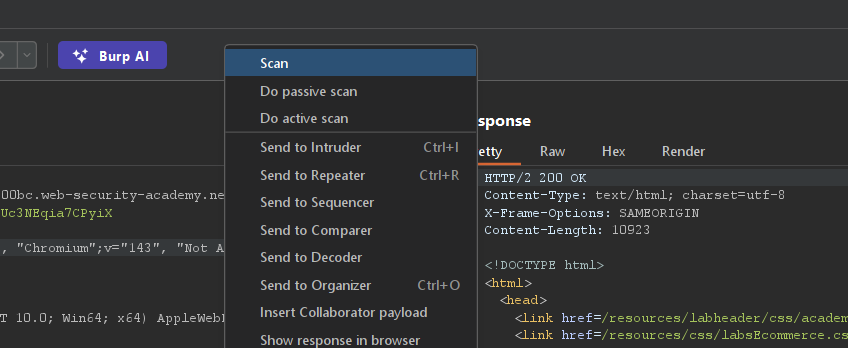
Запустите целевое сканирование через **Burp Scanner** для этого конкретного запроса.
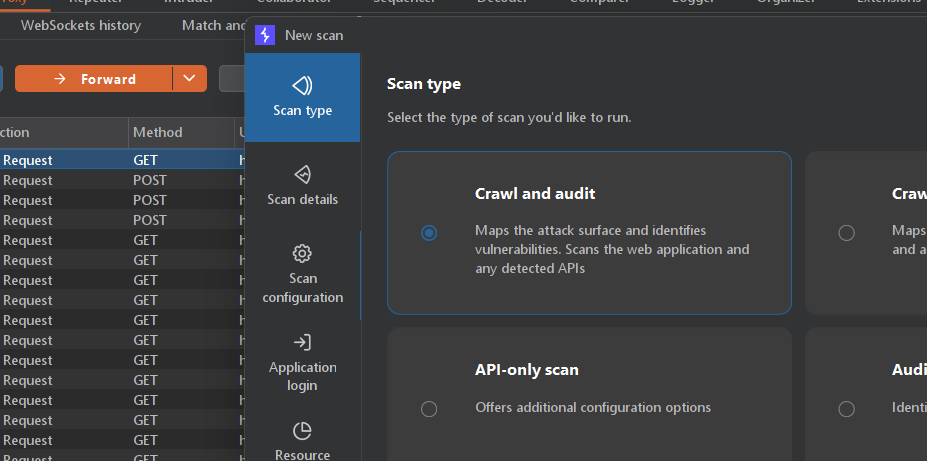
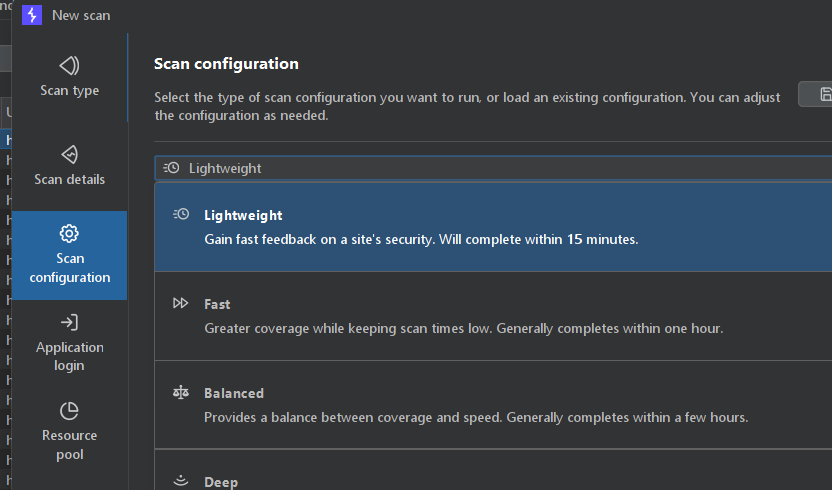
#### Конфигурация сканирования Burp
* Выбранный тип сканирования: **Обход и аудит**
* Режим : **Быстрое сканирование**
Цель: быстро определить эксплуатируемый вектор атаки
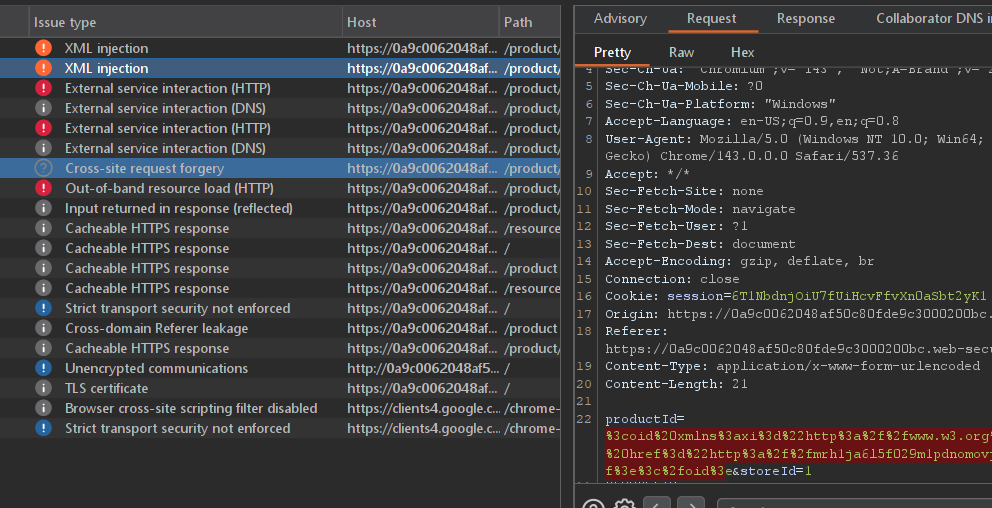
#### Уязвимость обнаружена
Сканирование выявляет уязвимость типа **Инъекция XML (XInclude)**.
Начальная полезная нагрузка, обнаруженная сканером Burp:
{% code overflow="wrap" %}
```xml
```
{% endcode %}
Это подтверждает, что сервер обрабатывает **XInclude** сущности без ограничений.
#### Эксплуатация: чтение `/etc/passwd`
Полезная нагрузка изменяется, чтобы включить локальный системный файл:
{% code overflow="wrap" %}
```http
productId=
id>&storeId=1
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/essential-skills/fast-detection-with-targeted-scanning.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.