> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/business-logic/bypassing-authentication-via-encryption-oracle.md).
# Bypassing Authentication via Encryption Oracle
Bypassing Authentication via Encryption Oracle notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remediation context.
### Authentication Bypass via Encryption Oracle
**Description of lab**
This lab has a logical flaw exposing a \*\*server-side encryption \*\*oracle. By exploiting this weakness, it is possible to forge a valid encrypted value in order to bypass authentication, access the admin panel and delete user **carlos**.
Identifier provided:
* User: `wiener`
* Password: `peter`
**Initial observation**
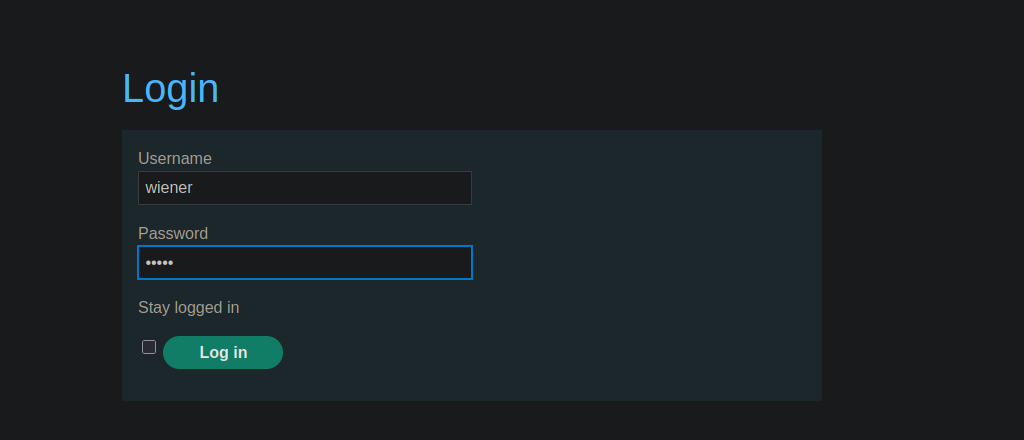
On the login page, the **Stay logged in** option is available.
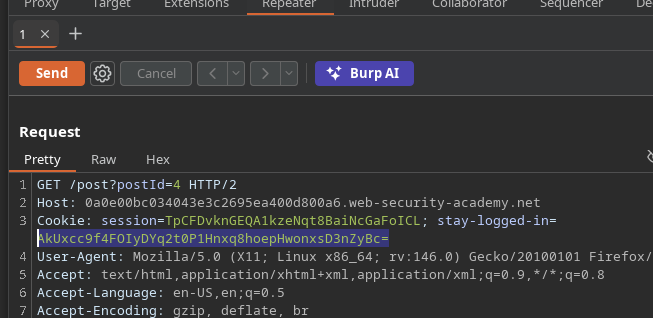
When used, a cookie encrypted in **Base64** is generated and stored on the customer side.
```bash
echo '0HE6oMYJL//S1fLwttqR7WMF3EX4KJmvfFRI53qpVnk=' | base64 -d
# The decoded value is binary ciphertext, not readable text.
```
### Identification of Encryption Oracle
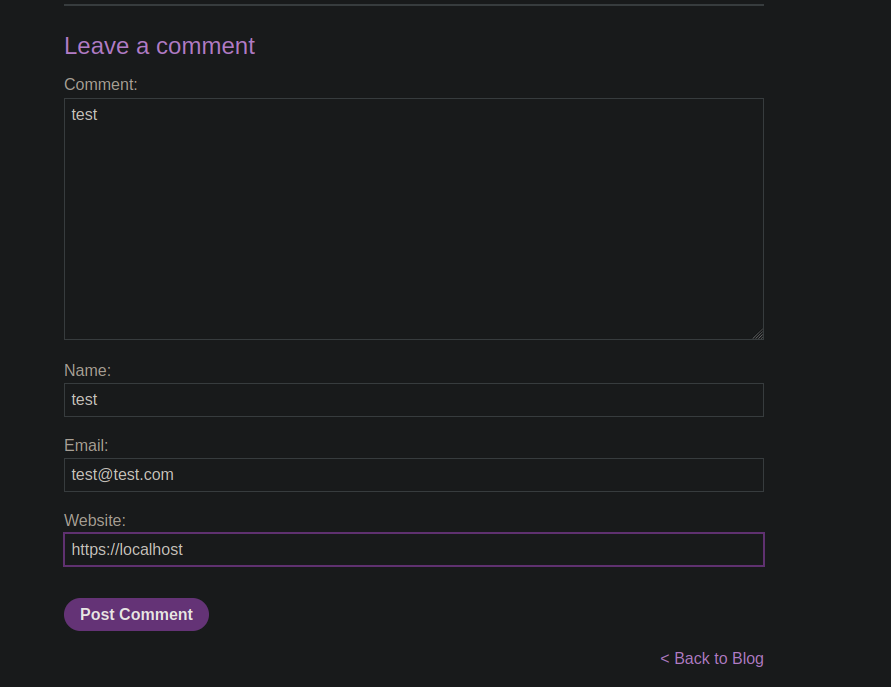
When a valid comment is submitted, no specific response is observed.
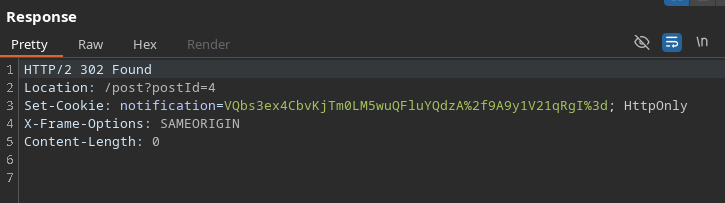
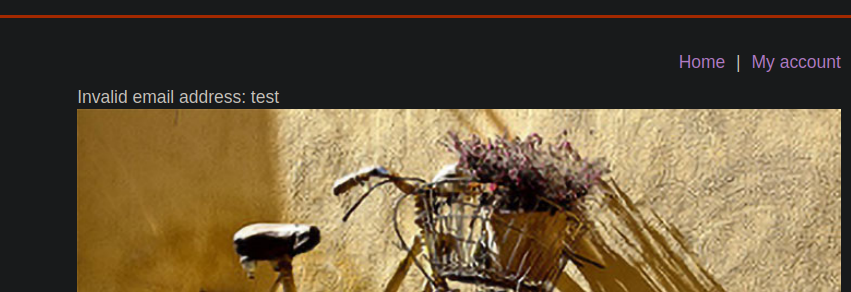
However, if a comment causes an application error (e.g. an invalid email address), the server:
* returns an error message displayed on the screen;
{% code overflow="wrap" %}
```bash
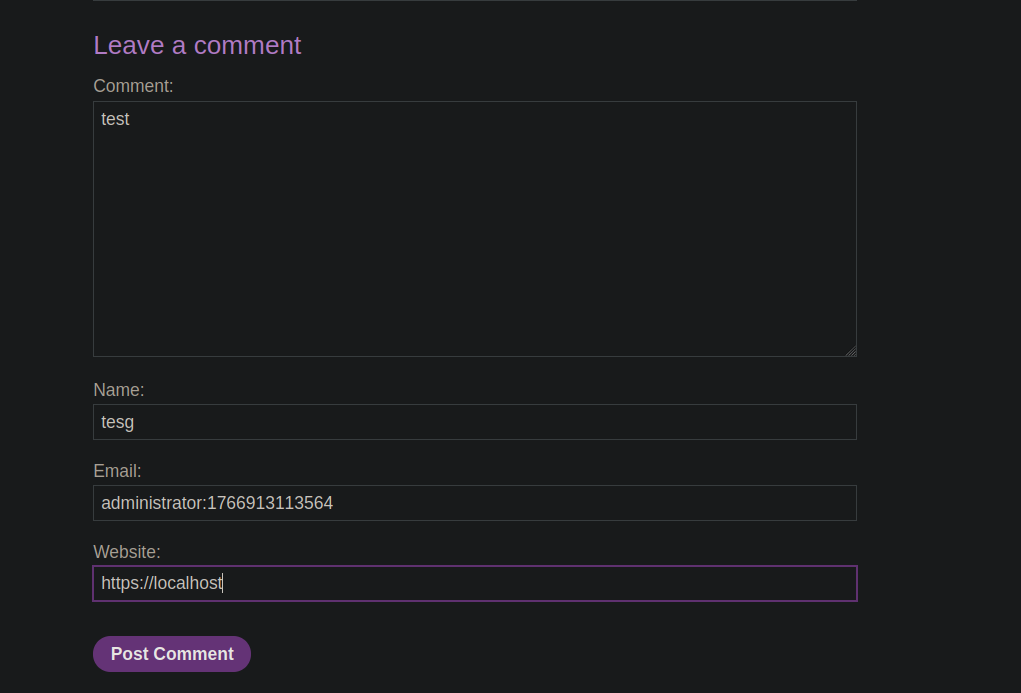
csrf=cFMQUjAyzETtEr8TLsoir7V5p4C3m4ZG&postId=4&comment=test&name=test&email=test&website=https://localhost
```
{% endcode %}
* generates a new cookie `notification`\*\*, encrypted.
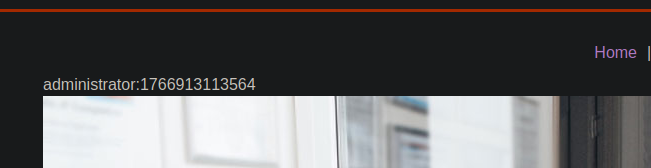
The content displayed is for example:
This shows that:
* the server \*\*decrypts the content of the `notification` cookie;
The server therefore acts as a **oracle of encryption and decryption**.
* the deciphered text is **reinjected in HTML response**.
### Correlation with the Cookie
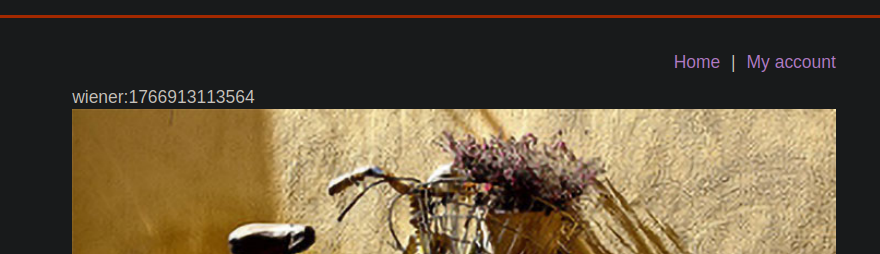
By injecting the encrypted value of the cookie \*\*
The observed format is:
This clearly corresponds to:
* a user name;
* a timestamp.
#### Forgery of an Administrator Identity
The objective is to have the server encrypt the following string:
```bash
administrator:1766913113564
```
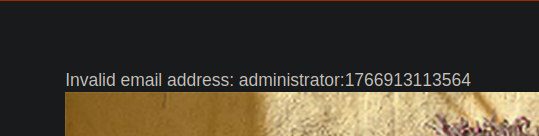
To do this, this value is injected into the vulnerable field (invalid comment/email), causing:
* display the error message containing this string;
the generation of a new `notification` cookie, including the text injected.
{% code overflow="wrap" %}
```bash
Set-Cookie: notification=VQbs3ex4CbvKjTm0LM5wuZa79pnAzKI9MEsa1O0MbX%2fJpfl9baj6yL3ryxh4u6nyiWHVwxP7%2fVDPyft%2f1qAbbQ%3d%3d; HttpOnly
```
{% endcode %}
### Encryption Algorithm Identification
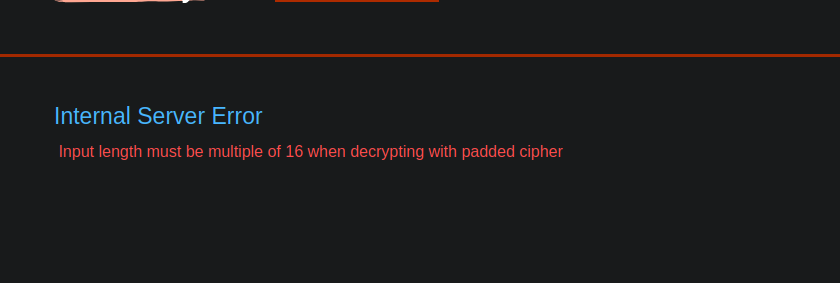
By arbitrarily truncating the encrypted value, the server returns the following error
```bash
PTBLGtTtDG1/yaX5fW2o%2bsi968sYeLup8olh1cMT%2b/1Qz8n7f9agG20%3d
```
`Input length must be multiple of 16 when decrypting with padded cipher`
This clearly indicates the use of **AES with padding**, operating in blocks of **16 bytes**.
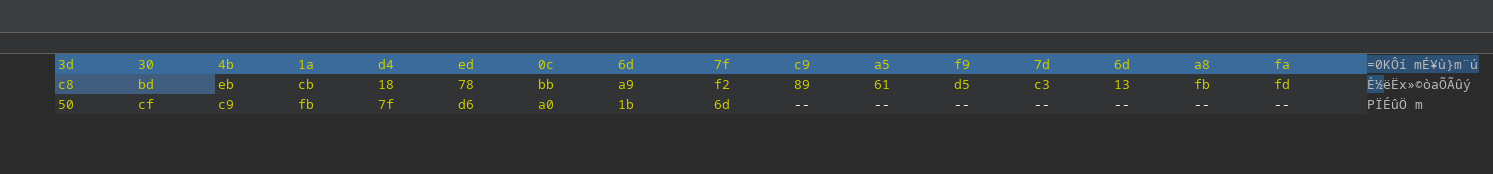
#### Cipher Block Manipulation
The problem encountered is the presence of invalid padding characters at the end of the message. / To remedy this, the injected chain is preceded by filling characters to align the blocks correctly:
```
xxxxxxxxxadministrator:1766913113564
```
A new encrypted cookie is then generated.
VQbs3ex4CbvKjTm0LM5wuZJqwlVboMZ2IzNuiTfVH6iHj9RZUT59d5kGoS64tVE5wWiEfmp6VbJG%2bb%2fNW5%2bblA%3d%3d
### Cutting and Recomposing the Cookie
By deleting the first **two encrypted blocks** (corresponding to filling), only blocks containing:
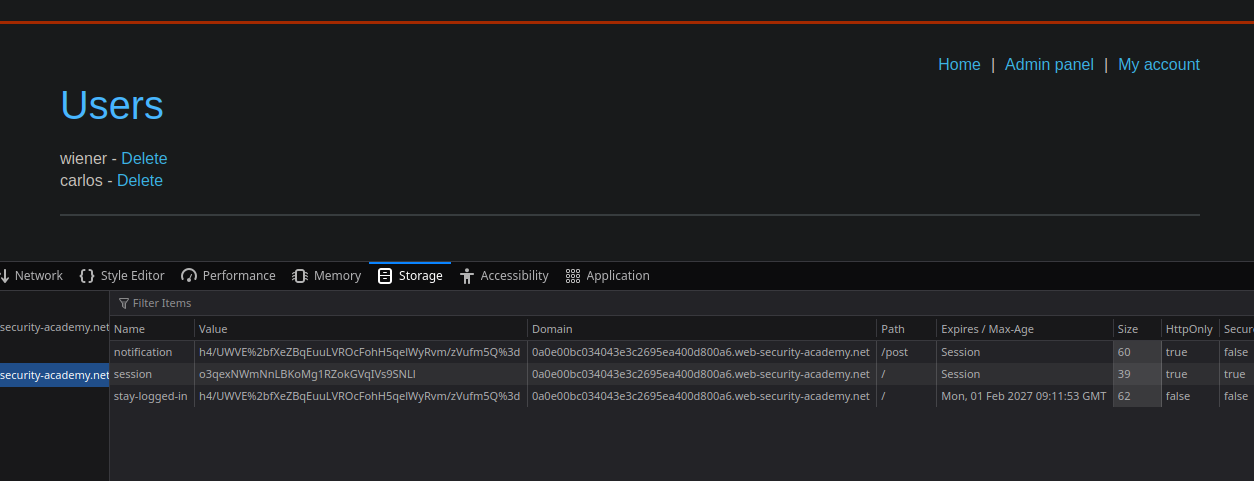
This final encrypted value is accepted by the server.
```
h4/UWVE%2bfXeZBqEuuLVROcFohH5qelWyRvm/zVufm5Q%3d
```
#### Contouring Authentication
Final steps:
1. Delete the existing session cookie.
2. Replace the value of the cookie \*\*
3. Refresh the page.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/web/business-logic/bypassing-authentication-via-encryption-oracle.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.