> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/zh/reconnaissance/web-fuzzing.md).
# Web 模糊测试
Web 模糊测试方法,用于借助 Gobuster 和 Wfuzz 等工具发现隐藏目录、文件、扩展名、参数和暴露的资源。
Web fuzzing 有助于在 Web 应用侦察过程中发现隐藏的目录、文件、扩展名、参数、虚拟主机和暴露的资源。
{% hint style="info" %}
用于发现网站目录和文件的工具和方法有很多,无论是通过命令行还是在线资源。以下是主要方法和最有用的工具:
{% endhint %}
## Gobuster:
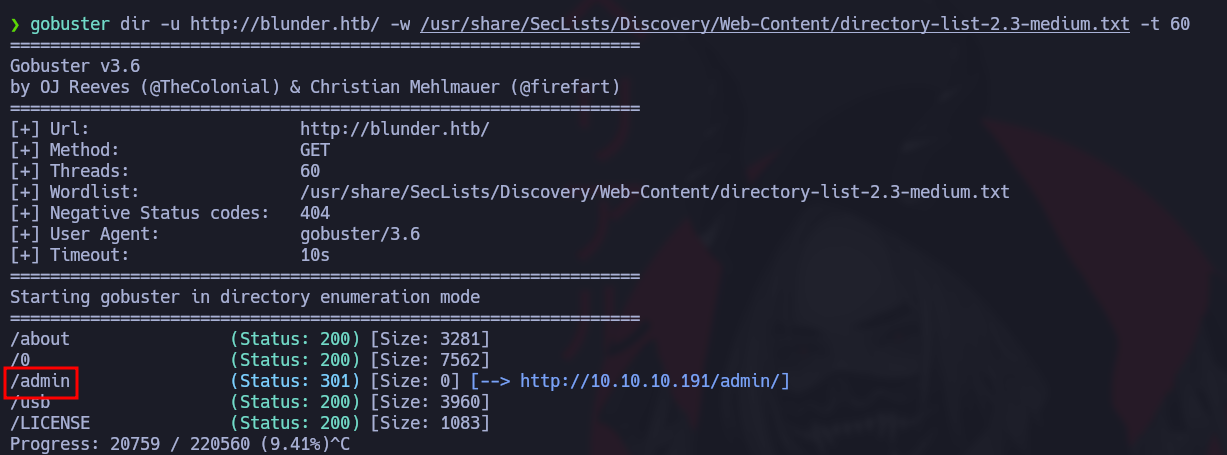
> Gobuster 是一款快速且高效的工具,用于对网站目录和文件进行暴力破解攻击。
### **仅目录:**
```bash
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt -t 100
```
* **-u**: 目标站点的 URL。
* **-w**: 包含关键字列表(字典文件)的文件路径。
* **-t**: 用于搜索的线程数。
### **具有特定扩展名的文件:**
```bash
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/quickhits.txt -t 100 -x html,php,txt
```
* **-x**: 指定要搜索的扩展名。
### **为响应添加特定过滤条件:**
* **-hh**: 按响应正文大小(字节)过滤。
* **-hc**: 排除具有特定状态码的响应(例如 404)。
## Wfuzz:
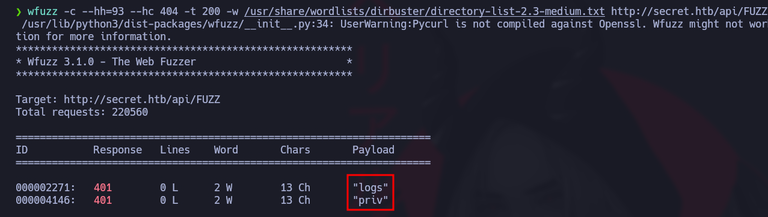
> Wfuzz 允许通过暴力破解攻击进行高级且可配置的搜索,无论是目录还是 URL 中的参数。
### **仅目录:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt http://website.com/FUZZ
```
* **-c**: 以彩色显示输出。
* **FUZZ**: 指示将插入关键字的位置。
### **具有特定扩展名的文件:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/quickhits.tx -z list,html-txt-php http://website.com/
```
* **-z**: 定义搜索中要使用的附加扩展名(list 允许你定义多个扩展名)。
### **动态参数值(`?product_id=`) :**
```bash
wfuzz -c -t 100 -z range,1-200000 'http://website.com/shop/buy/detail?product_id=FUZZ'
```
* **-z range,1-200000**: 使用 1 到 200,000 的数字范围执行暴力破解攻击。
## **其他方法:**
### 公共来源发现:
如果你更喜欢可视化的公共来源方法,请使用维护中的目录,位于 [OSINT 与研究工具](/zh/hacking-tools/osint.md).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/zh/reconnaissance/web-fuzzing.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.